 黑客技术
点击放大
项目说明
<p align="center">
<img src=" alt="Hacker roadmap" /><br>
</p>
This repository is an o of what you need to learn penetration testing and a collection of hacking tools, resources and references to practice ethical hacking. Most of the tools are UNIX compatible, free and open 源码.
Status
This project has been terminated and archived. Content might be outdated.
----
Before you start
Table of Contents
- What is penetration testing?
- Want to become a penetration tester?
- :male_detecti Gathering
- :lock: Password Attacks
- :memo: Wordlists
- :globe_with_meridians: Wireless Testing
- :wrench: Exploitation Tools
- :busts_in_silhouette: Sniffing & Spoofing
- :rocket: Web Hacking
- :tada: Post Exploitation
- :package: Frameworks
- Books / Manuals
- Discussions
- Security Ad
- Challenges
(TOC made with nGitHubTOC)
Introduction
What is penetration testing?
Penetration testing is a type of security testing that is used to test the security of an application. It is conducted to find a security risk which might be present in a system.
If a system is not secure, then an attacker may be able to disrupt or take unauthorized control of that system. A security risk is normally an accidental error that occurs while de and implementing software. For example, configuration errors, design errors, and software bugs, etc. Learn more
Want to become a penetration tester?
Knowing about risks on the internet and how they can be pre is very useful, especially as a de. Web hacking and penetration testing is the v2.0 of self-defense! But is knowing about tools and how to use them really all you need to become a pen tester? Surely not. A real penetration tester must be able to proceed rigorously and detect the weaknesses of an application. They must be able to identify the technology behind and test every single door that might be open to hackers.
This repository aims first to establish a reflection method on penetration testing and explain how to proceed to secure an application. And secondly, to regroup all kind of tools or resources pen testers need. Be sure to know basics of programming languages and internet security before learning pen testing.
Also, this is important to inform yourself about the law and what you are allowed to do or not. According to your country, the computer laws are not the same. First, check laws about privacy and sur: Nine eyes countries, Five eyes and Fourteen Eyes. Always check if what you're doing is legal. Even when it's not offensi gathering can also be illegal!
(Table of Contents)
Some
Infosec: Information security, which is the practice of pre unauthorized access, use, disclosure, disruption, modification, inspection, recording or destruction of information. The information or data may take any form, e.g. electronic or physical. Infosec can also be a person who practices ethical security. Wikipedia
Opsec: Operations security, which is a process that identifies critical information to determine if friendly actions can be observed by enemy intelligence, determines if information obtained by ad could be interpreted to be useful to them, and then executes selected measures that eliminate or reduce ad exploitation of friendly critical information. Wikipedia
Black/grey/white hat hacker: Someone who uses bugs or exploits to break into systems or applications. The goal and the method differs depending if they're a black, grey or white hat hacker. A black hat is just someone malicious that does not wait permission to break into a system or application. A white hat is *usually* a security researcher who practice ethical hacking. A grey hat is just in the middle of these two kind of hackers, they might want to be malicious if it can be benefit (data breach, money, whistleblowing ...).
Red team: According to Wikipedia, a red team or the red team is an independent group that challenges an organization to improve its effecti by assuming an ad role or point of view. It is particularly effective in organizations with strong cultures and fixed ways of approaching problems. The United States intelligence community (military and ci) has red teams that explore alternati and write articles as if they were foreign world leaders. Little formal doctrine or publications about Red Teaming in the military exist. In infosec exercises, Red teamers are playing the role of attackers. Wikipedia
Blue team: A blue team is a group of indi who perform an analysis of information systems to ensure security, identify security flaws, the effecti of each security measure, and to make certain all security measures will continue to be effecti implementation. As a result, blue teams were de to design defensi against red team acti. In infosec exercises, Blue teamers are playing the role of defenders. Wikipedia)
Penetration tester: An ethical hacker who practices security, tests applications and systems to prevent intrusions or find .
Security researcher: Someone who practices pen testing and browses the web to find phishing/fake websites, infected servers, bugs or . They can work for a company as a security consultant and are most likely a Blue teamer.
Reverse engineering: Reverse engineering, also called back engineering, is the process by which a man-made object is deconstructed to reveal its designs, architecture, or to extract knowledge from the object. Similar to scientific research, the only difference being that scientific research is about a natural phenomenon. Wikipedia
Social engineering: In the context of information security, it refers to psychological manipulation of people into performing actions or di confidential information. A type of confidence trick for the purpose of information gathering, fraud, or system access, it differs from a traditional "con" in that it is often one of many steps in a more complex fraud scheme. The term "social engineering" as an act of psychological manipulation of a human, is also associated with the social sciences, but its usage has caught on among computer and information security professionals. Wikipedia)
Threat analyst: A threat hunter, also called a cybersecurity threat analyst, is a security professional or managed service provider (MSP) that proactively uses manual or machine-assisted techniques to detect security incidents that may elude the grasp of automated systems. Threat hunters aim to unco that an enterprise would otherwise not find out about, pro chief information security officers (CISOs) and chief information officers (CIOs) with an additional line of defense against ad persistent threats (APTs). SearchCIO
(Table of Contents)
Difference between hacking and ethical hacking
A black hat is practicing penetration testing, but unlike a white hat, this is not ethical hacking. Ethical hacking is about finding and improve the security of a system. An ethical hacker is the ultimate security professional. Ethical hackers know how to find and exploit and weaknesses in systems, just like a malicious hacker (a black hat hacker). In fact, they both use the same skills; however, an ethical hacker uses those skills in a legitimate, lawful manner to try to find and fix them before the bad guys can get there and try to break in. An ethical hacker is basically a white hat hacker.
(Table of Contents)
Languages
Learning programming is the very first way to start learning about security. There's a lot of languages, most people start with Python, it's the easiest and the most popular one. PHP and Go are the less popular to write security-related stuff, but any of these can still be used in such context. Bash and Powershell are mostly about scripting and writing simple CLI applications.
Since not all languages work the same way, you need to look at how they work and what you want to learn. For example, C++ and Ja, PHP and Python do not, they are interpreted languages. This definitely changes what you should use them for. Each language also has its own design patterns.
Scripting
Software & mobile apps
General purpose
(Table of Contents)
Content Management Systems
These are the most used Content Management Systems (CMS). See a complete list here.
(Table of Contents)
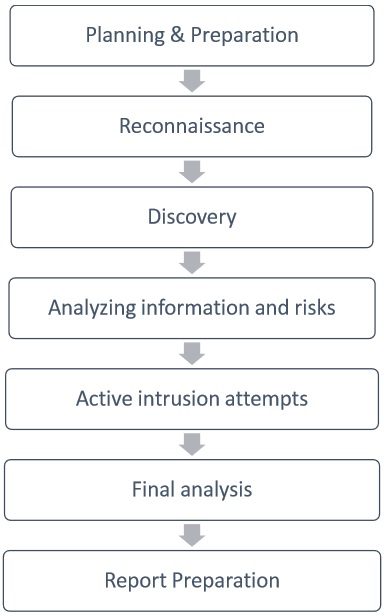
Basic steps of pen testing
<p align="center">
<img src="
</p>
*Source: tutorialspoint*
Read more about pen testing methodology
(Table of Contents)
Tools by category
A more complete list of tools can be found on Kali Linux official website.
#### :male_detecti Gathering
Information Gathering tools allows you to collect host metadata about services and users. Check informations about a domain, IP address, phone number or an email address.
| Tool | Language | Support | Description |
| ----------- |-------------------------|----------|----------------|
| theHar | Python | Linux/Windows/macOS | E-mails, subdomains and names Har. |
| CTFR | Python | Linux/Windows/macOS | Abusing Certificate Transparency logs for getting HTTPS websites subdomains. |
| Sn1per | bash | Linux/macOS | Automated Pentest Recon Scanner. |
| RED Hawk | PHP | Linux/Windows/macOS | All in one 工具 for Information Gathering, Scanning and Crawling. A must have 工具 for all penetration testers. |
| Infoga | Python | Linux/Windows/macOS | Email Information Gathering. |
| KnockMail | Python | Linux/Windows/macOS | Check if email address exists. |
| a2sv | Python | Linux/Windows/macOS | Auto Scanning to SSL . |
| Wfuzz | Python | Linux/Windows/macOS | Web application fuzzer. |
| Nmap | C/C++ | Linux/Windows/macOS | A very common 工具. 网络 host, vuln and port detector. |
| PhoneInfoga | Go | Linux/macOS | An OSINT framework for phone numbers. |
#### :lock: Password Attacks
Crack passwords and create wordlists.
| Tool | Language | Support | Description |
| ----------- |-------------------------|----------|----------------|
| John the Ripper | C | Linux/Windows/macOS | John the Ripper is a fast password cracker. |
| hashcat | C | Linux/Windows/macOS | World's fastest and most ad password recovery utility. |
| Hydra | C | Linux/Windows/macOS | Parallelized login cracker which supports numerous protocols to attack. |
| ophcrack | C++ | Linux/Windows/macOS | Windows password cracker based on rainbow tables. |
| Ncrack | C | Linux/Windows/macOS | High-speed 网络 authentication cracking 工具. |
| WGen | Python | Linux/Windows/macOS | Create awesome wordlists with Python. |
| SSH Auditor | Go | Linux/macOS | The best way to scan for weak ssh passwords on your 网络. |
###### :memo: Wordlists
| Tool | Description |
| ----------- |----------------|
| Probable Wordlist | Wordlists sorted by probability originally created for password generation and testing. |
#### :globe_with_meridians: Wireless Testing
Used for intrusion detection and wifi attacks.
| Tool | Language | Support | Description |
| ----------- |-------------------------|----------|----------------|
| Aircrack | C | Linux/Windows/macOS | WiFi security auditing tools suite. |
| bettercap | Go | Linux/Windows/macOS/Android | bettercap is the Swiss army knife for 网络 attacks and monitoring. |
| WiFi Pumpkin | Python | Linux/Windows/macOS/Android | 框架 for Rogue Wi-Fi Access Point Attack. |
| Airgeddon | Shell | Linux/Windows/macOS | This is a multi-use bash script for Linux systems to audit wireless networks. |
| Airbash | C | Linux/Windows/macOS | A POSIX-compliant, fully automated WPA PSK handshake capture script aimed at penetration testing. |
#### :wrench: Exploitation Tools
Acesss systems and data with ser exploits.
| 工具 | Language | Support | Description |
| ------------------------------------------------------- | ---------- | --------------------- | ------------------------------------------------------------ |
| SQLmap | Python | Linux/Windows/macOS | Automatic SQL injection and 数据库 takeover 工具. |
| XSStrike | Python | Linux/Windows/macOS | Ad XSS detection and exploitation suite. |
| Commix | Python | Linux/Windows/macOS | Automated All-in-One OS command injection and exploitation 工具. |
| Nuclei | Go | Linux/Windows/macOS | Fast and customisable scanner based on simple YAML based DSL. |
#### :busts_in_silhouette: Sniffing & Spoofing
Listen to 网络 traffic or fake a 网络 entity.
| Tool | Language | Support | Description |
| ----------- |-------------------------|----------|----------------|
| Wireshark | C/C++ | Linux/Windows/macOS | Wireshark is a 网络 协议 analyzer. |
| WiFi Pumpkin | Python | Linux/Windows/macOS/Android | 框架 for Rogue Wi-Fi Access Point Attack. |
| Zarp | Python | Linux/Windows/macOS | A free network attack framework. |
#### :rocket: Web Hacking
Exploit popular CMSs that are hosted online.
| Tool | Language | Support | Description |
| ----------- |-------------------------|----------|----------------|
| WPScan | Ruby | Linux/Windows/macOS | WPScan is a black box WordPress scanner. |
| Droopescan | Python | Linux/Windows/macOS | A plugin-based scanner to identify issues with several CMSs, mainly Drupal & Sil. |
| Joomscan | Perl | Linux/Windows/macOS | Joomla Scanner. |
| Drupwn | Python | Linux/Windows/macOS | Drupal Security Scanner to perform enumerations on Drupal-based web applications. |
| CMSeek | Python | Linux/Windows/macOS | CMS Detection and Exploitation suite - Scan WordPress, Joomla, Drupal and 130 other CMSs. |
#### :tada: Post Exploitation
Exploits for after you ha gained access.
| Tool | Language | Support | Description |
| ----------- |-------------------------|----------|----------------|
| TheFatRat | C | Linux/Windows/macOS | Easy 工具 to generate backdoor and easy 工具 to post exploitation attack like browser attack, dll. |
#### :package: Frameworks
Frameworks are packs of pen testing tools with custom shell na and documentation.
| Tool | Language | Support | Description |
| ----------- |-------------------------|----------|----------------|
| Operati | Python | Linux/Windows/macOS | 框架 based on fingerprint action, this 工具 is used to get information on a website or a enterprise target with multiple modules. |
| Metasploit | Ruby | Linux/Windows/macOS | A penetration testing 框架 for ethical hackers. |
| cSploit | Java | Android | The most complete and ad IT security professional toolkit on Android. |
| radare2 | C | Linux/Windows/macOS/Android | Unix-like reverse engineering 框架 and commandline tools. |
| Wifiphisher | Python | Linux | The Rogue Access Point Framework. |
| Beef | Ja | Linux/Windows/macOS | The Browser Exploitation 框架. It is a penetration testing 工具 that focuses on the web browser. |
| Mobile Security Framework (MobSF) | Python | Linux/Windows/macOS | Mobile Security 框架 (MobSF) is an automated, all-in-one mobile application (Android/iOS/Windows) pen-testing, malware analysis and security assessment 框架 capable of performing static and dynamic analysis. |
| Burp Suite | Java | Linux/Windows/macOS | Burp Suite is a leading range of cybersecurity tools, brought to you by PortSwigger. This tool is not free and open source |
(Table of Contents)
Additional resources
Books / Manuals
Warning : I haven't read them all so do not consider I am recommending as I liked them. They just seem to provide useful resources.
Discussions
Security Ad
Challenges
(Table of Contents)
License
This repository is under MIT license.
(Table of Contents)
项目信息
开发语言:未知
Star 数:15632
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A collection of hacking tools, resources and references to practice ethical hacking.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | hacker-roadmap - 一系列黑客工具、资源和推荐信 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:01:48 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 457 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |