 黑客技术
点击放大
项目说明

![Donate]()
![GitHub tag (latest SemVer)]()
![GitHub All Releases]()
![gitlocalized]()
Detect It Easy (DiE) is a cross-platform 工具 for file identification and static inspection, used by malware analysts, cybersecurity experts, and reverse engineers. It combines nati parsers with an extensible DiE-JS analysis layer, supporting both compact signatures and multi-stage static analysis across Windows, Linux, and MacOS.
🚀 Getting started
> [!WARNING]
> detectiteasy.com is not affiliated with the Detect It Easy project or its official website. Do not trust it as an official 源码 or use it to download DiE. Use only the release links provided in this repository.
!Screenshot
💡 Why use Detect It Easy?
Detect It Easy combines format-aware parsing, signature matching, and programmable analysis for malware analysis, reverse engineering, and digital forensics. DiE-JS modules can use parsed structures and low-le primitives to implement bounded algorithms while keeping detection policy re in the 数据库.
!Screenshot
Key ad:
🧠 Heuristic engine
PE heuristic 引擎: analysis beyond a signature match
A signature can tell you what a file resembles. The Generic Heuristic Analysis 引擎 (__GenericHeuristicAnalysis_By_DosX.7.sg) goes further: it reports concrete structural and beha anomalies together with the e behind them. The PE heuristic 引擎 is created and maintained by DosX.
> [!NOTE]
> DiE-JS is the implementation language of this analysis 引擎, not a shorthand for a few nati calls. The native DiE core supplies format parsing, bounded reads, address translation, searching, and disassembly primitives. The PE heuristic 引擎 builds analysis algorithms on those primitives: it selects candidates, maintains state, tra bounded control flow, relationships across structures, rejects benign explanations, correlates independent e, and reconciles results.
Heuristic analysis is not merely a fallback used when signatures fail. When enabled, it runs as a separate higher-le 引擎 and can corroborate, qualify, or reject earlier 数据库 results while keeping every heuristic conclusion marked.
With heuristic scanning enabled, the PE heuristic 引擎 makes a series of specialized passes o and managed images. The file is ne. Instead, the 引擎 works with headers, data directories, sections, imports, exports, resources, .NET metadata, bytecode, o, debug records, and reachable startup 代码 rooted at the entry point. The same co extends to DLL initialization 代码, closing a common blind spot when protected or suspicious behavior begins inside a library rather than an application. This makes it useful both when an exact signature is known and when a sample has been modified enough to evade ordinary identification.
The PE heuristic 引擎's nati analysis combines cached linear disassembly with bounded tra of reachable startup 代码 and purpose-built state machines. It tracks the register, flag, stack, address-pro, and instruction-boundary facts required by each rule without pretending to be a sandbox or full CPU emulator. This allows DiE to expose opaque and degenerate branches, synthetic and indirect transfers, o instruction streams, position-independent and self-modifying stubs, bitstream unpackers, anti-analysis probes, and irregular control flow used by polymorphic packers and protectors. The checks remain effecti register substitution, neutral padding, equi arithmetic forms, and bounded reordering of independent instructions commonly produced by commercial generators and private cryptors.
For managed 代码, the PE heuristic 引擎 uses an internal MSIL opcode model to build operand-aware bytecode patterns for indirect calls and function pointers, control-flow transformations, arithmetic mutations, invalid instruction sequences, and other forms of obfuscation. It is not a CLR emulator, but it allows the 引擎 to reason about executable IL patterns instead of treating a managed assembly as little more than metadata and strings.
Much of the analysis comes from joining e across layers. The 引擎 can relate identity to Authenticode state, Rich build metadata, runtime model, and detected protection; cross-check the file-system extension; interpret mangled import and export symbols used by MSVC, GNU/MinGW, Borland, and Swift; and recognize fingerprints left by dumpers, unpackers, and PE reconstructors. Nati are architecture-aware across x86/x64 and the ARM family, while security-mitigation flags are checked as meaningful combinations rather than isolated bits.
A single scan may independently identify a known protector, recognize its characteristic section layout, describe entry-point transformations, reco or 游戏-引擎 pro, and associate licensing metadata. These findings come from separate analysis paths; no single backend predicate produces the complete report.
These are the main passes rather than a complete in of every check:
#### Code, protection, and e
<details>
<summary>(click) 🧩 <strong>.NET obfuscation</strong></summary>
</details>
<details>
<summary>(click) 🕵️ <strong>.NET anti-analysis</strong></summary>
</details>
<details>
<summary>(click) 🛡️ <strong>Nati</strong></summary>
PEB and debug-register access, Trap Flag tricks, low-le and probes, pri instructions, direct syscalls, and other attempts to detect or disrupt analysis before the main program begins.</details>
<details>
<summary>(click) 🧱 <strong>Nati</strong></summary>
Call/Pop and FPU-based position recovery, self-modifying stubs, bitstream unpackers, opaque branches, and irregular polymorphic control flow.RET-based transfers are covered as part of the same startup-flow analysis.IAT/EAT, image flags, linker , and other structural signals.</details>
<details>
<summary>(click) 📦 <strong>Packers and protectors</strong></summary>
RunPE-like behavior, compression and crypto clues, o, high entropy, embedded PE files, and damaged unpacking results.</details>
<details>
<summary>(click) 🔑 <strong>Licensing / DRM</strong></summary>
</details>
#### Structure, pro, and triage
<details>
<summary>(click) 🩺 <strong>Format integrity</strong></summary>
IAT/EAT/resources, CLR metadata and strings, and Authenticode placement are checked for damage or tampering.WIN_CERTIFICATE entries.Corrupted data also states the impact: Uncritical covers damage limited to optional metadata, Degraded marks structural inconsistencies that may leave the image operational, and Critical identifies damage to structures required for reliable loading or execution.</details>
<details>
<summary>(click) 🧾 <strong>Debug leftovers</strong></summary>
</details>
<details>
<summary>(click) ☣️ <strong>Malware-related patterns</strong></summary>
</details>
<details>
<summary>(click) 🛠️ <strong>Toolchain / platform</strong></summary>
</details>
<details>
<summary>(click) 🏷️ <strong>Filename anomalies</strong></summary>
.bpl as Borland Package, .xll as Microsoft Excel Add-In, .arx as AutoCAD ObjectARX Module, or .wcx as Total Commander Packer Plug-In—while missing, custom, or misleading extensions, application images carrying a .dll suffix, and DLL images presented as .exe files are reported separately.</details>
This is not a black-box malware score. DiE produces a practical e map for triage: what probably built the file, whether the image looks original, damaged, dumped, or reconstructed, which protection or DRM may explain its structure, and which artifacts deser next. A heuristic result is a lead, not automatic proof of malicious intent. scan messages keep general, managed-代码, and instruction-deri separated as [HEUR/Any], [HEUR/.NET], and [HEUR/EMU]. Use --heuristicscan together with -- to see the fullest report.
Malware clues without pretending to be an antivirus
DiE is not an antivirus, and the PE heuristic 引擎 is not designed to declare a file safe. It provides no real-time protection or disinfection, and a clean report only means that the enabled rules did not find the static e they know how to recognize. Reputation services, an antivirus, dynamic analysis, and manual reverse engineering still answer different questions.
What DiE can do is expose a surprisingly broad range of threat-related clues while the file is still on disk. The examples below are only a small part of the actual rule set, not a complete catalogue. The heuristic 引擎 e faster than this README and new families, markers, and cross-checks are added regularly.
MZ match. Other payload and build anomalies are covered as well.These are explainable static detections built from entry-point 代码, import fingerprints, metadata, strings, resources, section structure, and other relationships inside the image. They are leads, but they are not a promise of complete malware-family co: modified samples may evade a rule, and an unusual clean program may share part of a suspicious pattern.
Heuristic results stay
Heuristic findings are ne mixed into ordinary signature matches. Every result produced by the heuristic layer is kept separate and marked with (Heur), so it is always clear which conclusion came from an exact rule and which one was inferred from a combination of e.
The 引擎 does more than append extra lines. In a few deliberate cases it can reject a misleading result from the main signature 数据库 and replace it with a more precise heuristic conclusion. Programming-language detection is a typical example: a compiler signature may suggest C or C++, while stronger structural and runtime e identifies Rust. The replacement still carries (Heur) and ne itself off as an exact signature match. The same reconciliation mechanism is used to suppress known fake packer, protector, and dongle signatures left behind by obfuscators.
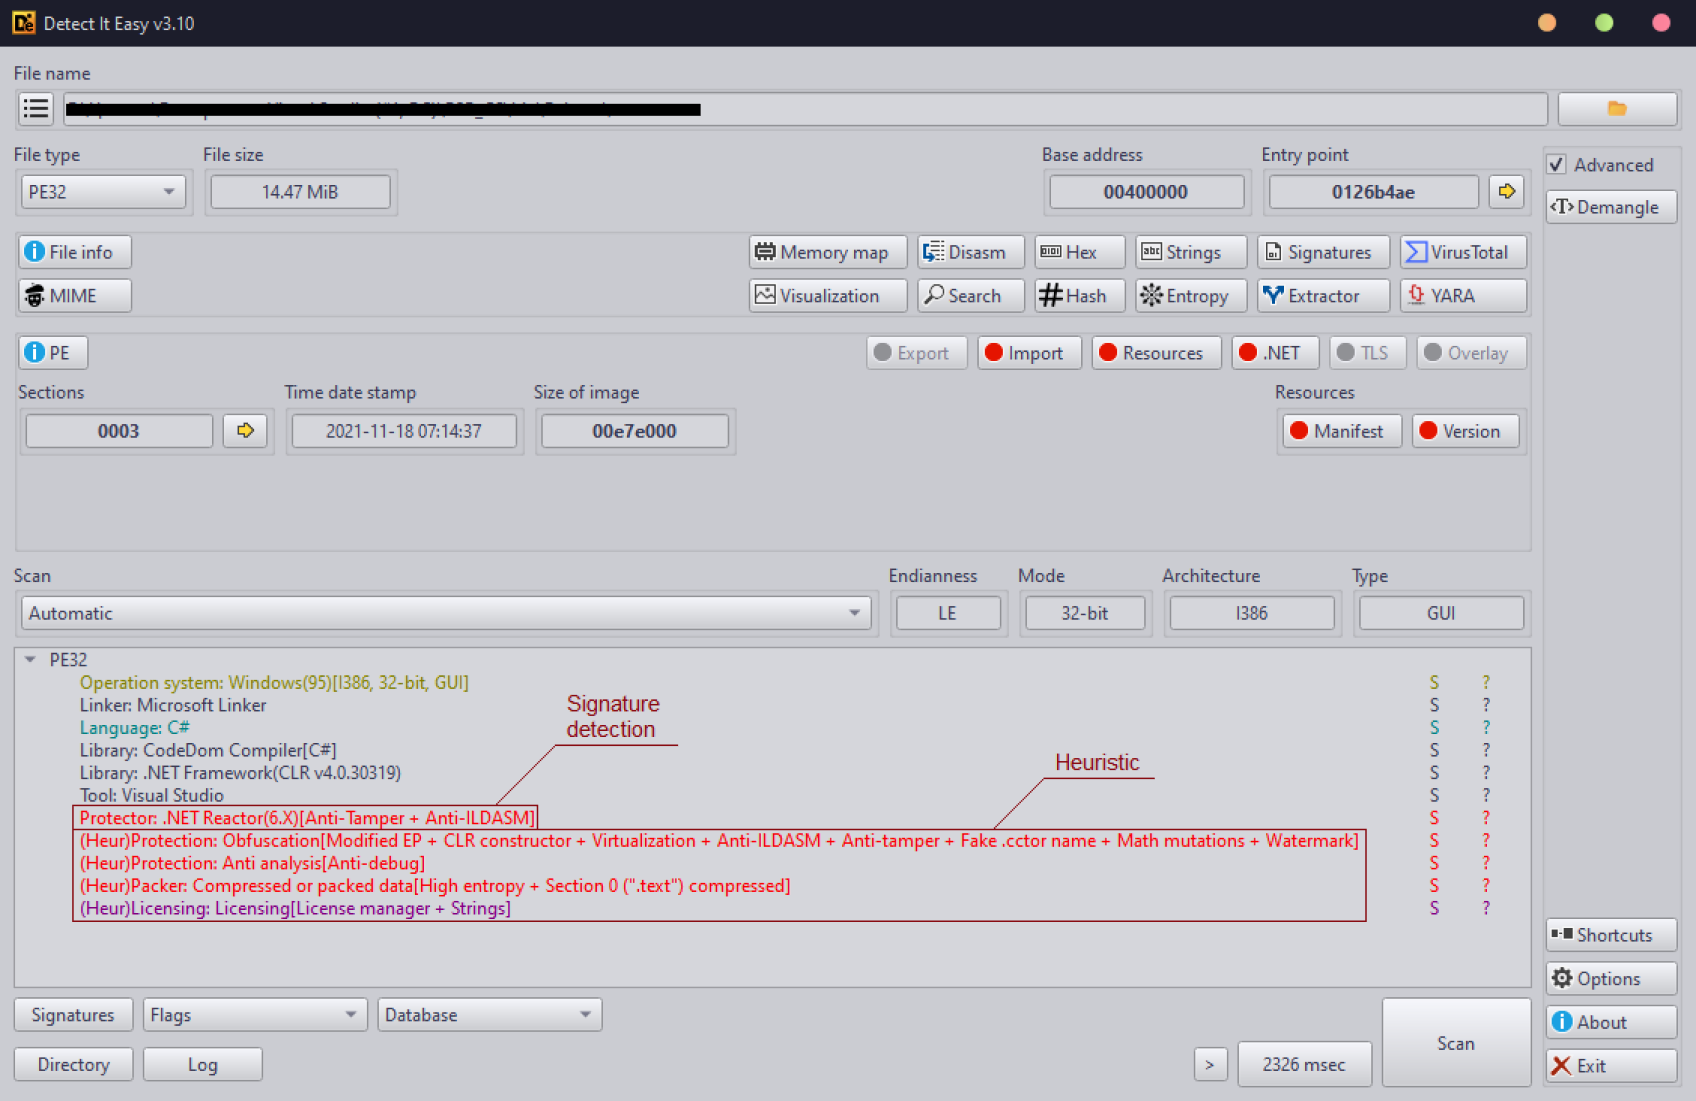
A protected .NET sample may produce a report like this:
For a nati, signatures and heuristic e can complement each other while remaining distinct:
Smaller heuristics for e files
The PE heuristic 引擎 is accompanied by smaller heuristic modules for other e file types:
🧰 Several engines under one GUI
The desktop of DiE is not limited to its own scanning 引擎. It brings several independent analyzers into the same interface, each with a different rule model and a different idea of what constitutes a useful match. On a difficult or unfamiliar file, running them in turn can expose details that one 数据库 alone would miss. Their output is complementary rather than a vote: three engines repeating a weak signature do not turn it into proof.
userdb ecosystem. The bundled 数据库 preserves a large amount of historical material imported from the original PEiD rules. It remains useful for reproducing legacy detections, but many signatures are noisy by modern standards and can produce con false positives, so its results should be treated as secondary e.🧩 Anatomy of a minimal detection rule
DiE 数据库 entries are DiE-JS modules ranging from compact signatures to stateful, multi-stage format analyzers. The example below intentionally demonstrates only the result contract of a minimal standalone rule; it is not representative of the PE heuristic 引擎.
A typical standalone rule declares the kind of result it produces, inspects the current file through the format API, fills optional result fields, and returns the 引擎-built result:
The result are supplied by the DiE 引擎 and must not be redeclared:
| Field | Purpose |
| ----------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| bDetected | Marks the rule as matched. This is the field a normal rule must set when its conditions succeed. |
| sName | O the default name from meta() when the exact is only known at runtime. |
| s | , build, generation, or another short value. |
| sOptions | Architecture, mode, modification state, or other useful qualifiers. |
| sLang | Adds a programming-language result. It is intentionally uncommon, used mostly by compiler rules, and con assigned at the end of detect(), immediately before the blank line preceding return result();. |
| sType | Rare runtime o for the result category; reserve it for multi-purpose modules. |
meta("type", "name") supplies the normal result category and default name. Optional shared helpers are loaded with includeScript("module") between meta() and detect(). Simple rules finish with return result();; keep one empty line immediately before it.
Before submitting a rule or script module, follow the complete DiE-JS 代码-formatting standard.
Before writing a real rule
The skeleton abo syntax and result construction only. DiE determines the file class first and then runs the rules from the matching directory, so format-specific logic belongs beside that format: PE rules use db/PE, ELF rules use db/ELF, and so on. db/Binary is intended for unclassified or genuinely format-independent data, not as a shortcut for 代码 that belongs to a more specific parser.
The scripting API is documented in help. Start with the global functions, the common Binary API, and the signature-pattern reference, then use the class reference for the format being inspected: PE, .NET metadata, ELF, Mach-O, or another document from the same directory.
DiE byte signatures are a small pattern language embedded inside Ja strings. Hex bytes match literally, .. and ?? are byte wildcards, text is written inside single quotes, and $/# forms describe relative or address-dependent . They are not regular expressions. The complete syntax and examples live in the signature reference.
Rules can inspect the scan mode with isHeuristicScan(), isDeepScan(), isAggressi(), and is(). These calls reflect options selected by the user; they do not make an unnecessarily expensive rule acceptable. E 代码 must use cheap structural gates and antipatterns before bounded signature searches.
Repository placement also carries a quality meaning. db is the re main database. db_extra contains rules that were not approved for the main 数据库 and is explicitly not recommended as a quality or performance reference. dbs_min is generated output and must not be edited by hand.
Finally, a rule that works on one private sample is not yet maintainable co. The contribution requirements require reproducible samples, expected DiE output, independently checkable sources, and relevant false-positi. The same document explains the performance requirements that are enforced during review.
📄 Supported file types
Detect It Easy supports a wide range of executable and archi, including:
And that's not all... The list is expanding as the 工具 is updated
Unknown formats undergo heuristic analysis, pro identification for both known and unrecognized files.
🔑 Key features
📥 Installation
📦 Install managers
- Chocolatey
- Microsoft Store
- Parrot OS: Package name detect-it-easy
- Arch Linux: AUR package detect-it-easy-git
- openSUSE: OBS
- REMnux: Malware analysis distribution
![Packaging status]()
> [!NOTE]
> Use Detect It Easy bot via to quickly check files:
⚙️ Build from source
See the BUILD.md for detailed instructions.
🐳 Docker installation
Run DiE in a Docker container:
🖥️ Usage
Detect It Easy offers three :
For detailed usage, refer to the RUN.md.
🔎 Example use cases
💬 Our community
👋 Hello! / Привет! Welcome to the Detect It Easy community!
Ha, ideas, or just want to chat? Here's where to find us:
🏆 Special thanks
🤝 Thanks to all contributors
<a href="
<img src=" />
</a>
---
!Mascot
<!-- Dinosaur -->
<!--
. - ~ ~ ~ - .
.. _ .-~ ~-.
//| \ ..~ .
|| | } } / \ \
(\ \\ \~^..' | } \
\.-~ o / } | / \.
(__ | / | /
- - ~ ~ -._| /_ - ~ ~ ^| /- _ .
| / | / ~-. ~- _
|_____| |_____| ~ - . _ _~_-_
(Grr-r-r!)
-->
项目信息
开发语言:Ja
Star 数:11632
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Program for determining types of files for Windows, Linux and MacOS.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | 轻松检测 - 用于确定Windows文件类型的程序 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:01:58 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 359 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |