 黑客技术
点击放大
项目说明
RedTeam-Tools
<p align="center">
<img src=" height="300">
</p>
This github repository contains a collection of 150+ tools and resources that can be useful for red teaming acti.
Some of the tools may be specifically designed for red teaming, while others are more general-purpose and can be adapted for use in a red teaming context.
> 🔗 If you are a Blue Teamer, check out BlueTeam-Tools
> Warning
>
> *The materials in this repository are for informational and educational purposes only. They are not intended for use in any illegal acti.*
> Note
>
> *Hide 工具 List headings with the arrow.*
>
> *Click 🔙 to get back to the list.*
Tool List
<details open>
<summary><b>Red Team Tips</b> 19 tips</summary>
<ul>
<ul>
<li><b><a href="#impromouse-mo">Improved HTML smuggling with mouse mo</a></b><i> </i></li>
<li><b><a href="#google-translate-for-phishing">Google translate for phishing</a></b><i> </i></li>
<li><b><a href="#hiding-the-local-admin-account">Hiding the local admin account</a></b><i> </i></li>
<li><b><a href="#cripple-windows-defender-by-deleting-signatures">Cripple windows defender by deleting signatures</a></b><i> </i></li>
<li><b><a href="#enable-multiple-rdp-sessions-per-user">Enable multiple RDP sessions per user</a></b><i> </i></li>
<li><b><a href="#sysinternals-psexecexe-local-alternative">Sysinternals PsExec.exe local alternative</a></b><i> </i></li>
<li><b><a href="#linner">Live off the land port scanner</a></b><i> </i></li>
<li><b><a href="#proxy-aware-powershell-downloadstring">Proxy aware PowerShell DownloadString</a></b><i> </i></li>
<li><b><a href="#looking-for-internal-endpoints-in-browser-bookmarks">Looking for internal endpoints in browser bookmarks</a></b><i> </i></li>
<li><b><a href="#query-dns-records-for-enumeration">Query DNS records for enumeration</a></b><i> </i></li>
<li><b><a href="#unquoted-serup">Unquoted service paths without PowerUp</a></b><i> </i></li>
<li><b><a href="#bypass-a-disabled-command-prompt-with-k">Bypass a disabled command prompt with /k</a></b><i> Martin Sohn Christensen</i></li>
<li><b><a href="#stop-windows-defender-deleting-mimikatzexe">Stop windows defender deleting mimikatz.exe</a></b><i> </i></li>
<li><b><a href="#check-if-you-are-in-a-">Check if you are in a machine</a></b><i> </i></li>
<li><b><a href="#enumerate-applocker-rules">Enumerate AppLocker rules</a></b><i> </i></li>
<li><b><a href="#cmd-shortcut-with-6-pixels-">CMD shortcut with 6 pixels </a></b><i> PenTestPartners</i></li>
<li><b><a href="#link-spoofing-with-preethod">Link spoofing with Pre Ja method</a></b><i> </i></li>
<li><b><a href="#check-smb-firewall-rules-with-responder">Check SMB firewall rules with Responder</a></b><i> </i></li>
<li><b><a href="#disable-aspend">Disable AV with SysInternals PsSuspend</a></b><i> @0gtweet</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Reconnaissance</b> 24 tools</summary>
<ul>
<ul>
<li><b><a href="#spiderfoot">spiderfoot</a></b><i> Automated OSINT and attack surface mapping</i></li>
<li><b><a href="#reconftw">reconftw</a></b><i> Automated subdomain and recon 工具</i></li>
<li><b><a href="#subzy">subzy</a></b><i> Subdomain takeo checker</i></li>
<li><b><a href="#smtp-user-enum">smtp-user-enum</a></b><i> SMTP user enumeration</i></li>
<li><b><a href="#crtsh---httprobe---eyewitness">crt.sh -> httprobe -> EyeWitness</a></b><i> Automated domain screenshotting</i></li>
<li><b><a href="#jsendpoints">jsendpoints</a></b><i> Extract page DOM links</i></li>
<li><b><a href="#nuclei">nuclei</a></b><i> scanner</i></li>
<li><b><a href="#certsniff">certSniff</a></b><i> Certificate transparency log keyword sniffer</i></li>
<li><b><a href="#gobuster">gobuster</a></b><i> Website path brute force</i></li>
<li><b><a href="#feroxbuster">feroxbuster</a></b><i> Fast content discovery 工具 written in Rust</i></li>
<li><b><a href="#cloudbrute">CloudBrute</a></b><i> Cloud infrastructure brute force</i></li>
<li><b><a href="#dnsrecon">dnsrecon</a></b><i> Enumerate DNS records</i></li>
<li><b><a href="#shodanio">Shodan.io</a></b><i> Public facing system knowledge base</i></li>
<li><b><a href="#aort">AORT (All in One Recon 工具)</a></b><i> Subdomain enumeration</i></li>
<li><b><a href="#spoofcheck">spoofcheck</a></b><i> SPF/DMARC record checker</i></li>
<li><b><a href="#awsbucketdump">AWSBucketDump</a></b><i> S3 bucket enumeration</i></li>
<li><b><a href="#githar">GitHar</a></b><i> GitHub credential searcher</i></li>
<li><b><a href="#trufflehog">truffleHog</a></b><i> GitHub credential scanner</i></li>
<li><b><a href="#dismap">Dismap</a></b><i> Asset discovery/identification</i></li>
<li><b><a href="#enum4linux">enum4linux</a></b><i> Windows/samba enumeration</i></li>
<li><b><a href="#skanuvaty">skanuvaty</a></b><i> Dangerously fast dns/网络/port scanner</i></li>
<li><b><a href="#metabigor">Metabigor</a></b><i> OSINT 工具 without API</i></li>
<li><b><a href="#gitrob">Gitrob</a></b><i> GitHub sensiti scanner</i></li>
<li><b><a href="#gowitness">gowitness</a></b><i> Web screenshot utility using Chrome Headless</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Resource De</b> 12 tools</summary>
<ul>
<ul>
<li><b><a href="#remoteinjector">remoteinjector</a></b><i> Inject remote template link into word document</i></li>
<li><b><a href="#chimera">Chimera</a></b><i> PowerShell obfuscation</i></li>
<li><b><a href="#msfvenom">msfvenom</a></b><i> Payload creation</i></li>
<li><b><a href="#shellter">Shellter</a></b><i> Dynamic shellcode injection 工具</i></li>
<li><b><a href="#freeze">Freeze</a></b><i> Payload creation (circum EDR)</i></li>
<li><b><a href="#wordsteal">WordSteal</a></b><i> Steal NTML hashes with Microsoft Word</i></li>
<li><b><a href="#ntapi-undocumented-functions">NTAPI Undocumented Functions</a></b><i> Windows NT Kernel, Native API and drivers</i></li>
<li><b><a href="#kernel-callback-functions">Kernel Callback Functions</a></b><i> Undocumented Windows APIs</i></li>
<li><b><a href="#offensivevba">OffensiveVBA</a></b><i> Office macro 代码 execution and e techniques</i></li>
<li><b><a href="#wsh">WSH</a></b><i> Wsh payload</i></li>
<li><b><a href="#hta">HTA</a></b><i> Hta payload</i></li>
<li><b><a href="#vba">VBA</a></b><i> Vba payload</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Initial Access</b> 10 tools</summary>
<ul>
<ul>
<li><b><a href="#credmaster">CredMaster</a></b><i> CredKing password spraying 工具</i></li>
<li><b><a href="#tre">TRE</a></b><i> Password sprayer with threading</i></li>
<li><b><a href="#evilqr">evilqr</a></b><i> QRLJacking phishing PoC</i></li>
<li><b><a href="#cupp">CUPP</a></b><i> Common User Passwords Profiler (CUPP)</i></li>
<li><b><a href="#bash-bunny">Bash Bunny</a></b><i> USB attack 工具</i></li>
<li><b><a href="#e">E</a></b><i> Phishing campaign 框架</i></li>
<li><b><a href="#social-engineer-toolkit-set">The Social-Engineer Toolkit</a></b><i> Phishing campaign 框架</i></li>
<li><b><a href="#hydra">Hydra</a></b><i> Brute force 工具</i></li>
<li><b><a href="#squarephish">SquarePhish</a></b><i> OAuth/QR 代码 phishing 框架</i></li>
<li><b><a href="#king-phisher">King Phisher</a></b><i> Phishing campaign 框架</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Execution</b> 13 tools</summary>
<ul>
<ul>
<li><b><a href="#responder">Responder</a></b><i> LLMNR, NBT-NS and MDNS poisoner</i></li>
<li><b><a href="#secretsdump">secretsdump</a></b><i> Remote hash dumper</i></li>
<li><b><a href="#e">e</a></b><i> WinRM shell</i></li>
<li><b><a href="#donut">Donut</a></b><i> In-memory .NET execution</i></li>
<li><b><a href="#macro_pack">Macro_pack</a></b><i> Macro obfuscation</i></li>
<li><b><a href="#powersploit">PowerSploit</a></b><i> PowerShell script suite</i></li>
<li><b><a href="#rubeus">Rubeus</a></b><i> Acti hack 工具</i></li>
<li><b><a href="#sharpup">SharpUp</a></b><i> Windows identifier</i></li>
<li><b><a href="#sqlrecon">SQLRecon</a></b><i> Offensi toolkit</i></li>
<li><b><a href="#ultimateapplockerbypasslist">UltimateAppLockerByPassList</a></b><i> Common AppLocker Bypass Techniques</i></li>
<li><b><a href="#starfighters">StarFighters</a></b><i> Ja and Based Empire Launcher</i></li>
<li><b><a href="#demiguise">demiguise</a></b><i> HTA encryption 工具</i></li>
<li><b><a href="#powerzure">PowerZure</a></b><i> PowerShell 框架 to assess Azure security</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Persistence</b> 4 tools</summary>
<ul>
<ul>
<li><b><a href="#impacket">Impacket</a></b><i> Python script suite</i></li>
<li><b><a href="#empire">Empire</a></b><i> Post-exploitation 框架</i></li>
<li><b><a href="#sharpersist">SharPersist</a></b><i> Windows persistence toolkit</i></li>
<li><b><a href="#ligolo-ng">ligolo-ng</a></b><i> Tunneling 工具 that uses a TUN interface</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Pri Escalation</b> 11 tools</summary>
<ul>
<ul>
<li><b><a href="#crassus">Crassus</a></b><i> Windows pri escalation discovery 工具</i></li>
<li><b><a href="#linpeas">LinPEAS</a></b><i> Linux pri escalation</i></li>
<li><b><a href="#winpeas">WinPEAS</a></b><i> Windows pri escalation</i></li>
<li><b><a href="#linux-smart-enumeration">linux-smart-enumeration</a></b><i> Linux pri escalation</i></li>
<li><b><a href="#certify">Certify</a></b><i> Acti pri escalation</i></li>
<li><b><a href="#get-gpppassword">Get-GPPPassword</a></b><i> Windows password extraction</i></li>
<li><b><a href="#sherlock">Sherlock</a></b><i> PowerShell pri escalation 工具</i></li>
<li><b><a href="#watson">Watson</a></b><i> Windows pri escalation 工具</i></li>
<li><b><a href="#impulsi">Impulsi</a></b><i> DLL Hijack 工具</i></li>
<li><b><a href="#adfsdump">ADFSDump</a></b><i> AD FS dump 工具</i></li>
<li><b><a href="#beroot">BeRoot</a></b><i> Multi OS Pri Escalation Project</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Defense E</b> 8 tools</summary>
<ul>
<ul>
<li><b><a href="#in">In</a></b><i> Script obfuscator</i></li>
<li><b><a href="#veil">Veil</a></b><i> Metasploit payload obfuscator</i></li>
<li><b><a href="#sharpblock">SharpBlock</a></b><i> EDR bypass point execution pre</i></li>
<li><b><a href="#alcatraz">Alcatraz</a></b><i> 界面 x64 binary obfuscator</i></li>
<li><b><a href="#mangle">Mangle</a></b><i> Compiled executable manipulation</i></li>
<li><b><a href="#amsi-fail">AMSI Fail</a></b><i> PowerShell snippets that break or disable AMSI</i></li>
<li><b><a href="#scarecrow">ScareCrow</a></b><i> Payload creation 框架 designed around EDR bypass</i></li>
<li><b><a href="#moonwalk">moonwalk</a></b><i> Linux system log and filesystem timestamp remover</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Credential Access</b> 11 tools</summary>
<ul>
<ul>
<li><b><a href="#mimikatz">Mimikatz</a></b><i> Windows credential extractor</i></li>
<li><b><a href="#lazagne">LaZagne</a></b><i> Local password extractor</i></li>
<li><b><a href="#hashcat">hashcat</a></b><i> Password hash cracking</i></li>
<li><b><a href="#john-the-ripper">John the Ripper</a></b><i> Password hash cracking</i></li>
<li><b><a href="#scomdecrypt">SCOMDecrypt</a></b><i> SCOM Credential Decryption 工具</i></li>
<li><b><a href="#nanodump">nanodump</a></b><i> LSASS process minidump creation</i></li>
<li><b><a href="#e">e</a></b><i> Tree remake for credential discovery</i></li>
<li><b><a href="#seeyoucm-thief">SeeYouCM-Thief</a></b><i> Cisco phone systems configuration file parsing</i></li>
<li><b><a href="#mailsniper">MailSniper</a></b><i> Microsoft Exchange Mail Searcher</i></li>
<li><b><a href="#sharpchromium">SharpChromium</a></b><i> Cookie, history and sa chromium extractor</i></li>
<li><b><a href="#dploot">dploot</a></b><i> DPAPI looting remotely in Python</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Discovery</b> 6 tools</summary>
<ul>
<ul>
<li><b><a href="#pcredz">PCredz</a></b><i> Credential discovery PCAP/li</i></li>
<li><b><a href="#pingcastle">PingCastle</a></b><i> Acti assessor</i></li>
<li><b><a href="#seatbelt">Seatbelt</a></b><i> Local scanner</i></li>
<li><b><a href="#adrecon">ADRecon</a></b><i> Acti recon</i></li>
<li><b><a href="#adidnsdump">adidnsdump</a></b><i> Acti Integrated DNS dumping</i></li>
<li><b><a href="#sca">sca</a></b><i> Scanning 工具 for sca systems</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Lateral Mo</b> 12 tools</summary>
<ul>
<ul>
<li><b><a href="#crackmapexec">crackmapexec</a></b><i> Windows/Acti lateral mo toolkit</i></li>
<li><b><a href="#wmiops">WMIOps</a></b><i> WMI remote commands</i></li>
<li><b><a href="#powerlessshell">PowerLessShell</a></b><i> Remote PowerShell without PowerShell</i></li>
<li><b><a href="#psexec">PsExec</a></b><i> Light-weight telnet-replacement</i></li>
<li><b><a href="#liquidsnake">LiquidSnake</a></b><i> Fileless lateral mo</i></li>
<li><b><a href="#enabling-rdp">Enabling RDP</a></b><i> Windows RDP enable command</i></li>
<li><b><a href="#upgrading-shell-to-meterpreter">Upgrading shell to meterpreter</a></b><i> Reverse shell impro</i></li>
<li><b><a href="#forwarding-ports">Forwarding Ports</a></b><i> Local port forward command</i></li>
<li><b><a href="#jenkins-re">Jenkins reverse shell</a></b><i> Jenkins shell command</i></li>
<li><b><a href="#adfspoof">ADFSpoof</a></b><i> Forge AD FS security tokens</i></li>
<li><b><a href="#kerbrute">kerbrute</a></b><i> A 工具 to perform Kerberos pre-auth bruteforcing</i></li>
<li><b><a href="#coercer">Coercer</a></b><i> Coerce a Windows 服务端 to authenticate</i></li>
<li><b><a href="#wmiops">WMIOps</a></b><i> WMI remote commands</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Collection</b> 3 tools</summary>
<ul>
<ul>
<li><b><a href="#bloodhound">BloodHound</a></b><i> Acti </i></li>
<li><b><a href="#snaffler">Snaffler</a></b><i> Acti credential collector</i></li>
<li><b><a href="#linwinpwn">linWinPwn</a></b><i> Acti Enumeration and checks</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Command and Control</b> 9 tools</summary>
<ul>
<ul>
<li><b><a href="#liroject">Living Off Trusted Sites Project</a></b><i> Le legitimate domains for your C2</i></li>
<li><b><a href="#havoc">Havoc</a></b><i> Command and control 框架</i></li>
<li><b><a href="#co">Co</a></b><i> Command and control 框架 (.NET)</i></li>
<li><b><a href="#merlin">Merlin</a></b><i> Command and control 框架 (Golang)</i></li>
<li><b><a href="#metasploit-框架">Metasploit 框架</a></b><i> Command and control 框架 (Ruby)</i></li>
<li><b><a href="#pupy">Pupy</a></b><i> Command and control 框架 (Python)</i></li>
<li><b><a href="#brute-ratel">Brute Ratel</a></b><i> Command and control 框架 ($$$)</i></li>
<li><b><a href="#nimplant">NimPlant</a></b><i> C2 implant written in Nim</i></li>
<li><b><a href="#hoaxshell">Hoaxshell</a></b><i> PowerShell reverse shell</i></li>
</ul>
</ul>
</details>
<details open>
<summary><b>Exfiltration</b> 6 tools</summary>
<ul>
<ul>
<li><b><a href="#dnscat2">Dnscat2</a></b><i> C2 via DNS tunneling</i></li>
<li><b><a href="#cloakify">Cloakify</a></b><i> Data transformation for exfiltration</i></li>
<li><b><a href="#pyexfil">PyExfil</a></b><i> Data exfiltration PoC</i></li>
<li><b><a href="#powershell-rat">Powershell RAT</a></b><i> Python based backdoor</i></li>
<li><b><a href="#gd-thief">GD-Thief</a></b><i> Google dri</i></li>
<li><b><a href="#goshs">goshs</a></b><i> Single-binary multi-协议 服务端 for file transfer and exfiltration </i>
</ul>
</ul>
</details>
<details open>
<summary><b>Impact</b> 4 tools</summary>
<ul>
<ul>
<li><b><a href="#conti-pentester-guide-leak">Conti Pentester Guide Leak</a></b><i> Conti ransomware group affilate toolkit</i></li>
<li><b><a href="#slowloris">SlowLoris</a></b><i> Simple denial of service</i></li>
<li><b><a href="#usbkill">usbkill</a></b><i> Anti-forensic kill-switch</i></li>
<li><b><a href="#keytap">Keytap</a></b><i> Get pressed keyboard keys from typing audio</i></li>
</ul>
</ul>
</details>
Red Team Tips
====================
*Learn from Red Teamers with a collection of Red Teaming Tips. These tips cover a range of tactics, tools, and methodologies to improve your red teaming abilities.*
🔙Improved HTML smuggling with mouse mo
Description: *'Qakbot added an E for mouse mo to the HTML smuggling attachment for anti e in sandbox's the zip wont drop.'*
Credit:
Link: Twitter
🔙Google translate for phishing
Description: *Successful phishing page credential stealing being proxied via the google translate page view functionality.*
Credit:
Link: Twitter
🔙Hiding the local admin account
Description: *'Creating accounts is risky when e blue, but when creating a local admin, use some cute sorcery in the registry to hide it.'*
Credit:
Link: Twitter
🔙Cripple windows defender by deleting signatures
Description: *'A bit messy, but if Windows Defender is causing you a big headache, rather than disabling it (which alerts the user), you should just neuter it by deleting all the signatures.'*
Credit:
Link: Twitter
🔙Enable multiple RDP sessions per user
Description: *'Sometimes you want to log in to a host via RDP or similar, but your user has an acti. Enable multiple sessions per user.'*
Credit:
Link: Twitter
🔙Sysinternals PsExec.exe local alternative
Description: *'Are you tired of uploading Sysinternals PsExec.exe when doing lateral mo? Windows has a better alternati. Try this instead.'*
Credit:
Link: Twitter
🔙Live off the land port scanner
Description: *'When possible, live off the land rather than uploading tools to machines (for many reasons). PowerShell/.NET help. Ex: simple port scanner in Powershell.'*
Credit:
Link: Twitter
🔙Proxy aware PowerShell DownloadString
Description: *'Most large orgs are using web proxies these days. The standard PowerShell download cradle is not proxy aware. Use this one.'*
Credit:
Link: Twitter
🔙Looking for internal endpoints in browser bookmarks
Description: *'You'd be surprised what you can find out from a user's bookmarks alone. Internal endpoints they can access, for instance.'*
Credit:
Link: Twitter
🔙Query DNS records for enumeration
Description: *'Enumeration is 95% of the 游戏. However, launching tons of scans to e the en is very loud. Why not just ask the DC/DNS 服务端 for all DNS records?'*
Credit:
Link: Twitter
🔙Unquoted service paths without PowerUp
Description: *'Finding unquoted service paths without PowerUp'*
Credit:
Link: Twitter
🔙Bypass a disabled command prompt with /k
Description: *'This command prompt has been disabled by your administrator...' Can usually be seen in en such as kiosks PCs, a quick hacky work around is to use /k via the windows run box. This will carry out the command and then show the restriction message, allowing for command execution.*
Credit: Martin Sohn Christensen
Link: Blog
🔙Stop windows defender deleting mimikatz.exe
Description: *'Are you tired of Windows Defender deleting mimikatz.exe? Try this instead.'*
Credit:
Link: Twitter
🔙Check if you are in a machine
Description: *'Want to know if you are in a Machine? Query the registry Keys and find out!!! If any results show up then you are in a Machine.'*
Credit:
Link: Twitter
🔙Enumerate AppLocker rules
Description: *'AppLocker can be a pain. Enumerate to see how painful'*
Credit:
Link: Twitter
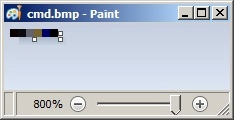
🔙CMD shortcut with 6 pixels
!image
1. Open MSPaint.exe and set the canvas size to: Width=6 and Height=1 pixels
2. Zoom in to make the following tasks easier
3. Using the colour picker, set pixels to (from left to right):
- 1st: R: 10, G: 0, B: 0
- 2nd: R: 13, G: 10, B: 13
- 3rd: R: 100, G: 109, B: 99
- 4th: R: 120, G: 101, B: 46
- 5th: R: 0, G: 0, B: 101
- 6th: R: 0, G: 0, B: 0
4. Save it as 24-bit Bitmap (*.bmp;*.dib)
5. Change its extension from bmp to bat and run.
Description: *'An unusual, yet effecti of gaining a shell by creating a shortcut to cmd.exe by drawing certain colours in Microsoft Paint. Due to the encoding algorithm used to write BMP files, it is possible to dictate ASCII data written into a file by carefully selecting certain RGB colours.'*
Credit: PenTestPartners
Link: Blog
🔙Link spoofing with Pre Ja method
!image
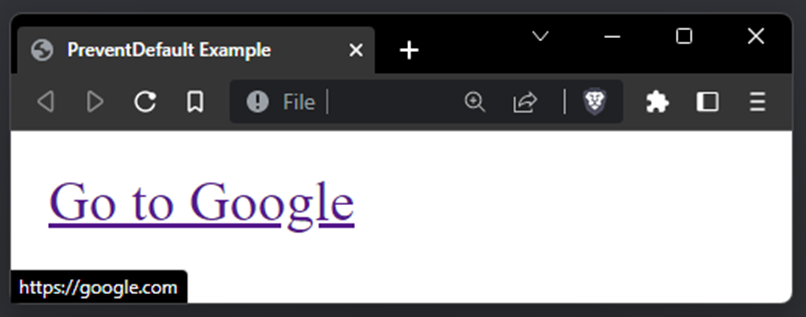
Description: *Threat actors have been obser this technique to trick into clicking spoofed in-page malware download links. Using the Pre Ja method you can spoof the hover link to display a legit link google.com, but once clicked the will be redirected to your malicious link bing.com. Great for getting to download payloads via a controlled site.*
Link: Pre Docs
🔙Check SMB firewall rules with Responder
!image
Description: *'When I do a Compromise Assessment, I often ask the customer if I can do a last quick check: Copy-Item -Path "C:\tmp\" -Destination "\\<ip_running_responder>\c$". If Responder could capture the hash, the firewall allows outgoing SMB connections'*
Credit:
Link: Twitter
🔙Disable AV with SysInternals PsSuspend
!image
Description: *Using the Microsoft Sysinternals 工具 PsSuspend.exe it's possible to suspend some A executables. The Microsoft signed 工具 can be passed the PID or Name of a running service, it will suspend the process via the NtSuspendProcess Windows API.*
Related Blog Post: Bypassing A with PsSuspend.exe
Link: Twitter
Reconnaissance
====================
🔙spiderfoot
SpiderFoot is an open 源码 intelligence (OSINT) automation 工具. It integrates with just about every data 源码 a and utilises a range of methods for data analysis, making that data easy to na.
SpiderFoot can be used offensively (e.g. in a red team exercise or penetration test) for reconnaissance of your target or defensively to gather information about what you or your organisation might ha over the Internet.
Install:
For full installation instructions see here.
Usage:
Lots of usage tutorial here
!spiderfoot
*Image used from
🔙reconftw
reconFTW automates the entire process of reconnaissance for you. It outperforms the work of subdomain enumeration along with checks and obtaining maximum information about your target.
Install:
For full installation instructions see here.
Usage:
For full usage instructions see here.
!reconftw
*Image used from
🔙subzy
Subdomain takeover 工具 which works based on matching response fingerprints from can-i-take-o.
Install:
For full installation instructions see here.
Usage:
!subzy
*Image used from
🔙smtp-user-enum
SMTP user enumeration via VRFY, EXPN and RCPT with cle, retry and reconnect functionality.
Install:
Usage:
!smtp-user-enum
*Image used from
🔙crt.sh -> httprobe -> EyeWitness
I have put together a bash one-liner that:
Usage:
*Note: You must ha, pup and EyeWitness installed and change 'DOMAIN_COM' to the target domain. You are able to run this script concurrently in terminal windows if you ha target root domains*
!image
!image
🔙jsendpoints
A Ja bookmarklet for extracting all webpage endpoint links on a page.
Created by , this Ja 代码 snippet can be used to extract all endpoints (starting with /) from the current webpage DOM including all external script sources embedded on the webpage.
Usage (Bookmarklet)
Create a bookmarklet...
Right click your bookmark barClick 'Add Page'Paste the abo in the 'url' boxClick 'Save'...then visit the page in the browser and click the bookmarklet.
!image
Usage (Console)
Paste the abo into the console window F12 and press enter.
!image
🔙nuclei
Fast scanner that uses .yaml templates to search for specific issues.
Install:
Usage:
!image
🔙certSniff
certSniff is a Certificate Transparency logs keyword watcher I wrote in Python. It uses the certstream library to watch for certificate creation logs that contain keywords, defined in a file.
You can set this running with several keywords relating to your domain, any certificate creations will be recorded and may lead to the discovery of domains you were pre unaware of.
Install:
Usage:
!image
🔙gobuster
Nice 工具 for brute forcing file/folder paths on a website.
Install:
Usage:
!image
🔙feroxbuster
A 工具 designed to perform Forced Browsing, an attack where the aim is to enumerate and access resources that are not referenced by the web application, but are still accessible by an attacker.
Feroxbuster uses brute force combined with a wordlist to search for unlinked content in target directories. These resources may store sensiti about web applications and operational systems, such as 源码 代码, credentials, internal 网络 addressing, etc...
Install: (Kali)
Install: (Mac)
Install: (Windows)
For full installation instructions see here.
Usage:
Full usage examples can be found here.
!image
*Image used from
🔙CloudBrute
A 工具 to find a company (target) infrastructure, files, and apps on the top cloud pro (Amazon, Google, Microsoft, DigitalOcean, Alibaba, Vultr, Linode).
Features:
Install:
Download the latest release for your system and follow the usage.
Usage:
!image
*Image used from
🔙dnsrecon
dnsrecon is a pyhton 工具 for enumerating DNS records (MX, SOA, NS, A, AAAA, SPF and TXT) and can provide a number of new associated hosts to pivot into from a single domain search.
Install:
Usage:
!image
🔙shodan.io
Shodan crawls public infrastructure and displays it in a searchable format. Using a company name, domain name, IP address it is possible to disco systems relating to your target .
!image
🔙AORT
工具 for enumerating subdomains, enumerating DNS, WAF detection, WHOIS, port scan, wayback machine, email har.
Install:
Usage:
!image
🔙spoofcheck
A program that checks if a domain can be spoofed from. The program checks SPF and DMARC records for weak configurations that allow spoofing. Additionally it will alert if the domain has DMARC configuration that sends mail or HTTP requests on failed SPF/DKIM emails.
Domains are spoofable if any of the following conditions are met:
~all or -allp=none or is nonexistentInstall:
Usage:
!image
🔙AWSBucketDump
AWSBucketDump is a 工具 to quickly enumerate AWS S3 buckets to look for interesting files. It's similar to a subdomain bruteforcer but is made specifically for S3 buckets and also has some extra features that allow you to grep for files, as well as download interesting files.
Install:
Usage:
🔙GitHar
Nice 工具 for finding information from GitHub with regex, with the ability to search specific GitHub users and/or projects.
Install:
Usage:
🔙truffleHog
TruffleHog is a 工具 that scans git repositories and looks for high-entropy strings and patterns that may indicate the presence of secrets, such as passwords and API keys. With TruffleHog, you can quickly and easily find sensiti that may have been accidentally committed and pushed to a repository.
Install (Binaries): Link
Install (Go):
Usage:
!image
🔙Dismap
Dismap is an asset discovery and identification 工具. It can quickly identify protocols and fingerprint information such as web/tcp/udp, locate asset types, and is suitable for internal and external networks.
Dismap has a complete fingerprint rule base, currently including tcp/udp/tls 协议 fingerprints and 4500+ web fingerprint rules, which can identify favicon, body, header, etc.
Install:
Dismap is a binary file for Linux, MacOS, and Windows. Go to Release to download the corresponding to run:
Usage:
!image
*Image used from
🔙enum4linux
A 工具 for enumerating information from Windows and Samba systems.
It can be used to gather a wide range of information, including:
Install: (Apt)
Install: (Git)
Usage:
Full usage information can be found in this blog.
!image
*Image used from
🔙skanuvaty
Dangerously fast dns/网络/port scanner, created by Esc4iCEscEsc, written in rust.
You will need a subdomains file. *E.g. Subdomain wordlist by Sublist3r*.
Install:
Download the latest release from here.
Usage:
!image
*Image used from
🔙Metabigor
Metabigor is Intelligence 工具, its goal is to do OSINT tasks and more but without any API key.
Main Features:
Install:
Usage:
!image
*Image used from
🔙Gitrob
Gitrob is a 工具 to help find potentially sensiti pushed to public repositories on Github.
Gitrob will clone repositories belonging to a user or organization down to a configurable depth and iterate through the commit history and flag files that match signatures for potentially sensiti.
The findings will be presented through a web interface for easy browsing and analysis.
Note: *Gitrob will need a Github access token in order to interact with the Github API. Create a personal access token and save it in an en in your .bashrc or similar shell configuration file:*
Install: (Go)
Install: (Binary)
A precompiled is a for each release.
Usage:
!image
*Image used from
🔙gowitness
Gowitness is a website screenshot utility written in Golang, that uses Chrome Headless to generate screenshots of web interfaces using the command line, with a handy report to process results. Both Linux and macOS is supported, with Windows support mostly working.
Install: (Go)
Full installation information can be found here.
Usage:
Full usage information can be found here.
!image
*Image used from
Resource De
====================
🔙remoteInjector
Injects link to remote word template into word document.
This Python-based utility modifies a .docx file’s settings.xml.rels link to a remote hosted .dotm template containing a , executing when the document is opened and macros are enabled.
Related Blog Post
Install:
Usage:
🔙Chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and antivirus solutions. It digests malicious PS1's known to trigger AV and uses string substitution and concatenation to evade common detection signatures.
Install:
Usage:
!image
🔙msfvenom
Msfvenom allows the creation of payloads for operating systems in a wide range of formats. It also supports obfuscation of payloads for A.
Set Up Listener
#### Msfvenom Commands
PHP:
Windows:
Linux:
Java:
HTA:
!image
🔙Shellter
Shellter is a dynamic shellcode injection 工具, and the first truly dynamic PE infector e.
It can be used in order to inject shellcode into nati applications (currently 32-bit applications only).
Shellter takes ad of the original structure of the PE file and doesn’t apply any modification such as changing memory access permissions in sections (unless the user wants), adding an extra section with RWE access, and whate look dodgy under an AV scan.
Full README information can be found here.
Install: (Kali)
Install: (Windows)
Visit the download page and install.
Usage:
Just pick a legit binary to backdoor and run Shellter.
Some nice tips can be found here.
Lots of community usage demos can be found here.
!image
*Image used from
🔙Freeze
Freeze is a payload creation 工具 used for circum EDR security controls to execute shellcode in a stealthy manner.
Freeze utilizes multiple techniques to not only remo EDR hooks, but to also execute shellcode in such a way that it circumvents other endpoint monitoring controls.
Install:
Usage:
!image
*Image used from
🔙WordSteal
This script will create a Microsoft Word Document with a remote image, allowing for the capture of NTML hashes from a remote endpoint.
Microsoft Word has the ability to include images from remote locations, including a remote image hosted on an attacker controlled SMB 服务端. This gives you the opportunity to listen for, and capture, NTLM hashes that are sent when an authenticated opens the Word document and renders the image.
Install:
Usage:
!image
*Image used from
🔙NTAPI Undocumented Functions
This site provides information on undocumented Windows internals, system calls, data structures, and other low-le of the Windows operating system.
It can be a resource for indi who want to explore the internals of Windows for purposes, including analysis, exploit de, and pri escalation.
When de exploits, understanding the internals of the target system is crucial. This site can help develop exploits by le the low-le aspects of Windows.
Usage:
Visit
!image
*Image used from
🔙Kernel Callback Functions
This technical note provides a comprehensive list all the APIs exported by the Windows Kernel, for dri to register callback routines that are invoked by kernel components under circumstances.
Most of these routines are documented in the Windows Driver Kit (WDK) but some of them are for use by in-box drivers.
The undocumented functions are described briefly whereas the documented ones are just listed here for reference.
Usage:
Visit
!image
*Image used from
🔙OffensiveVBA
A collection of offensi, scripts and useful links for achieving 代码 execution and defense e macros.
Usage:
Visit
!image
*Image used from
🔙WSH
Creating payload:
Execute:
🔙HTA
Creating payload:
Execute: Run file
🔙VBA
Creating payload:
Execute: Set function to Auto_Open() in macro enabled document
Initial Access
====================
🔙CredMaster
Launch a password spray / brute force attach AWS passthrough proxies, shifting the requesting IP address for every authentication attempt. This dynamically creates FireProx APIs for more e password sprays.
CredMaster provides a method of running anonymous password sprays against endpoints in a simple, easy to use 工具. The FireProx 工具 provides the rotating request IP, while the base of CredMaster spoofs all other identifying information.
Features:
Install:
For full installation instructions see here.
Usage:
This 工具 requires AWS API access keys, a walkthrough on how to acquire these keys can be found here:
!credmaster
*Image used from
🔙TRE
TRE is a modular password sprayer with threading, SSH proxying, loot modules, and more!
Install:
Usage:
For full usage instructions see here.
!TRE
*Image used from
🔙evilqr
Toolkit demonstrating another approach of a QRLJacking attack, allowing to perform remote account takeover, through sign-in QR 代码 phishing.
It consists of a browser extension used by the attacker to extract the sign-in QR 代码 and a ser, which retrieves the sign-in QR codes to display them on the hosted phishing pages.
Demo video
Install: (Extension)
You can load the extension in Chrome, through Load unpacked feature:
Once the extension is installed, make sure to pin its icon in Chrome's extension toolbar, so that the icon is always .
Install: (Server)
Usage:
1. Run the 服务端 by running the built ser: ./ser/e
2. Open any of the supported websites in your Chrome browser, with installed Evil QR extension:
3. Make sure the sign-in QR 代码 is and click the Evil QR extension icon in the toolbar. If the QR 代码 is recognized, the icon should light up with colors.
4. Open the 服务端's phishing page URL: (default)
!evilqr
*Image used from
🔙CUPP
The most common form of authentication is the combination of a username and a password or passphrase. Passwords can sometimes be guessed profiling the user, such as a birthday, nickname, address, name of a pet or relative, or a common word such as God, lo or password.
That is why CUPP was born.
Install:
Usage:
!cupp
*Image used from
🔙Bash Bunny
The Bash Bunny is a physical USB attack 工具 and multi-function payload delivery system. It is designed to be plugged into a computer's USB port and can be programmed to perform a of functions, including manipulating and exfiltrating data, installing malware, and bypassing security measures.
hackinglab: Bash Bunny – Guide
Hak5 Documentation
Nice Payload Repo
Product Page
!image
🔙E
e + gophish. (GoPhish) Gophish is a powerful, open-源码 phishing 框架 that makes it easy to test your organization's exposure to phishing. (e) Standalone man-in-the-middle attack 框架 used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor authentication
Install:
Usage:
!image
🔙Social Engineer Toolkit (SET)
This 框架 is great for creating campaigns for initial access, 'SET has a number of custom attack that allow you to make a believable attack quickly'.
Install:
Usage:
!image
🔙Hydra
Nice 工具 for logon brute force attacks. Can bf a number of services including SSH, FTP, TELNET, HTTP etc.
Install:
Usage:
!image
🔙SquarePhish
SquarePhish is an ad phishing 工具 that uses a technique combining OAuth Device 代码 authentication flow and QR codes (See PhishInSuits for more about OAuth Device 代码 flow for phishing attacks).
Attack Steps:
Install:
Note: *Before using either module, update the required information in the settings.config file noted with Required.*
Usage (Email Module):
Usage (Ser):
!image
🔙King Phisher
King Phisher is a 工具 that allows attackers to create and send phishing emails to to obtain sensiti.
It includes features like customizable templates, campaign management, and email sending capabilities, making it a powerful and easy-to-use 工具 for carrying out phishing attacks. With King Phisher, atackers can target indi or organizations with targeted and con phishing emails, increasing the chances of success in their attacks.
Install (Linux - Client & Server):
Usage:
Once King Phisher has been installed please follow the wiki page to setup SSH, 数据库 config, SMTP 服务端 etc.
!image
Execution
====================
🔙Responder
Responder is a 工具 for poisoning the LLMNR and NBT-NS protocols on a 网络, to allow for credential capture and arbitrary 代码 execution.
The LLMNR (Link-Local Multicast Name Resolution) and NBT-NS (NetBIOS Name Service) protocols are used by Windows systems to resol to IP addresses on a local 网络. If a hostname cannot be resol these protocols, the system will broadcast a request for the hostname to the local 网络.
Responder listens for these broadcasts and responds with a fake IP address, tricking the requesting system into sending its credentials to the attacker.
Install:
Usage:
Full usage information can be found here.
!image
*Image used from
🔙secretsdump
A utility that is part of the Impacket library that can be used to extract password hashes and other secrets from a Windows system.
It does this by interacting with the Security Account Manager (SAM) 数据库 on the system and extracting the hashed passwords and other information, such as:
Install:
Usage:
!image
*Image used from
🔙e
E is a 工具 that provides a command line interface for Windows Remote Management (WinRM: *A service that allows administrators to remotely execute commands on a Windows machine*).
E allows an attacker to remotely connect to a Windows machine using WinRM and execute arbitrary commands.
Some features include:
Install: (Git)
Install: (Ruby gem)
Alternati instructions can be found here.
Usage:
Full usage documentation can be found here.
!image
*Image used from
🔙Donut
A 工具 for in-memory execution of , JScript, EXE, DLL files and dotNET assemblies. It can be used to load and run custom payloads on target systems without the need to drop files to disk.
Install: (Windows)
To generate the loader template, dynamic library donut.dll, the static library donut.lib and the generator donut.exe. Start an x64 Microsoft Studio De Command Prompt, change to the directory where you cloned the Donut repository and enter the following:
To do the same, except using MinGW-64 on Windows or Linux, change to the directory where you cloned the Donut repository and enter the following:
Install: (Linux)
Usage:
For full usage information, see the donut GitHub Page.
See a recent blog post from The Wover for more info.
!image
🔙Macro_pack
A 工具 used to automatize the obfuscation and generation of Office documents, , shortcuts, and other formats for red teaming.
Install: (Binary)
1. Get the latest binary from
2. Download binary on PC with genuine Microsoft Office installed.
3. Open console, CD to binary dir and call the binary
Install: (Git)
Usage:
!image
🔙PowerSploit
A collection of PowerShell scripts and modules that can be used to achieve a of red teaming objectives.
Some of the features of PowerSploit:
Install: *1. Save to PowerShell modules folder*
First you will need to download the PowerSploit Folder and save it to your PowerShell modules folder.
Your PowerShell modules folder path can be found with the following command:
Install: *2. Install PowerSploit as a PowerShell module*
You will then need to install the PowerSploit module (use the name of the downloaded folder).
Note: *Your PowerShell execution policy might block you, to fix this run the following command.*
Now you can install the PowerSploit module.
Usage:
!image
🔙Rubeus
A 工具 that can be used to perform actions related to Microsoft Acti (AD) en, such as dumping password hashes, creating/deleting users, and modifying user properties.
Some of the features of Rubeus:
Install: (Download)
You can install the unofficial pre-compiled Rubeus binary here.
Install: (Compile)
Rubeus is compatible with Studio 2019 Community Edition. Open the rubeus project .sln, choose "Release", and build.
Usage:
!image
🔙SharpUp
A nice 工具 for checking a endpoint for relating to high integrity processes, groups, hijackable paths, etc.
Install: (Download)
You can install the unofficial pre-compiled SharpUp binary here.
Install: (Compile)
SharpUp is compatible with Studio 2015 Community Edition. Open the SharpUp project .sln, choose "Release", and build.
Usage:
!image
🔙SQLRecon
MS-SQL (Microsoft SQL 服务端) is a relational 数据库 management system de and marketed by Microsoft.
This C# MS-SQL toolkit is designed for offensi and post-exploitation. For detailed usage information on each technique, refer to the wiki.
Install: (Binary)
You can download the latest binary release from here.
Usage:
Full usage information can be found on the wiki.
工具 module usage information can be found here.
!image
*Image used from SQLRecon help page*
🔙UltimateAppLockerByPassList
This resrouce is a collection of the most common and known techniques to bypass AppLocker.
Since AppLocker can be configured in different ways maintains a list of bypasses (that works against the default AppLocker rules) and a list with possible bypass technique (depending on configuration) or claimed to be a bypass by someone.
They also have a list of generic bypass techniques as well as a legacy list of methods to execute through DLLs.
Indexed Lists
!image
*Image used from
🔙StarFighters
A Ja and Based Empire Launcher, which runs within their own embedded PowerShell Host.
Both Launchers run within their own embedded PowerShell Host, so we don't need PowerShell.exe.
This might be usefull when a company is blocking PowerShell.exe and/or is using a Application Whitelisting solution, but does not block running JS/.
Usage:
For the Ja use the following :
For the use the following :
!image
*Image used from
🔙demiguise
The aim of this project is to generate .html files that contain an encrypted HTA file.
The idea is that when your target the page, the key is fetched and the HTA is decrypted dynamically within the browser and pushed directly to the user.
This is an e technique to get round content / file-type inspection implemented by some security-appliances.
Further technical information here.
Install:
Usage:
!image
*Image used from
🔙PowerZure
PowerZure is a PowerShell project created to assess and exploit resources within Microsoft’s cloud platform, Azure. PowerZure was created out of the need for a 框架 that can both perform reconnaissance and exploitation of Azure, AzureAD, and the associated resources.
There is zero reason to ever run PowerZure on a ’s machine. Authentication is done by using an existing accesstoken.json file or by logging in when logging into Azure, meaning you can safely use PowerZure to interact with a ’s cloud instance from your operating machine.
Install:
Usage:
Blog - Attacking Azure, Azure AD, and Introducing PowerZure
!image
*Image used from
Persistence
====================
🔙Impacket
Impacket provides a set of low-le bindings for 网络 protocols, including SMB, Kerberos, and LDAP, as well as higher-le for interacting with 网络 services and performing specific tasks such as dumping password hashes and creating 网络 shares.
It also includes a number of command-line tools that can be used to perform tasks such as dumping SAM databases, enumerating domain trusts, and cracking Windows passwords.
Install:
Install: (With Example Scripts)
Download and extract the package, then na to the install folder and run...
Usage:
Great cheat sheet for Impacket usage.
!image
🔙Empire
Empire is a post-exploitation 框架 that allows you to generate payloads for establishing remote connections with systems.
Once a payload has been executed on a system, it establishes a connection back to the Empire 服务端, which can then be used to issue commands and control the target system.
Empire also includes a number of built-in modules and scripts that can be used to perform specific tasks, such as dumping password hashes, accessing the Windows registry, and exfiltrating data.
Install:
Usage:
Nice usage cheat sheet by HarmJoy.
!image
🔙SharPersist
A Windows persistence toolkit written in C#.
The project has a wiki.
Install: (Binary)
You can find the most recent release here.
Install: (Compile)
-
Install-Package Costura.Fody - 3.3.3-
Install-Package TaskScheduler - 2.8.11Usage:
A full list of usage examples can be found here.
!image
🔙ligolo-ng
Ligolo-ng is a simple, lightweight and fast 工具 that allows pentesters to establish tunnels from a reverse TCP/TLS connection using a tun interface (without the need of SOCKS).
Instead of using a SOCKS proxy or TCP/UDP forwarders, Ligolo-ng creates a userland 网络 stack using Gvisor.
When running the relay/proxy 服务端, a tun interface is used, packets sent to this interface are translated, and then transmitted to the agent remote 网络.
Install: (Download)
Precompiled binaries (Windows/Linux/macOS) are a on the Release page.
Install: (Build)
*Building ligolo-ng (Go >= 1.17 is required):*
Setup: (Linux)
Setup: (Windows)
You need to download the Wintun driver (used by WireGuard) and place the wintun.dll in the same folder as Ligolo (make sure you use the right architecture).
Setup: (Proxy server)
Usage:
*Start the agent on your target () computer (no pri are required!):*
A session should appear on the proxy 服务端.
Use the session command to select the agent.
Full usage information can be found here.
!image
*Image used from
Pri Escalation
====================
🔙Crassus
"Accenture made a 工具 called Spartacus, which finds DLL hijacking opportunities on Windows. Using Spartacus as a starting point, we created Crassus to extend Windows pri escalation finding capabilities beyond simply looking for missing files. The ACLs used by files and directories of pri processes can find more than just looking for missing files to achieve the goal." - Link
Install: (Build)
Crassus was de as a Studio 2019 project. To build Crassus.exe:
1. Open Crassus.sln
2. Press Ctrl+Shift+B on your keyboard
Install: (precompiled)
If you trust running other people's 代码 without knowing what it does, Crassus.exe is provided in this repository.
Usage:
1. In Process Monitor, select the Enable Boot Logging option.
2. Reboot.
3. Once you ha in and Windows has settled, optionally also run scheduled tasks that may be configured to run with pri.
4. Run Process Monitor once again.
5. When prompted, save the boot log.
6. Reset the default Process Monitor filter using Ctrl-R.
7. Save this log file, e.g., to boot.PML. The reason for re-saving the log file is twofold:
1. Older of Process Monitor do not save boot logs as a single file.
2. Boot logs by default will be unfiltered, which may contain extra noise, such as a local-user DLL hijacking in the launching of of Process Monitor itself.
!Crassus
*Image used from
🔙LinPEAS
LinPEAS is a nice pri escalation for finding local privesc routes on Linux endpoints.
Install + Usage:
!image
🔙WinPEAS
WinPEAS is a nice pri escalation for finding local privesc routes on Windows endpoints.
Install + Usage:
!image
🔙linux-smart-enumeration
Linux smart enumeration is another good, less , linux privesc 工具 for Linux.
Install + Usage:
!image
🔙Certify
Certify is a C# 工具 to enumerate and abuse misconfigurations in Acti Certificate Services (AD CS).
Certify is designed to be used in conjunction with other red team tools and techniques, such as Mimikatz and PowerShell, to enable red teamers to perform types of attacks, including man-in-the-middle attacks, impersonation attacks, and pri escalation attacks.
Key features of Certify:
Install: (Compile)
Certify is compatible with Studio 2019 Community Edition. Open the Certify project .sln, choose "Release", and build.
Install: (Running Certify Through PowerShell)
If you want to run Certify in-memory through a PowerShell wrapper, first compile the Certify and base64-encode the resulting assembly:
Certify can then be loaded in a PowerShell script with the following (where "aa..." is replaced with the base64-encoded Certify assembly string):
The Main() method and any arguments can then be invoked as follows:
Full compile instructions can be found here.
Usage:
Full example walkthrough can be found here.
!image
🔙Get-GPPPassword
Get-GPPPassword is a PowerShell script part of the PowerSploit toolkit, it is designed to retrie for local accounts that are created and managed using Group Policy Preferences (GPP).
Get-GPPPassword works by searching the SYS on the domain controller for any GPP files that contain password information. Once it finds these files, it decrypts the password information and displays it to the user.
Install:
Follow the PowerSploit installation instructions from this 工具 sheet.
Usage:
!image
🔙Sherlock
PowerShell script to quickly find missing software patches for local pri escalation .
*Supports:*
Install: (PowerShell)
Usage: (PowerShell)
!image
*Image used from
🔙Watson
Watson is a .NET 工具 designed to enumerate missing KBs and suggest exploits for Pri Escalation .
Great for identifying missing patches and suggesting exploits that could be used to exploit known in order to gain higher pri on the system.
Install:
Using Studio 2019 Community Edition. Open the Watson project .sln, choose "Release", and build.
Usage:
!image
*Image text used from
🔙Impulsi
A C# based 工具 that automates the process of disco and exploiting DLL Hijacks in target binaries.
The discovered Hijacked paths can be weaponized, during an engagement, to evade EDR's.
Install:
- These are DLL files which assist the 工具 to get the confirmation whether the DLL's are been successfully loaded from the identified hijack path
- Compiled from the MalDLL project provided above (or use the precompiled binaries if you trust me!)
- 32Bit dll name should be: maldll32.dll
- 64Bit dll name should be: maldll64.dll
- Install NuGet Package: PeNet -> (Prereq while compiling the Impulsi project)
Note: i & ii prerequisites should be placed in the Impulsi.exe's directory itself.
- Impulsi
- Clone the repository in Studio
- Once project is loaded in Studio go to "Project" --> "Manage NuGet packages" --> Browse for packages and install "PeNet" ->
- Build the project!
- The Impulsi.exe will be inside the bin directory.
- And for Confirmatory DLL's:
- Clone the repository in Studio
- Build the project with x86 and x64
- Rename x86 release as maldll32.dll and x64 release as maldll64.dll
- Setup: Copy the Confirmatory DLL's (maldll32 & maldll64) in the Impulsi.exe directory & then execute Impulsi.exe :))
*Install instructions from
Usage:
Usage examples can be found here.
!image
*Image used from
🔙ADFSDump
A C# 工具 to dump all sorts of goodies from AD FS.
Created by Doug Bienstock while at Mandiant FireEye.
This 工具 is designed to be run in conjunction with ADFSpoof. ADFSdump will output all of the information needed in order to generate security tokens using ADFSpoof.
Requirements:
Install: (Compile)
ADFSDump was built against .NET 4.5 with Studio 2017 Community Edition. Simply open up the project .sln, choose "Release", and build.
Usage: (Flags)
Blog - Exploring the Golden SAML Attack Against ADFS
!image
*Image used from
🔙BeRoot
BeRoot Project is a post exploitation 工具 to check common misconfigurations to find a way to escalate our pri.
The goal of BeRoot is to only output potential pri escalation opportunities and not a endpoint configuration assessment.
This project works on Windows, Linux and Mac OS.
Install: (Linux)
Install: (Windows)
A pre-compiled of BeRoot can be found here.
Usage:
Further information can be found here for:
!image
*Image used from
Defense E
====================
🔙In
A PowerShell v2.0+ compatible PowerShell command and script obfuscator. If a endpoint is able to execute PowerShell then this 工具 is great for creating heavily obfuscated scripts.
Install:
Usage:
!image
🔙Veil
Veil is a 工具 for generating metasploit payloads that bypass common anti-virus solutions.
It can be used to generate obfuscated shellcode, see the official veil 框架 blog for more info.
Install: (Kali)
Install: (Git)
Usage:
Veil creators wrote a nice blog post explaining further ordnance and e command line usage.
!image
🔙SharpBlock
A method of bypassing EDR's acti DLL's by pre entry point execution.
Features:
Install:
Use Studio 2019 Community Edition to compile the SharpBlock binary.
Open the SharpBlock project .sln, choose "Release", and build.
Usage:
Nice PenTestPartners blog post here.
!image
*Image used from
🔙Alcatraz
Alcatraz is a 界面 x64 binary obfuscator that is able to obfuscate different pe files including:
Some supported obfuscation features include:
Install: (Requirements)
Install:
Usage:
Using the GUI to obfuscate a binary:
1. Load a binary by clicking file in the top left corner.
2. Add functions by expanding the Functions tree. (You can search by putting in the name in the searchbar at the top)
3. Hit compile (Note: *Obfuscating lots of functions might take some seconds*)
!image
*Image used from
🔙Mangle
Mangle is a 工具 that manipulates aspects of compiled executables (.exe or DLL).
Mangle can remo Indicators of Compromise (IoC) based strings and replace them with random characters, change the file by inflating the size to avoid EDRs, and can clone 代码-signing certs from legitimate files.
In doing so, Mangle helps loaders evade on-disk and in-memory scanners.
Install:
The first step, as always, is to clone the repo. Before you compile Mangle, you'll need to install the dependencies. To install them, run the following commands:
Then build it
Usage:
Full usage information can be found here.
!image
*Image used from
🔙AMSI Fail
AMSI.fail is a great website that can be used to generate obfuscated PowerShell snippets that break or disable AMSI for the current process.
The snippets are randomly selected from a small pool of techniques/ before being obfuscated. Every snippet is obfuscated at runtime/request so that no generated output share the same signatures.
Nice f-secure blog explaining AMSI here.
!image
*Image used from
🔙ScareCrow
ScareCrow is a payload creation 框架 for side loading (not injecting) into a legitimate Windows process (bypassing Application Whitelisting controls).
Once the DLL loader is loaded into memory, it utilizes a technique to flush an EDR’s hook out of the system DLLs running in the process's memory.
When executed, ScareCrow will copy the bytes of the system DLLs stored on disk in C:\Windows\System32\. These DLLs are stored on disk “clean” of EDR hooks because they are used by the system to load an unaltered copy into a new process when it’s spawned. Since EDR’s only hook these processes in memory, they remain unaltered.
Nice blogs for learning about techniques utilized by ScareCrow:
Install:
*ScareCrow requires golang 1.16.1 or later to compile loaders.*
Usage:
Full usage information can be found here.
!image
*Image used from
🔙moonwalk
moonwalk is a 400 KB single-binary executable that can clear your traces while penetration testing a Unix machine.
It saves the state of system logs pre-exploitation and reverts that state including the filesystem timestamps post-exploitation leaving zero traces of a ghost in the shell.
Install:
Usage:
!image
*Image used from
Credential Access
====================
🔙Mimikatz
Great 工具 for gaining access to hashed and cleartext passwords on a endpoint. Once you ha pri access to a system, drop this 工具 to collect some creds.
Install:
1. Download the mimikatz_trunk.7z file.
2. Once downloaded, the mimikatz.exe binary is in the x64 folder.
Usage:
!image
🔙LaZagne
Nice 工具 for extracting locally stored passwords from browsers, databases, games, mail, git, wifi, etc.
Install: (Binary)
You can install the standalone binary from here.
Usage:
!image
🔙hashcat
工具 for cracking password hashes. Supports a large list of hashing algorithms (Full list can be found here).
Install: Binary
You can install the standalone binary from here.
Usage:
Nice hashcat command cheatsheet.
!image
🔙John the Ripper
Another password cracker, which supports hundreds of hash and cipher types, and runs on many operating systems, CPUs and GPUs.
Install:
Usage:
!image
🔙SCOMDecrypt
This 工具 is designed to retrieve and decrypt RunAs credentials stored within Microsoft System Center Operations Manager (SCOM) databases.
NCC blog post - 'SCOMplicated? – Decrypting SCOM “RunAs” credentials'
Pre-requisites:
To run the 工具 you will require administrati on the SCOM 服务端. You will also need to ensure that you have read access to the following registry key:
You can check manually that you can see the 数据库 by gathering the connection details from the following keys:
Install: (PS1)
Install: (Compile)
Using Studio 2019 Community Edition you can compile the SCOMDecrypt binary.
Open the SCOMDecrypt project .sln, choose "Release", and build.
Usage:
!image
*Image text used from
🔙nanodump
The LSASS (Local Security Authority Subsystem Service) is a system process in the Windows operating system that is responsible for enforcing the security policy on the system. It is responsible for a number of tasks related to security, including authenticating users for logon, enforcing security policies, and generating audit logs.
Creating a dump of this process can allow an attacker to extract password hashes or other sensiti from the process's memory, which could be used to compromise the system further.
This allows for the creation of a minidump of the LSASS process.
Install:
Install: (Linux with MinGW)
Install: (Windows with MSVC)
Install: (CobaltStrike only)
Import the NanoDump.cna script on Cobalt Strike.
Full installation information can be found here.
Usage:
Full usage information can be found here.
!nanodump
*Image used from
🔙e
A standalone python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those that contain matches. Created for two main reasons:
tree is an amazing 工具 for analyzing directory structures. It's really handy to have a standalone alternative of the command for post-exploitation enumeration as it is not pre-installed on every linux distro and is kind of limited on Windows (compared to the UNIX ).Install:
Usage:
!image
*Image used from
🔙SeeYouCM-Thief
Simple 工具 to automatically download and parse configuration files from Cisco phone systems searching for SSH credentials.
Will also optionally enumerate acti users from the UDS API.
Blog - Exploiting common misconfigurations in cisco phone systems
Install:
Usage:
!image
*Image used from
🔙MailSniper
MailSniper is a penetration testing 工具 for searching through email in a Microsoft Exchange en for specific terms (passwords, insider intel, 网络 architecture information, etc.). It can be used as a non-administrative user to search their own email or by an Exchange administrator to search the mailboxes of every user in a domain.
MailSniper also includes additional modules for password spraying, enumerating users and domains, gathering the Global Address List (GAL) from OWA and EWS and checking mailbox permissions for every Exchange user at an organization.
Nice blog post with more information about here.
MailSniper Field Manual
Install:
Usage:
!image
*Image used from
🔙SharpChromium
SharpChromium is a .NET 4.0+ CLR project to retrieve data from Google Chrome, Microsoft Edge, and Microsoft Edge Beta. Currently, it can extract:
This rewrite has several ad to previous implementations, which include:
Install:
Using Studio Community Edition.
Open up the project .sln, choose "release", and build.
Usage:
!image
*Image used from
🔙dploot
DPAPI (Data Protection Application Programming Interface) provides a set of APIs to encrypt and decrypt data where a user password is typically used to set the 'master key' (in a user scenario). So to le DPAPI to gain access to certain data (Chrome Cookies/Login Data, the Windows Credential Manager/Vault etc) we just need access to a password.
dploot is Python rewrite of SharpDPAPI written un C# by Harmj0y, which is itself a port of DPAPI from Mimikatz by gentilkiwi. It implements all the DPAPI logic of these tools, but this time it is usable with a python interpreter and from a Linux en.
Blog - Operational Guidance for Offensive User DPAPI Abuse
Install: (Pip)
Install: (Git)
Usage:
Discovery
====================
🔙PCredz
This 工具 extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP, IMAP, etc from a pcap file or from a li.
Install:
Usage: (PCAP File Folder)
Usage: (Li)
!image
🔙PingCastle
Ping Castle is a 工具 designed to assess quickly the Acti security level with a methodology based on risk assessment and a maturity 框架. It does not aim at a perfect e but rather as an efficiency compromise.
Install: (Download)
Usage:
!image
🔙Seatbelt
Seatbelt is a useful 工具 for gathering detailed information about the security posture of a target Windows machine in order to identify potential and attack .
It is designed to be run on a compromised machine to gather information about the current security configuration, including information about installed software, services, group policies, and other security-related settings
Install: (Compile)
Seatbelt has been built against .NET 3.5 and 4.0 with C# 8.0 features and is compatible with Studio Community Edition.
Open up the project .sln, choose "release", and build.
Usage:
Full command groups and parameters can be found here.
!image
*Image used from
🔙ADRecon
Great 工具 for gathering information about a 's Microsoft Acti (AD) en, with support for Excel outputs.
It can be run from any workstation that is connected to the en, e that are not domain members.
BlackHat USA 2018 SlideDeck
Prerequisites
Install: (Git)
Install: (Download)
You can download a zip archive of the latest release.
Usage:
Full usage and parameter information can be found here.
!image
*Image used from
🔙adidnsdump
By default any user in Acti can enumerate all DNS records in the Domain or Forest DNS zones, similar to a zone transfer.
This 工具 enables enumeration and exporting of all DNS records in the zone for recon purposes of internal networks.
Install: (Pip)
Install: (Git)
Note: *The tool requires impacket and dnspython to function. While the 工具 works with both Python 2 and 3, Python 3 support requires you to install impacket from GitHub.*
Usage:
Blog - Getting in the Zone: dumping Acti DNS using adidnsdump
!adidnsdump
*Image used from
🔙kerbrute
A 工具 to quickly bruteforce and enumerate valid Acti accounts through Kerberos Pre-Authentication.
Install: (Go)
Install: (Make)
Usage:
!image
*Image used from
🔙sca
Sca is a multi-threaded post-exploitation scanning 工具 for sca systems, finding most frequently used files and folders as well as "interesting" files containing sensiti.
Sca confronts a challenging issue typically faced by Penetration Testing consultants during internal penetration tests; the issue of having too much access to too many systems with limited days for testing.
Install:
First install CrackMapExec from here.
Usage:
Nice blog post.
!image
*Image used from
Lateral Mo
====================
🔙crackmapexec
This is a great 工具 for pi in a Windows/Acti en using credential pairs (username:password, username:hash). It also offered other features including enumerating logged on users and spidering SMB shares to executing psexec style attacks, auto-injecting Mimikatz/Shellcode/DLL’s into memory using Powershell, dumping the NTDS.dit and more.
Install:
Usage:
!image
🔙WMIOps
WMIOps is a powershell script that uses WMI to perform a of actions on hosts, local or remote, within a Windows en.
De by .
Original blog post documenting release.
Install: (PowerShell)
Usage:
!image
!image
*Images used from
🔙PowerLessShell
工具 that uses MSBuild.exe to remotely execute PowerShell scripts and commands without spawning powershell.exe.
Install:
Usage:
Full usage information can be found here.
!image
*Image used from
🔙PsExec
PsExec is a part of the Sysinternals suite of tools, which is a collection of utilities for managing and troubleshooting Windows systems.
It is great for remotely executing commands on target machines.
Note: Some A PsExec as a 'remote admin' virus.
Install: (PowerShell)
Usage:
Great blog post on PsExec usage.
!image
*Image used from
🔙LiquidSnake
Liquid Snake is a program aimed at performing lateral mo against Windows systems without touching the disk.
The 工具 relies on WMI Event Subscription in order to execute a .NET assembly in memory, the .NET assembly will listen for a shellcode on a named pipe and then execute it using a of the thread hijacking shellcode injection.
The project is composed by two separate solutions:
CSharpNamedPipeLoader - the component that will be transformed in VBS LiquidSnake - the component responsible to creating the WMI Event Subscription on the remote systemInstall:
Open both solutions in Studio and build. *Make sure to target x64 architecture for the CSharpNamedPipeLoader.*
Output: Two separate EXEs: CSharpNamedPipeLoader.exe and LiquidSnake.exe
Full build information can be found here.
Usage:
Use LiquidSnake.exe agains a host where you ha access over as follows:
If e went fine, you should obtain an output similar as the following:
General usage information can be found here.
Full LiquidSnake usage information can be found here.
!LiquidSnake
*Image used from
🔙Enabling RDP
🔙Upgrading shell to meterpreter
Shells ()
After getting basic shell access to an endpoint a meterpreter is nicer to continue with.
[attacker] Generate a meterpreter shell:
!image
[] Download to endpoint:
[attacker] Configure listener:
[] Execute payload:
!image
🔙Forwarding Ports
Sometimes, after gaining access to an endpoint there are local ports. Making these internal ports external routable can help for lateral mo to other services on the host.
🔙Jenkins reverse shell
If you gain access to a jenkins script console you can use this to gain a reverse shell on the node.
🔙ADFSpoof
Created by Doug Bienstock while at Mandiant FireEye.
ADFSpoof has two main functions:
1. Given the EncryptedPFX blob from the AD FS configuration 数据库 and DKM decryption key from Acti, produce a usable key/cert pair for token signing.
2. Given a signing key, produce a signed security token that can be used to access a federated application.
This 工具 is meant to be used in conjunction with ADFSDump. ADFSDump runs on an AD FS 服务端 and outputs important information that you will need to use ADFSpoof.
Install:
Note: *ADFSpoof requires the installation of a custom fork of the Python Cryptography package, a here.*
Usage:
Full usage information can be found here.
Additional command examples can be found here.
!image
*Image used from
🔙Coercer
A python script to automatically coerce a Windows 服务端 to authenticate on an arbitrary machine through many methods.
Features:
More feature information here.
Install: (pip)
Usage:
!image
*Image used from
Collection
====================
🔙BloodHound
An application used to acti en. A quick way to attack paths and understand ' acti properties.
Install: PenTestPartners Walkthrough
Custom Queries: CompassSecurity BloodHoundQueries
!image
🔙Snaffler
Snaffler is an ad credential scanner/collector for Acti en. *With a great README*.
Snaffler uses a system of "classifiers", each of which examine shares or folders or files or file contents, passing some items downstream to the next classifier, and discarding others. Each classifier uses a set of rules to decide what to do with the items it classifies.
*More information about Snaffler rules.*
'*Broadly speaking - it gets a list of Windows computers from Acti, then spreads out its snaffly appendages to them all to figure out which ones have file shares, and whether you can read them.*' - Snaffler README (2023)
Install:
You can download the binary from the GitHub Releases Page.
Usage:
!image
*Image used from
🔙linWinPwn
linWinPwn is a bash script that automates a number of Acti Enumeration and checks.
The script uses a number of tools and serves as wrapper of them. Tools include: impacket, bloodhound, crackmapexec, enum4linux-ng, ldapdomaindump, lsassy, smbmap, kerbrute, adidnsdump, certipy, silenthound, and others.
linWinPwn is particularly useful when you ha to an Acti en for a limited time only, and you wish to automate the enumeration process and collect e efficiently.
Install:
Usage:
Full usage information here.
!image
*Image used from
Command and Control
====================
🔙Living Off Trusted Sites Project
C2 implants can be detected by defenders looking for unusual 网络 traffic to uncommon domains. Additionally proxy solutions can sometimes block connections to untrusted domains.
Being able to hide your C2 traffic via a trusted domain will help you to stay undetected and reduce the likelihood of being blocked at the proxy level by security solutions.
This resource contains a list of trusted sites that can be used.
Usage:
Visit
Search for +C&C in the search bar to view all potential domains / subdomains that can be used for command and control operations.
Results include:
!image
*Image used from
🔙Havoc
Havoc is a modern and malleable post-exploitation command and control 框架, created by .
Features include: Sleep Obfuscation, x64 return address spoofing, Indirect Syscalls for Nt* APIs
Pre-requisites: (Ubuntu 20.04 / 22.04)
Build + Usage:
Pre-requisites: (Ubuntu 20.04 / 22.04)
Build + Usage:
Run the teamserver
*Full install, build and run instructions on the wiki*
!image
🔙Co
Co is a .NET command and control 框架, it has a web interface that allows for multi-user collaboration.
It can be used to remotely control compromised systems and perform a of different tasks, including executing arbitrary 代码, capturing keystrokes, exfiltrating data, and more.
Install: (Dotnet Core)
You can download dotnet core for your platform from here.
Note: *After starting Co, you must register an initial user through the web interface. Na to the web interface will allow you to register the initial user*
Usage: (Dotnet Core)
Install: (Docker)
Usage: (Docker)
Full installation and startup instructions can be found on the wiki here.
!image
*Image from
🔙Merlin
Merlin is an open-源码 post-exploitation 框架 that is designed to be used after a initial compromise of a system.
It is written in Python and can be used to perform a of different tasks, such as executing arbitrary 代码, moving laterally through a 网络, and exfiltrating data.
Install:
1. Download the latest compiled of Merlin 服务端 from the releases section
2. Extract the files with 7zip using the x function The password is: merlin
3. Start Merlin
4. Configure a listener
5. Deploy an agent. See Agent Execution Quick Start Guide for examples
Usage:
1. Ensure the Merlin 服务端 is running with a configured listener
2. Download and deploy an agent to the
3. Execute agent
For detailed usage information see the official Merlin wiki.
!image
*Image from
🔙Metasploit Framework
Metasploit is an open-源码 框架 for de, testing, and using exploit 代码.
The Metasploit 框架 includes a large number of pre-built exploits and payloads, as well as a fully-featured integrated de en (IDE) for creating and testing custom exploits.
Install: (Installer)
Usage:
Full installation instructions can be found on the official wiki.
Rapid7 Metasploit blogs
Cheat sheet graphic
Nice command list
!image
*Image used from
🔙Pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation 框架 written in python and C.
It allows an attacker to remotely control a 's computer and execute actions, such as command execution, key logging, and taking screen shots.
Install: (Git)
Roll fix to fix the error:
Start:
*Git install instructions used from here.*
Install: (Docker)
For detailed docker and pupy installation instructions see the wiki.
Usage:
Full usage information can be found on the wiki.
The wiki contains good post exploitation information.
!image
*Image used from
🔙Brute Ratel
BruteRatel is a great command and control (C4) 框架 created by . The 框架 consists of a 客户端 component 'badger' that is installed on the compromised system, and a ser 'commander' that is run by the red team.
The 客户端 and ser with each other using communication channels, such as HTTP, DNS, or TCP, and can be configured to use different encoding and encryption methods to evade detection.
Some nice features:
Install:
To legally get access to the 框架 you will need to buy a licence (1 Year $2500 per user). See the pricing page for more information.
After purchase you can download the 框架 from here with your Acti Key and License User ID.
Usage:
Full commander terminal usage information can be found here.
!image
*Image used from
🔙NimPlant
A light-weight first-stage C2 implant written in Nim.
Features:
inline-execute, shinject (using dynamic in), or in-thread execute-assemblyInstall:
Usage:
Before running make sure to create the config.tool configuration file, more information can be found here.
Full usage information can be found here.
Blog - Building a C2 Implant in Nim - Considerations and Lessons Learned
!image
*Image used from
🔙Hoaxshell
A Windows reverse shell payload generator and handler that abuses the http(s) 协议 to establish a beacon-like reverse shell.
Install:
Usage:
Full usage documentation here.
Usage Demo - YouTube
Hoaxshell vs AV
!image
*Image used from
Exfiltration
====================
🔙Dnscat2
A 工具 for establishing C2 connections via DNS, even if the attacker and machines are behind a firewall / 网络 address translation (NAT).
The 工具 is designed to be stealthy and difficult to detect, as it uses legitimate DNS traffic to transmit data.
Install: (Compile - Server)
Install: (Compile - Client)
Full installation information can be found in the Installation Section.
Usage: (Server)
Usage: (Client)
Usage: (Tunnels)
Full usage information can be found in the Usage Section.
!image
🔙Cloakify
When exfiltrating files, DLP (Data Loss Pre) solutions will typically trigger on strings within these files. Cloakify reduces this risk by transforming the data.
Cloakify transforms any filetype (e.g. .zip, .exe, .xls, etc.) into a list of harmless-looking strings. This lets you hide the file in plain sight, and transfer the file without triggering alerts.
Note: You can make your own ciphers, see here for more info.
Install:
Usage:
!image
!image
🔙PyExfil
"An Alpha-Alpha stage package, not yet tested (and will appreciate any feedbacks and commits) designed to show several techniques of data exfiltration is real-world scenarios."
Install:
Usage: (Full Usage here)
#### HTTP Cookies
#### ICMP Echo 8
#### NTP Request
!image
🔙Powershell RAT
Python based backdoor that uses Gmail to exfiltrate data as an e-mail attachment. It tracks the user activity using screen capture and sends the information to an attacker as an e-mail attachment.
Install:
Usage: (Full Usage here)
#### Setup
$username & $password for your account in the Mail.ps1 Powershell file$msg.From & $msg.To.Add with throwaway gmail address!image
🔙GD-Thief
工具 for exfiltrating files from a target's Google Drive that you ha to, 's API.
This includes all shared files, all files from shared drives, and all files from domain drives that the target has access to.
Install:
then...
1. Create a new Google Cloud Platform (GCP) project
2. Enable a Google Workspace API
3. Configure OAuth Consent screen
4. Create a credential
5. Add the 's Google account to the Application's Test Users
For detailed setup instructions see the How To Guide.
Usage:
Nice blog post explaining the logic behind the 工具.
🔙goshs
goshs is a single-binary file 服务端 for red teamers, replacing python3 -m http.server
with HTTP/S, WebDAV, SFTP, SMB, NTLM hash capture, DNS/SMTP OOB callbacks,
authentication, and share links — all from one command.
Install:
Usage:
![goshs]()
*Image used from
Impact
====================
🔙Conti Pentester Guide Leak
Conti is a ransomware group that is known for targeting large organizations and using sophisticated tactics to evade detection and maximize the impact of their attacks.
Conti has been responsible for a number of high-profile ransomware attacks, including ones against the computer systems of the City of Pensacola, Florida, and the computer systems of the Irish health service.
The Conti Pentester Guide Leak - Repository contains leaked pentesting materials given to Conti ransomware group affilates.
Topics include:
Note: *.org obtained more training materials and tools used by Conti ransomware operators here.*
!image
*Image used from
🔙SlowLoris
Slowloris is a type of denial-of-service (DoS) attack that in sending HTTP requests to a web 服务端 in a way that ties up the 服务端's resources, pre it from being able to process legitimate requests.
This attack would typically be conducted with a botnet, it is designed to be difficult to detect and mitigate, as it uses a relatively small number of connections and does not generate a large amount of traffic.
Install: (Pip)
Install: (Git)
Usage:
!image
🔙usbkill
This is an anti-forensic kill-switch that waits for a change in USB port status, immediately shutting down endpoint if a change is detected.
In some situations, it is imperative that no data is added or removed from an endpoint via USB.
This is where USBkill comes in.
Install:
Usage:
!image
*Image used from
🔙Keytap
This is a 工具 that can guess the pressed keyboard keys from the audio of a computer's microphone.
Keytap2 can also be used to retrieve text from audio snippets of keyboard typing.
Install: (Build)
Usage:
See full usage documentation here.
Try the online demo at
!image
*Image used from
项目信息
开发语言:未知
Star 数:9804
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Tools and Techniques for Red Team / Penetration Testing展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | RedTeam-Tools - 红队/渗透技术工具和技术 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:02:02 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 271 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |