 黑客技术
点击放大
awesome-pentest-cheat-sheets - 收集对pentesti有用的速查表
项目说明
THIS REPOSITORY IS DEPRECATED.
ALL OF ITS CONTENT HAS BEEN UPDATED AND MOVED TO awesome-pentest-cheat-sheets
Awesome Pentest Cheat Sheets ![Awesome]()
Collection of cheat sheets useful for pentesting
Contribution
Your contributions and suggestions are heartily welcome. Please check the Contributing Guidelines for more details.
Security Talks and
* InfoCon - Hacking Conference Archive
* Curated list of Security Talks and
General
* Docker Cheat Sheet
* Mobile App Pentest Cheat Sheet
* OSX Command Line Cheat Sheet
* PowerShell Cheat Sheet - SANS PowerShell Cheat Sheet from SEC560 Course (PDF )
* Rawsec's CyberSecurity In - An open-源码 in of tools, resources, CTF platforms and Operating Systems about CyberSecurity. (源码)
* Regexp Security Cheat Sheet
* Security Cheat Sheets - A collection of security cheat sheets
* Unix / Linux Cheat Sheet
Discovery
* Google Dorks - Google Dorks Hacking 数据库 (Exploit-DB)
* Shodan - Shodan is a search 引擎 for finding specific devices, and device types, that exist online
* ZoomEye - Zoomeye is a Cyberspace Search 引擎 recording information of devices, websites, services and components etc.
* Amass - OWASP 网络 mapping of attack surfaces and external asset discovery using open 源码 information
Enumeration
* enum4linux-ng - Python 工具 for enumerating information from Windows/Samba systems
Exploitation
* Empire Cheat Sheet - Empire is a PowerShell and Python post-exploitation 框架
* Exploit De Cheat Sheet - 's exploit de in one picture
* Ja Cheat Sheet - A cheat sheet for pentesters about Ja Binary Deserialization
* Local File Inclusion (LFI) Cheat Sheet #1 - Arr0way's LFI Cheat Sheet
* Local File Inclusion (LFI) Cheat Sheet #2 - Aptive's LFI Cheat Sheet
* Metasploit Unleashed - The ultimate guide to the Metasploit 框架
* Metasploit Cheat Sheet - A quick reference guide (PNG )(PDF )
* PowerSploit Cheat Sheet - PowerSploit is a powershell post-exploitation 框架
* PowerView 2.0 Tricks
* PowerView 3.0 Tricks
* PHP htaccess Injection Cheat Sheet - htaccess Injection Cheat Sheet by PHP Secure Configuration Checker
* Reverse Shell Cheat Sheet #1 - Pentestmonkey Reverse Shell Cheat Sheet
* Reverse Shell Cheat Sheet #2 - Arr0way's Reverse Shell Cheat Sheet
* SQL Injection Cheat Sheet - Netsparker's SQL Injection Cheat Sheet
* SQLite3 Injection Cheat Sheet
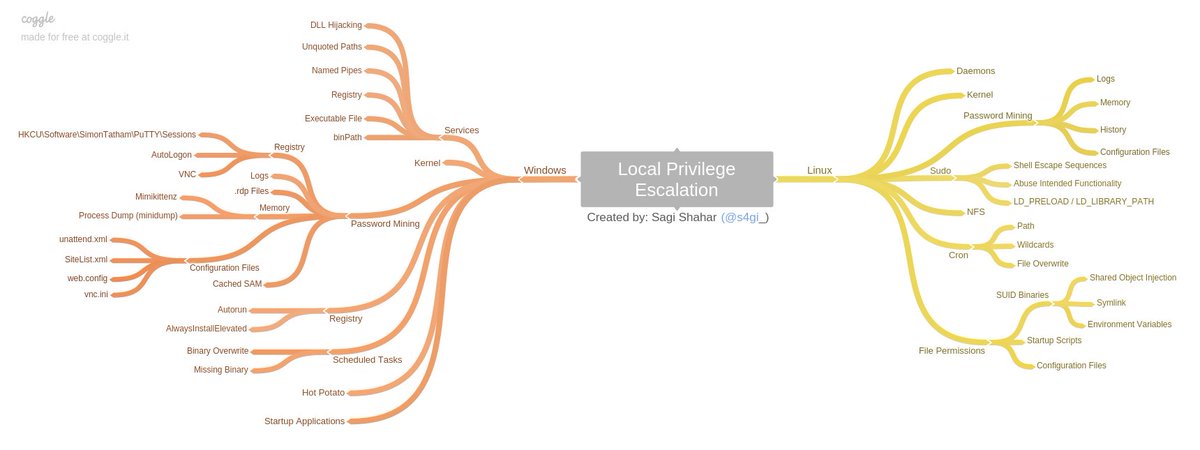
Pri Escalation
Learn Pri Escalation
* Windows / Linux Local Pri Escalation Workshop - The Pri Escalation Workshop covers all known (at the time) attack of local user pri escalation on both Linux and Windows operating systems and includes slides, , test VMs.
<img src="
Linux Pri Escalation
* Basic Linux Pri Escalation - Linux Pri Escalation by
* linux-exploit-suggester.sh - Linux pri escalation auditing 工具 written in bash (updated)
* Linux_Exploit_Suggester.pl - Linux Exploit Suggester written in Perl (last update 3 years ago)
* Linux_Exploit_Suggester.pl v2 - Next-generation exploit suggester based on Linux_Exploit_Suggester (updated)
* Linux Soft Exploit Suggester - linux-soft-exploit-suggester finds exploits for all software in a system helping with the pri escalation. It focuses on software packages instead of Kernel
* checksec.sh - bash script to check the properties of executables (like PIE, RELRO, PaX, Canaries, ASLR, Fortify 源码)
* linuxpri.py - This script is intended to be executed locally on a Linux box to enumerate basic system info and search for common pri escalation such as world writable files, misconfigurations, clear-text passwords and applicable exploits ()
* LinEnum - This 工具 is great at running through a heap of things you should check on a Linux system in the post exploit process. This include file permissions, cron jobs if , weak credentials etc.()
* linPEAS - LinPEAS - Linux Pri Escalation Awesome Script. Check the Local Linux Pri Escalation checklist from book.hacktricks.xyz
* MimiPenguin - A 工具 to dump the login password from the current linux desktop user. Adapted from the idea behind the popular Windows 工具 mimikatz.
Windows Pri Escalation
* PowerUp - Excellent powershell script for checking of common Windows pri escalation . Written by harmj0y (direct link)
* PowerUp Cheat Sheet
* Windows Exploit Suggester - 工具 for detection of missing security patches on the windows operating system and mapping with the public a exploits
* Sherlock - PowerShell script to quickly find missing software patches for local pri escalation
* Watson - Enumerate missing KBs and suggest exploits for useful Pri Escalation
* Precompiled Windows Exploits - Collection of precompiled Windows exploits
* Metasploit Modules
* post/multi/recon/local_exploit_suggester - suggests local meterpreter exploits that can be used
* post/windows/gather/enum_patches - helps to identify any missing patches
Tools
* Nmap Cheat Sheet
* SQLmap Cheat Sheet
* SQLmap Tamper Scripts - SQLmap Tamper Scripts General/MSSQL/MySQL
*
* Wireshark Display Filters - Filters for the best sniffing 工具
Tools Online
* XSS'OR Encoder/Decoder - Online Decoder/Encoder for testing purposes (@e)
* WebGun - WebGun, XSS Payload Creator ()
* Hack - 工具 to convert encodings and generate attack ()
* JSFiddle - Test and share XSS payloads, Example PoC
Payloads
Genaral
* Fuzzdb - Dictionary of attack patterns and primitives for black-box application testing
Polyglot Challenge with submitted solutions
* SecList - A collection of multiple types of lists used during security assessments. List types include usernames, passwords, URLs, sensitive data grep strings, fuzzing payloads, and many more
XSS
* XSS Polyglot Payloads #1 - Unleashing an Ultimate XSS Polyglot list by 0xsobky
* XSS Polyglot Payloads #2 - 's XSS
* Browser's-XSS-Filter-Bypass-Cheat-Sheet- Excellent List of working XSS bypasses running on the latest of Chrome / Safari, IE 11 / Edge created by Masato Kinugawa
Write-Ups
* Bug Bounty Reference - huge list of bug bounty write-up that is categorized by the bug type (SQLi, XSS, IDOR, etc.)
* Write-Ups for CTF challenges
* Facebook Bug Bounties - Categorized Facebook Bug Bounties write-ups
Learning Platforms
Online
* Hack The Box :: Penetration Testing Labs
* OWASP Web Applications Directory Project (Online) - List of online a applications for learning purposes
* Pentestit labs - Hands-on Pentesting Labs (OSCP style)
* Root-me.org - Hundreds of challenges are a to train yourself in different and not simulated en
* .com - By Design VMs for practical 'hands-on' experience in digital security
Off-Line
* Damn Xebia Training En - Docker Container including several web applications (D, D, WebGoat, Juiceshop, Railsgoat, django.N Bank, Mutilidae II and more)
* OWASP Web Applications Directory Project (Offline) - List of offline a applications for learning purposes
* SOAP Web Service - a SOAP web service lab en
* Flask Web App - Flask Web App lab en
Wireless Hacking
Tools
* wifite2 - Full automated WiFi security testing script
Defence Topics
* Docker Security Cheat Sheet - The following tips should help you to secure a container based system (PDF )
* Windows Domain Hardening - A curated list of awesome Security Hardening techniques for Windows
Programming
* Ja Cheat Sheet - Learn ja in one picture (Online ) (PNG )
* Python Cheat Sheet #1 - Learn python3 in one picture (PNG )
* Python Cheat Sheet #2 - Learn python3 in one picture (Online ) (PNG )
* Python Snippets Cheat Sheet - List of helpful re-usable 代码 snippets in Python
项目信息
开发语言:未知
Star 数:4370
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Collection of the cheat sheets useful for pentesting展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | awesome-pentest-cheat-sheets - 收集对pentesti有用的速查表 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:03:19 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 133 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |