 黑客技术
点击放大
linux-smart-enumeration - 用于pentesting和CTFS wit的Linux枚举工具
项目说明
First, a couple of useful oneliners ;)
Note that since 2.10 you can *serve the script* to other hosts with the -S flag!
linux-smart-enumeration
Linux enumeration tools for pentesting and CTFs
This project was inspired by and uses
many of its tests.
Unlike LinEnum, lse tries to gradualy expose the information depending on its importance from a privesc point of view.
What is it?
This shell script will show relevant information about the security of the local Linux system, helping to escalate pri.
From 2.0 it is *mostly* POSIX compliant and tested with shellcheck and posh.
It can also monitor processes to disco program executions. It monitors while it is executing all the other tests so you save some time. By default it monitors during 1 minute but you can choose the watch time with the -p parameter.
It has 3 levels of so you can control how much information you see.
In the default level you should see the highly important security flaws in the system. The level 1 (./lse.sh -l1) shows
interesting information that should help you to privesc. The level 2 (./lse.sh -l2) will just dump all the information it
gathers about the system.
By default it will ask you some questions: mainly the current user password (if you know it ;) so it can do some additional tests.
How to use it?
The idea is to get the information gradually.
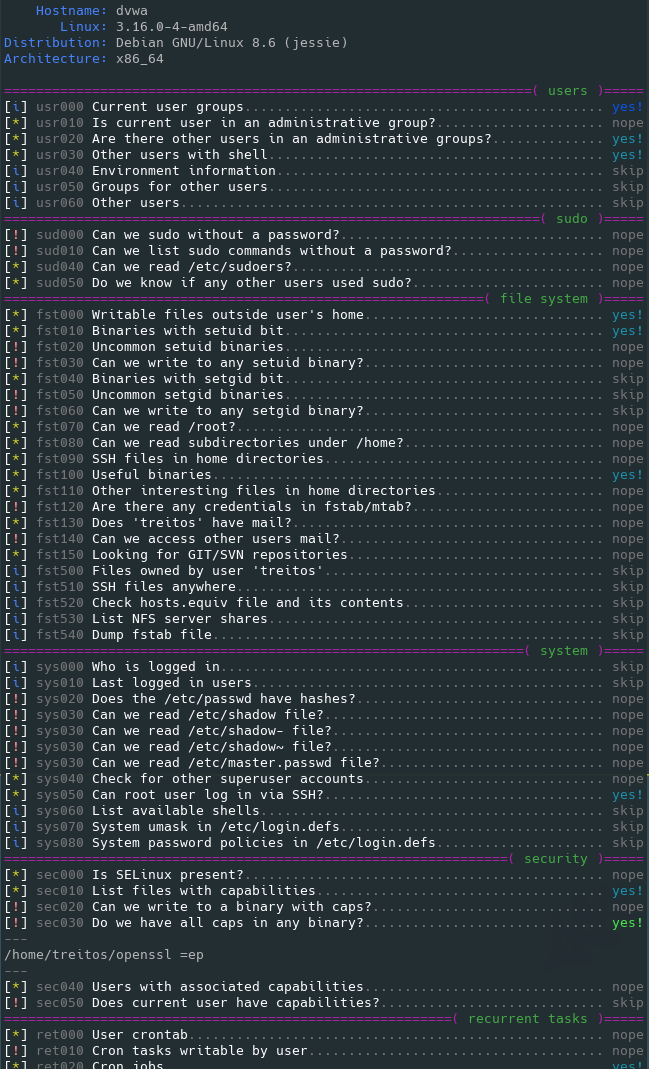
First you should execute it just like ./lse.sh. If you see some green yes!, you probably ha some good stuff to work with.
If not, you should try the level 1 with ./lse.sh -l1 and you will see some more information that can be interesting.
If that does not help, level 2 will just dump e you can gather about the service using ./lse.sh -l2. In this case you might find useful to use ./lse.sh -l2 | less -r.
You can also select what tests to execute by passing the -s parameter. With it you can select specific tests or sections to be executed. For example ./lse.sh -l2 -s usr010,net,pro will execute the test usr010 and all the tests in the sections net and pro.
Is it pretty?
Usage demo
Also a in webm video
!LSE Demo
Level 0 (default) output sample
!LSE level0
Level 1 output sample
!LSE level1
Level 2 output sample
!LSE level2
Examples
Direct execution oneliners
Buy me a beer
Feel free to buy me a beer if this script was useful
:)₿: 1DNBZRAzP6W
项目信息
开发语言:Shell
Star 数:3988
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Linux enumeration 工具 for pentesting and CTFs with levels展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | linux-smart-enumeration - 用于pentesting和CTFS wit的Linux枚举工具 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:03:35 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 517 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |