 黑客技术
点击放大

项目说明
<p align="center">
<img src="banner/hero.svg" alt="Pentest Swarm AI — the first open-源码 pentesting 工具 built on a real swarm" width="880">
</p>
<h1 align="center">The open-源码 XBOW alternative —<br>an autonomous API & web-app pentester.</h1>
<p align="center">
<strong>Dozens of AI agents don't just scan — they <em>exploit</em>. They chain attacks (BOLA/IDOR, JWT forgery, mass assignment, SSRF, injection), build and score attack paths, and prove real at machine speed.</strong>
</p>
<p align="center">
<sub>Built for <strong>pentesters</strong> · <strong>bug bounty hunters</strong> · <strong>red teamers</strong> · <strong>security researchers</strong></sub>
</p>
<p align="center">
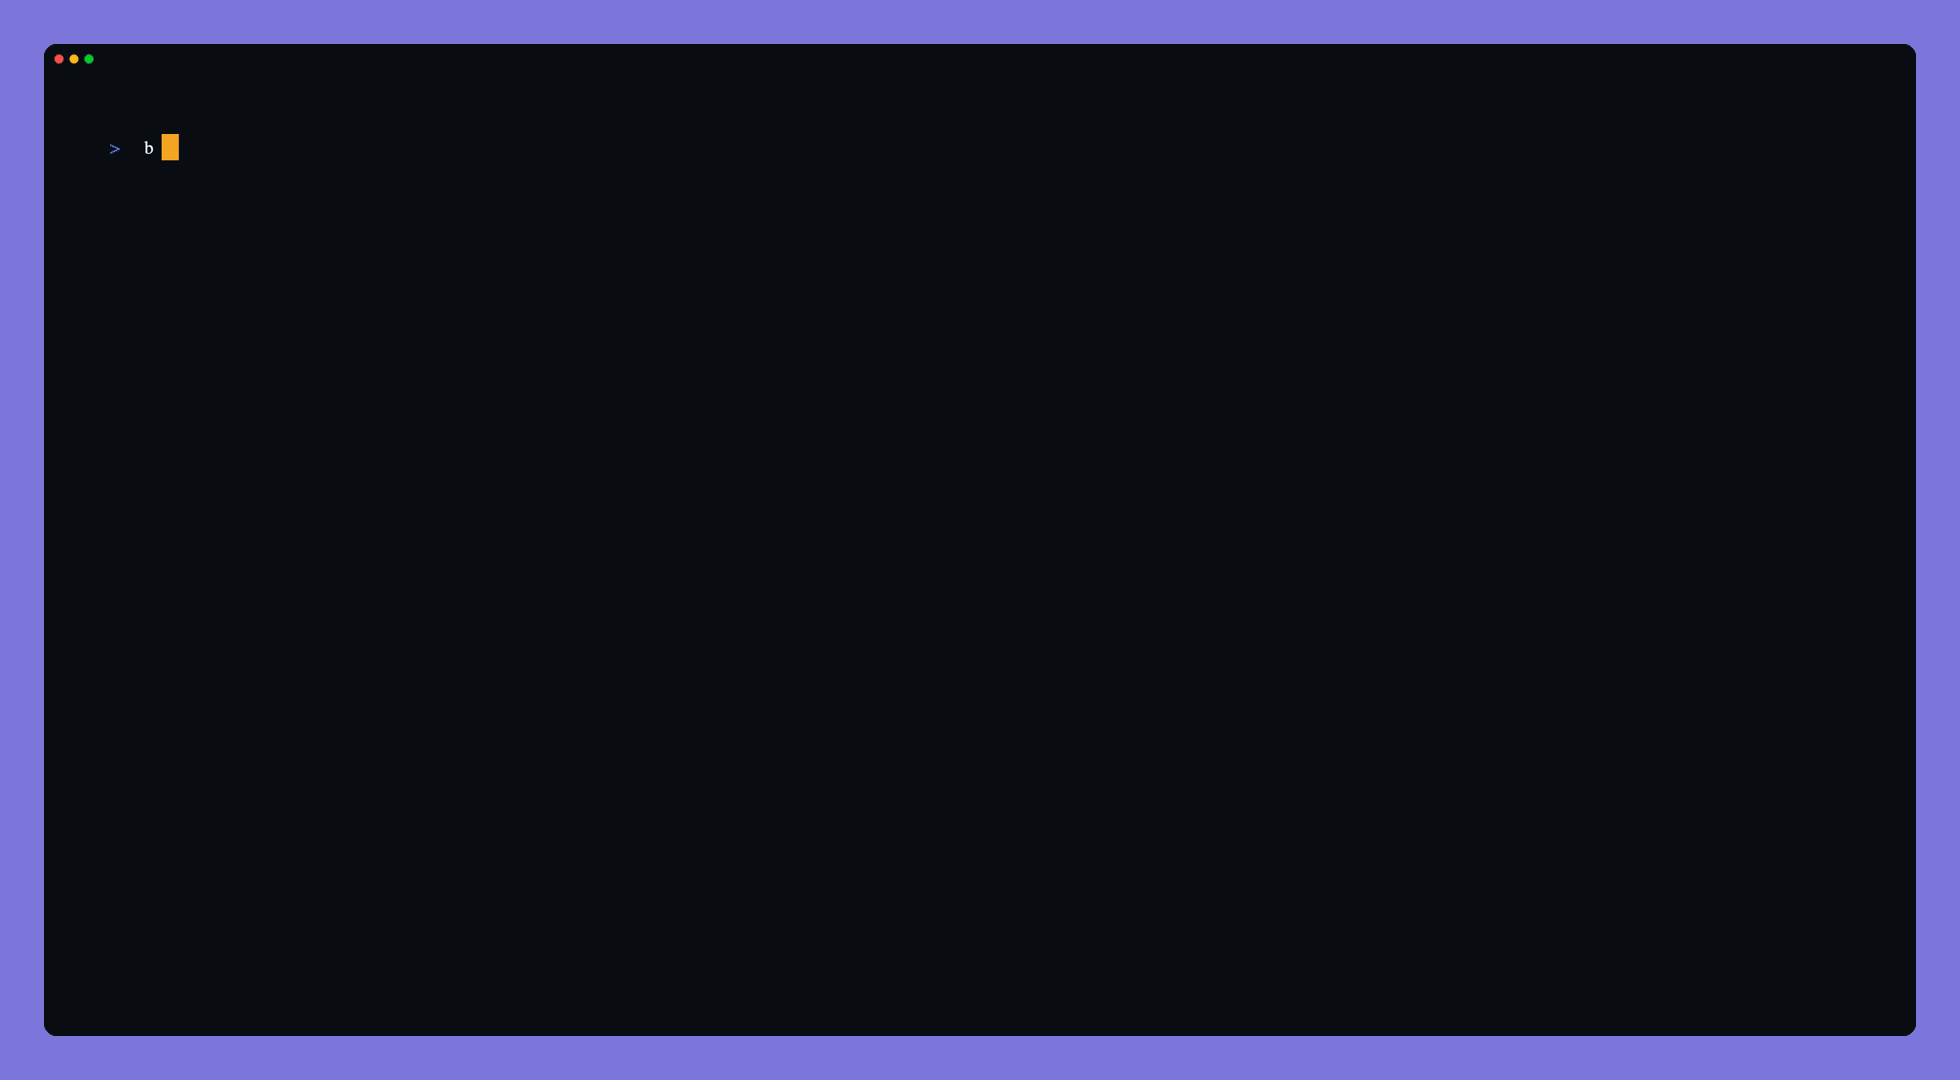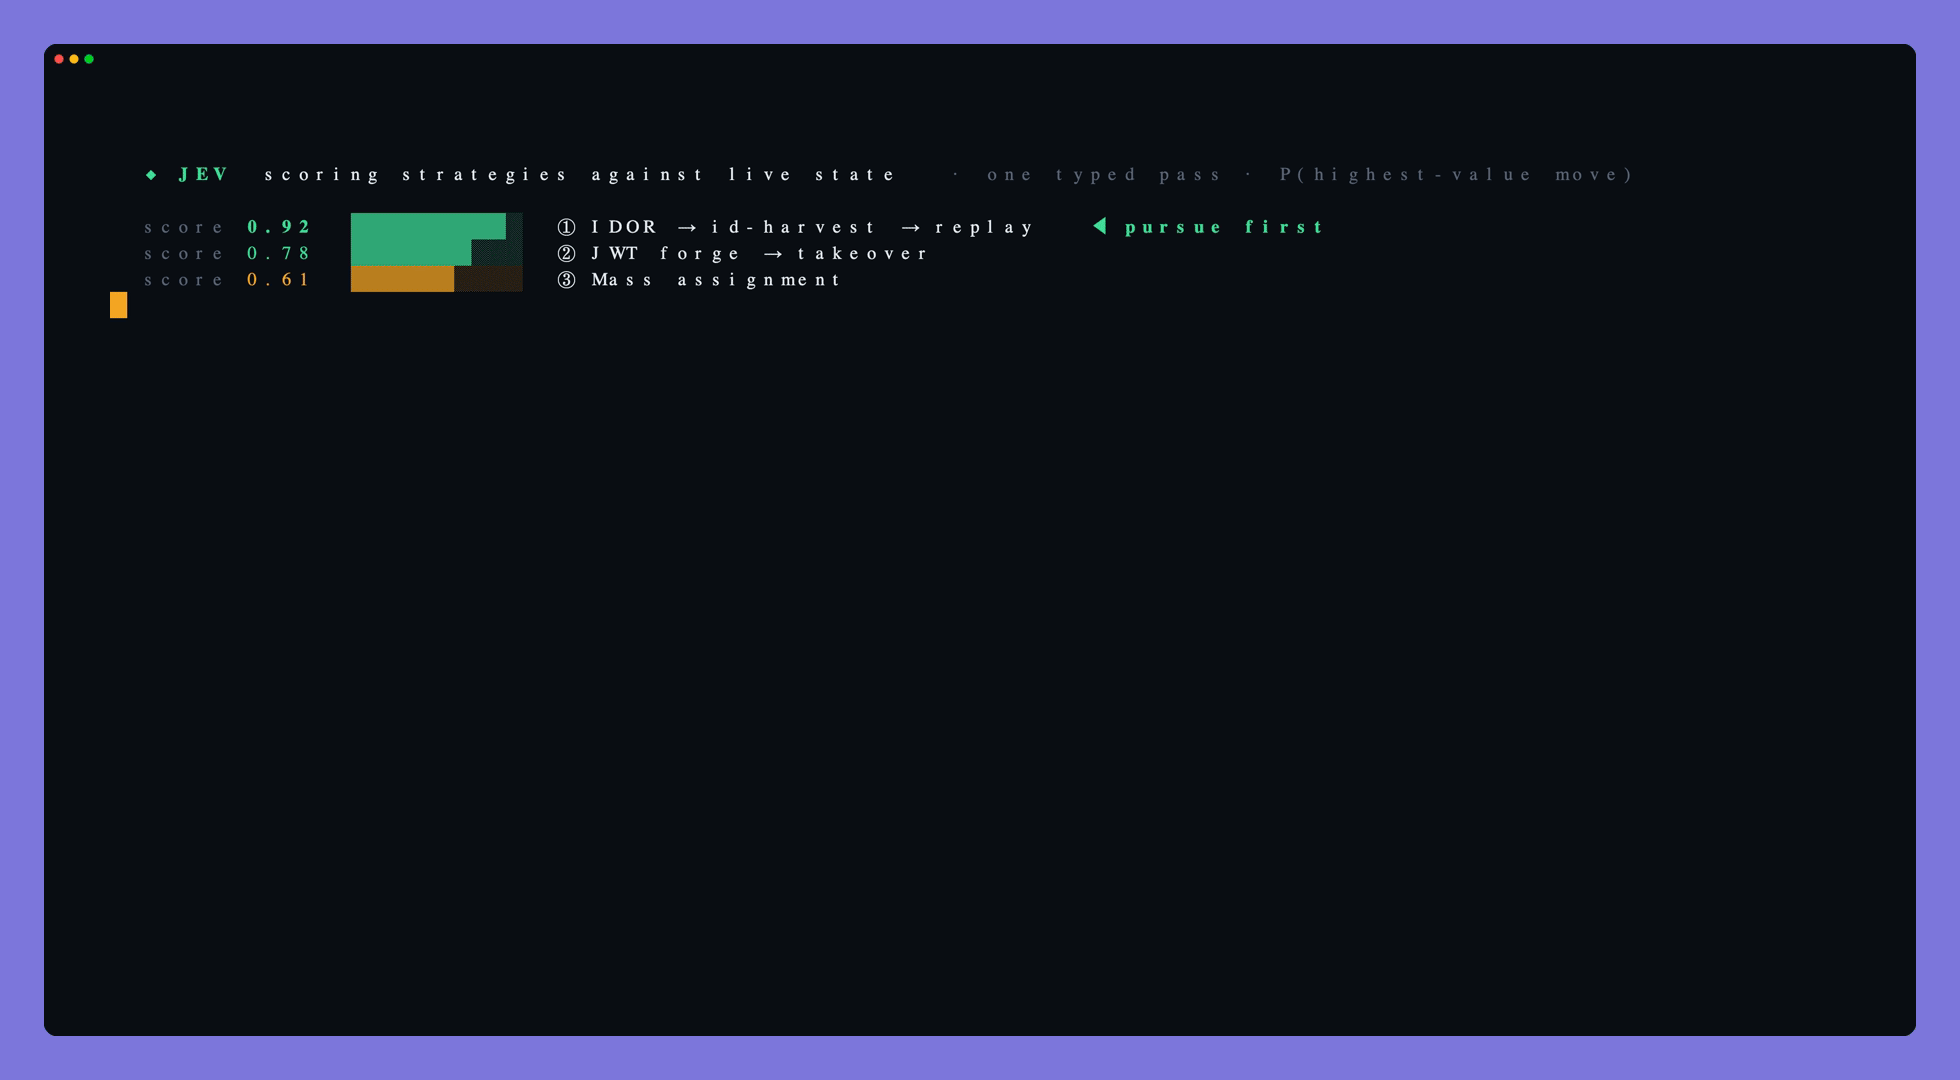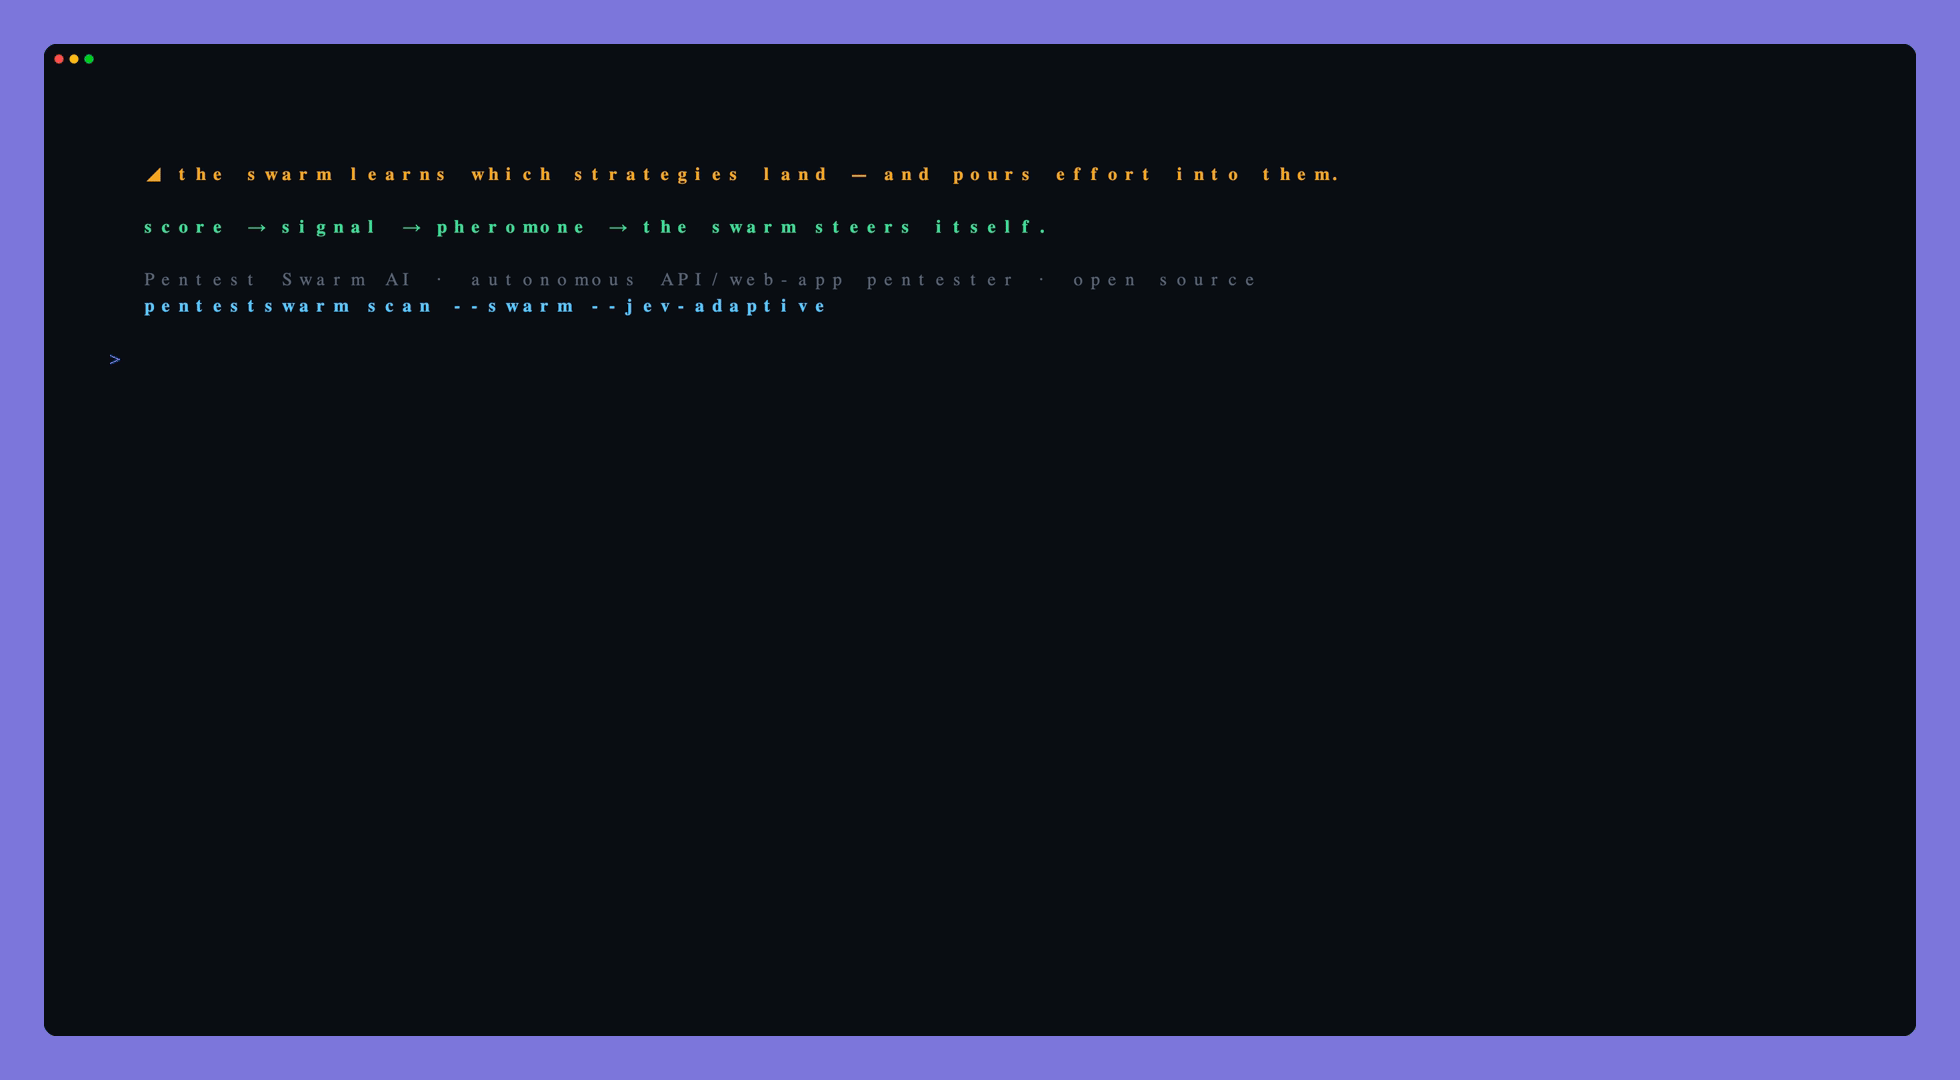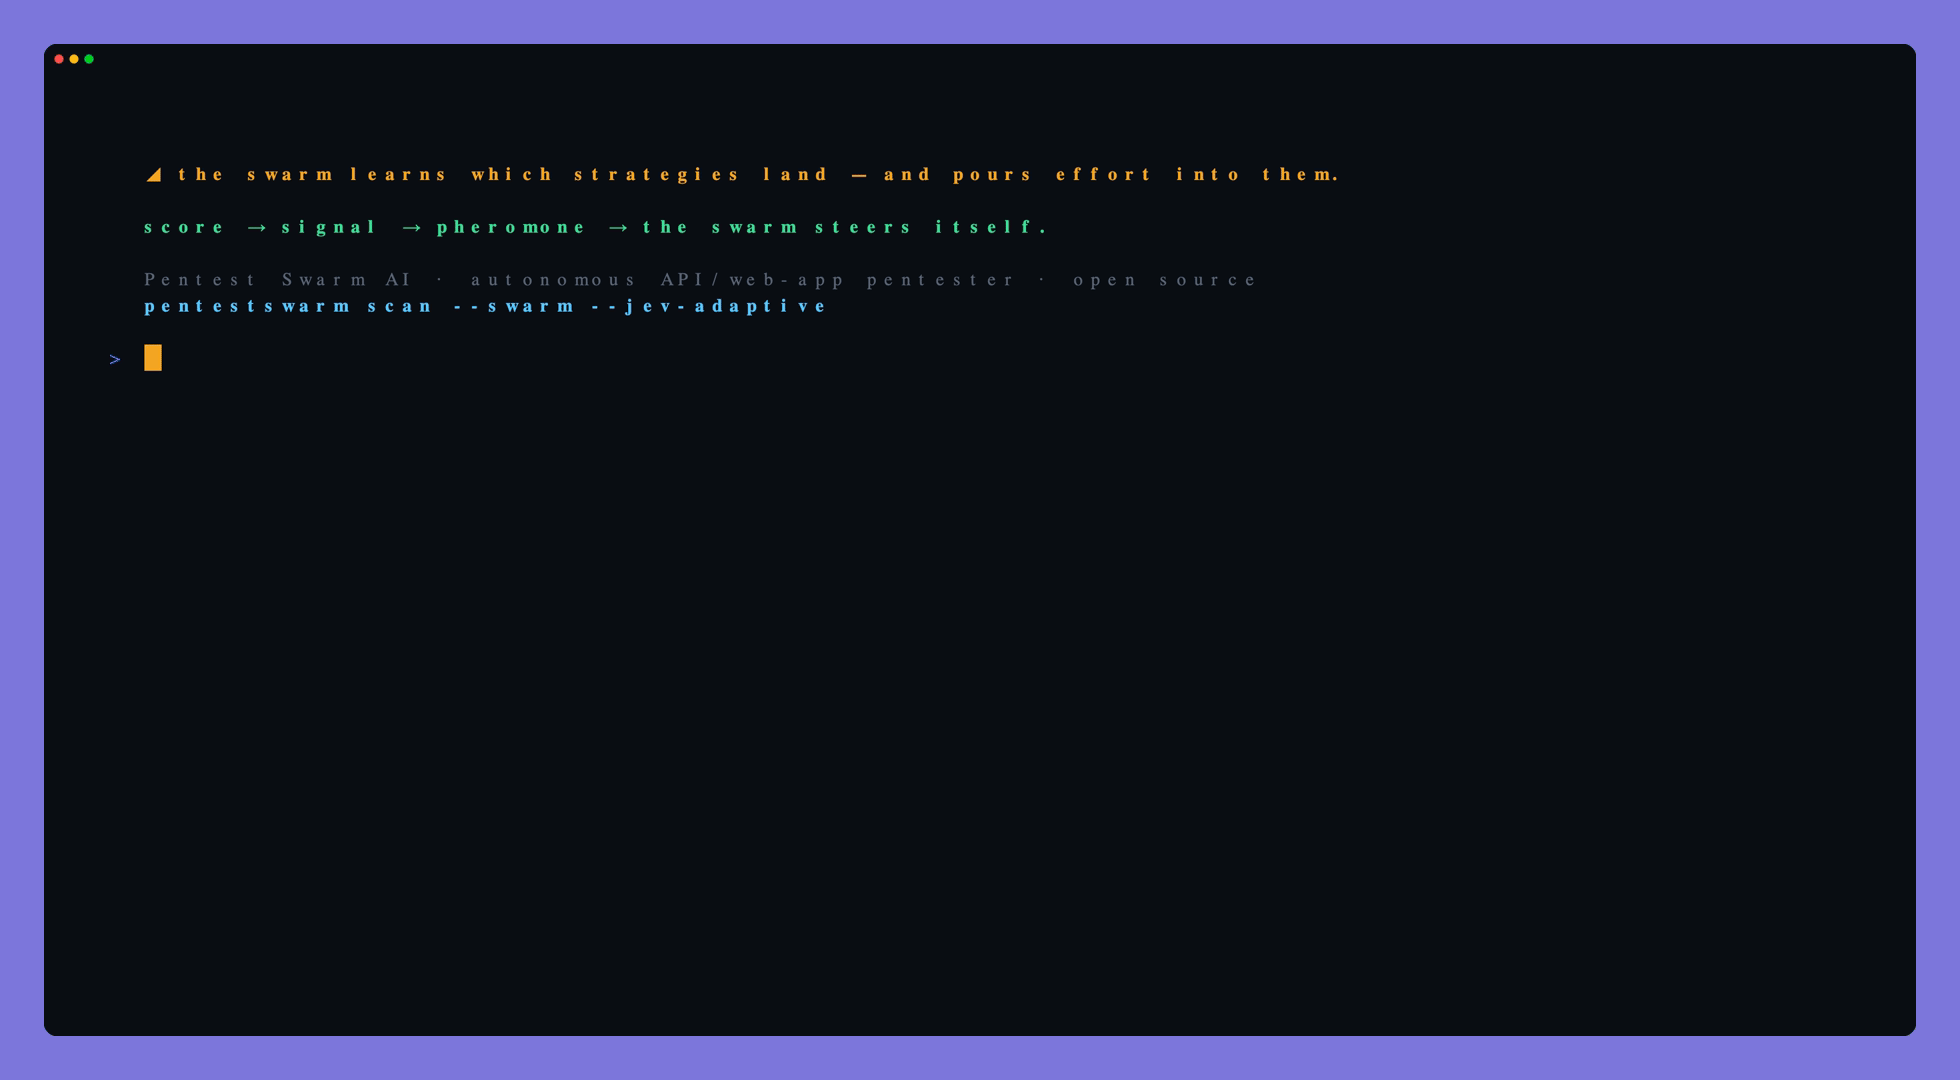
<img src="docs/adapti.gif" alt="Adapti scoring — the swarm generates candidate attack strategies, scores them with JE li, pursues the best, and reinforces what works " width="880">
</p>
<p align="center">
<a href=" Documentation</strong></a> ·
<a href="#quick-start">Quick Start</a> ·
<a href="#pentest-swarm-">vs. XBOW</a> ·
<a href="#what-makes-this-a-swarm">Swarm </a> ·
<a href="#how-the-swarm-works">How It Works</a> ·
<a href="ROADMAP.md">Roadmap</a>
</p>
<p align="center">
<a href=" src=" alt="Discord"></a>
<img src=" alt="Stars">
<img src=" alt="Go">
<img src=" alt="License">
<img src=" alt="AI">
<img src=" alt="Status">
</p>
<!-- Once trendshift.io lists the repo, replace the numeric id below.
PentAGI's badge (for reference):
<p align="center">
<a href=" target="_blank">
<img src="
alt="Armur-Ai/Pentest-Swarm-AI | Trendshift"
width="250" height="55"/>
</a>
</p>
-->
<p align="center">
<img src="docs/demo-flashy.gif" alt="Pentest Swarm AI — li demo" width="900">
</p>
Hack at machine speed.
> 📖 New here? Start with the documentation — quickstart, provider setup, CLI reference, and troubleshooting. (Or run pentestswarm docs to open it.)
XBOW proved a point: AI can top the bug-bounty leaderboards. But XBOW is a closed, hosted SaaS — one agent, on their cloud, on their model, at their price. We think the future of offense is open, self-hosted, and a swarm — so we built it.
Pentest Swarm vs. XBOW
| | Pentest Swarm AI | XBOW |
|---|:---:|:---:|
| Open source | ✅ AGPL, fork it | ❌ closed |
| Self-hosted | ✅ your infra, your model, $0 floor | ❌ their cloud, their bill |
| A real swarm | ✅ dozens of agents, concurrent | ❌ single agent |
Three structural wins — and the swarm is the one that compounds. This isn't a single planner LLM walking recon → classify → exploit → report down a fixed line. Dozens of agents work your surface at once, coordinating through a shared stigmergic blackboard: the instant a finding lands it wakes whiche it's relevant to, so a 1,000-subdomain target gets hit in parallel — attacking at machine speed. And unlike a scanner that spits out un "maybes," the swarm *exploits what it finds, proves it* with captured e, then writes the report.
Who it's for: pentesters co a whole scope o · bug bounty hunters racing to first-blood on a fresh target · red teamers who need breadth fast · researchers pushing autonomous offense.
Run it on any model — Claude, anything OpenAI-compatible (incl. Together AI's hosted Llama/Qwen/DeepSeek), the new security-tuned open models (Pentest-R1 and the wa it), or fully local Ollama / LM Studio. We don't compete with those models — we're the harness that gives them hands: real tools, swarm coordination, scope safety, and e reports. Air-gapped, zero API cost, and not one byte of your data leaving your box.
*For authorized testing only — see the disclaimer below.*
---
> ### Credits & Inspiration
> This project stands on the shoulders of giants. We credit and thank these projects for pioneering AI-powered offensi:
>
> - PentestGPT — the OG that proved LLMs can pentest
> - PentAGI — fully autonomous agent architecture
> - Strix — AI hackers that find and fix vulns
> - CAI — cybersecurity AI 框架, 3600x faster than humans
> - HackingBuddyGPT — LLM hacking in 50 lines of code
> - Shannon — white-box AI pentester
> - BlacksmithAI — multi-agent pentest framework
> - PentestAgent — black-box AI security testing
>
> Their open-源码 contributions made tools like this possible.
> Legal Disclaimer: Pentest Swarm AI is designed exclusively for authorized security testing, bug bounty programs, CTF competitions, and educational research. You must obtain explicit written permission from the target system owner before running any scan. Unauthorized access to computer systems is illegal under the Computer Fraud and Abuse Act (CFAA), the Computer Misuse Act, and equi laws worldwide. The authors and contributors of this project accept no liability for misuse, damage, or any illegal activity conducted with this 工具. By using this software, you agree that you are solely responsible for ensuring your use complies with all applicable laws and regulations. Do not use this 工具 against systems you do not own or ha authorization to test.
---
What makes this a swarm?
Most "multi-agent" pentesting tools are a single planner LLM dispatching to specialist agents in a fixed order — recon → classify → exploit → report. That's a pipeline, not a swarm.
Pentest Swarm AI is built around three swarm-intelligence primitives:
Why it wins: a pipeline is sequential (one stage at a time), can't fold a mid-run discovery back into recon, and is bounded by its slowest stage. A swarm works your surface concurrently, reacts to every new finding, lets attack chains emerge instead of scripting them, and lets stale paths decay and die. The payoff on stage is breadth — a long list of *proven* findings, because many agents chew on the surface at once.
📖 Full write-up: Architecture — Swarm (the blackboard, pheromone decay, emergent chains, and why concurrency stays cheap). Diagrams also live in docs/.
We built this because the category was empty. Every 工具 marketed as "swarm" was actually a pipeline. If you find a counter-example, open an issue — we'll add them to the comparison table.
---
Quick Start
One command to install. One command to run. No API key, no cloud, no bill to start.
1 · Install (pick one)
2 · Run it
That's it. run opens the interactive TUI launcher — no flags to memorize:
localhost:7777 *and* a full-screen terminal TUI with li, a swarm-topology diagram, and a graded findings stream. Both, by default.A readiness check runs right in the launcher (Go, Docker, tools, provider) — it ne; anything missing is shown as a note you can fix or ignore.
Prefer flags? (scripting / CI)
run just wraps scan, so e is scriptable too:
New here? pentestswarm demo plays the whole campaign offline — that's the GIF abo inside GitHub Actions? See deploy/github-action/example-workflow.yml.
---
How the swarm works
<p align="center">
<img src="docs/architecture.svg" alt="Pentest Swarm AI architecture — a seed feeds a shared pg blackboard that triggers four independent agents (recon, classify, exploit, report) by pheromone threshold; exploit results feed back to wake other agents" width="900">
</p>
Key beha:
1. Agents are independent. Any one of them can be removed, replaced, or added without rewiring the others.
2. Pheromones decay per-finding-type. A PORT_OPEN stays hot for hours; a SESSION for minutes. Config-dri.
3. Scope is enforced at the 工具 layer and again at the executor. Defence in depth — --scope is not bypassable.
4. Cleanup is always registered before execution. SIGINT, crashes, and budget exhaustion all trigger re cleanup. See internal/pipeline/cleanup_memory.go and cleanup.go.
5. Prompt caching on Claude cuts cost and latency on repeated system prompts (enabled by default for recon + classifier).
<p align="center">
<img src="docs/pheromone-lifecycle.svg" alt="Pheromone lifecycle — a finding's weight spikes to 1.0 when written and decays over time; above 0.5 the exploit agent fires, above 0.2 the classifier fires, below 0.2 it goes stale. Different finding types decay at different rates." width="820">
</p>
---
Comparison
How we position vs. the rest of the ecosystem. We'll ship real benchmark numbers in a future release (see the benchmarks roadmap).
| Tool | Open / self-host | Architecture | Executes | Memory | Tools wired | MCP | Swarm? |
|---|---|---|---|---|---|---|---|
| Pentest Swarm AI | ✅ open, self-hosted | Stigmergic blackboard | Executes | pg + pheromones | 8 ProjectDiscovery + nmap; sqlmap / Burp MCP / Metasploit in roadmap | Yes | ✅ real |
| XBOW | ❌ closed SaaS | Autonomous agent (hosted) | Executes | Hosted | Managed | No public API | No |
| PentestGPT | ✅ open | Single-agent ReAct | Suggests | None | None native | No | No |
| HackingBuddyGPT | ✅ open | Single-agent | Executes | Run logs | Shell passthrough | No | No |
| PentAGI | ✅ open | 4 agents + planner | Executes | pg | 40+ via MCP/shell | Partial | Pipeline |
| Shannon | ✅ open | White-box + browser | Executes | Session state | Browser DOM | No | Pipeline |
| HexStrike | ✅ open | MCP tool wrapper | Delegates to client LLM | None (stateless) | 150+ via MCP | Yes | No |
| Pentest-R1 | ✅ open (model) | RL-tuned LLM | Executes | Trajectory | CTF-scope | No | No |
If any entry here is wrong or out of date, please open a PR — we want this table to stay honest.
---
Feature status
Honesty labels: *stable* means shipped + tested, *beta* means works but rough edges, *alpha* means experimental, *planned* means in the roadmap.
| Feature | Status | Notes |
|---|---|---|
| Sequential 5-phase runner | stable | Default mode; battle-tested core |
| Stigmergic swarm scheduler | alpha | --swarm flag; memory-backed blackboard wired |
| ProjectDiscovery toolchain | stable | subfinder, httpx, nuclei, naabu, katana, dnsx, gau |
| nmap adapter | stable | XML parsed; scope- |
| Cleanup registry | stable | Always runs on SIGINT / exit / budget-cancel |
| Claude prompt caching | stable | Enabled for recon + classifier by default |
| --strict LLM mode | stable | Promotes LLM errors to fatal |
| CVSS v3.1 scoring | stable | FIRST spec |
| Je filter | beta | --jev; optional second-opinion pass 's Jev — off by default, fails open. Docs |
| Je attack-path scoring | beta | --je; the swarm scores its candidate attack strategies with Jev in real time and pursues the best first (graded pheromone). Off by default, fails open. |
| Exploit chains | beta | chain run/list/update; a growing library of named, C exploit chains (SSRF→RCE, auth-bypass→RCE…) — fingerprint + safe + report. Lean binary + on-demand updates. Docs |
| Chain Forge | beta | chain forge; draft a new exploit chain from an ad using any configured reasoning model (Ollama/Together/Claude/Muse Spark…) — safe , , human-re before it ships. |
| Postgres blackboard backend | beta | Migration shipped; runner uses memory-board for now |
| MCP server | beta | pentestswarm mcp serve |
| VS Code extension | beta | deploy// |
| GitHub Action | beta | deploy/github-action/action.yml with SARIF |
| Swarm playbooks (5) | beta | playbooks/{bug-bounty,external-asm,ci-cd,internal-network,ctf-solver}.yaml |
| Li | alpha | web/; UI built, wiring to li in progress |
| Burp MCP bridge | planned | Wave 2 |
| Metasploit / ZAP / sqlmap adapters | planned | Wave 2 |
| Fine-tuned Pentest-Swarm model | planned | Wave 3 (Pentest-R1 recipe) |
| Cybench / AutoPenBench benchmarks | planned | Wave 3 |
---
CLI
pentestswarm run is the front door — an interacti (provider + key entry, target or bundled lab, li choice, readiness checks) so you never have to remember flags. The scan form stays fully scriptable for CI.
---
LLM Pro
All agents inherit from a single provider config. Set one key, the entire swarm works.
Bring your own model — we're the harness, not the model. A new wave of open models is topping the cyber-offense benchmarks — GLM (5.3), Qwen (3.x), DeepSeek, and security-tuned fine-tunes like Pentest-R1. Pentest Swarm turns any of them — or a frontier model, or a fully-local one — into an *operating* pentester: real tools, swarm coordination, scope enforcement, and e reports. The model does the reasoning; the swarm does the work.
Together AI is first-class — pick together (in pentestswarm run or --provider together) and just add your key; the endpoint is handled for you. Any other OpenAI-API-compatible endpoint (OpenAI, DeepSeek, Groq, …) works via openai + a base-URL, plus first-party Gemini. The only hard requirement is native 工具/function calling, which GLM, Qwen, and DeepSeek all support.
<p align="center">
<img src="docs/pro.svg" alt="One key, whole swarm — one API key configures the orchestrator and all four agents inherit that provider by default; swap Claude / OrcaRouter / Ollama / LM Studio and the whole swarm follows" width="820">
</p>
| Provider | provider: | Setup | Privacy | Best for |
|----------|-------------|-------|---------|----------|
| Claude (default) | claude | export PENTESTSWARM_ORCHESTRATOR_API_KEY=... | Cloud | Best quality, zero setup, prompt caching |
| Together AI | together | Just set the key — endpoint auto-configured | Cloud | Open cyber-benchmark leaders: GLM zai-org/GLM-5.3, Qwen Qwen/..., DeepSeek, Kimi |
| OpenAI-compatible | openai | Set key + the 's /v1 endpoint | Cloud | OpenAI, DeepSeek, Groq, or any Chat-Completions API |
| Gemini | gemini | export PENTESTSWARM_ORCHESTRATOR_API_KEY=AIza... | Cloud | Large context, free tier |
| Ollama | ollama | Install Ollama + pull models | 100% local | Full privacy, air-gapped (GLM / Qwen builds a) |
| LM Studio | lmstudio | Load model, enable server | 100% local | GUI model management |
| OrcaRouter | orcarouter | export PENTESTSWARM_ORCHESTRATOR_API_KEY=sk-orca-... | Cloud | One endpoint for Claude/GPT + other frontier models, gateway-le |
Together AI example — run the whole swarm on GLM 5.3:
---
Tech Stack
| Component | Technology | Why |
|-----------|-----------|-----|
| Platform | Go 1.24 | Single binary, goroutine concurrency, nati tools |
| CLI | Cobra + bubbletea | Beautiful TUI with multi-panel agent view |
| LLM | Claude / Together AI (GLM · Qwen · DeepSeek) / Gemini / OrcaRouter / Ollama / LM Studio | Best quality cloud + open cyber-bench leaders + full privacy local |
| Security Tools | subfinder · httpx · nuclei · naabu · katana · dnsx · gau · nmap | ProjectDiscovery Go libs + nmap subprocess |
| Blackboard | Postgres 16 + pg | Transactional writes, similarity, pheromone decay in SQL |
| Cache | Redis 7 | Rate limiting, session state |
| Dashboard | Next.js 15 + shadcn/ui + tremor | Dark-first, chart-heavy |
| MCP | JSON-RPC stdio | Claude Desktop + Cursor integration |
---
De
Regenerate the demo GIF after any CLI change:
---
Roadmap
🧠 The Adapti — headline releases
Today the swarm reacts to findings and runs attack playbooks (BOLA/IDOR, mass assignment, NoSQL injection, excessive data exposure) end-to-end. Next, we make it *think* — three major capabilities, each shipping as its own release:
Together these turn a reacti into an adaptive one — attack surface it has never seen, handled without anyone writing a plan. Generalization beyond curated targets and full LLM-dri ride on top of these.
Follow the GitHub Project board for li.
---
Why "Swarm"?
Single agents are tools. Pipelines dressed up as agents are slightly fancier tools. A swarm is different: agents share an en, each agent's writes influence other agents' behaviour, and the useful work is emergent rather than prescribed. That's what lets a swarm handle a 1,000-subdomain target without anyone writing a plan for it.
One agent is a 工具. A swarm is a platform.
---
Community
Join the swarm on Discord → 🐝
We're building the first *real* open-源码 pentest swarm in the open — come build it with us. In Discord you can share findings, request a 工具 adapter, argue about stigmergy and pheromone decay, get help running your first scan, or grab a good first issue and ship a PR. Researchers, red-teamers, and the AI-security-curious all welcome.
> ⭐ If a real open-源码 swarm is something you want to exist, drop a star. Star is the fuel that keeps this shipping — it's the single biggest thing you can do in ten seconds.
---
Who's using Pentest Swarm?
Running Pentest Swarm — internally, on 客户端 engagements, in CI, or embedded in your own workflow? Add your org to ADOPTERS.md with a quick PR — it helps others trust the project and helps us prioritize what to build. Not ready to be listed publicly? A hello in Discord still helps.
---
Community
Pentest Swarm AI is free and open 源码 (AGPL-3.0), and always will be — and we don't hold the good stuff back. The community edition is a fully capable autonomous API/web-app pentester: it exploits and chains attacks (BOLA/IDOR, JWT, SSRF, SQLi, GraphQL, BFLA…), builds and scores attack paths, and ships a large, growing library of attack-path + C.
The Enterprise edition — from Armur AI, the team behind the project — adds what teams need to run it at scale, in production, and always current:
| | Community (free, self-host) | Enterprise |
|---|---|---|
| Exploit classes (BOLA · JWT · SSRF · SQLi · GraphQL · BFLA …) | ✅ all | ✅ all |
| Attack-path / C library | ✅ large, updated each release | ✅ live feed — new critical-C within hours, |
| Adapti | ✅ swarm + adapti scoring | ✅ cross-engagement learning, deeper agent coordination, premium models |
| Team & platform | single user, CLI/TUI + local dashboard | ✅ multi-user, RBAC, SSO, hosted/managed, scheduling, audit, compliance reports |
| Integrations | local reports (SARIF) | ✅ Jira/Ser, SIEM/SOAR, Burp, CI/CD, cloud, API + webhooks |
| Support | community / Discord | ✅ SLA support, onboarding, custom chains, managed pentest service |
Enterprise services in detail:
> Some Enterprise capabilities are a today and others are on the near-term roadmap — tell us what you need and we'll tell you exactly where it stands.
📧 — tell us your setup and what you're trying to do, and we'll get you set up.
---
License
GNU Affero General Public License v3.0 (AGPL-3.0) — see LICENSE.
What this means for you
| Use case | Allowed? |
|---|---|
| Run Pentest Swarm on your own infrastructure (CI, laptop, internal red team) | ✅ yes, no obligations |
| Use it on authorized bug-bounty programs / pentests | ✅ yes, no obligations |
| Fork it for your own private experiments | ✅ yes, no obligations |
| Distribute a modified binary | ✅ yes — must share your modifications under AGPL |
| Run a modified as a paid SaaS or network service | ✅ yes — must share your modifications under AGPL |
The AGPL exists specifically to prevent the SaaS-fork loophole: anyone who impro Swarm and offers it commercially must share their impro with the community. We made it open 源码; we want it to *stay* open 源码 even as it scales.
If you have a use case the table doesn't cover, open an issue and ask.
Built by Armur AI.
项目信息
开发语言:Go
Star 数:2737
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Autonomous penetration testing using a swarm of AI agents. Orchestrates recon, classification, exploitation, and reporting specialists with ReAct reasoning — supports bug bounty, continuous monitoring, and CTF modes. Built with Go and 7+ nati tools.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Pentest-Swarm-AI - 使用一群人工智能进行自主渗透测试 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:04:54 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 107 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |