 黑客技术
点击放大
项目说明
Sudomy
![License]() ![Build Status]() ![]() ![Build]() ![Build]() ![Contributions Welcome]() ![Donate]()
Subdomain Enumeration & Analysis
<img width="935" alt="sudomy" src="
*Sudomy* is a subdomain enumeration 工具 to collect subdomains and analyzing domains performing ad automated reconnaissance (框架). This 工具 can also be used for OSINT (Open-源码 intelligence) acti.
Features !
##### For recent time, *Sudomy* has these 20 features:
- Acti
- *Sudomy* utilize Gobuster tools because of its highspeed performance in carrying out DNS Subdomain Bruteforce attack (wildcard support). The wordlist that is used comes from combined SecList (Discover/DNS) lists which contains around 3 million entries
- Passi
- By e and selecting the good third-party sites/resources, the enumeration process can be optimized. More results will be obtained with less time required. *Sudomy* can collect data from these well-curated 22 third-party sites:
How Sudomy Works
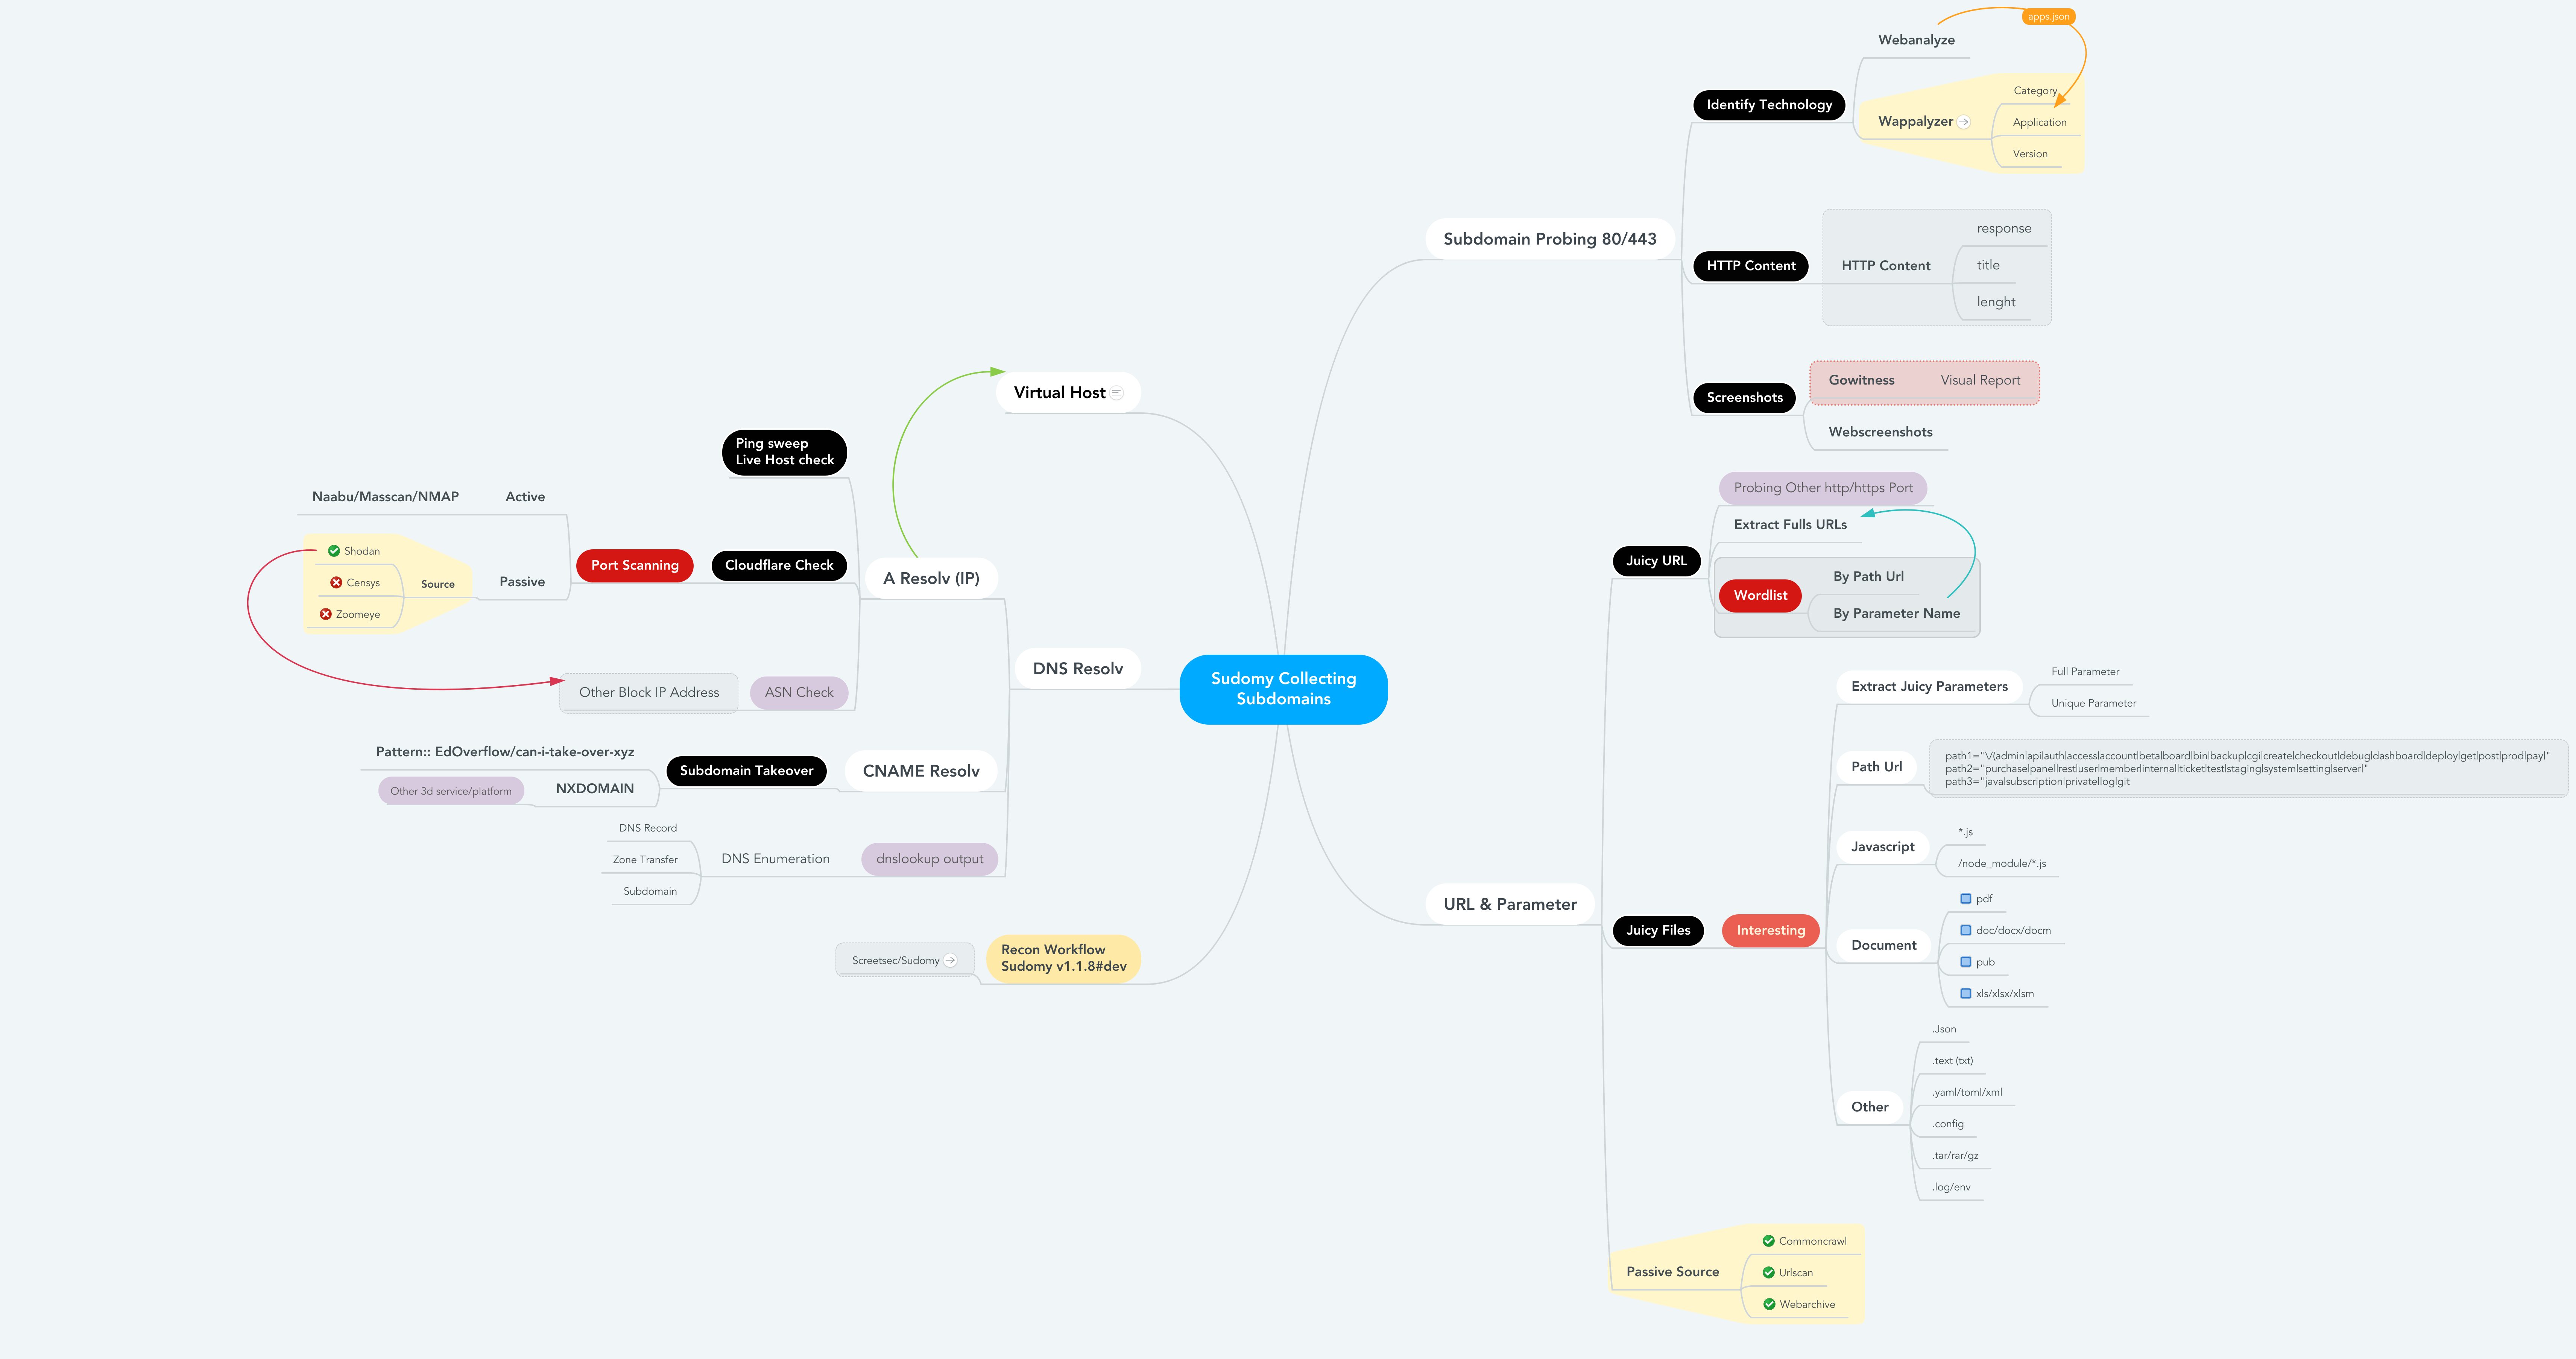
How sudomy works or recon flow, when you run the best arguments to collect subdomains and analyze by doing automatic recon.
Recon Worfklow
This Recon Workflow Sudomy v1.1.8#dev
!Recon Workflow
Detail information
Detail information File Reconnaissance & Juicy Data
Publication
User Guide
Comparison
Sudomy minimize more resources when use resources (Third-Party Sites) By e and selecting the good third-party sites/resources, so the enumeration process can be optimized. The domain that is used in this comparison is *tiket.com*.
The following are the results of passi DNS testing of *Sublist3r v1.1.0, Subfinder v2.4.5*, and *Sudomy v1.2.0*.
<img width="935" alt="Untitled" src="
In here subfinder is still classified as very fast for collecting subdomains by utilizing quite a lot of resources. Especially if the resources used have been optimized (?).
For compilation results and , you can check here:
When I have free time. Maybe In the future, sudomy will use golang too. If you want to contributes it's open to pull requests.
But it's shit! And your implementation sucks!
Installation
*Sudomy* is currently extended with the following tools. Instructions on how to install & use the application are linked below.
To Download Sudomy From Github
Dependencies
*Sudomy* requires jq and GNU grep to run and parse. Information on how to download and install jq can be accessed here
Running in a Docker Container
Post Installation
API Key is needed before querying on third-party sites, such as and .
YOUR_WEBHOOK_URL is needed before using the slack notifications
Usage
To use all 22 Sources and Probe for working http or https servers ():
To use one or more source:
To use all Sources Without :
To use one or more plugins:
To use all plugins: testing host status, http/https status 代码, subdomain takeover and screenshots.
Nmap,Gobuster,wappalyzer and wscat Not Included.
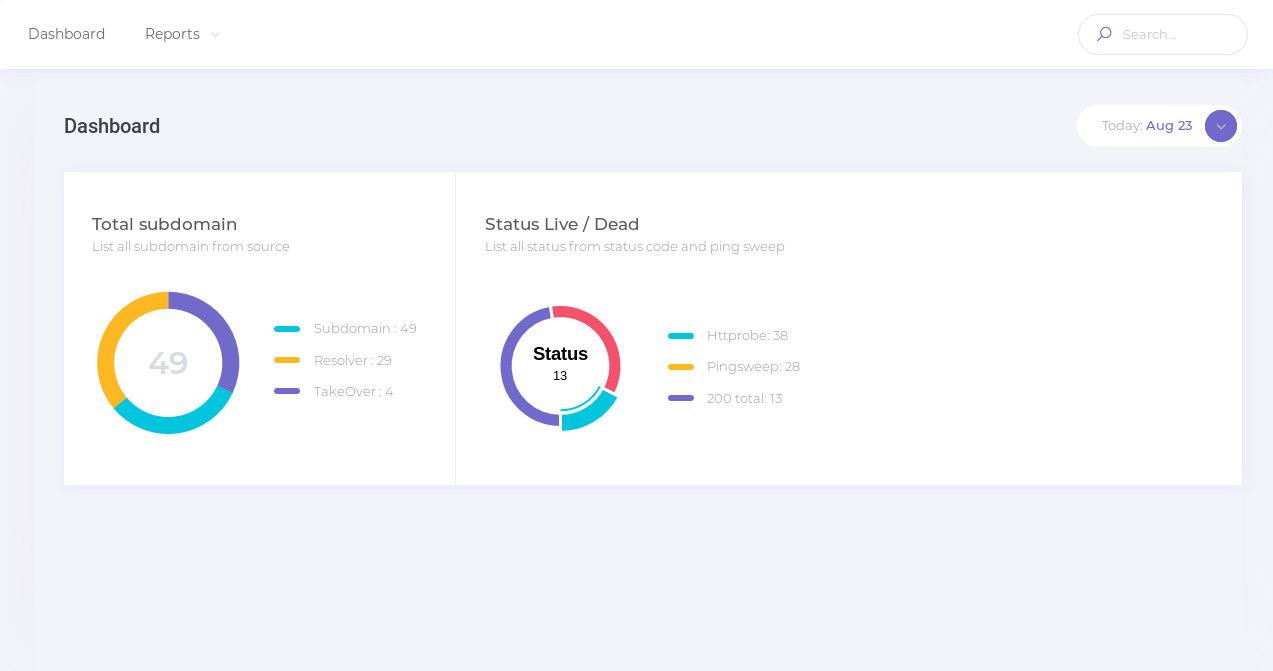
To create report in HTML Format
HTML Report Sample:
| Dashboard | Reports |
| ------------ | ------------ |
|!Index|!f|
To gnereate 网络 graph subdomain &
Graph Sample:
| nGraph |
| ------------ |
|!nGraph|
To use best arguments to collect subdomains, analyze by doing automatic recon and sending notifications to slack
Slack Notification Sample:
| Slack |
| ------------ |
|!Slacks|
Tools O
Translations
Changelog
All notable changes to this project will be documented in this file.
Alternative Best 工具 - Subdomain Enumeration
Credits & Thanks
项目信息
开发语言:Shell
Star 数:2433
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Sudomy is a subdomain enumeration 工具 to collect subdomains and analyzing domains performing automated reconnaissance (recon) for bug hunting / pentesting展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Sudomy - Sudomy是一个子域枚举工具,用于收集 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:05:32 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 456 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |