 黑客技术
点击放大
macro_pack - macro_pack is a tool by @EmericNasi used to automa
项目说明
!Supported Python
macro\_pack
Short description
----------------------------------------------------------------
Warning: MacroPack is not maintained since 2021, if you are a pro and need Offensi tools for initial access, assume breach, EDR bypass, check
----------------------------------------------------------------
MacroPack Community is a 工具 used to automatize obfuscation and generation of retro formats such as MS Office documents or VBS like format.
It also handles shortcuts formats.
This 工具 can be used for red teaming, pentests, demos, and social engineering assessments.
MacroPack will simplify antimalware solutions bypass and automatize the process from to final Office document or other payload type.
It is very simple to use:
* No configuration required
* E can be done using a single line of 代码
* Generation of majority of Office formats and formats
* Payloads designed for ad social engineering attacks (email, USB key, etc)
The 工具 is compatible with payloads generated by popular pentest tools (Metasploit, Empire, ...).
It is also easy to combine with other tools as it is possible to read input from stdin and have a quiet output to another 工具. T
his 工具 is written in Python3 and works on both Linux and Windows platforms
Note: Windows platform with the right MS Office applications installed is required for Office documents automatic generation or trojan features.
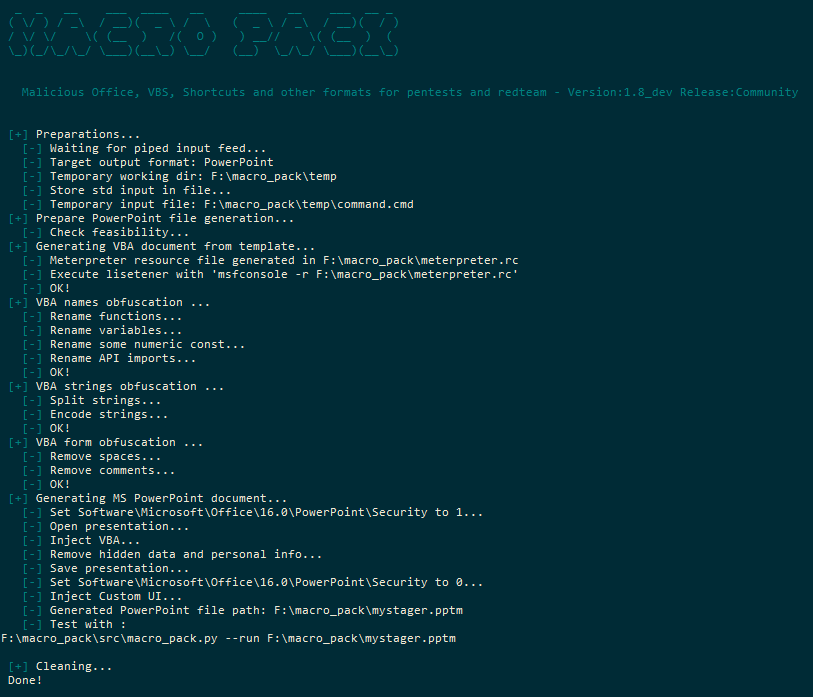
<p align="center"><img src="./assets/mp_intro.png" alt="Demo 1"></p>
Obfuscation
The 工具 will use obfuscation techniques, all automatic.
Obfuscation features are compatible with all VBA and format which can be generated by MacroPack.
Basic obfuscation (-o option) includes:
* Renaming functions
* Renaming
* Removing spaces
* Removing comments
* Encoding Strings
Generation
MacroPack can generate several kinds of MS office documents and scripts formats.
The format will be automatically guessed depending on the given file extension.
File generation is done using the option --generate or -G.
MacroPack pro also allows you to trojan existing Office files with option --trojan or -T.
Ms Office Supported formats are:
* MS Word (.doc, .docm, .docx, .dotm)
* MS Excel (.xls, .xlsm, .xslx, .xltm)
* MS PowerPoint (.pptm, .potm)
* MS Access (.accdb, .mdb)
* MS Visio (.vsd,.vsdm)
* MS Project (.mpp)
Scripting (txt) supported formats are:
* VBA text file (.vba)
* VBS text file (.vbs).
* Windows Script File (.wsf)
* Windows Script Components scriptlets (.wsc, .sct)
* HTML Applications (.hta)
* XSLT Stylesheet (.xsl) (Yes MS XSLT contains scripts ^^)
Shortcuts/Shell supported formats are:
* Shell Link (.lnk)
* Explorer Command File (.scf)
* URL Shortcut (.url)
* Groo (.glk)
* Settings Shortcuts (.settingcontent-ms)
* MS Library (.library-ms)
* Setup Information (.inf)
* Excel Web Query (.iqy)
* Studio Project (.csproj)
* Command line (.cmd)
* SYmbolic LinK (.slk) Pro only
* Compressed HTML Help (.chm) Pro only
Note that all scripting and shortcuts formats (except LNK) can be generated on Linux of MacroPack as well.
Ethical use
This software must be used only in the context of a Red Team engagement, penetration testing, phishing simulation,
security research, or other form of security assessments, with the lawful and formal authorization of the system owners.
Usage of this software for attacking targets without prior consent is forbidden and illegal.
It is the User’s responsibility to comply with all applicable local, state, federal and national laws.
We assume no liability and are not responsible for any misuse or damage that may be caused by using this software.
About pro mode...
Not all capabilities and options of MacroPack are a on MacroPack Community.
Only the community is a online.
Features of the pro are truly "weaponizing" the process, hence their access is restricted to professionals.
The pro mode includes features such as:
* Advance antimalware bypass
* Ad Shellcode injection methods
* Command line obfuscation (Dosfuscation)
* ASR and AMSI bypass
* Self unpacking VBA/
* Trojan existing MS Office documents, Help files and Studio projects.
* Embed decoy payload
* Lateral mo using DCOM objects
* Anti reverse engineering
* Sandbox detection
* Support of more formats such as Excel 4.0 SYLK and compiled help files
* Run ad from unusual formats
* Weaponized templates and additional templates (ex EMPIRE, AUTOSHELLCODE)
* Excel 4.0 macros (XLM)
* And much more…
Some short demo are a on the BallisKit Vimeo channel.
Important: If you wish to contact me about MacroPack pro, use my emeric.nasi [at] sevagas.com email address.
I will not answer anonymous inquiries for the Pro but only professional emails.
Run/Install
Run Windows binary
1) Get the latest binary from
2) Download binary on PC with genuine Microsoft Office installed.
3) Open console, CD to binary dir and call the binary, simple as that!
Install from sources
You need to be on a Windows machine to build MacroPack. Download and install dependencies:
The 工具 is in python 3, so just start with your python3 install. ex:
If you want to produce a standalone exe using pyinstaller:
* Install pyinstaller: pip install pyinstaller
* Double-click on the "build.bat" script.
The resulted macro\_pack.exe will be inside the bin directory.
Some examples
MacroPack Community
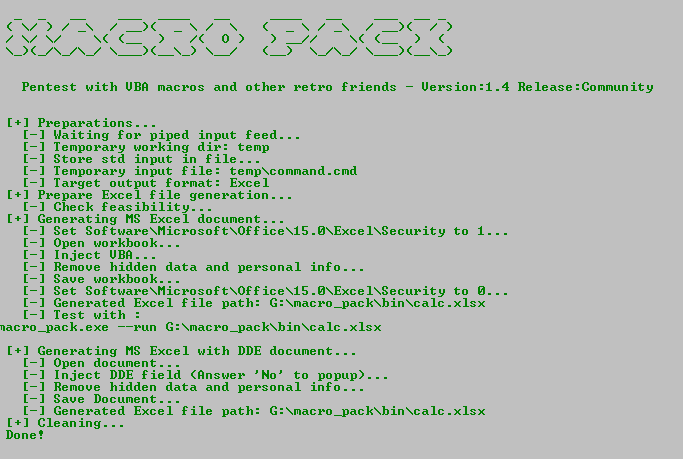
<p align="center"><img src="./assets/excel_dde.png" alt="Excel DDE demo"></p>
<p align="center"><img src="./assets/iqy_dde.PNG" alt="IQY demo"></p>
- Generate obfuscated meterpreter reverse TCP VBS file and run it
Some MacroPack Pro examples
Keep-alive is needed because we need meterpreter to stay ali we migrate.
All community options
Template usage
Templates can be called using -t, --template=TEMPLATE_NAME combined with other options.
Here are all the a templates.
HELLO
Just print a hello message and awareness about macro.
Give this template the name or email of the author:
-> Example:
CMD
Execute a command.
Give this template a command line
-> Example (pop calc.exe from and xslt file):
REMOTE_CMD
Execute a command line and send results to remote HTTP 服务端.
Give this template the 服务端 url and the command to run:
-> Example:
DROPPER
Download and execute a file.
Give this template the file url and the target file path
-> Example:
DROPPER_PS
Download and execute Powershell script using rundll32 (to bypass blocked powershell.exe).
Note: This payload will download PowerShdll from Github.
Give this template the url of the powershell script you want to run:
-> Example:
DROPPER_DLL
Download a DLL with another extension and run it using Office VBA.
-> Example, load meterpreter DLL using Office:
METERPRETER
Meterpreter reverse TCP template using MacroMeter by Cn33liz.
This template is CSharp meterpreter Stager build by Cn33liz and embedded within DotNetToJScript from James Forshaw.
Give this template the IP and PORT of listening mfsconsole:
-> Example:
This template also generates a meterpreter.rc file to create the Metasploit handler
-> Example:
EMBED_EXE
Drop and execute an embedded file.
Combine with --embed option, it will drop and execute the embedded file with random name under TEMP folder.
-> Example:
EMBED_DLL
Combine with --embed option, it will drop and call a function in the given DLL.
Give this template the name and parameters of function to call in DLL
-> Example1 :
-> Example2 :
Efficiency
The features were tested against locally installed Antimalware solutions as well as online services.
I ran multiple tests with several kinds of payloads and MacroPack features.
A majority of antivirus static will be evaded by the simple "obfuscate" option.
However, as most free tools, payloads are generally caught by beha analysis such as AMSI.
Features a in MacroPack pro mode generally permit full A including AMSI.
Warning: Do not submit your samples to online scanners (ex ), It's the best way to break your stealth macro.
I also suggest you do not submit to non-reporting sites such as NoDistribute.
You cannot be sure what these sites will do with the data you submit. If you have an issue with macro_pack A, you can write to us for advice or submit an issue or pull request.
Relevant resources
Blog posts about MacroPack Pro:
-
- (Excel 4.0 payloads in MacroPack Pro)
- (XLM injection in MacroPack Pro)
Blog posts about hacking with MS Office, VBS, and other retro stuff security:
-
-
- (write a full VBA RAT, includes how to bypass VBOM protection)
- (run hta 代码 in non-hta files and hta polyglots)
- (About Dynamic Data Exchange attacks)
-
Other useful links:
- (Run PowerShell with dlls only)
- (Run powershell script with PowerShdll )
-
-
-
-
-
-
Contact
Feel free to message me on my Twitter account
Emails:
* emeric.nasi[ at ]sevagas.com
* ena.sevagas[ at ]protonmail.com
Important: If you wish to contact me about MacroPack pro, use my sevagas.com email address.
Also please note that I will not answer anonymous inquiries for the Pro , only professional emails.
License and credits
The Apache License 2.0
Copyright 2017,2018,2019,2020,2021,2022 Emeric “Sio” Nasi (blog.sevagas.com)
项目信息
开发语言:Python
Star 数:2302
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕macro_pack is a 工具 by used to automatize obfuscation and generation of Office documents, , shortcuts, and other formats for pentest, demo, and social engineering assessments. The goal of macro_pack is to simplify exploitation, antimalware bypass, and automatize the process from malicious macro and script generation to final document generation. It also provides a lot of helpful features useful for redteam or security research. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | macro_pack - macro_pack is a tool by @EmericNasi used to automa |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:05:44 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 246 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |