 黑客技术
点击放大
vulnx - vulnx 🕷️ an intelligent Bot, Shell can achieve aut
项目说明
<h1 align="center">
<br>
<a href=" src=" alt="VulnX"></a>
<br>
VulnX
<br>
</h1>
<h4 align="center">Vulnx 🕷️ is An Intelligent Bot Auto Shell Injector that detects in multiple types of Cms </h4>
<p align="center">
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
</p>
!Screenshot from 2019-06-19 05-22-04
<p align="center">
<a href=" Wiki</a> •
<a href=" To Use</a> •
<a href=" •
<a href=" •
</p>
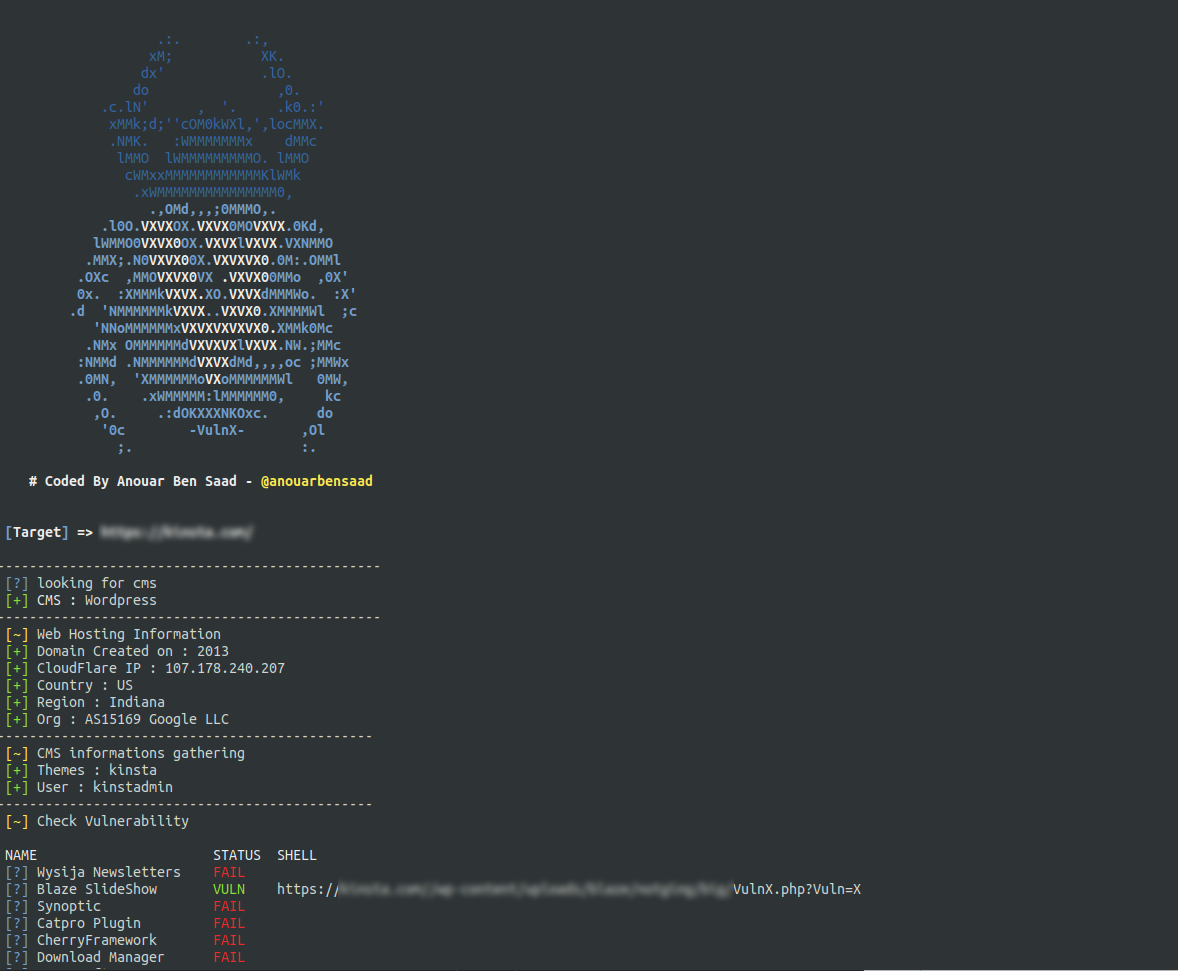
Vulnx is An Intelligent Bot Auto Shell Injector that detects in multiple types of Cms, fast cms detection,informations gathering and Scanning of the target like subdomains, ipaddresses, country, org, timezone, region, ans and more ...
Instead of injecting each and every shell manually like all the other tools do, VulnX analyses the target website checking the presence of a if so the shell will be Injected.searching urls with dorks 工具.
-------------------------------------
_🕷️ Features_
Ports Scan High LevelDns-Servers Dump-------------------------------------
_🕷️ DNS-Map-Results_
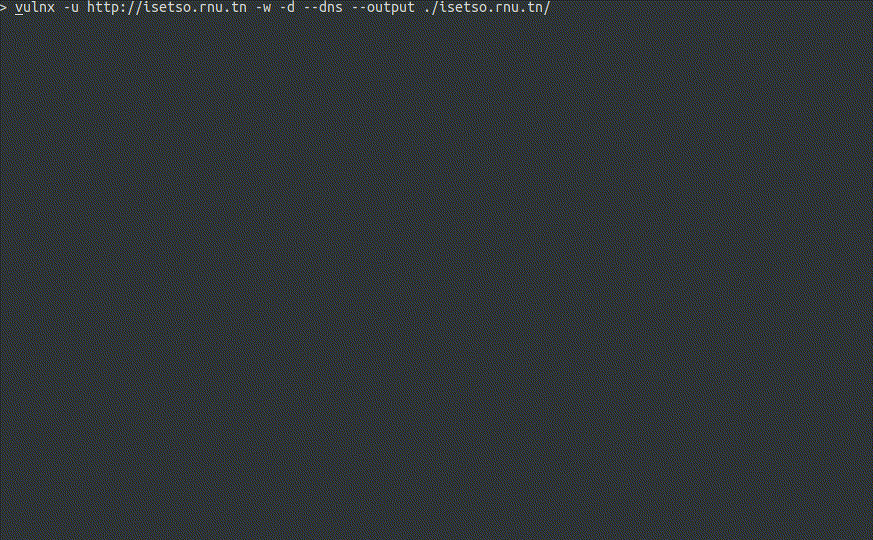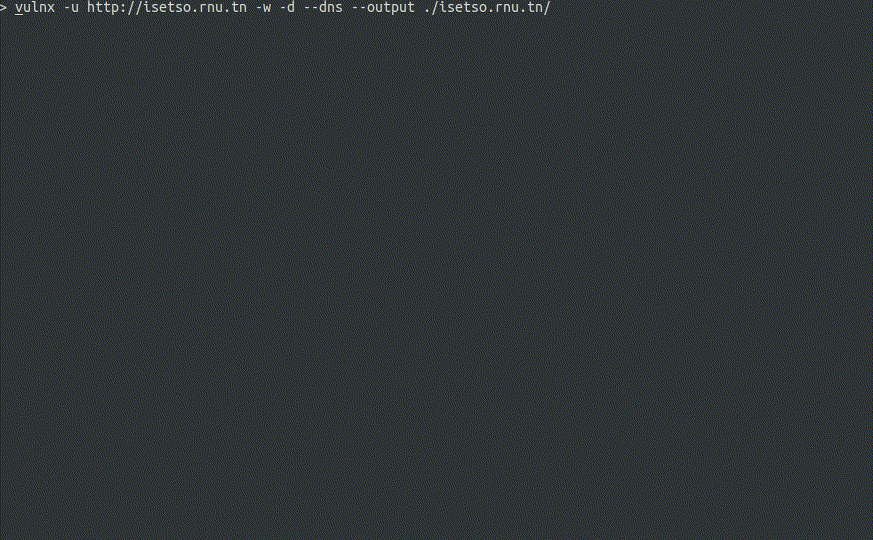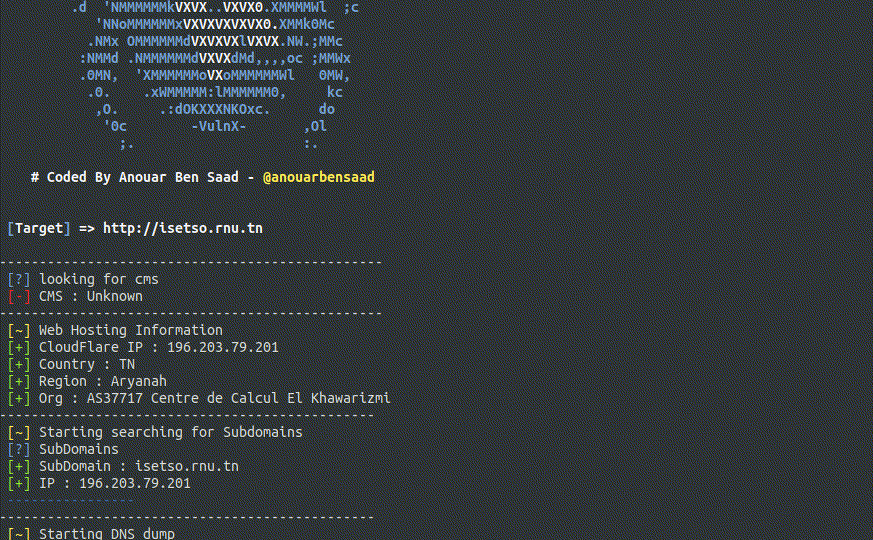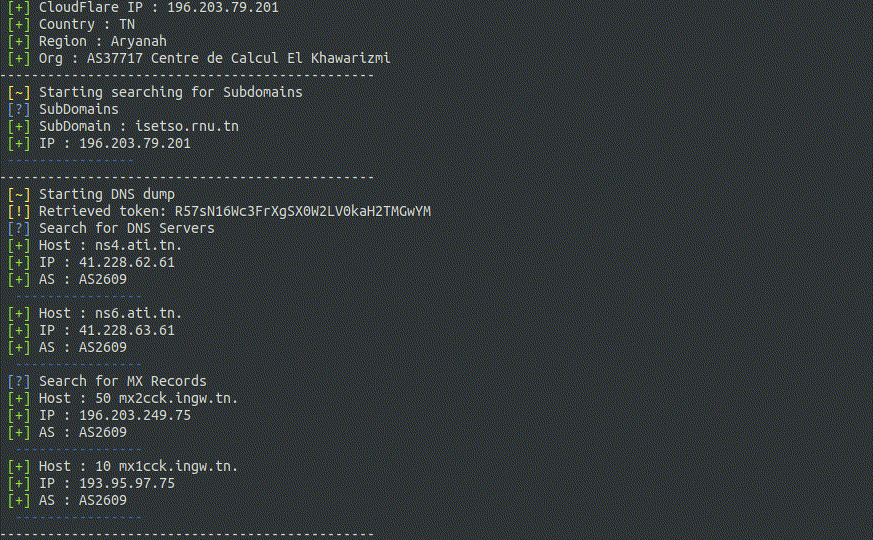
To do this,run a scan with the --dns flag and -d for subdomains.
To generate a map of isetso.rnu.tn, you can run the command vulnx -u isetso.rnu.tn --dns -d --output $PATHin a new terminal.
$PATH : Where the graphs results will be stored.
!-44-07
Let's generates an image displaying target Subdomains,MX & DNS data.
!demo
-------------------------------------
_🕷️ Exploits_
<h1 align="center">
<a href=" src=" alt="Exploits Running"></a>
</h1>
##### Joomla
##### Wordpress
##### Drupal
##### PrestaShop
##### Opencart
-------------------------------------
_🕷️
NEWvulnx now have an interactive mode.
*URLSET*
!
*DORKSET*
!
-------------------------------------
_🕷️ A command line options_
READ VULNX WIKIusage: vulnx [options]
-u --url url target
-D --dorks search webs with dorks
-o --output specify output directory
-t --timeout http requests timeout
-c --cms-info search cms info[themes,plugins,user,..]
-e --exploit searching & run exploits
-w --web-info web informations gathering
-d --domain-info subdomains informations gathering
-l, --dork-list list names of dorks exploits
-n, --number-page number page of search 引擎(Google)
-p, --ports ports to scan
-i, --input specify domains to scan from an input file
--threads number of threads
--dns dns informations gathering
-------------------------------------
_🕷️ Docker_
VulnX in DOCKER !!.
run vulnx container in interactive mode
!-53-20
to view logfiles mount it in a like so:
change the mounting directory..
-------------------------------------
_🕷️ Install vulnx on Ubuntu_
Now run vulnx
!-59-48
_🕷️ Install vulnx on Termux_
CLICK HERE TO SHOW THE RESULT
_🕷️ Install vulnx in Windows_
-------------------------------------
##### example command with options : settimeout=3 , cms-gathering = all , -d subdomains-gathering , run --exploitsvulnx -u --timeout 3 -c all -d -w --exploit
##### example command for searching dorks : -D or --dorks , -l --list-dorks vulnx --list-dorks
return table of exploits name.vulnx -D blaze
return urls found with blaze dork
-------------------------------------
_🕷️
-------------------------------------
:warning: Warning!
*I Am Not Responsible of any Illegal Use*
-------------------------------------
_🕷️ Contribution & License_
You can contribute in following ways:
Do you want to have a con in private? email me :
*VulnX* is licensed under GPL-3.0 License
项目信息
开发语言:Python
Star 数:2149
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕vulnx 🕷️ an intelligent Bot, Shell can achie injection, and help researchers detect security CMS system. It can perform a quick CMS security detection, information collection (including sub-domain name, ip address, country information, organizational information and time zone, etc.) and scanning.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | vulnx - vulnx 🕷️ an intelligent Bot, Shell can achieve aut |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:06:05 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 292 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |