 黑客技术
点击放大
Sn1per - Automated penetration testing & attack surface man
项目说明
![Sn1per]()
![GitHub release]()
![License]()
![GitHub issues]()
![Last commit]()
![Contributors]()
![GitHub Stars]()
![GitHub Forks]()
![GitHub Followers]()
![Follow on Twitter]()
[Products] [Attack Surface Management] [About Sn1per] [News] [Contact] [Demo] [Pricing] [Shop]
Sn1per — The Offensi Platform for Modern Teams
> Recon, scanning, exploitation, and reporting in a single workspace — whether you're a solo pentester or a global SOC.
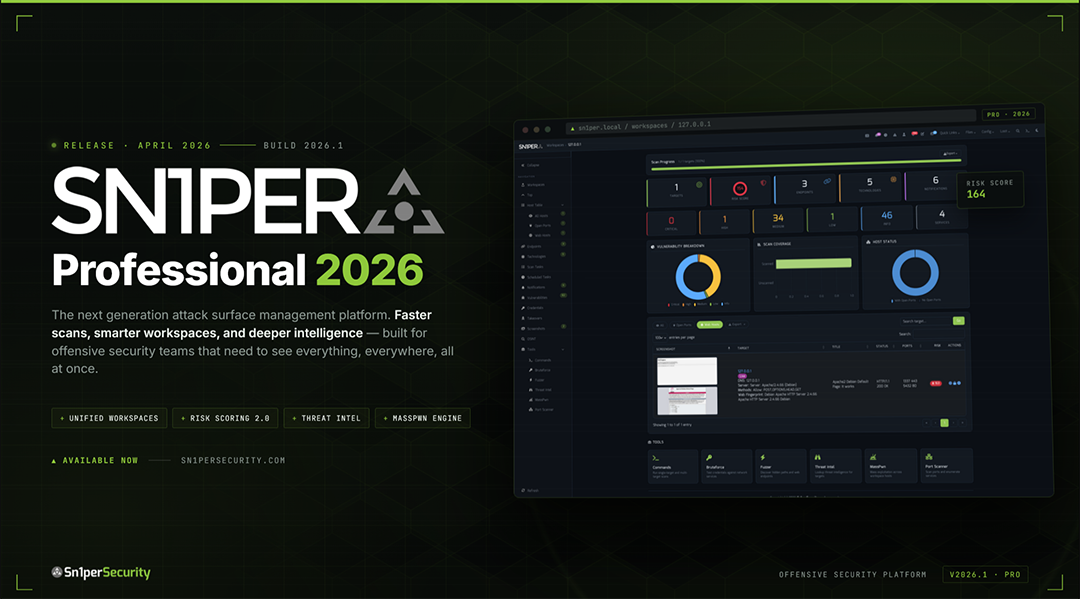
> ## Sn1per Professional 2026 is here
>
> The largest release since v10.0 — Docker-first deployment, Bootstrap 5 / Tabler UI, Workspace Na, Workspace + Host Reports with CS / PDF export, JSON API v1.0, an Offcan Commands sidebar with 13 panels, and expanded modules for Re, MassPwn, Threat Intel, Nessus, and Burp.
>
> Read the release notes → · View pricing →
Table of Contents
About Sn1per
Sn1per is an offensi platform that consolidates reconnaissance, scanning, exploitation, and reporting into a single workspace. Built by pentesters since 2015, it ships in three editions — a free Community Edition (源码-a, custom EULA — see LICENSE.md) in this repository, a paid Professional edition for indi operators and small teams, and an Enterprise edition for global SOCs — all backed by the same core scanning 引擎.
Sn1per orchestrates 90+ third-party tools, ships with 600+ exploits and 10,000+ detections, and is used by 500+ teams worldwide. Battle-tested by the community. Built by pentesters, for pentesters.
500+ Teams · 90+ Integrations · 10,000+ Detections · 600+ Exploits · Trusted since 2015
What Sn1per Is For
Sn1per ships as one platform that covers the core jobs offensi teams otherwise stitch together from a dozen tools:
What's New in 2026
![Sn1per Pro 2026 Workspace Na]()
*Workspace Na — switch contexts across hosts, scopes, and engagements.*
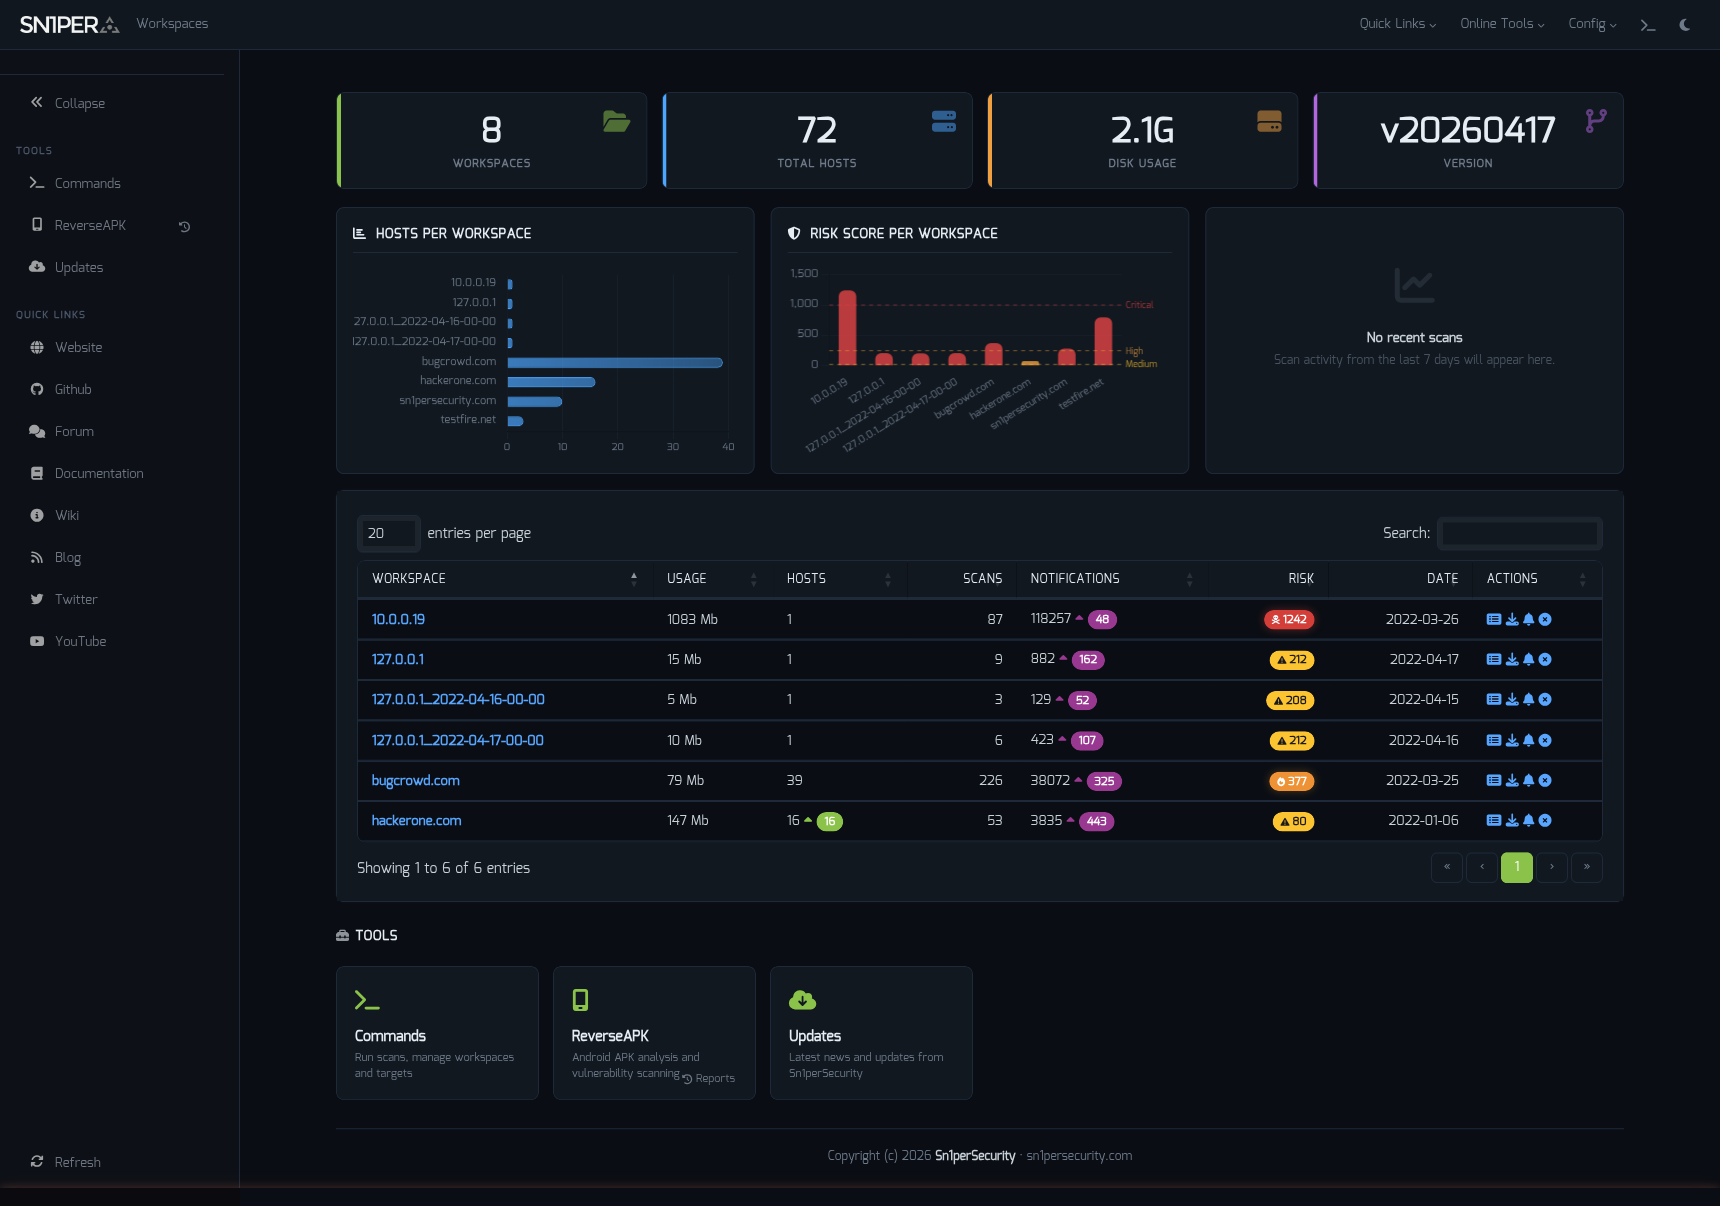
![Sn1per Pro 2026 Dashboard]()
*Dashboard — at-a-glance scan posture, top findings, and exploitable assets.*
Highlights
-v (), -db (debug), -rr (remo files)> *"Sn1per Professional 2026 is the largest release since the v10.0 line."*
Read the full release notes →
Editions & Pricing
The Community Edition is free and lives in this repository. The Professional and Enterprise editions add a Web UI, commercial integrations, and email support.
| | Sn1per Professional | Sn1per Enterprise |
|---|---|---|
| Price | $984 / year (per seat) | Get a quote |
| Subscription | 1 year | 1 year |
| — Included — | | |
| Web UI | Professional Web UI | Enterprise Web UI |
| Scan Engine & UI Updates | ✓ | ✓ |
| All Modules & Integrations | ✓ | ✓ |
| On-Prem (Self Hosted) | ✓ | ✓ |
| Email Support | 1 Year | 1 Year |
| Impro & Scalability | — | ✓ |
| Cutting-Edge Features | — | ✓ |
| — Limits & Quotas — | | |
| Max Scans | Unlimited | Unlimited |
| Max Assets / Workspace | 30 | Unlimited |
| Max Workspaces | 5 | Unlimited |
| Total Assets | 150 | 500+ |
| Licensed Systems | 1 | 1 |
Buy a Sn1per Professional license → · Get an Enterprise quote →
Install
Linux (Kali / Ubuntu / Debian / Parrot)
> Sn1per installs to /usr/share/sniper and requires root. Use sudo bash install.sh force to skip the confirmation prompt.
Docker
Sn1per on Docker Hub →
#### Kali Linux base
#### BlackArch base
AWS Marketplace (EC2 AMI)
Subscribe via AWS Marketplace:
1. Click Continue to Subscribe
2. Click Continue to Configuration, choose region/instance type
3. Click Continue to Launch
4. SSH to the EC2 public IP — Sn1per is preinstalled
Quick Start
Results land in /usr/share/sniper/loot/<workspace>/. See Usage for more modes.
Usage
Scan Modes
| Mode | Description |
|------|-------------|
| normal | Active + passive scan of the target and its open ports |
| stealth | Quick, mostly non-intrusi to avoid WAF / IPS |
| flyover | Fast multi-threaded high-le of many hosts |
| airstrike | Open-port enumeration + basic fingerprinting against a host file |
| nuke | Full audit across all targets in a host file |
| discover | Walks a CIDR and runs Sn1per on every live host |
| port | Targeted scan of a specific port |
| fullportonly | Full TCP port scan, results saved to XML |
| web | Web app scan on 80/tcp + 443/tcp only |
| webporthttp / webporthttps | Web app scan on a specific HTTP / HTTPS port |
| webscan | Full HTTP + HTTPS web app scan via Burp Suite + Arachni |
| | Open scan |
| mass* | Multi-target of the above (-f targets.txt) |
Integrations
Sn1per ships with nati for 90+ tools and services. Featured partners:
| Category | Integrations |
|----------|--------------|
| scanners | Nessus · OpenVAS · GVM 21.x · Nuclei |
| Web app testing | Burp Suite Pro · OWASP ZAP · WPScan |
| Exploitation | Metasploit |
| Reconnaissance | Shodan · Censys · Hunter.io · · Nmap |
| AI / LLM | OpenAI · Claude · Gemini |
| Notifications & DevOps | Slack · GitHub API |
Browse all integrations on the wiki →
Documentation & Help
Configuration & Templates
News & Releases
Guides & deep dives (2026)
Reconnaissance
Penetration testing
Attack surface management
All releases & blog posts →
Community & Support
Contributing
Pull requests welcome. For substantial changes, open an issue first to discuss the design.
modes/ — one bash file per scan modeCHANGELOG.md35 contributors and counting. Thank you.
License & Legal
LICENSE.md and THIRD_PARTY_LICENSES.mdNOTICE---
About Sn1perSecurity
Sn1per is built and maintained by Sn1perSecurity, the team behind the Sn1per attack surface management and automated penetration testing platform. Small team of pentesters shipping offensi tooling since 2015. We focus on the workflows we want to use ourselves — fast recon, ergonomic reporting, honest pricing, and a Community Edition that genuinely keeps up with the commercial editions. If that resonates, say hi.
Topics: penetration-testing · offensi · attack-surface-management · · recon · osint · red-team · bug-bounty · security-tools
项目信息
开发语言:Shell
Star 数:11360
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Automated penetration testing & attack surface management platform. Recon, scan, exploit, report — 600+ exploits, 90+ integrations, 10K+ detections.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Sn1per - Automated penetration testing & attack surface man |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:06:40 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 524 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |