 黑客技术
点击放大
gef - GEF (GDB Enhanced Features) - a modern experience
项目说明
<p align="center">
<img src="docs/assets/images/logo.png" alt="logo"/>
</p>
<p align="center">
<a href=" alt="Discord" src="
<a href=" alt="Docs" src="
<a title="Use the IDs: gef/gef-demo" href=" alt="Try GEF" src="
</p>
GEF (pronounced ʤɛf - "Jeff") is a set of commands for x86/64, ARM, MIPS, PowerPC and SPARC to
assist exploit de and re when using old school GDB. It provides additional
features to GDB using the Python API to assist during the process of dynamic analysis and exploit
de. Application de will also benefit from it, as GEF lifts a great part of regular
GDB obscurity, a repeating traditional commands, or bringing out the relevant information
from the debugging runtime.
Instant Setup
Simply make sure you have GDB 10.0 or higher compiled with Python3.10+
bindings, then:
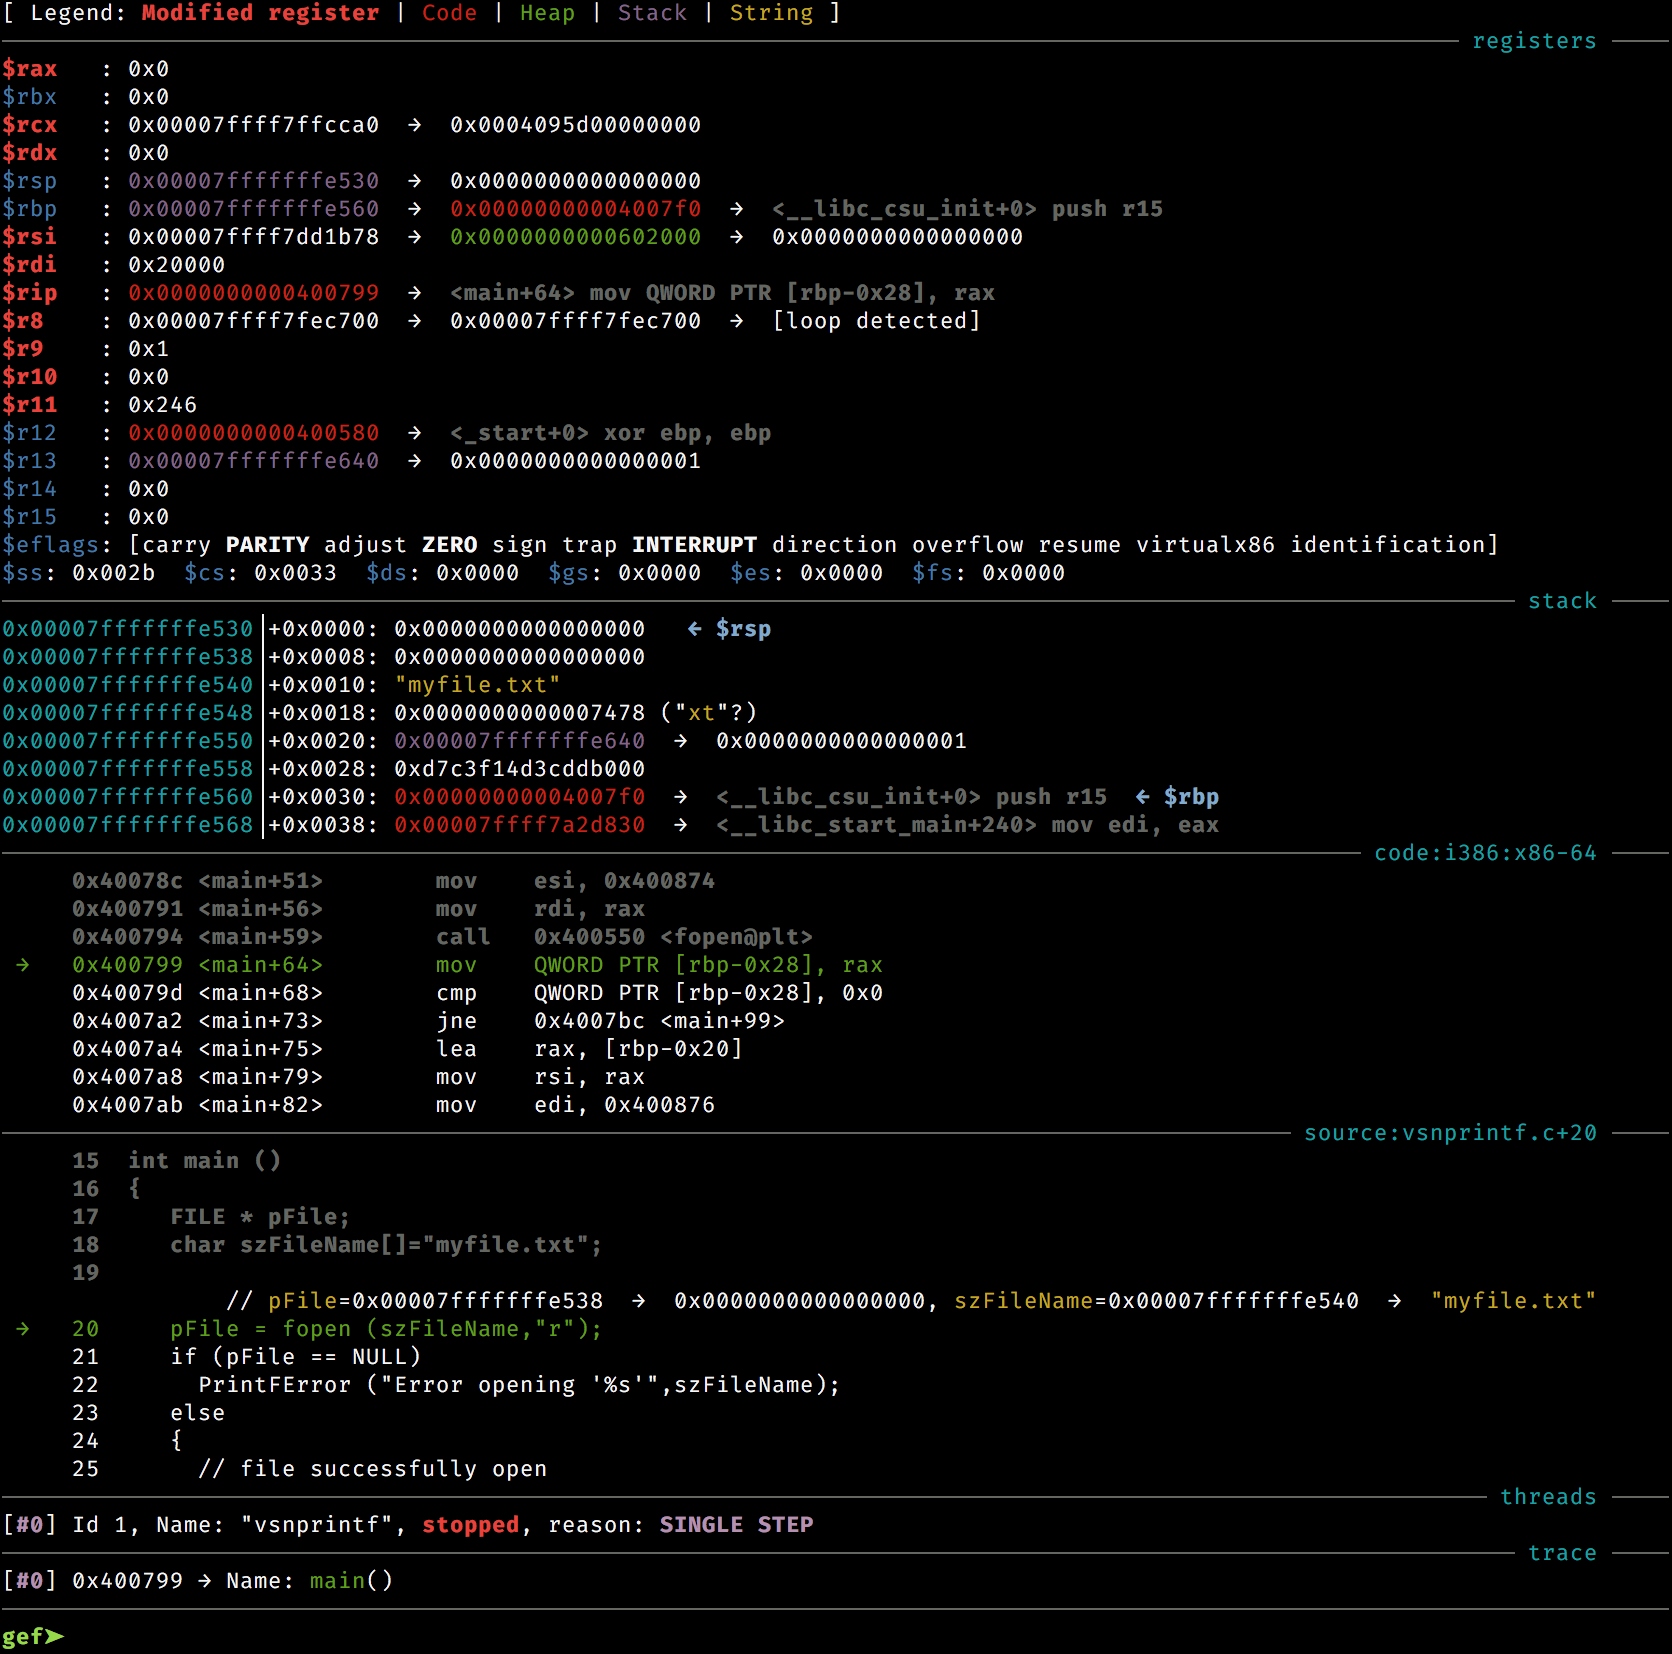
You can immediately see that GEF is correctly installed by launching GDB:
!gef-context
A few of GEF features include:
* One single GDB script
* Entirely architecture agnostic, NO dependencies: GEF is battery-included and is
installable instantly
* Fast limiting the number of dependencies and optimizing 代码 to make the commands as fast as
possible
* Provides a great of commands to drastically change your experience in GDB.
* Easily extensible to create other commands by pro
d more comprehensible layout to GDB Python API.
* Full Python3 support (Python2 support was
dropped - see
gef-legacy).
* Built around an architecture abstraction layer, so all commands work in any GDB-supported
architecture such as x86-32/64, ARMv5/6/7, AARCH64, SPARC, MIPS, PowerPC, etc.
* Suited for real-life apps debugging, exploit de, just as much as CTF
* And a lot more commands contributed by the community a on
GEF-Extras !!
Check out the Screenshot page for more or try it
online (user:gef/password:gef-demo)
Documentation
Unlike other GDB plugins, GEF has an extensive and up-to-date
documentation. Users are recommended to refer to it as it may help
them in their attempts to use GEF. In particular, new users should na through it (see the
FAQ for common installation problems), and the problem persists,
try to reach out for help on the Discord channel or submit an issue.
Current status
| Documentation | License | Compatibility | CI Tests (main) |
| :--------------------------------------------------------------------------------------------------------------------------------------------------------------: | :----------------------------------------------------------------------------------------------------------------------------------------: | :-------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------- |
| ![Documentation]() | ![MIT]() | ![Python 3]() | ![CI Test for GEF]() |
Contribute
To get in, refer to the Contribution
documentation and the
guidelines to start.
Sponsors
Another way to contribute to keeping the project alive is by sponsoring it! Check out the
sponsoring documentation for details so you can be part of
the list of those awesome sponsors.
Happy Hacking 🍻
项目信息
开发语言:Python
Star 数:8383
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕GEF (GDB Enhanced Features) - a modern experience for GDB with ad debugging capabilities for exploit devs & reverse engineers on Linux展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | gef - GEF (GDB Enhanced Features) - a modern experience |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:07:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 447 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |