 黑客技术
点击放大
PhoneSploit-Pro - An all-in-one hacking tool to remotely take over A
项目说明
<di="center">
PhoneSploit Pro
The Swiss Army knife for Android.
An all-in-one hacking tool written in Python to remotely take o devices using ADB, scrcpy, Nmap, and Metasploit-Framework.
!GitHub release (latest by date)
!Python
!GitHub Repo stars
!GitHub forks
</div>
Table of contents
---
O
#### Own the device. Every way that matters.
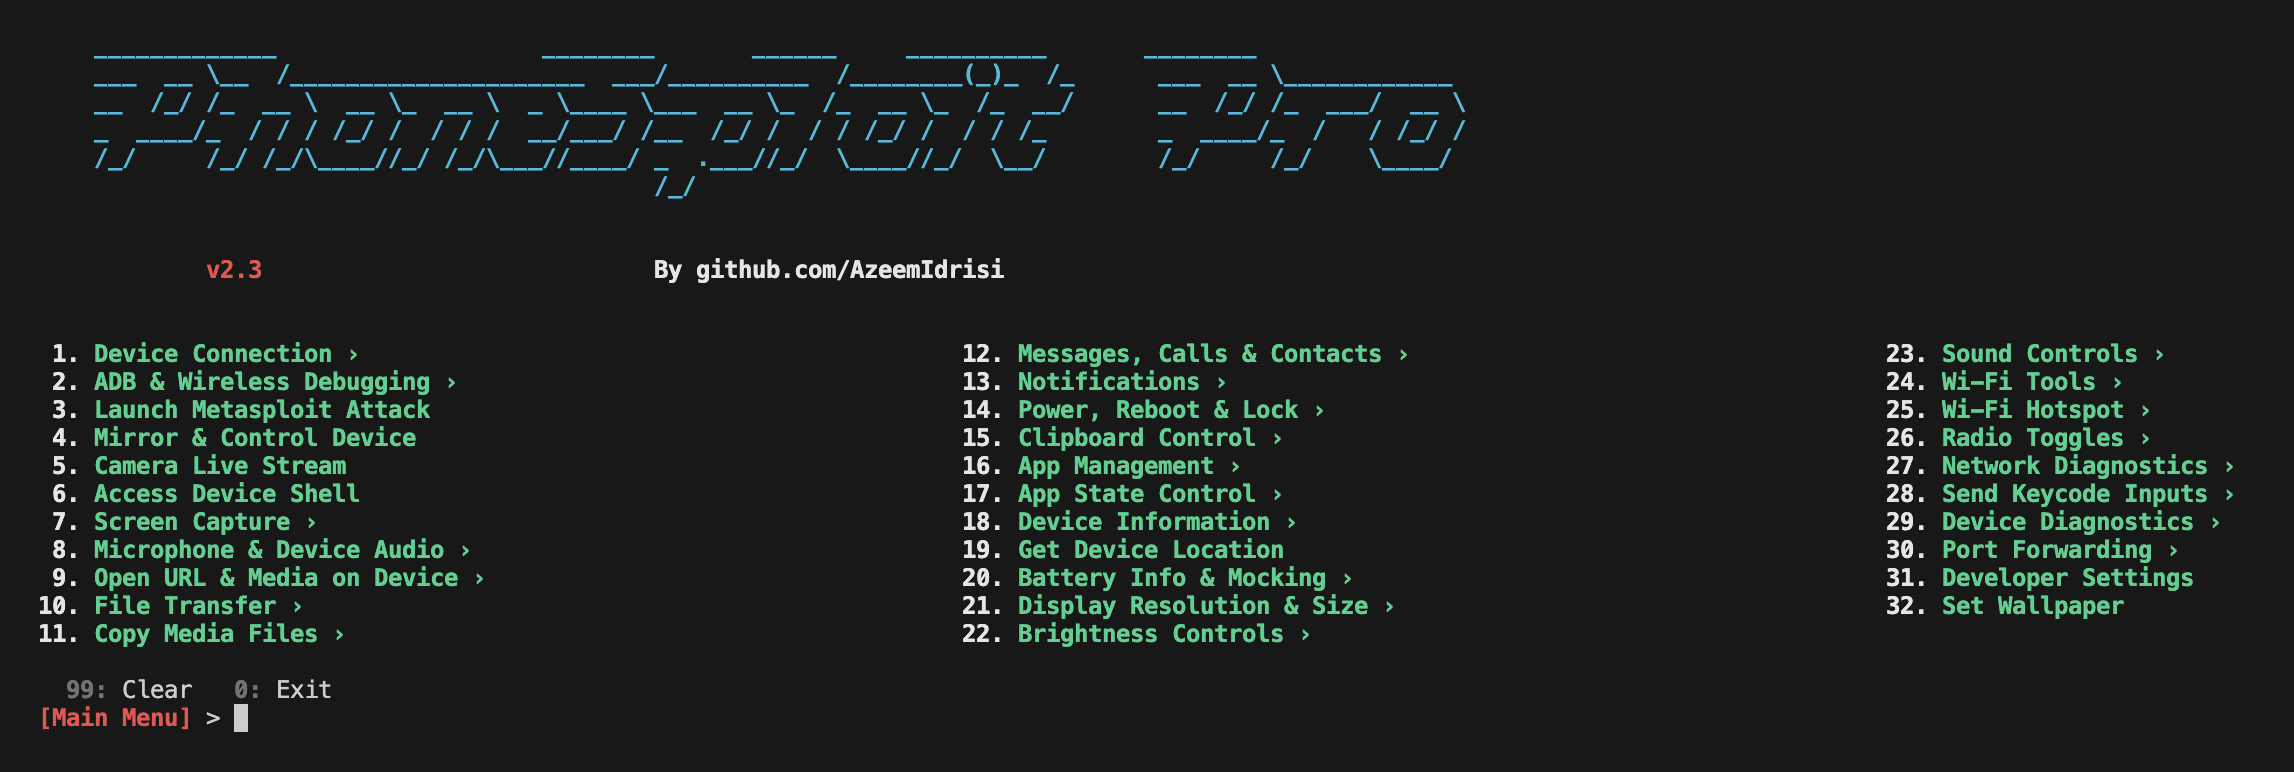
Connect over USB or Wi‑Fi, then control the device, extract data, stream camera and microphone, manage apps, and automate a full Metasploit compromise, all from one menu.
You no longer need to memorize commands and arguments, PhoneSploit Pro does it for you. Pick a number and run.
---
Screenshots
!Screenshot
---
Features
| Feature | Description |
| ---------------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Connect a device | Connect to a device remotely using ADB. |
| List connected devices | Show all devices currently attached to ADB. |
| Disconnect all devices | Disconnect every ADB session. |
| Multi-device selection | If several ADB devices are connected (USB or 网络), choose which device to use for the session (ANDROID_SERIAL). |
| Stop ADB server | Stop the ADB ser. |
| Restart ADB server | Restart the ADB ser. |
| Access device shell | Open an interacti on the connected device. |
| Keycodes | Send keycodes to control the device remotely. |
| Unlock device | Turn the screen on, swipe up, and enter a password when needed. |
| Lock device | Lock the device. |
| Restart / reboot | Restart or reboot the device to System, Recovery, Bootloader, or Fastboot. |
| Power off | Power off the target device. |
| Screenshot | Take a screenshot and pull it to the computer automatically. |
| Screen recording | Record the target device’s screen for a specified time and pull the recording to the computer automatically. |
| Anonymous screenshot / screen record | Take screenshots or screen recordings and remove the file from the target device afterward. |
| Mirror and control | Mirror the screen and control the target device. |
| List files and folders | List all files and folders on the target device. |
| Download from device | Download a file or folder from the target device. |
| Send to device | Send a file or folder from the computer to the target device. |
| Copy WhatsApp data | Copy all WhatsApp data to the computer. |
| Copy screenshots | Copy all screenshots to the computer. |
| Copy camera photos | Copy all camera photos to the computer. |
| Camera live | Stream li from the front or back camera on the target device. |
| Dump SMS | Export all SMS from the device to the computer. |
| Dump contacts | Export all contacts from the device to the computer. |
| Dump call logs | Export all call logs from the device to the computer. |
| Run an app | Launch an application on the device. |
| Install APK | Install an APK from the computer to the target device. |
| Install split APKs | Install apps shipped as multiple APK splits (e.g. split bundles). |
| Uninstall an app | Remove an installed application. |
| List installed apps | List all apps installed on the target device. |
| Extract APK | Extract the APK from an installed app. |
| Force-stop app | Force-stop a running application. |
| Clear app data | Clear storage/data for a chosen app (factory reset for that app). |
| Restart app | Restart an application (force-stop then relaunch). |
| Grant / revoke permission | Grant or revoke a runtime permission for an app. |
| Open a link | Open a URL on the target device. |
| Display a photo | Show an image or photo on the target device. |
| Play audio | Play an audio file on the target device. |
| Play video | Play a video on the target device. |
| Send SMS | Send SMS messages through the target device. |
| Device information | Read device information. |
| Battery information | Read battery status and related details. |
| Record microphone audio | Record audio from the microphone. |
| Stream microphone audio | Stream li audio. |
| Record device audio | Record internal device audio. |
| Stream device audio | Stream li audio. |
| Hack device completely | Automated Metasploit flow: fetch your IP address to set LHOST; create a payload with msfvenom, install it, and run it on the target device; launch and configure Metasploit-Framework to obtain a meterpreter session. A meterpreter session means the device is fully compromised , and you can run further actions from the session. |
| LAN network scan | Disco on the local 网络 to help find a target IP address; probe TCP ports 5555 and 5554 with service detection and show ADB-related fingerprints and hints for likely Android/ADB targets. |
| TCP port forwarding | Forward, reverse, list, remove, or remove all TCP port forwarding rules over ADB. |
| Sa snippet | Capture a slice of logcat output and save it to a file on the computer. |
| Li stream | Stream logcat live from the device. |
| Network snapshot | Show a snapshot of 网络 interfaces and connectivity on the device. |
| De settings | Open the system De options screen on the device. |
| Read locale | Read locale and language settings from the device. |
| Screen stay-on | Set s stayon (stay on over USB, stay on always, or turn stay-on off). |
| Wi‑Fi status dump | Dump detailed Wi‑Fi status from the device. |
| WLAN IP info | Show WLAN IP addressing information. |
| Wi‑Fi radio toggle | Turn the Wi‑Fi radio on or off. |
| Ping connectivity | Run ping checks against a host to test connectivity. |
| Saved Wi‑Fi networks | List saved Wi‑Fi networks known to the device. |
| Root heuristics | Heuristic checks for common signs of root access. |
| Set resolution & display size | View current display settings; set screen resolution (wm size) from 720p/1080p/2K/4K presets in portrait or landscape, or a custom WxH; set display density (wm density) from common DPI presets or a custom value; toggle display scaling (wm scaling); and reset e to device defaults. |
| Clipboard management | Read, set, or clear the device clipboard. |
| GPS / location | Retrieve the device's last-known GPS location (latitude, longitude, provider). |
| IMEI / device identifiers | Read IMEI, Android ID, serial number, and other hardware/software identifiers. |
| App usage statistics | Show foreground app usage stats over 1 day / 7 days / all time. |
| Radio toggles | Toggle mobile data, Bluetooth, NFC, and airplane mode. |
| Mock battery | Fake a battery level, simulate plugged or unplugged, or reset readings. |
| Sound & display settings | Set media , screen brightness, screen timeout, and Do Not Disturb mode. |
| Notifications | Post a notification, expand or collapse the notification panel and quick settings. |
| Set wallpaper | Push an image to the device and open the system wallpaper picker. |
| Nearby Wi‑Fi scan | Scan and list nearby Wi‑Fi networks with SSID, BSSID, frequency, and signal. |
| Local hotspot | Start or stop a local-only Wi‑Fi hotspot directly from the device. |
| Wireless ADB setup | Pair, connect, switch to TCP/IP, or switch back to USB — all wireless ADB commands. |
| Enable / disable app | Disable a system or user app, or re-enable it later. |
| Suspend / unsuspend app | Suspend an app (icon greyed out, no data usage) or unsuspend it. |
| Ignore battery optimization | Whitelist an app from Doze battery optimization, un-whitelist it, or show the battery whitelist. |
| Set default home app | Change the default launcher/home app to any installed launcher package, or show the current home app. |
---
Requirements
python3 — Python 3.10 or newerpip — Package installer for Pythonadb — Android Debug Bridge (ADB) from Android SDK Platform Toolsmetasploit-framework — Metasploit-Framework (msfvenom and msfconsole)scrcpy — scrcpynmap — Nmap---
Installing dependencies
Use the bundled installer to set up all dependencies automatically. It detects your OS and uses the appropriate package manager.
Linux / macOS / Termux
To install specific tools only: ./install.sh --components adb,nmap,pip
For per-component prompts: ./install.sh --interactive
Windows
Run PowerShell as Administrator, then:
To install specific tools only: .\install.ps1 -Components adb,nmap,pip
For per-component prompts: .\install.ps1 -Interactive
From PhoneSploit Pro
If a dependency is missing, the program shows a Missing Dependencies warning. Press I to run the installer, Y to continue anyway, or N to exit.
---
Getting started
> [!IMPORTANT]
> PhoneSploit Pro requires Python 3.10 or higher. Please update Python before running the program.
Linux and macOS
Make sure all required software is installed.
> [!TIP]
> You only need to activate the en (source .venv/bin/activate) each time you open a new terminal before running the program.
Windows
Make sure all required software is installed.
1. Download and extract the latest platform-tools from here.
2. Copy all files from the extracted platform-tools or adb directory into the PhoneSploit-Pro directory, then run:
---
Device setup tutorial
Setting up an Android phone for the first time
1. Open Settings.
2. Go to About Phone.
3. Find Build Number.
4. Tap Build Number se.
5. Enter your pattern, PIN, or password to enable the De options menu.
6. The De options menu will now appear in your Settings menu.
1. Open Settings.
2. Go to System > De options.
3. Scroll down and enable USB debugging.
1. Connect your Android device and the adb host computer to the same Wi‑Fi network.
2. Connect the device to the host computer with a USB cable.
3. Open a terminal on the computer and run the following command:
4. A pop-up will appear on the Android phone when you connect to a new PC for the first time: Allow USB debugging?.
5. Select Always allow from this computer, then tap Allow.
6. Then, in the terminal, run the following command:
7. You can now connect the Android phone to the computer over Wi‑Fi using adb.
8. Disconnect the USB cable.
9. Go to Settings > About Phone > Status > IP address and note the phone’s IP address.
10. Run PhoneSploit Pro, choose Connect a device, and enter the target’s IP address to connect over Wi‑Fi.
Connecting the Android phone the next time
1. Connect your Android device and host computer to the same Wi‑Fi network.
2. Run PhoneSploit Pro, choose Connect a device, and enter the target’s IP address to connect over Wi‑Fi.
---
Compatibility
This tool is tested on:
> [!NOTE]
> New features are primarily tested on Linux, so Linux is recommended for running PhoneSploit Pro.
> Some features might not work properly on Windows.
---
Installing tools manually
If you prefer to install tools yourself, or the automatic installer is not a for your platform, use the sections below.
ADB
#### Linux
Open a terminal and run the following commands:
For other Linux distributions, see: Android platform-tools downloads
#### macOS
Open a terminal and run the following command:
Or download from: Android platform-tools downloads
#### Windows
Download from: Android platform-tools downloads
#### Termux
Metasploit-Framework
#### Linux and macOS
brew install without --cask):Or follow: Installing Metasploit on Linux / macOS
Or visit: Metasploit download
#### Windows
Visit: Metasploit download
Or see: Windows: antivirus and installers
scrcpy
Visit the scrcpy GitHub page for the latest installation instructions: scrcpy — get the app
On Windows: Copy all files from the extracted scrcpy folder into the PhoneSploit-Pro folder.
> [!IMPORTANT]
> If scrcpy is not a for your Linux distribution (for example Kali Linux), you can install it manually (Linux guide)
> or build it in a few steps (Build guide).
Nmap
#### Linux
Open a terminal and run the following commands:
For other Linux distributions, see: Nmap download
#### macOS
Open a terminal and run the following command:
Or visit: Nmap download
#### Windows
Download and install the latest stable release: Nmap for Windows
#### Termux
---
Disclaimer
---
De
<a href="
<!-- <img src=" /> -->
<img width="150px" src= />
</a>
Azeem Idrisi -
Support
If you like my work, you can support me via:
<a href=" target="_blank"> <kbd> <img
src=" alt="PayPal"
width="147"></a> <a href=" target="_blank"> <kbd> <img src=" alt="Buy Me A Coffee" width="200"></a>
---
Attribution
PhoneSploit Pro is built upon and gratefully acknowledges the contributions of the following open-源码 projects:
adb — Android Debug Bridge (ADB)metasploit-framework — Metasploit-Frameworkscrcpy — scrcpynmap — Nmapadb-clip — adb-cliprich — Richpython-nmap — python-nmap<hr>
Copyright © 2026 Azeem Idrisi (github.com/AzeemIdrisi)
项目信息
开发语言:Python
Star 数:6334
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An all-in-one hacking 工具 to remotely take o devices.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | PhoneSploit-Pro - An all-in-one hacking tool to remotely take over A |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:08:09 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 124 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |