 黑客技术
点击放大
作者:admin
发布:2026-10-05
peda - PEDA - Python Exploit Development Assistance for G
项目说明peda====PEDA - Python Exploit De Assistance for GDBKey Features:* Enhance the display of gdb: colorize and display disassembly codes, registers, m…
资源可下载
免费下载
0 条讨论
会员资源
开通会员后即可下载全部资源。
212浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-05
人工审核发布
评论区答疑
项目说明
peda
====
PEDA - Python Exploit De Assistance for GDB
Key Features:
* Enhance the display of gdb: colorize and display disassembly codes, registers, memory information during debugging.
* Add commands to support debugging and exploit de (for a full list of commands use
peda help):*
aslr -- Show/set ASLR setting of GDB*
checksec -- Check for security options of binary*
dumpargs -- Display arguments passed to a function when stopped at a call instruction*
dumprop -- Dump all ROP gadgets in specific memory range*
elfheader -- Get headers information from debugged ELF file*
elfsymbol -- Get non-debugging symbol information from an ELF file*
lookup -- Search for all addresses/references to addresses which belong to a memory range*
patch -- Patch memory start at an address with string/hexstring/int*
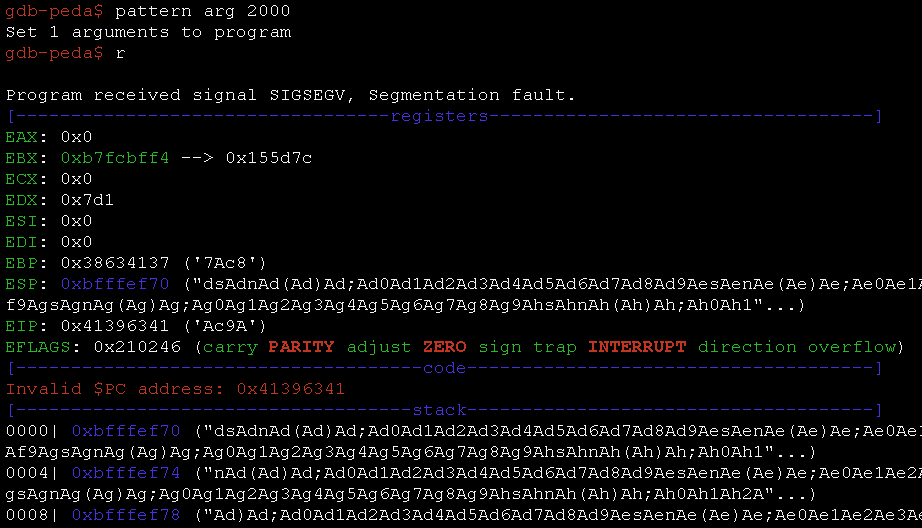
pattern -- Generate, search, or write a cyclic pattern to memory*
procinfo -- Display info from /proc/pid/*
pshow -- Show PEDA options and other settings*
pset -- Set PEDA options and other settings*
readelf -- Get headers information from an ELF file*
ropgadget -- Get common ROP gadgets of binary or library*
ropsearch -- Search for ROP gadgets in memory*
searchmem|find -- Search for a pattern in memory; support regex search*
shellcode -- Generate or download common shellcodes.*
skeleton -- Generate python exploit code template*
vmmap -- Get mapping address ranges of section(s) in debugged process*
xormem -- XOR a memory region with a keyInstallation
git clone ~/peda
echo "source ~/peda/peda.py" >> ~/.gdbinit
echo "DONE! debug your program with gdb and enjoy"
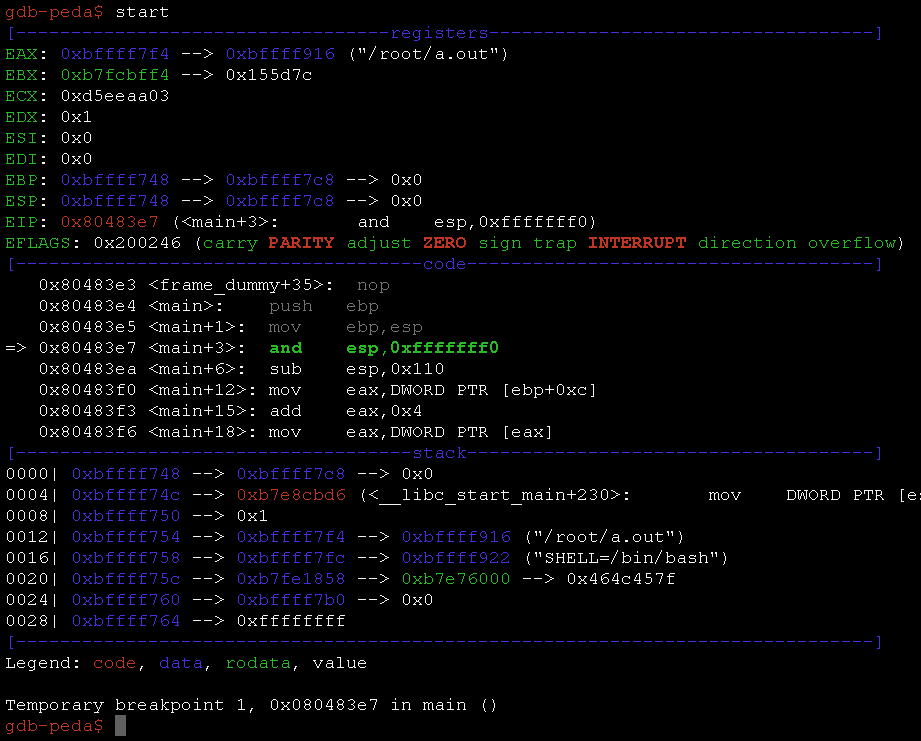
Screenshot
!start
!pattern arg
!patts
项目信息
开发语言:Python
Star 数:6151
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕PEDA - Python Exploit De Assistance for GDB展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | peda - PEDA - Python Exploit Development Assistance for G |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:08:11 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 212 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |
本资源免费,登录后即可在本页「下载链接」区域获取全部附件。
请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。
请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
还没有讨论,快来抢沙发~
登录 后才能参与讨论