 黑客技术
点击放大
Awesome-Redteam - 一个攻防知识库。A knowledge base for red teaming and offen
项目说明
Awesome-Redteam
<p align="left">
<a href="
<img src=" alt="stars">
</a>
<a href="
<img src=" alt="forks">
</a>
<a href="
<img src=" alt="last-commit">
</a>
</p>
❗【免责声明】本项目所涉及的技术、思路和工具仅供学习,任何人不得将其用于非法用途和盈利,不得将其用于非授权渗透测试,否则后果自行承担,与本项目无关。 使用本项目前请先阅读 法律法规。
_Disclaimer: The technologies, concepts, and tools provided in this Git repository are intended for educational and research purposes only. Any use for illegal acti, unauthorized penetration testing, or commercial purposes is strictly prohibited. Please read the Awesome-Laws before using this repository._
📖 一个攻防知识库。_A knowledge base for red teaming and offensi._
👍 means recommend 推荐使用
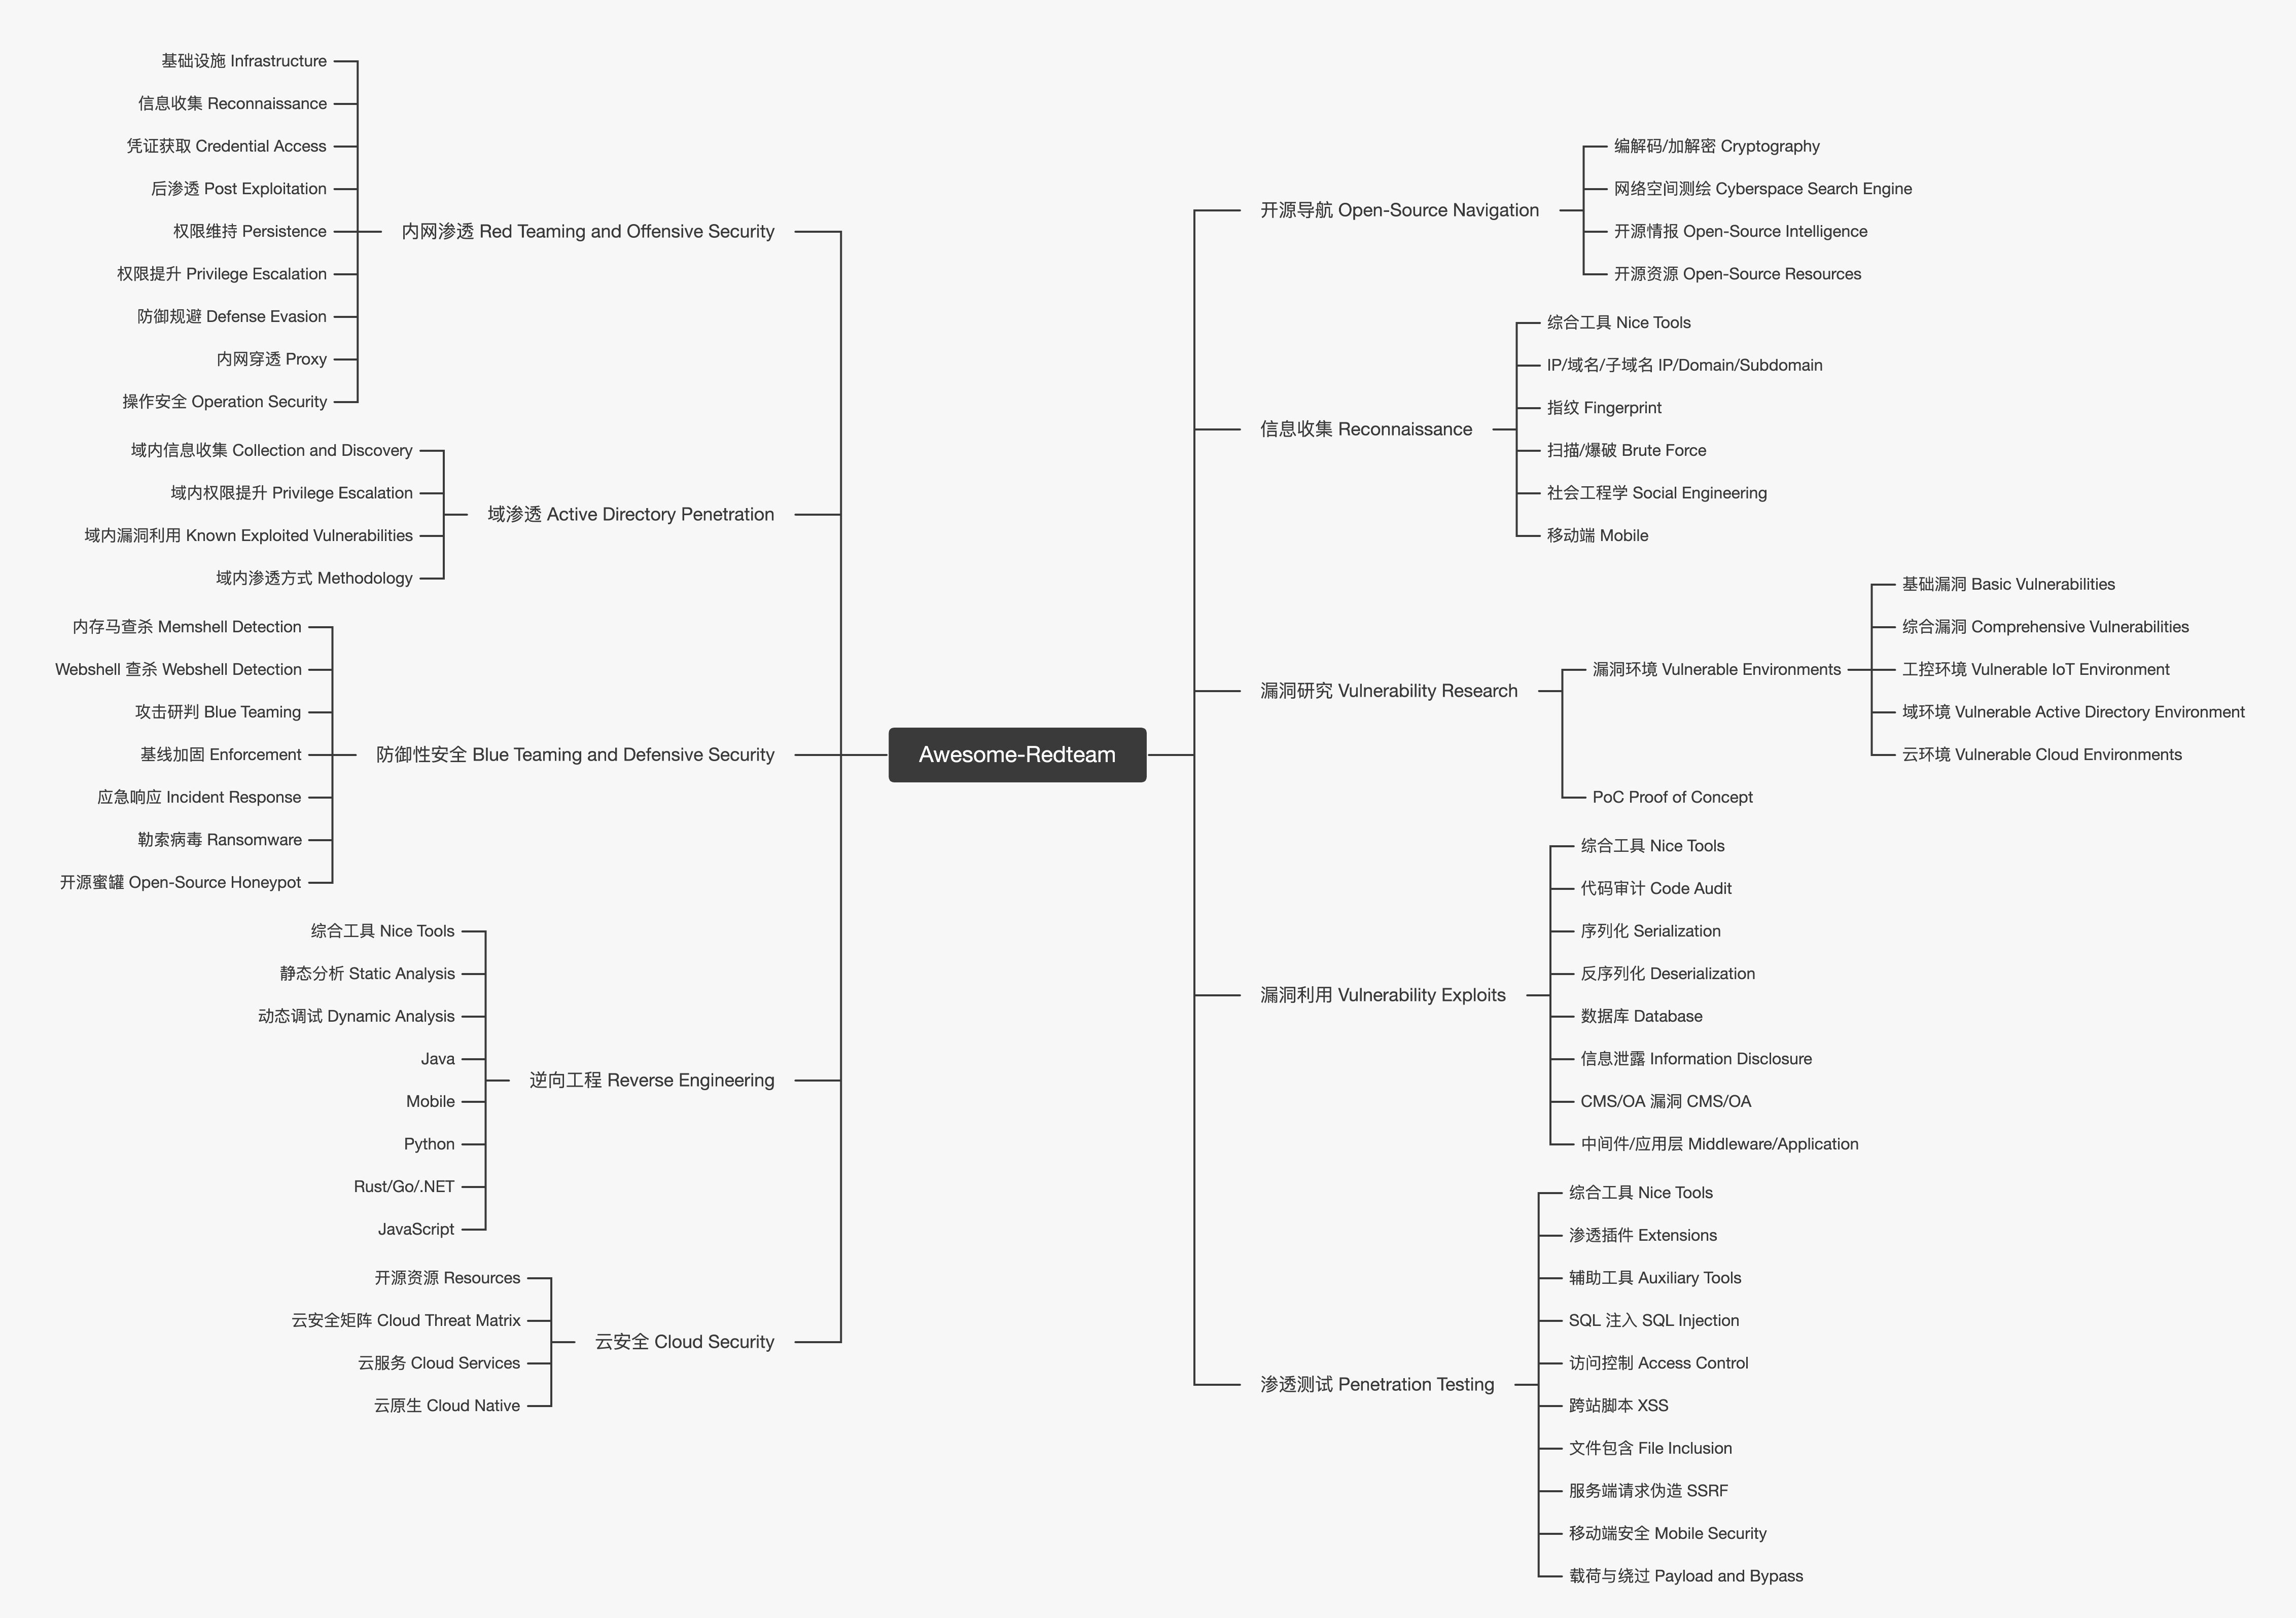
_Roadmap_

目录 _Contents_
- 速查文档 _CheatSheets_
- 一些代码 _Scripts_
- 攻防知识 _Tips_
- 编解码/加解密 _Cryptography_
- 在线工具 _Online Tools_
- 离线工具 _Offline Tools_
- 编码/解码 _Encode/Decode_
- 正则表达式 _Regular Expressions_
- 哈希算法 _Hash Algorithms_
- 公钥密码算法 _RSA_
- 国密算法 _SM Algorithms_
- 网络空间测绘 _Cyberspace Search Engine_
- 综合工具 _Nice Tools_
- 网页/端口 _Web/Ports_
- 谷歌搜索 _Google Hacking_
- Github 搜索 _Github Dork_
- 开源情报 _Open-Source Intelligence_
- 综合工具 _Nice Tools_
- 威胁情报 _Threat Intelligence_
- 漏洞披露 _Disclosed
- 接口检索 _API Search_
- 源代码检索 _Source Code Search_
- 开源资源 _Open-Source Resources_
- 社区/知识库 _Communities/Knowledge Base_
- 思维导图/备忘录 _Mindmap/Cheat Sheets_
- 进攻性安全 _Red Teaming and Offensi
- 防御性安全 _Blue Teaming and Defensi
- 操作安全 _Operation Security_
- 实战平台 _Learning and Practice Platforms_
- 综合工具 _Nice Tools_
- IP/域名/子域名 _IP/Domain/Subdomain_
- 指纹 _Fingerprint_
- 指纹库 _Fingerprint Collection_
- 指纹识别 _Fingerprint Reconnaissance_
- WAF 识别 _Waf Checks_
- 扫描/爆破 _Brute Force_
- 扫描/爆破工具 _Brute Force Tools_
- 扫描/爆破字典 _Brute Force Dictionaries_
- 字典生成 _Generate a Custom Dictionary_
- 默认口令查询 _Default Credentials_
- 社会工程学 _Social Engineering_
- 凭据泄露 _Leaked Credentials_
- 邮箱 _Email_
- 短信 _SMS Online_
- 钓鱼 _Phishing_
- 移动端 _Mobile_
- 漏洞环境 _ En
- 基础漏洞 _Basic
- 综合漏洞 _Comprehensi
- 工控环境 _ IoT En
- 域环境 _ Acti En
- 云环境 _ Cloud En
- PoC _Proof of Concept_
- PoC/ExP
- PoC 模板 _PoC Templates_
- 综合工具 _Nice Tools_
- 代码审计 _Code Audit_
- 序列化 _Serialization_
- Java
- 反序列化 _Deserialization_
- Java
- PHP
- 数据库 _Database_
- Redis
- MySQL
- Oracle
- MSSQL
- 信息泄露 _Information Disclosure_
- CMS/OA 漏洞 _CMS/OA_
- 中间件/应用层 _Middleware/Application_
- 综合工具 _Nice Tools_
- 渗透插件 _Extensions_
- Chrome
- Burp Suite
- Yakit
- 辅助工具 _Auxiliary Tools_
- 工具集 _Open-Source Toolkit_
- 带外通道 _DNSLog_
- 终端优化 _Command Line_
- 代码美化 _Beautifier_
- 生成器 _Generator_
- SQL 注入 _SQL Injection_
- 访问控制 _Access Control_
- 403 绕过 _Bypass 40X errors_
- 跨站脚本 _XSS_
- 文件包含 _File Inclusion_
- 服务端请求伪造 _SSRF_
- 移动端安全 _Mobile Security_
- 小程序 _Mini Program_
- 应用程序 _APK_
- SessionKey 解密 _SessionKey_
- 载荷与绕过 _Payload and Bypass_
- 基础设施 _Infrastructure_
- 信息收集 _Reconnaissance_
- 凭证获取 _Credential Access_
- 凭证转储 _Credential Dumping_
- 本地枚举 _Local Enumeration_
- 哈希破解 _NTLM Cracking_
- 后渗透 _Post Exploitation_
- 综合工具 _Nice Tools_
- 二进制库 _Binaries and Libraries_
- 权限维持 _Persistence_
- 内存马 _MemShell_
- Webshell 管理 _Webshell Management_
- Webshell 免杀 _Webshell Bypass_
- 反弹 Shell 管理 _Reverse Shell Management_
- 权限提升 _Pri Escalation_
- Linux 本地枚举 _Linux Local Enumeration_
- Windows 本地枚举 _Windows Local Enumeration_
- Windows 提权 _Windows Exploits_
- Linux 提权 _Linux Exploits_
- 数据库提权 _Database Exploits_
- 防御规避 _Defense E
- Linux 防御规避 _Linux Defense E
- Windows 防御规避 _Windows Defense E
- 内网穿透 _Proxy_
- 代理客户端 _Proxy Client_
- 代理工具 _Proxy Tools_
- DNS 隧道 _DNS Tunnel_
- ICMP 隧道 _ICMP Tunnel_
- 端口转发 _Port Forwarding_
- 操作安全 _Operation Security_
- 域内信息收集 _Collection and Discovery_
- 域内权限提升 _Pri Escalation_
- 域内漏洞利用 _Known Exploited
- MS14-068
- noPac
- Zerologon
- ProxyLogon/ProxyShell
- ProxyNotShell
- Printnightmare
- 域内渗透方式 _Methodology_
- Coerce and Relay
- Delegation
- ADCS
- ACLs and ACEs
- 内存马查杀 _Memshell Detection_
- Webshell 查杀 _Webshell Detection_
- 攻击研判 _Blue Teaming_
- 基线加固 _Enforcement_
- 应急响应 _Incident Response_
- 勒索病毒 _Ransomware_
- 搜索引擎 _Search Engine_
- 解密工具 _Decryption Tools_
- 开源蜜罐 _Open-Source Honeypot_
- 逆向工程 _Reverse Engineering_
- 综合工具 _Nice Tools_
- 静态分析 _Static Analysis_
- 动态调试 _Dynamic Analysis_
- Java
- Mobile
- Python
- Rust/Go/.NET
- 开源资源 _Resources_
- 云安全矩阵 _Cloud Threat Matrix_
- 云服务 _Cloud Ser
- 云管平台 _Management Tools_
- AK/SK 利用 _AK/SK Exploit_
- 云原生 _Cloud Native_
- 综合工具 _Nice Tools_
- 容器 _Docker_
- 集群 _Kubernetes_
- 如何快速使用 alias
- 如何优化原生终端
- 如何解决终端中文乱码
项目导航 _Project Na
速查文档 _CheatSheets_
戳这里 Click Here
一些代码 _Scripts_
戳这里 Click Here
攻防知识 _Tips_
戳这里 Click Here
开源导航 _Open-Source Na
编解码/加解密 _Cryptography_
#### 在线工具 _Online Tools_
#### 离线工具 _Offline Tools_
#### 编码/解码 _Encode/Decode_
#### 正则表达式 _Regular Expressions_
#### 哈希算法 _Hash Algorithms_
#### 公钥密码算法 _RSA_
#### 国密算法 _SM Algorithms_
网络空间测绘 _Cyberspace Search Engine_
#### 综合工具 _Nice Tools_
#### 网页/端口 _Web/Ports_
#### 谷歌搜索 _Google Hacking_
#### Github 搜索 _Github Dork_
开源情报 _Open-Source Intelligence_
#### 综合工具 _Nice Tools_
#### 威胁情报 _Threat Intelligence_
#### 漏洞披露 _Disclosed
curl | jq '[.cves[] | select(.cvss > 8)]'#### 接口检索 _API Search_
#### 源代码检索 _Source Code Search_
开源资源 _Open-Source Resources_
#### 社区/知识库 _Communities/Knowledge Base_
#### 思维导图/备忘录 _Mindmap/Cheat Sheets_
#### 进攻性安全 _Red Teaming and Offensi
#### 防御性安全 _Blue Teaming and Defensi
#### 操作安全 _Operation Security_
#### 实战平台 _Learning and Practice Platforms_
Mac M1 使用 等 ova 格式镜像,需要将 ova 格式转为 qcow2,再通过 UTM 运行:
信息收集 _Reconnaissance_
综合工具 _Nice Tools_
IP/域名/子域名 _IP/Domain/Subdomain_
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
指纹 _Fingerprint_
#### 指纹库 _Fingerprint Collection_
#### 指纹识别 _Fingerprint Reconnaissance_
#### WAF 识别 _Waf Checks_
扫描/爆破 _Brute Force_
#### 扫描/爆破工具 _Brute Force Tools_
-
-
-
-
-
-
-
-
-
-
-
-
- 支持 sshkey 和 openvpn
-
-
-
- hashcat 示例
- 哈希类型识别
- 哈希类型识别
-
-
-
-
-
-
-
#### 扫描/爆破字典 _Brute Force Dictionaries_
- 46.4k star
- + ffuf
-
-
-
-
-
-
-
-
-
-
-
-
-
-
#### 字典生成 _Generate a Custom Dictionary_
- Generate wordlists:
- Generate subdomains and wordlists:
- 汉字转拼音:
- 密码猜解:
- Generate wordlists(offline):
- Generate subdomains and wordlists(offline):
- pydictor:
- crunch:
- Kali/Linux:
- Windows:
#### 默认口令查询 _Default Credentials_
-
-
-
-
-
社会工程学 _Social Engineering_
#### 凭据泄露 _Leaked Credentials_
#### 邮箱 _Email_
-
-
-
#### 短信 _SMS Online_
#### 钓鱼 _Phishing_
移动端 _Mobile_
漏洞研究 _ Research_
漏洞环境 _ En
#### 基础漏洞 _Basic
#### 综合漏洞 _Comprehensi
#### 工控环境 _ IoT En
#### 域环境 _ Acti En
#### 云环境 _ Cloud En
PoC _Proof of Concept_
> Be careful Malware,POC 库最新的 CVE 可能存在投毒风险。
#### PoC/ExP
searchsploit <关键词> 使用#### PoC 模板 _PoC Templates_
漏洞利用 _ Exploits_
综合工具 _Nice Tools_
代码审计 _Code Audit_
序列化 _Serialization_
#### Java
反序列化 _Deserialization_
#### Java
#### PHP
数据库 _Database_
#### Redis
#### MySQL
#### Oracle
#### MSSQL
信息泄露 _Information Disclosure_
CMS/OA 漏洞 _CMS/OA_
中间件/应用层 _Middleware/Application_
Confluence
Druid
Fastjson
GitLab
Nacos
Nps
Java
Shiro
Struts
Spring Boot
Tomcat
Thinkphp
Weblogic
WebSocket
Zookeeper
渗透测试 _Penetration Testing_
综合工具 _Nice Tools_
渗透插件 _Extensions_
#### Chrome
#### Burp Suite
#### Yakit
辅助工具 _Auxiliary Tools_
#### 工具集 _Open-Source Toolkit_
#### 带外通道 _DNSLog_
#### 终端优化 _Command Line_
- 在线查询工具
- go 版本
- python 版本
#### 代码美化 _Beautifier_
#### 生成器 _Generator_
SQL 注入 _SQL Injection_
访问控制 _Access Control_
#### 403 绕过 _Bypass 40X errors_
跨站脚本 _XSS_
文件包含 _File Inclusion_
服务端请求伪造 _SSRF_
移动端安全 _Mobile Security_
#### 小程序 _Mini Program_
#### 应用程序 _APK_
#### SessionKey 解密 _SessionKey_
载荷与绕过 _Payload and Bypass_
内网渗透 _Red Teaming and Offensi
基础设施 _Infrastructure_
信息收集 _Reconnaissance_
凭证获取 _Credential Access_
#### 凭证转储 _Credential Dumping_
#### 本地枚举 _Local Enumeration_
- 版本 < 7.0
- 本地解密
-
#### 哈希破解 _NTLM Cracking_
- 3107
- 100k
后渗透 _Post Exploitation_
#### 综合工具 _Nice Tools_
- Awesome CobaltStrike:
- Erebus:
- LSTAR:
- Ele:
- C2Re:
- pystinger:
#### 二进制库 _Binaries and Libraries_
权限维持 _Persistence_
#### 内存马 _MemShell_
#### Webshell 管理 _Webshell Management_
#### Webshell 免杀 _Webshell Bypass_
#### 反弹 Shell 管理 _Reverse Shell Management_
权限提升 _Pri Escalation_
#### Linux 本地枚举 _Linux Local Enumeration_
#### Windows 本地枚举 _Windows Local Enumeration_
#### Windows 提权 _Windows Exploits_
#### Linux 提权 _Linux Exploits_
#### 数据库提权 _Database Exploits_
防御规避 _Defense E
#### Linux 防御规避 _Linux Defense E
#### Windows 防御规避 _Windows Defense E
内网穿透 _Proxy_
#### 代理客户端 _Proxy Client_
#### 代理工具 _Proxy Tools_
#### DNS 隧道 _DNS Tunnel_
#### ICMP 隧道 _ICMP Tunnel_
#### 端口转发 _Port Forwarding_
操作安全 _Operation Security_
域渗透 _Acti Penetration_
域内信息收集 _Collection and Discovery_
-
-
-
-
-
-
-
-
-
-
-
-
-
-
-
域内权限提升 _Pri Escalation_
域内漏洞利用 _Known Exploited
#### MS14-068
#### noPac
> C/C
#### Zerologon
> C
#### ProxyLogon/ProxyShell
> C
#### ProxyNotShell
> C/C
#### Printnightmare
> C/C
域内渗透方式 _Methodology_
#### Coerce and Relay
#### Delegation
#### ADCS
> Acti Certificate Services
- Certify:
- Certipy:
- certi:
- PKINITtools:
- ADCSPwn:
#### ACLs and ACEs
防御性安全 _Blue Teaming and Defensi
内存马查杀 _Memshell Detection_
Webshell 查杀 _Webshell Detection_
攻击研判 _Blue Teaming_
基线加固 _Enforcement_
应急响应 _Incident Response_
勒索病毒 _Ransomware_
#### 搜索引擎 _Search Engine_
#### 解密工具 _Decryption Tools_
开源蜜罐 _Open-Source Honeypot_
逆向工程 _Reverse Engineering_
#### 综合工具 _Nice Tools_
#### 静态分析 _Static Analysis_
#### 动态调试 _Dynamic Analysis_
#### Java
#### Mobile
#### Python
#### Rust/Go/.NET
#### Ja
云安全 _Cloud Security_
开源资源 _Resources_
-
-
-
-
云安全矩阵 _Cloud Threat Matrix_
云服务 _Cloud Ser
> 三大云服务提供商:
> - Amazon Web Services (AWS) / Microsoft Azure / Google Cloud Platform (GCP)
> - 阿里云 / 腾讯云 / 华为云
#### 云管平台 _Management Tools_
#### AK/SK 利用 _AK/SK Exploit_
云原生 _Cloud Native_
#### 综合工具 _Nice Tools_
#### 容器 _Docker_
#### 集群 _Kubernetes_
提高生产力的使用姿势
如何快速使用 alias
Windows 创建 alias.bat,激活 conda 虚拟环境,在隔离环境下运行程序或工具。双击 alias.bat,重启 cmd,配置生效。
将 alias.bat 配置为开机自启动:
计算机\HKEY_CURRENT_USER\Software\Microsoft\Command Processor;autorun,赋值为 alias.bat 所在位置,例如 D: \Software\alias.bat;MacOS 编辑 .zshrc,重启 shell,配置生效:
如何优化原生终端
Windows 通过 tabby + clink 优化原生终端,实现命令自动补全、vps ssh/ftp/sftp、输出日志记录等功能:
MacOS 通过 warp + ohmyzsh 优化原生终端,warp 自带命令自动补全,引入“块”概念,提供了更现代化的编程体验(Modern UX and Text Editing):
如何解决终端中文乱码
Windows 注册表进入 计算机\HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Command Processor,创建字符串值 autorun,赋值为 chcp 65001。
!Stargazers over time
项目信息
开发语言:Python
Star 数:4336
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕一个攻防知识库。A knowledge base for red teaming and offensi.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Awesome-Redteam - 一个攻防知识库。A knowledge base for red teaming and offen |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:08:56 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 523 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |