 黑客技术
点击放大
项目说明
<di="center">
<img src="images/logo.png" alt="WEF" width=23% height=50%>
</div>
<p align="center">
<h4 align="center">WiFi Exploitation 框架</h4>
<h6 align="center">Coded with 💙 by D3Ext</h6>
</p>
<p align="center">
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
</p>
<p align="center">
<a href="#introduction">Introduction</a> •
<a href="#supported-attacks">Attacks</a> •
<a href="#features">Features</a> •
<a href="#installation">Installation</a> •
<a href="#Usage">Usage</a>
</p></br>
<p align="center">
<a href="SPANISH.md">README in spanish</a>
</p>
Introduction
This 工具 is designed for security researchers and penetration testers to analyze and exploit in Wi-Fi networks. It provides an intuiti with a wide range of automated and manual attack techniques to test WPA/WPA2, WPS, and WEP security. With support for both 2.4 GHz and 5 GHz networks, detailed logging and customizable attack options, it offers flexibility for different testing scenarios. This is not a professional 工具.
If you find an error, please open an issue (you can write it in english or spanish, as you want).
Supported attacks
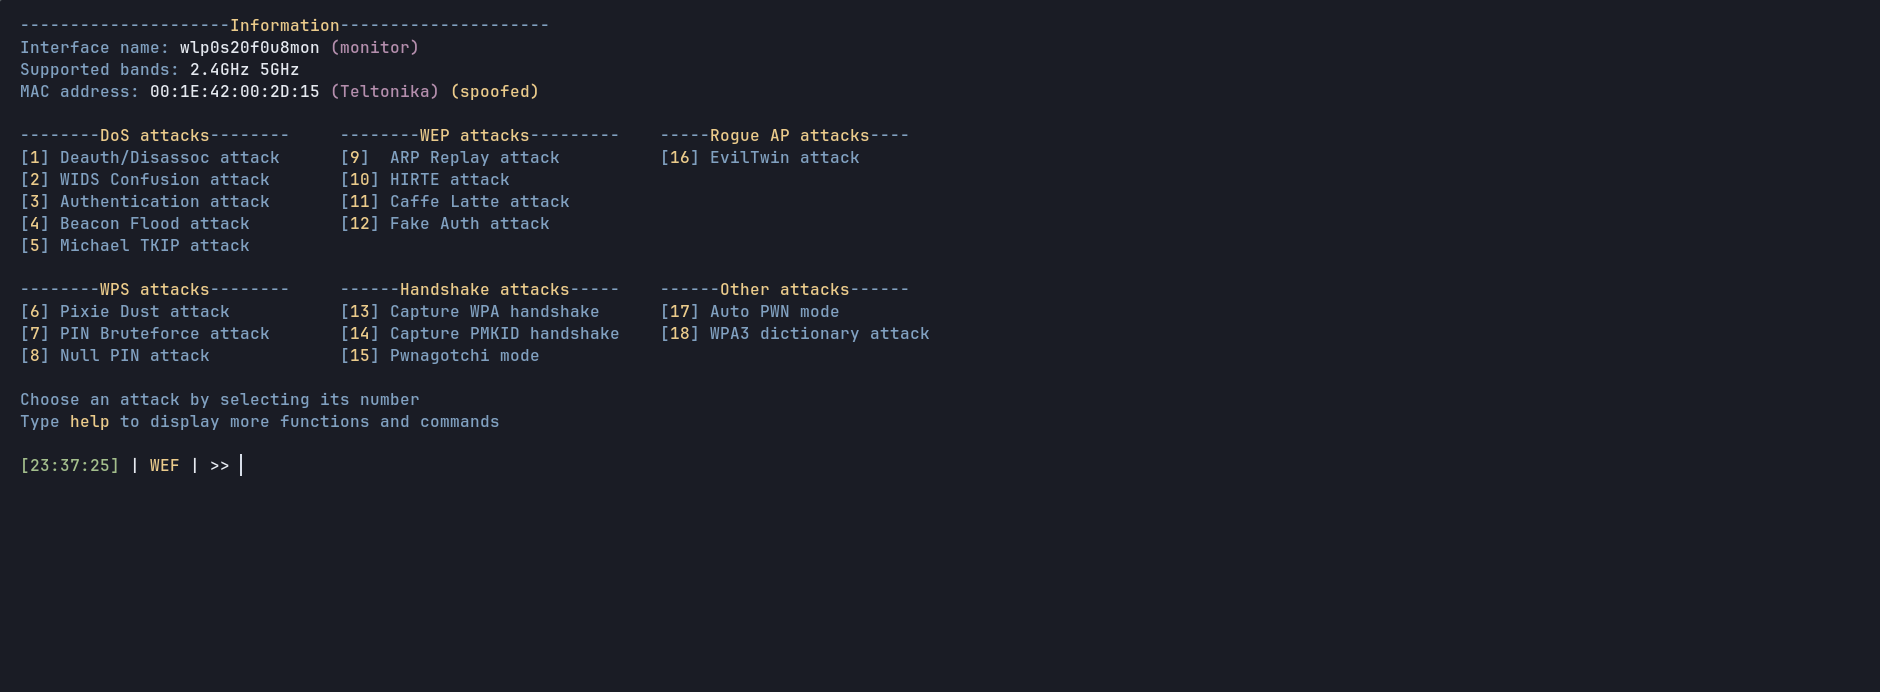
- Deauthentication/Disassociation attack
- WIDS Confusion attack
- Authentication attack
- Beacon Flood attack
- TKIP attack (Michael Shutdown Exploitation)
- Pixie Dust attack
- PIN Bruteforce attack
- Null Pin attack
- ARP Replay attack
- HIRTE attack
- Caffe Latte attack
- Fake Authentication attack
- WPA handshake attack
- PMKID handshake attack
- Pwnagotchi mode
- Evil Twin attack
- BSSID spoofing
- Karma mode
- Enterprise WPA supported
- Deauth supported
- Automatic attack mode (Auto PWN)
- WPA3 dictionary attack
All the mentioned attacks/techniques are explained here on the Wiki
Features
This are some of the most notable features:
:ballot_box_with_check: WPA/WPA2/WPA3, WPS, WEP, Rogue-AP, and Handshake Attacks
:ballot_box_with_check: Automatic attack mode based on the features of the AP
:ballot_box_with_check: Automatic handshake capture
:ballot_box_with_check: Online and offline handshake cracking
:ballot_box_with_check: Simple login template for Evil Twin attack (multiple languages supported)
:ballot_box_with_check: Toggle monitor mode and view information about the 网络 interface (frequencies, chipset, etc.)
:ballot_box_with_check: 2.4 GHz and 5 GHz supported
:ballot_box_with_check: Informati using HTML templates
:ballot_box_with_check: Standalone script
:ballot_box_with_check: English and spanish supported
Installation
> As root
Take a look at the Wiki where I have more info about the 工具
Usage
> Common usage of the 框架 (your interface may ha name)
> Help panel
See here for more information about how to use the 工具 and other related topics
Demo
<img src="
<img src="
<img src="
<img src="
<img src="
<img src="
<img src="
<img src="
TODO
Changelog
See CHANGELOG.md
References
Disclaimer
The creator has no responsibility for any kind of illegal use of the project.
License
This project is under MIT license
Copyright © 2025, *D3Ext*
项目信息
开发语言:Shell
Star 数:3223
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Wi-Fi Exploitation Framework展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | WEF - Wi-Fi Exploitation Framework |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:09:54 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 153 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |