 黑客技术
点击放大
jexboss - JexBoss: Jboss (and Java Deserialization Vulnerabi
项目说明
JexBoss - JBoss (and others Ja ) and EXploitation 工具
==============================================================================================
JexBoss is a 工具 for testing and exploiting in JBoss Application 服务端 and others Ja, Frameworks, Applications, etc.
Requirements
----
* Python >= 2.7.x
* urllib3
* ipaddress
Installation on Linux\Mac
-------------------------
To install the latest of JexBoss, please use the following commands:
git clone
cd jexboss
pip install -r requires.txt
python jexboss.py -h
python jexboss.py -host
OR:
Download the latest at:
unzip master.zip
cd jexboss-master
pip install -r requires.txt
python jexboss.py -h
python jexboss.py -host
If you are using CentOS with Python 2.6, please install Python2.7.
Installation example of the Python 2.7 on CentOS using Collections Software scl:
yum -y install centos-release-scl
yum -y install python27
scl enable python27 bash
Installation on Windows
-----------------------
If you are using Windows, you can use the Git Bash to run the JexBoss. Follow the steps below:
* Download and install Python
* Download and install Git for Windows
* After installing, run the Git for Windows and type the following commands:
Features
----
The 工具 and exploits were de and tested for:
* JBoss Application Ser: 3, 4, 5 and 6.
* Ja in multiple ja, platforms and applications (e.g., Ja Faces - JSF, Seam 框架, RMI over HTTP, Jenkins CLI RCE (C), Remote JMX (C, C), etc)
The exploitation are:
* /admin-console
- tested and working in JBoss 5 and 6
* /jmx-console
- tested and working in JBoss 4, 5 and 6
* /web-console/Invoker
- tested and working in JBoss 4, 5 and 6
* /invoker/JMXIn
- tested and working in JBoss 4, 5 and 6
* Application Deserialization
- tested and working against multiple ja, platforms, etc, via HTTP POST Parameters
* Servlet Deserialization
- tested and working against multiple ja, platforms, etc, that process serialized objets (e.g. when you see an "Invoker" in a link)
* Apache Struts2 C
- tested in Apache Struts 2 applications
* Others
------
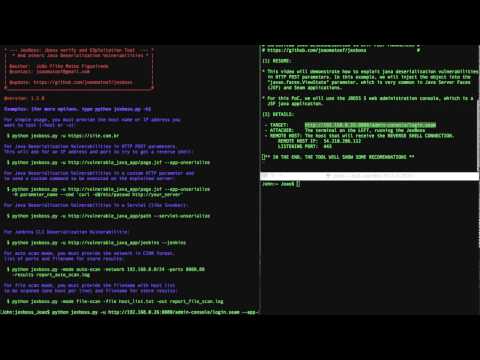
* Exploiting Ja (RCE) on JSF/Seam Applications .faces. with JexBoss
![Alt text]()
* Exploiting JBoss Application 服务端 with JexBoss
![Alt text]()
* Exploiting Apache Struts2 (RCE) with Jexboss (C)
![Alt text]()
Screenshots
----
* Simple usage examples:
!alt tag
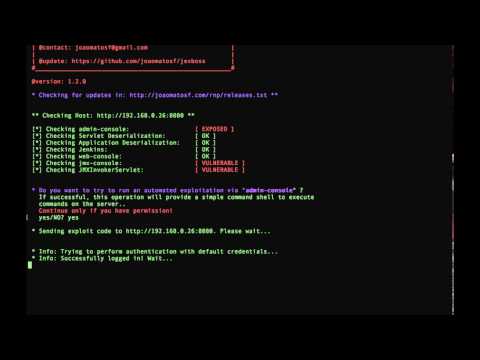
* Example of standalone mode against JBoss:
!alt tag
!alt tag
* Usage modes:
* Network scan mode:
!alt tag
* Network scan with auto-exploit mode:
!alt tag
* Results and recommendations:
!alt tag
Reverse Shell (meterpreter integration)
---------------------------------------
After you exploit a JBoss 服务端, you can use the own jexboss command shell or perform a reverse connection using the following command:
* Example:
!alt tag
When exploiting ja (Application Deserialization, Servlet Deserialization), the default options are: make a reverse shell connection or send a commando to execute.
Usage examples
--------------
* For Ja in a custom HTTP parameter and to send a custom command to be executed on the exploited 服务端:
* For Ja in a custom HTTP parameter and to make a reverse shell (this will ask for an IP address and port of your remote host):
* For Ja in a Servlet (like Invoker):
* For Apache Struts 2 (C)
* For Apache Struts 2 (C) with cookies for authenticated resources
* Auto scan mode:
* File scan mode:
* More Options:
Questions, problems, suggestions and etc:
----
*
项目信息
开发语言:Python
Star 数:2521
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕JexBoss: Jboss (and Ja ) and EXploitation 工具展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | jexboss - JexBoss: Jboss (and Java Deserialization Vulnerabi |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:10:53 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 101 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |