 黑客技术
点击放大
usbrubberducky-payloads - The Official USB Rubber Ducky Payload Repository
项目说明
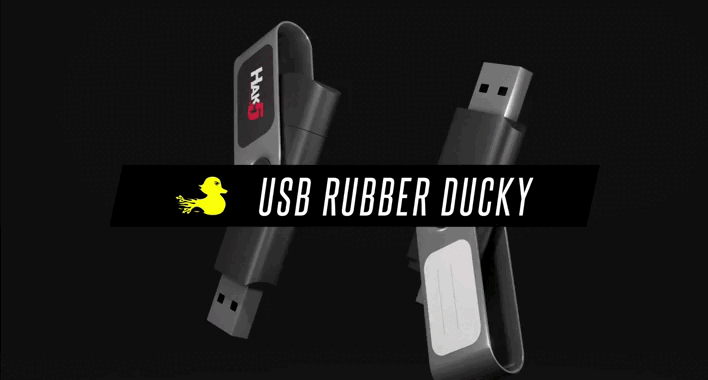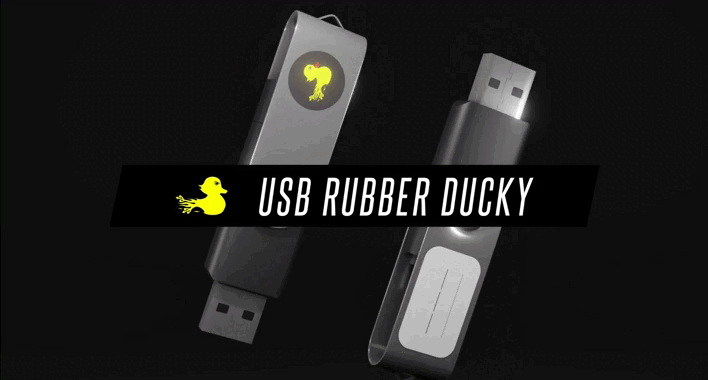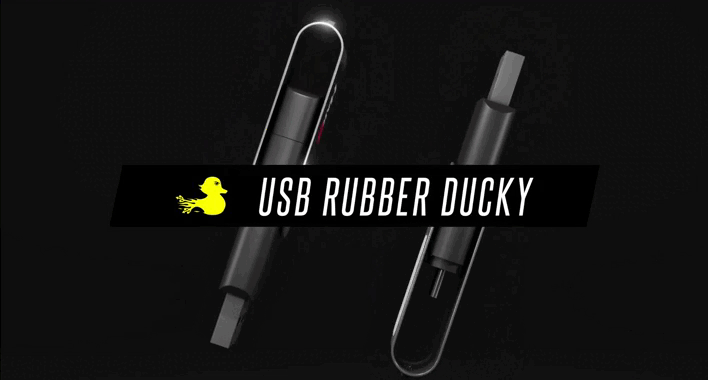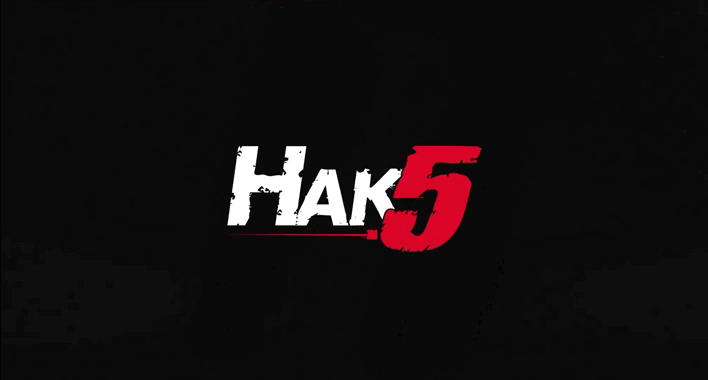
Payload Library for the USB Rubber Ducky by Hak5
This repository contains payloads, extensions and languages for the Hak5 USB Rubber Ducky. Community de payloads are listed and de are encouraged to create pull requests to make changes to or submit new payloads.
Payloads here are written in official DuckyScript™ specifically for the USB Rubber Ducky. Payloads here must be compiled using Hak5 PayloadStudio. Hak5 does NOT guarantee payload functionality. <a href="#legal"><b>See Legal and Disclaimers</b></a>
<di="center">
<img src="
<img src="
<br/>
<img src="
<img src="
</div>
<br/>
<p align="center">
<a href=" src="
<br/>
<a href=" Featured Ducky Payloads and Leaderboard</a>
<br/><i>Get your payload in front of thousands. Enter to win over $2,000 in prizes in the <a href=" Payload Awards!</a></i>
</p>
<di="center">
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<br/><br/>
</div>
Table of contents
<details open>
<ul>
<li><a href="#about-the-new-usb-rubber-ducky">About the USB Rubber Ducky</a></li>
<li><a href="#build-your-payloads-with-payloadstudio">PayloadStudio (Editor + Compiler)</a></li>
<li><a href="#about-duckyscript">About DuckyScript™</a></li>
<li><b><a href="#contributing">Contributing Payloads</a></b></li>
<li><a href="#legal"><b>Legal and Disclaimers</b></a></li>
</ul>
</details>
Shop
Getting Started
Documentation / Learn More
Community
*Got Questions? Need some help? Reach out:*
Additional Links
<b> Follow the creators </b><br/>
<p>
<b>Korben's Socials</b><br/>
<a href=" src="
<a href=" src="
<br/>
<b>Darren's Socials</b><br/>
<a href=" src="
<a href=" src="
</p>
<br/>
<h1><a href=" the NEW USB Rubber Ducky</a></h1>
A "flash drive" that types keystroke injection payloads into unsuspecting devices at incredible speeds.
<b><di="center">
<br/>
<a href=" Video</a> |
<a href=" Keystroke Reflection</a> |
<a href=" OS Detection</a>
<br/><br/>
</div></b>
<p align="center">
<a href=" src="
<br/>
<i>New USB Rubber Ducky (A+C, DuckyScript 3.0, 2022)</i>
</p>
Computers trust humans. Humans use keyboards. Hence the uni spec — HID, or Human Interface Device.
A keyboard presents itself as a HID, and in turn it's inherently trusted as human by the computer.
The USB Rubber Ducky — which looks like an innocent flash drive to humans — takes ad of this trust to deli payloads, injecting keystrokes at superhuman speeds.
Easily automate any task you can perform with a keyboard with an easy to learn language designed specifically for the USB Rubber Ducky.
About DuckyScript™
Legacy DuckyScript (1.0)
Hak5 introduced Keystroke Injection in 2010 with the USB Rubber Ducky™. This technique, de by Hak5 founder Darren Kitchen, was his weapon of choice for automating mundane tasks at his IT job — fixing printers, 网络 shares and the like.
Today the USB Rubber Ducky is a hacker culture icon, synonymous with the keystroke injection technique it pioneered. It’s found its way into the hearts and toolkits of Cybersecurity and IT pros the world over — including many movies and T!
Core to its success is its simple language, DuckyScript™. Originally just three commands, it could be learned by anyone—regardless of experience—in minutes.
<b> With the new USB Rubber Ducky in 2022, DuckyScript 3.0 has been introduced.</b>
DuckyScript 3.0
DuckyScript 3.0 is a feature rich, structured programming language. It includes all of the pre a commands and features of the original DuckyScript.
<b>(DuckyScript 3.0 is backwards compatible with DuckyScript 1.0; this means all your fa DuckyScript 1.0 payloads are valid DuckyScript 3.0) </b>
Additionally, DuckyScript 3.0 introduces control flow constructs, loops, functions, extensions.
Plus, DuckyScript 3.0 includes many features specific to keystroke injection attack/automation, such as HID & Storage attack modes, OS Detection, Keystroke Reflection (Video + Whitepaper), jitter and randomization to name a few.
While many of the Hak5 Tools run of DuckyScript; unlike the Bash Bunny, Key Croc and even the officially licenced DuckyScript compatible devices from O.MG - which use INTERPRETED of DuckyScript - the USB Rubber Ducky uses COMPILED inject.bin payloads.
_Interpreted DuckyScript means the payload runs straight from source code (the code you write e.g. DELAY 1000)._
_Compiled DuckyScript means that there is both source code and an inject.bin generated from the 源码 代码. (DuckyScript 1.0 was "encoded" rather than "compiled" - references to either mean the same)_
The files in this repository are _the source code_ in the form of payload.txt files.
<h1><a href=" DuckyScript directly from the creators</a></h1>
<p align="center">
<a href=" width="500px" src="
<p>
Learn Ad DuckyScript directly from the creators and unlock creati for the USB Rubber Ducky. Co all aspects of ad DuckyScript and Keystroke Injection attacks, these practical lessons build on one another from the basics on up.
This online course includes 7 hours of video instruction co 54 lessons, 40+ exercises to reinforce your knowledge, quizzes throughout as well as 8 projects to test your skills.
</p>
</p>
<h1><a href=" your payloads with PayloadStudio</a></h1>
<p align="center">
Take your DuckyScript™ payloads to the next level with this full-featured,<b> web-based (entirely 客户端 side) </b> de en.
<br/>
<a href=" width="500px" src="
<br/>
<i>Payload studio features all of the con of a modern IDE, right from your browser. From syntax highlighting and auto-completion to li and repo synchronization - building payloads for Hak5 hotplug tools has never been easier!
<br/><br/>
Supports your fa Hak5 gear - USB Rubber Ducky, Bash Bunny, Key Croc, Shark Jack, Packet Squirrel & LAN Turtle!
<br/><br/></i><br/>
<a href=" a PayloadStudio Pro</a> and <b> Unleash your hacking creativity! </b>
<br/>
OR
<br/>
<a href=" Try Community Edition FREE</a>
<br/><br/>
<img src="
<br/>
<i> Payload Studio Themes Preview GIF </i>
<br/><br/>
<img src="
<br/>
<i> Payload Studio Autocomplete Preview GIF </i>
</p>
DuckyScript Ecosystem
<h3><a href=' </a></h3>
Support for different keyboard layouts can be found, modified or contributed to in the <b><a href=' languages/ </a></b> directory of this repository.
Compiling payloads for the correct language / keyboard layout has never been easier:
<a href=' Open PayloadStudio \> Settings \> Compiler Settings</a>
PayloadStudio includes all the languages provided in this repo built-in for your con.
<a href=" Pro</a> has a <b>dedicated language editor</b> specifically for editing and building language files!
The default language is US <a href=')</a>
<h3><a href="
It should be clear by now that so much is possible with DuckyScript 3.0. The combination of keystroke injection with attack modes, logic and data processing, along with the built-in features like randomization and internal — the possibilities for ad payload functions seems endless.
<p align="center">
<br/>
<img src="
<br/>
<i> Payload Studio Extensions Preview GIF</i>
</p>
As the payload library continues to grow, so too will the DuckyScript 3.0 language. To that end, the extensions feature of the language and editor facilitate the continued growth of the language.
<b>Extensions are blocks of reusable 代码 which may be implemented in any payload. Think of them as snippets, or building blocks, upon which your next payload may benefit.</b>
While Hak5 de cannot en all possible use cases for the USB Rubber Ducky, the DuckyScript language has been architected in such a way so that the community as a whole may gain new features and abilities with each contributed extension.
Extensions (beyond some first party examples) are currently reserved for collections of helper functions (+ required , defines, and configuration options) required to make a complex task simple - abstracting very complex problems down into one or a few calls for the ease of use to others (example: the translate extension).
To add an extension to your payload, simply start typing the name of the desired extension in your payload from within PayloadStudio then select it from the auto-complete drop down. Alternatively the full library can be found from within the Extensions folder of this repo.
Read more here
<h1><a href='
<p align="center">
<a href=" src="
<br/>
<a href=" Featured Payloads and Leaderboard </a>
</p>
Please adhere to the following best practices and style guides when submitting a payload.
Once you ha your payload, you are encouraged to contribute to this repository by submitting a Pull Request. Re and Approved pull requests will add your payload to this repository, where they may be publically a.
Please include all resources required for the payload to run. If needed, provide a README.md in the root of your payload's directory to explain things such as intended use, required configurations, or anything that will not easily fit in the comments of the payload.txt itself. Please make sure that your payload is tested, and free of errors. If your payload contains (or is based off of) the work of other's please make sure to cite their work giving proper credit.
Purely Destructi will not be accepted. No, it's not "just a prank".
Subject to change. Please ensure any submissions meet the latest of these standards before submitting a Pull Request.
Naming Con
Please give your payload a unique, descriptive and appropriate name. Do not use spaces in payload, directory or file names. Each payload should be submit into its own directory, with
- or _ used in place of spaces, to one of the categories such as exfiltration, phishing, remote_access or recon. Do not create your own category.Staged Payloads
"Staged payloads" are payloads that download 代码 from some resource external to the payload.txt.
While staging 代码 used in payloads is often useful and appropriate, using this (or another) github repository as the means of deploying those stages is not. This repository is not a CDN for deployment on target systems.
Staged 代码 should be copied to and hosted on an appropriate 服务端 for doing so by the end user - Github and this repository are simply resources for sharing 代码 among de and users.
See: GitHub acceptable use policies
Additionally, any 源码 代码 that is intended to be staged (by the end user on the appropriate infrastructure) should be included in any payload submissions either in the comments of the payload itself or as a seperate file. Links to staged code are unacceptable; not only for the reasons listed above but also for control and user safety reasons. Arbitrary 代码 hidden behind some pre-defined external resource via URL in a payload could be replaced at any point in the future unbeknownst to the user -- potentially turning a harmless payload into something dangerous.
Including URLs
URLs used for retrieving staged 代码 should refer exclusively to example.com using DEFINE in any payload submissions see Payload Configuration section below.
Staged Example
Example scenario: your payload downloads a script and the executes it on a target machine.
Simple Example of this style of payload
Payload Configuration
Be sure to take the following into careful consideration to ensure your payload is easily tested, used and maintained.
In many cases, payloads will require some level of configuration by the end payload user.
DEFINE where possible. Best practice is to use labels that start with # for easy identification throughout your payload.<pre>
Example:
BEGINNING OF PAYLOAD
... Payload Documentation...
REM CONFIGURATION
REM REQUIRED - Provide URL used for Example
DEFINE #MY_TARGET_URL example.com
REM OPTIONAL - How long until payload starts; default 5s
DEFINE #BOOT_DELAY 5000
DELAY #BOOT_DELAY
...
STRING #MY_TARGET_URL
...
</pre>
Payload Documentation
Payloads should begin with
REM comments specifying the title of the payload, the author, the target, and a brief description.<pre>
Example:
BEGINNING OF PAYLOAD
REM Title: Example Payload
REM Author: Korben Dallas
REM Description: Opens hidden powershell and
REM Target: Windows 10
REM Props: Hak5, Darren Kitchen, Korben
REM : 1.0
REM Category: General
</pre>
<h1><a href="
Payloads from this repository are provided for educational purposes only. Hak5 gear is intended for authorized auditing and security analysis purposes only where permitted subject to local and international laws where applicable. Users are solely responsible for compliance with all laws of their locality. Hak5 LLC and affiliates claim no responsibility for unauthorized or unlawful use.
USB Rubber Ducky and DuckyScript are the trademarks of Hak5 LLC. Copyright © 2010 Hak5 LLC. All rights reserved. No part of this work may be reproduced or transmitted in any form or by any means without prior written permission from the copyright owner.
USB Rubber Ducky and DuckyScript are subject to the Hak5 license agreement ()
DuckyScript is the intellectual property of Hak5 LLC for the sole benefit of Hak5 LLC and its licensees. To inquire about obtaining a license to use this material in your own project, contact us. Please report counterfeits and brand abuse to .
This material is for education, authorized auditing and analysis purposes where permitted subject to local and international laws. Users are solely responsible for compliance. Hak5 LLC claims no responsibility for unauthorized or unlawful use.
Hak5 LLC products and technology are only a to BIS recognized license exception ENC fa treatment countries pursuant to US 15 CFR Supplement No 3 to Part 740.
See also:
Hak5 Software License Agreement
Terms of Service
Disclaimer
<h3><b>As with any script, you are advised to proceed with caution.</h3></b>
<h3><b>Generally, payloads may execute commands on your device. As such, it is possible for a payload to damage your device. Payloads from this repository are provided AS-IS without warranty. While Hak5 makes a best effort to review payloads, there are no guarantees as to their effecti.</h3></b>
项目信息
开发语言:PowerShell
Star 数:6082
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕The Official USB Rubber Ducky Payload Repository展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | usbrubberducky-payloads - The Official USB Rubber Ducky Payload Repository |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:11:12 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 331 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |