 黑客技术
点击放大
AboutSecurity - Everything for pentest. | 渗透测试知识库,以 AI Agent 可执行的格
项目说明
中文文档 | English
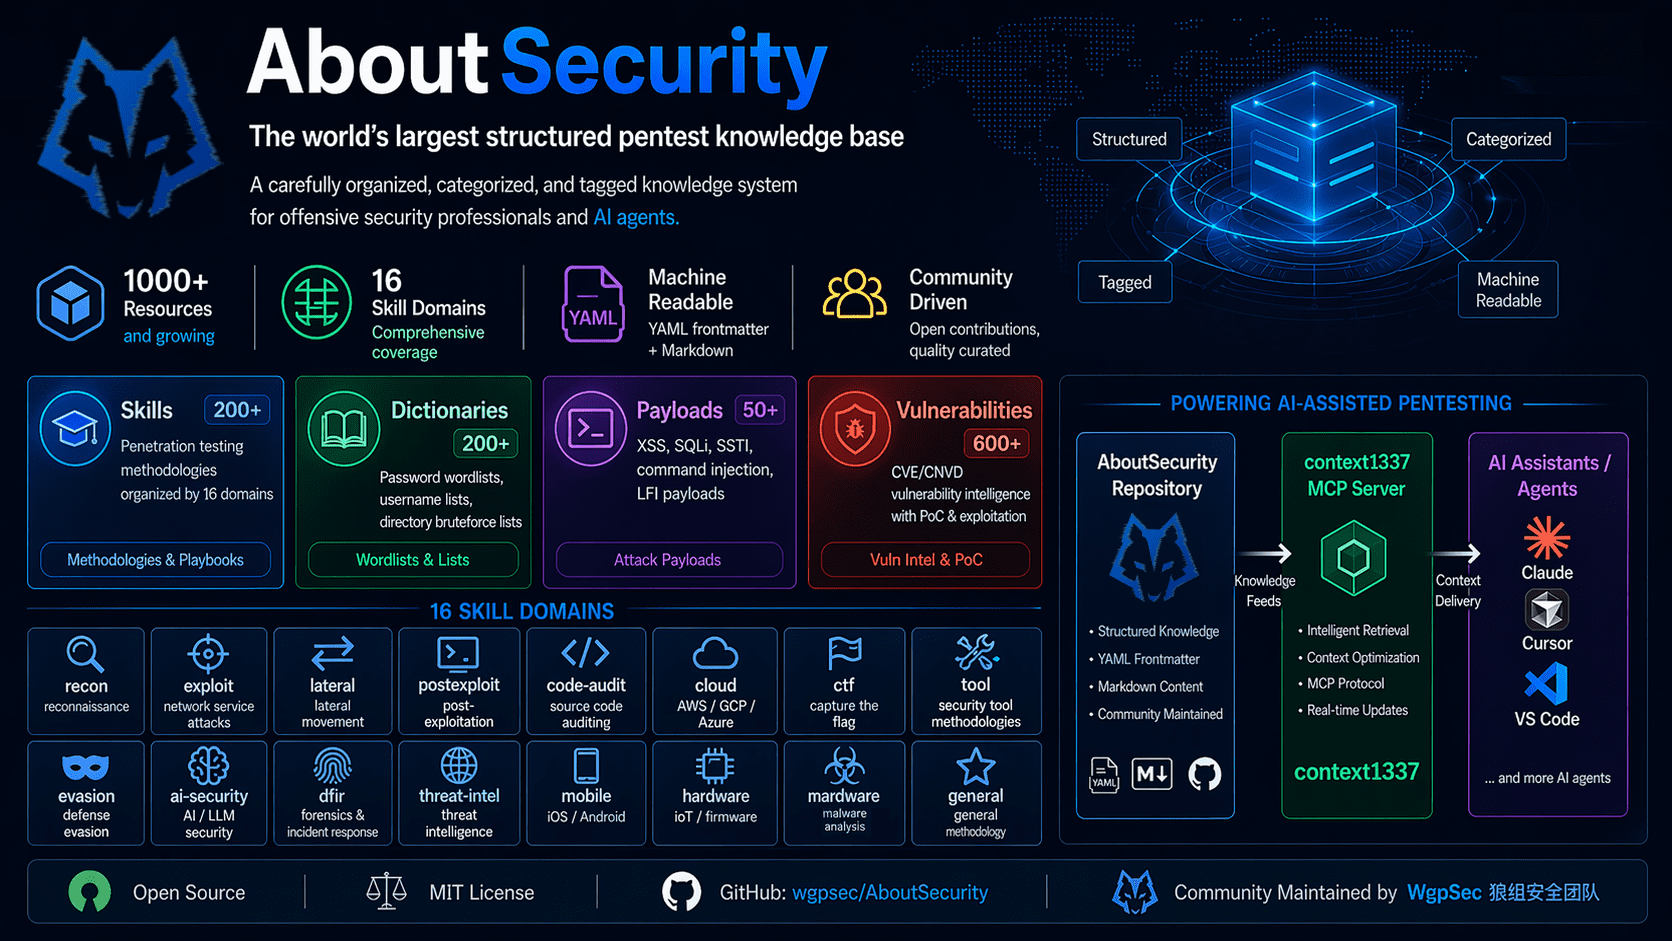
!AboutSecurity — The world's largest structured pentest knowledge base
AboutSecurity
Penetration testing knowledge base with security methodologies in AI Agent-executable format.
Core Modules
Skills/ — 200+ skill methodologies co the full chain from recon to post-exploitation
ai-security/ — AI security (prompt injection, model jailbreaking, prompt leaking, agent attack chains)cloud/ — Cloud en (Docker escape, K8s attack chains, AWS IAM, Alibaba Cloud, Tencent Cloud, Ser)code-audit/ — 代码 auditing (PHP 8-skill system, Ja system co injection/file/serialization/auth/框架/exploit chains)ctf/ — CTF competitions (Web challenges, re, PWN, cryptography, forensics, AI/ML)dfir/ — Digital forensics & incident response (memory forensics & anti-forensics, disk forensics, log e)e/ — E techniques (C2 frameworks, shellcode generation, security research)exploit/ — Exploitation (organized by subcategory)-
ad/ — Ad exploitation (HTTP smuggling, race conditions, supply chain attacks, OT/ICS, crypto attacks)-
auth/ — Authentication & authorization (JWT, OAuth/SSO, IDOR, CORS, CSRF, cookie analysis)-
binary/ — Binary exploitation methodology and tools-
network-service/ — 网络 service pentesting by port/协议 (SMB, FTP, SMTP, DNS, LDAP, etc.)-
web-method/ — Web methodology (injection, XSS, SSRF, SSTI, file upload, deserialization, WAF bypass...)general/ — General (report generation, supply chain auditing, mobile backend API)hardware/ — Hardware/physical access pentestinglateral/ — Lateral mo (AD domain attacks, NTLM relay, 数据库 pi, Kerberoasting, ACL abuse)malware/ — Malware (sample analysis methodology, C2 beacon config extraction, sandbox e)mobile/ — Mobile app pentesting (Android, iOS)postexploit/ — Post-exploitation-
post-exploit-linux/ / post-exploit-windows/ — OS-le escalation, credential theft-
persist-maintain/ — Persistence techniques (cron, services, webshell)-
tool-delivery/ — 工具 delivery to compromised hosts (fscan, frp, chisel, linpeas, mimikatz, etc.; Linux/Windows transfer methods: wget/curl/certutil/bitsadmin/PowerShell/python/nc/base64/SMB; no-egress scenarios, A, post-exec cleanup)-
product/ — Product-specific post-exploitation tactics (ArgoCD, Harbor, databases, middleware, Portainer, RabbitMQ)recon/ — Reconnaissance (subdomain enumeration, passi gathering, JS API extraction)threat-intel/ — Threat intelligence (IOC e, APT simulation, threat hunting e)tool/ — 工具 usage (fscan, nuclei, sqlmap, msfconsole, ffuf, hashcat)Dic/ — Dictionary library (lowercase hyphen-separated naming, each directory has _meta.yaml metadata)
auth/ — Usernames/passwords (complexity-rule passwords, WPA, pinyin names), plus default credentials of go/enterprise security appliances & OA systems (de/)network/ — DNS servers, excluded IP rangesport/ — Ser brute-force dictionaries (mysql, redis, ssh, etc. — 19 types)regular/ — General-purpose dictionaries (numbers, letters, addresses, keywords)web/ — Web directories, API parameters, middleware, upload bypass, webshells, HTTP headersPayload/ — Attack payloads (lowercase hyphen-separated naming, each directory has _meta.yaml metadata)
sqli/, xss/, ssrf/, xxe/, lfi/, rce/, upload/, cors/, hpp/, format/, ssi/, email/, access-bypass/, prompt-injection/Vuln/ — 600+ entries, structured data organized by product
ai/ — AI-related (ComfyUI, Dify, LangFlow, AnythingLLM, etc.)cloud/ — Cloud platforms (AWS API Gateway, etc.)middleware/ — Middleware (ActiveMQ, Nacos, Grafana, Jenkins, RocketMQ, etc. — 394 entries)network/ — 网络 devices (routers, switches, etc.)web/ — Web applications (1Panel, WordPress, OFBiz, etc.)> postexploit/ vs Vuln/: Skills under postexploit/ are the post-exploitation layer — what to do after gaining access (pri escalation, persistence, credential extraction, lateral mo, product-specific tactics). Entries under Vuln/ are the data layer — affected , PoC 代码, specific exploitation steps per CVE. In short: Skills tell you "what to do after you're in", Vuln tells you "how to get in".
Quick Start
1. Clone the Repository
2. Sync Skills to Your Project
> Omit --target to sync to the AboutSecurity repo itself (for using Agent directly in this repo). Re-run after adding or removing skills.
3. Using Dictionaries & Payloads
Dictionaries and payloads don't need syncing — just reference the paths in your Agent con:
The Agent reads these files directly via Read / Glob tools — just provide the correct repo path.
<details>
<summary><b>Background (for newcomers): What is a Skill? Why sync?</b></summary>
SKILL.md) that tells an AI Agent "what to do when encountering scenario X".claude/skills/<name>/SKILL.mdskills/exploit/web-method/sql-injection/SKILL.md), the sync script creates symlinks for the nested → flat mapping</details>
4. Use via MCP Service (context1337) (Highly Recommended)
If you want to search and invoke all resources in this repo language through AI assistants (Claude 代码, Cursor, Claude Desktop, etc.), deploy context1337 — a standalone MCP resource service that turns AboutSecurity from a file repo into a consumable API (like context7, but for security).
Then add the MCP service to your AI 工具:
After that, query with natural language: "Search for SQL injection resources", "List all XSS payloads", "Find critical Apache ", etc. See context1337 README for details.
---
Skills O
skills/README.md covers the skills classification architecture, format specification, and benchmark testing process.
Dic/Payload Naming Con
Directory Naming
file-backup/, api-param/, prompt-injection/File Naming
Fuzz_ prefix (legacy naming has been cleaned up)password-top100.txt, xss-tag-e.txt, complex-8char-upper-lower-digit.txt_meta.yaml Metadata
Every directory containing data files has a _meta.yaml pro structured metadata for AI search:
description and usage use Chinese, tags are bilingual (Chinese + English). Update the corresponding _meta.yaml when adding new dictionary/payload files.
Contributing
Read CONTRIBUTING.md before submitting, which covers Skill format specification, Vuln 数据库 writing standards, references requirements, and benchmark testing process.
WgpSec Agentic Ecosystem
AboutSecurity is the knowledge layer of the WgpSec Agentic Ecosystem — a full-stack pipeline from structured security knowledge to autonomous penetration testing.
| Project | Role |
|---------|------|
| AboutSecurity | Structured pentest knowledge base (Skills, Dic, Payload, Vuln) |
| context1337 | MCP Server — turns AboutSecurity into a searchable API for AI agents |
| tchkiller | Autonomous pentest agent with multi-round decision-making and team collaboration |
| benchmark-platform | HunXiang CTF challenge platform for e agent offensi |
| benchmark-challenges | Challenge data repository — packed & distributed Releases |
| PoJun | General-purpose AI problem-solving 引擎 (private) |
References
项目信息
开发语言:Python
Star 数:1773
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕E for pentest. | 渗透测试知识库,以 AI Agent 可执行的格式沉淀安全方法论。展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AboutSecurity - Everything for pentest. | 渗透测试知识库,以 AI Agent 可执行的格 |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:12:26 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 201 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |