 黑客技术
点击放大
项目说明
<p align="center">
<img src="./.github/img/banner.png">
<br/>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
</p>
Inroduction
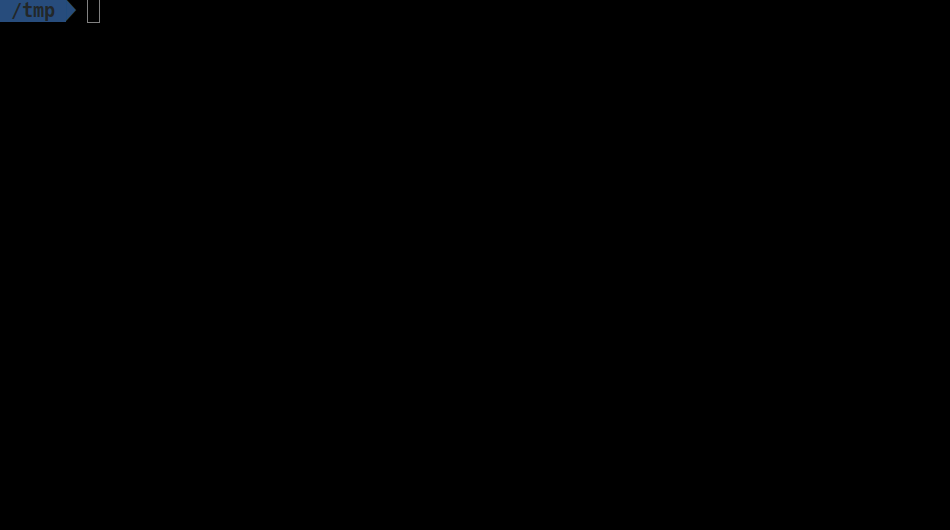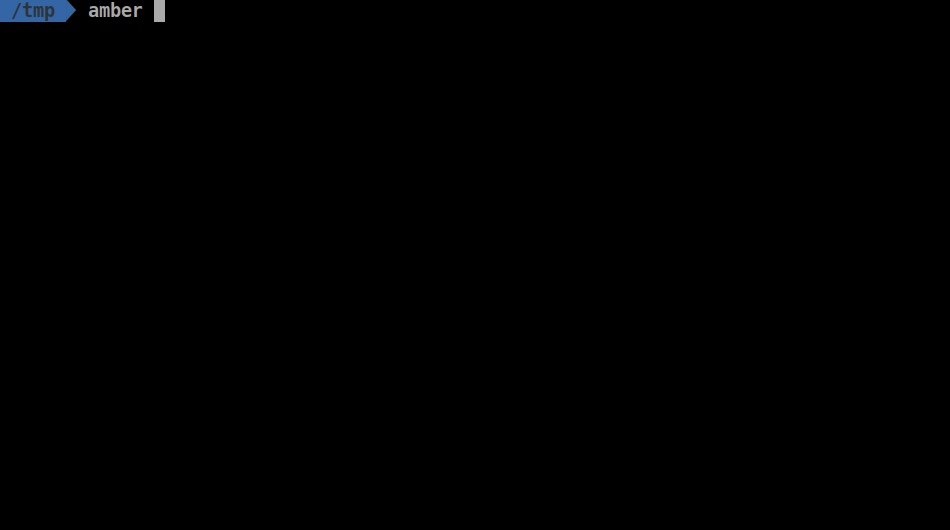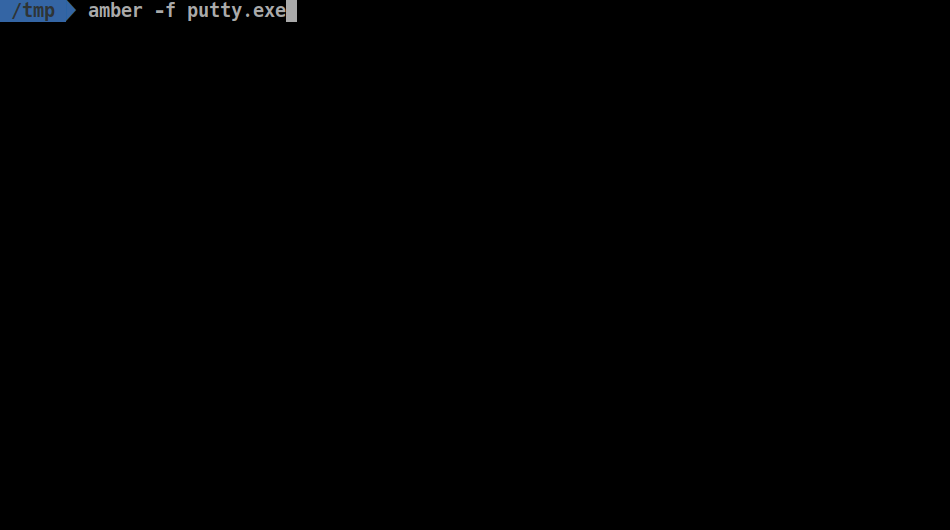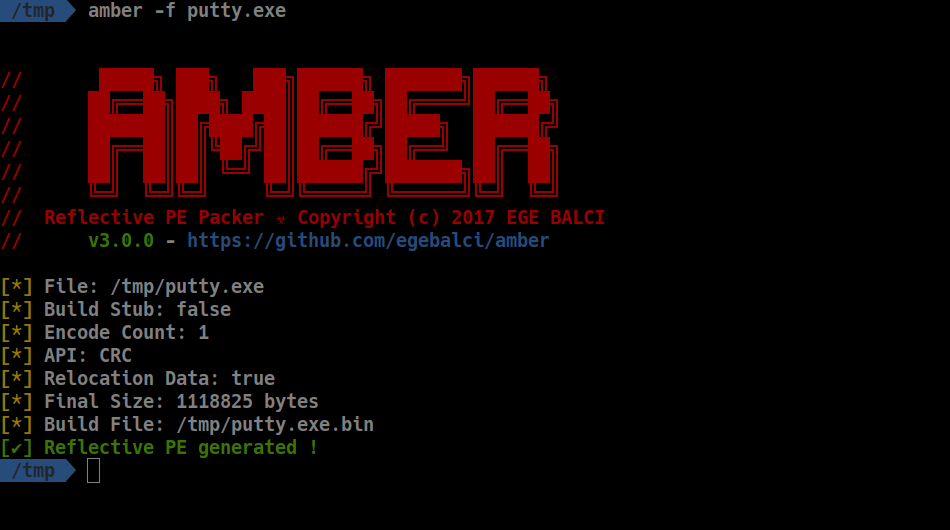
Amber is a position-independent(reflective) PE loader that enables in-memory execution of native PE files(EXE, DLL, SYS...). It enables stealthy in-memory payload deployment that can be used to bypass anti-virus, firewall, IDS, IPS products, and application white-listing mitigations. Reflecti generated by Amber can either be staged from a remote 服务端 or executed directly in memory much like a generic shellcode. By default, every generated payload is encoded using the new generation SGN encoder. Amber uses CRC32_API and IAT_API for inconspicuously resolving the Windows API function addresses. After the PE file is loaded and executed in memory, the reflecti is erased for e memory scanners.
Installation
Pre-compiled binaries can be found under releases.
*Building From Source*
The only dependency for building the 源码 is the keystone 引擎, follow these instructions for installing the library. Once libkeystone is installed on the system, simply just go get it ツ
*Docker Install*
![Docker]()
Usage
<p align="center">
<img src="./.github/img/usage.gif">
</p>
The following table lists switches supported by the amber.
<table border="1">
<tr>
<th>Switch</th>
<th>Type</th>
<th>Description</th>
</tr>
<tr>
<td><strong>-f,--file</strong></td>
<td><var>string</var></td>
<td>Input PE file.</td>
</tr>
<tr>
<td><strong>-o,--out</strong></td>
<td><var>string</var></td>
<td>Output binary payload file name.</td>
</tr>
<tr>
<td><strong>-e</strong></td>
<td><var>int</var></td>
<td>Number of times to encode the generated reflecti</td>
</tr>
<tr>
<td><strong>--iat</strong></td>
<td><var>bool</var></td>
<td>Use IAT API resol instead of CRC API resol</td>
</tr>
<tr>
<td><strong>-l</strong></td>
<td><var>int</var></td>
<td>Maximum number of bytes for obfuscation (default 5)</td>
</tr>
<tr>
<td><strong>--sys</strong></td>
<td><var>bool</var></td>
<td>Perform raw syscalls. (only x64)</td>
</tr>
<tr>
<td><strong>--scrape</strong></td>
<td><var>bool</var></td>
<td>Scrape magic byte and DOS stub from PE.</td>
</tr>
</table>
Example Usage
*Docker Usage*
Demo
项目信息
开发语言:Go
Star 数:1445
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Reflective PE packer.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | amber - Reflective PE packer. |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:13:03 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 354 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |