 黑客技术
点击放大
PackMyPayload - A PoC that packages payloads into output container
项目说明
PackMyPayload - Emerging Threat of Containerized Malware
Jump to supported formats
This 工具 takes a file or directory on input and embeds them into an output file acting as an archi.
It can ser for a Proof-of-Concept presenting emerging risk of container file formats with embedded malware, as well as helper for professional Red Team Operators to sharpen their Initial Access maneuvers.
Currently Threat Actors are known to smuggle their malware archived in container file formats, to name a few:
7zipzipISOIMGThey do that to get their payloads pass file content scanners, but more importantly to _avoid having Mark-Of-The-Web flag on their files_. There're motives on why ad don't want MOTW on their files: _Protected View_ in Microsoft Office was always among them.
Should they provide container file to their , a foundation for disabling in Internet-originated Office documents might be bypassed.
Background
On Feb, 7th Microsoft announced default configuration change to block originating from Internet. This is an incredible step towards hardening the baseline configuration of User's workstation and the 客户端 software installed within. Arguably o, yet an important step dramatically affecting in a positive way typical Windows+Office installation setups.
The implemented behavior is explained to work by differentating macro-enabled Office documents based on the MOTW (_Mark of the Web_) flag. That flag acts as a _tainted_ label a for software clients (browsers, mail clients, file archivers, etc) to mark files originating from untrusted areas like The Internet.
Outflank shed more light on MOTW, back in 2020 by indicating areas where MOTW flag is not uniformly propagated. These areas serve _defense gap_ role and are commonly abused by threat actors since years by now.
Their research disclosed, that some _container_ file formats - namely ISO, VHD/VHDX - do not propagate MOTW taint flag onto inner files upon auto-mount or auto-extraction. Moreover, Windows 8+ is able to open these formats automatically upon double-click, making them _notorius infection carriers, possibly de MOTW in its security measure role_.
Demo - How Threat Actors Evade MOTW and Smuggle Macros
Lets present how Mark of the Web flag looks like in practice:
1. Download a regular file using your Browser
!1.gif
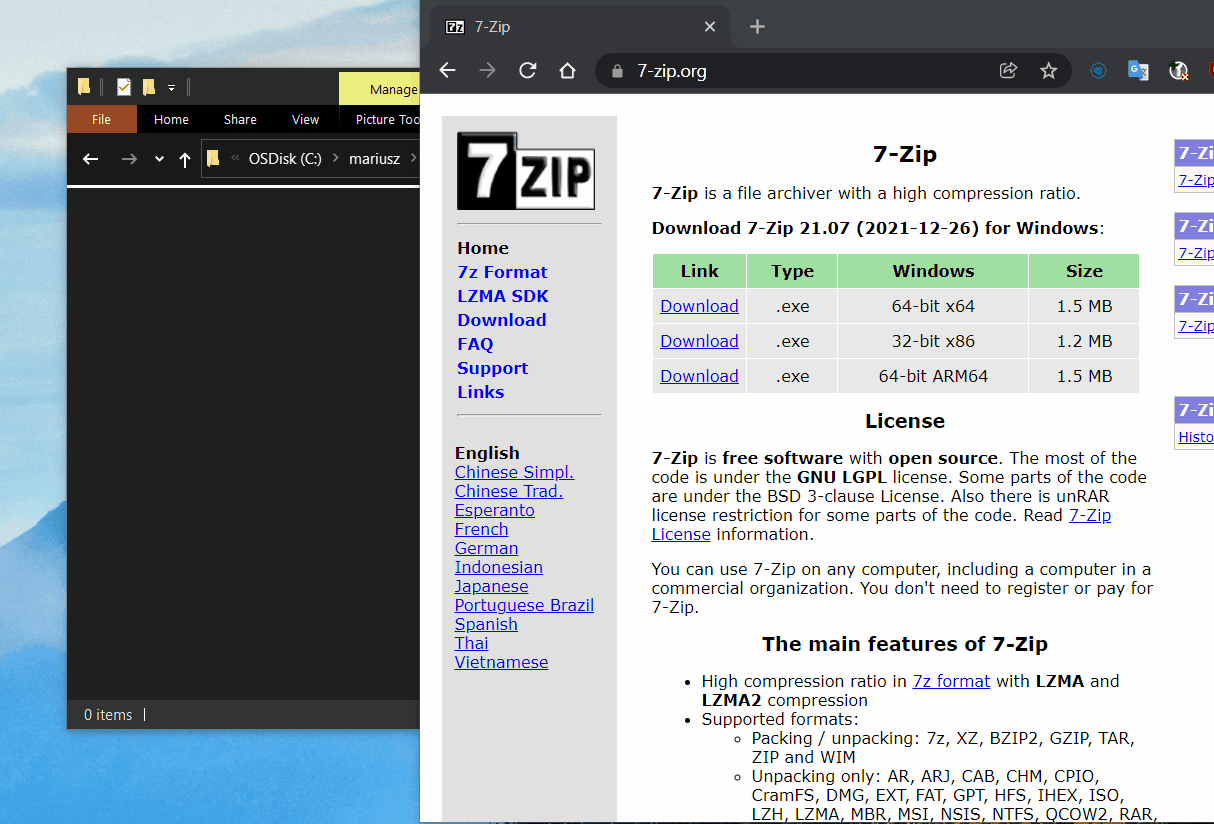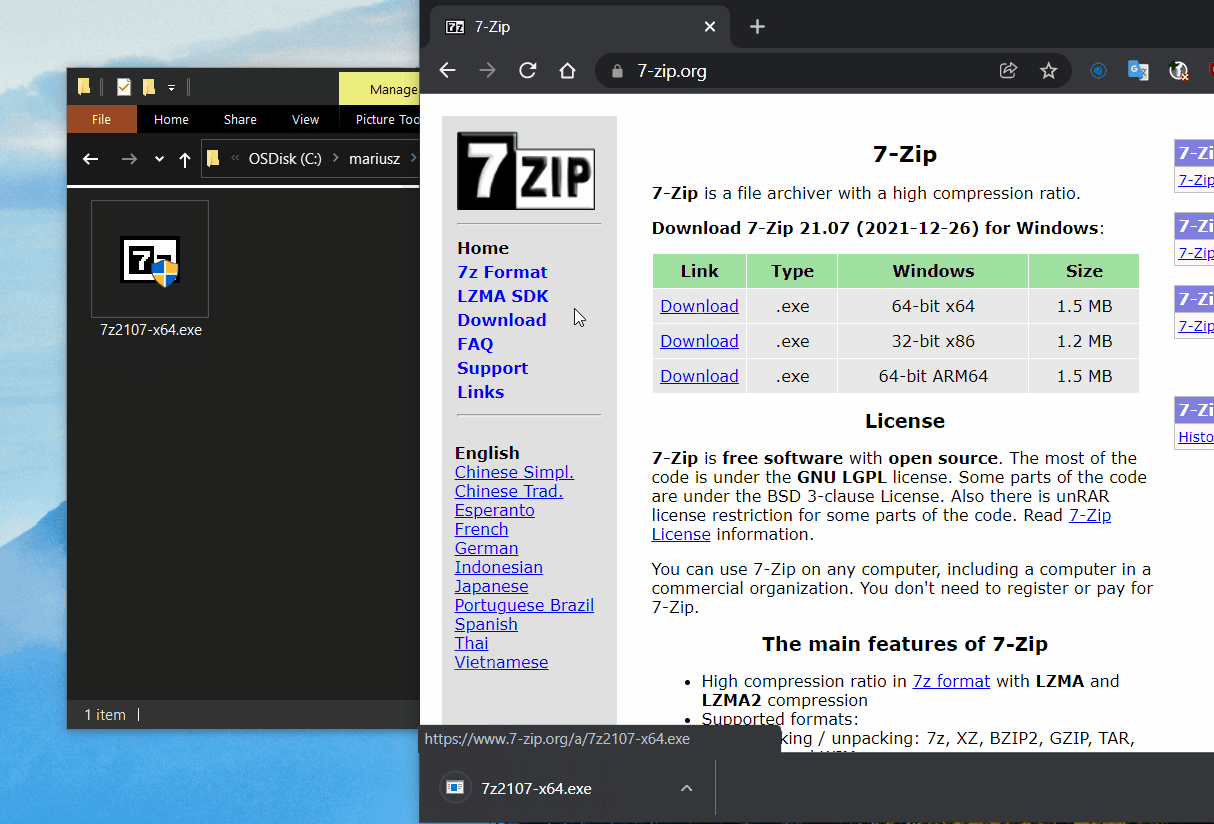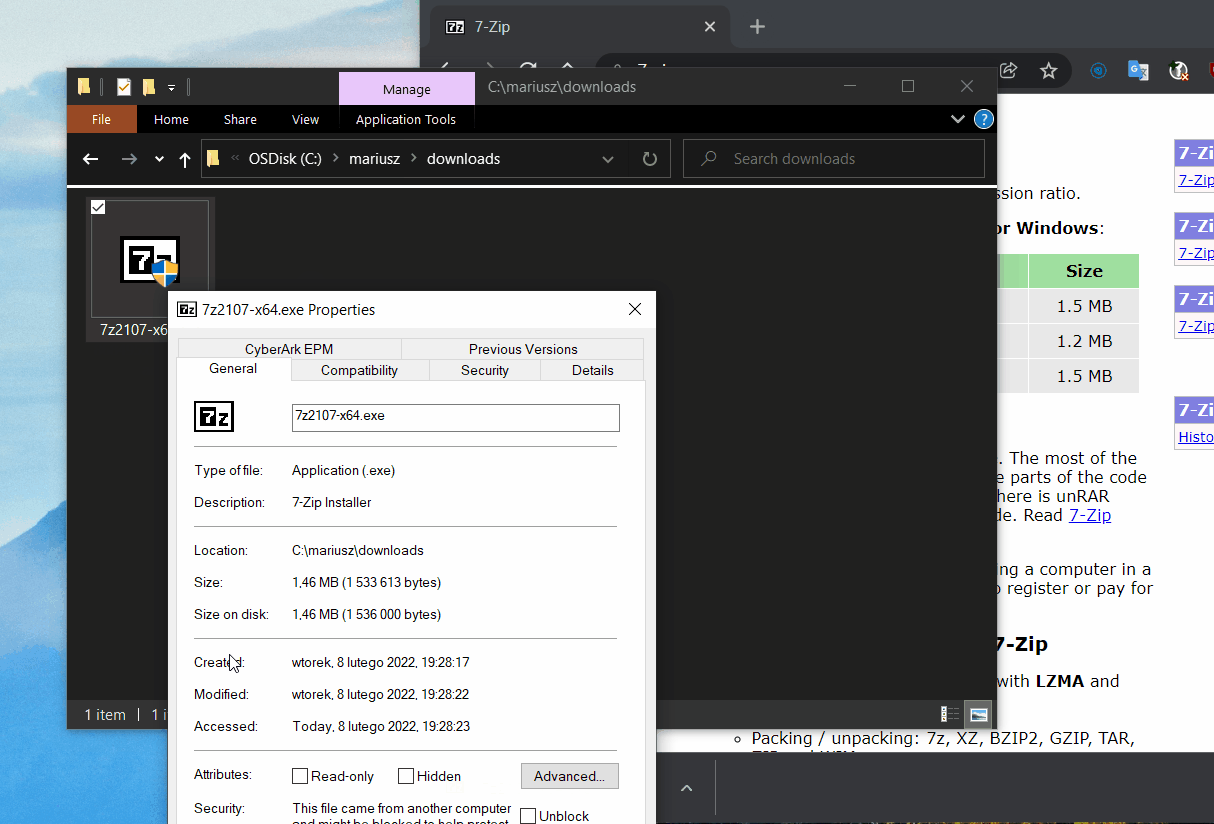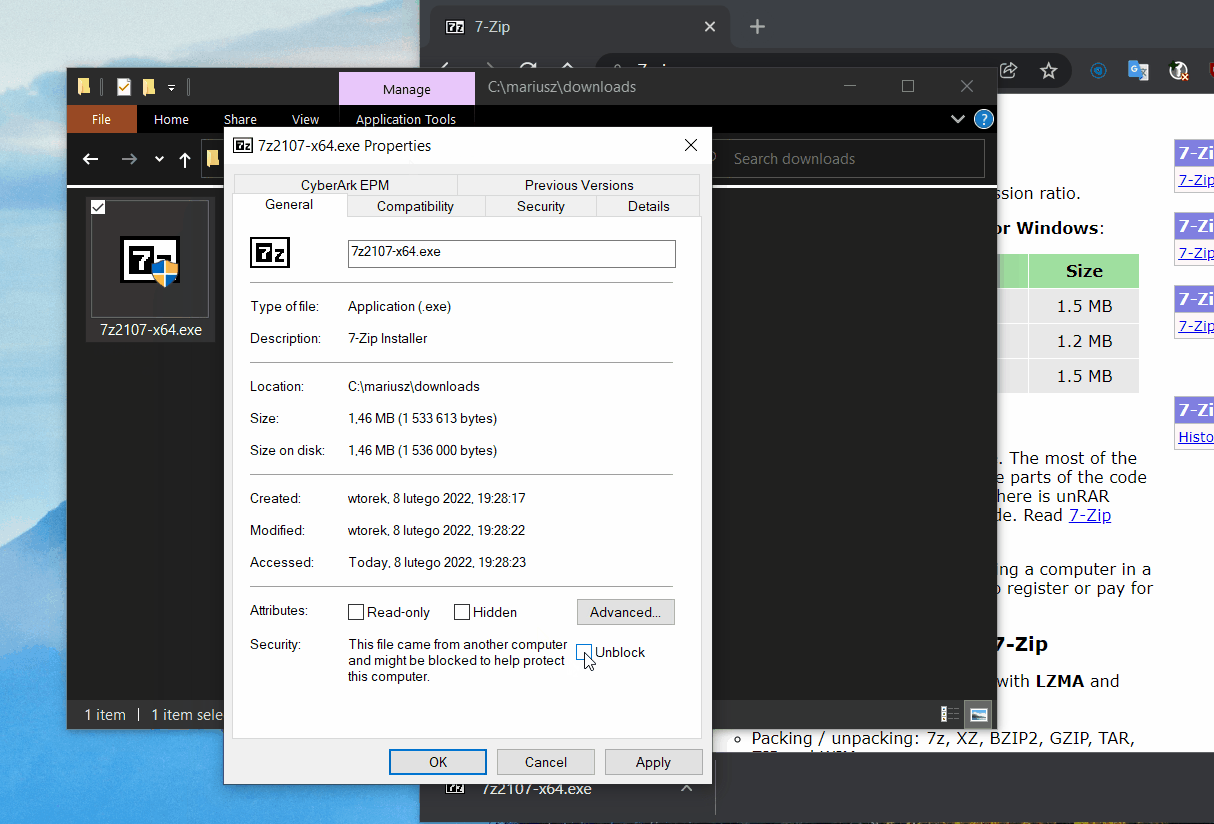
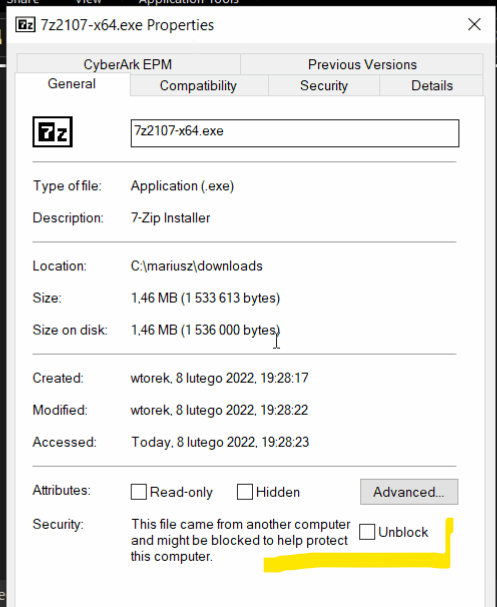
After downloading a file, right click on it and review its properties.
You'll see a message prompting to Unblock the file, because it originates from an untrusted zone.:
!motw
That information is stored in NTFS ADS (Alternate Data Stream) named Zone.Identifier which looks as follows:
!zone-identifier
The ZoneId=3 plays the role of marking file tainted.
2. Pack that file into ISO
Using PackMyPayload.py emplace the file into an ISO Joliet disk easily with a command:
!2.gif
3. Serve the file with Simple HTTP 服务端, download, open ISO, review MOTW
Having created ISO file, mimic a HTTP ser Python:
and then download the ISO file using your Browser.
!3.gif
When you review Properties of that ISO file, you'll see its marked with MOTW flag.
!marked
However, the inner 7zip installer EXE file is not MOTW-marked!
!not-marked
---
Rationale
Using the occassion that Industry's eyes are turned on Microsoft's bra to block , we, professional Security Researchers taking the utmost consideration on increasing World's technologies resielience against their misuse, want to add following insight into current Threat Actor TTPs:
Threat Actors are well aware of the impact MOTW has on their phishing payloads. They' long time ago and are now smuggling their malicious programs inside of containers. Among the most commonly observed ones we can highlight are ISO, IMG, CAB.
I am now releasing this 工具 to increase the momentum built on Microsoft's stand and to help intensify discussions on these e a.
It is advised to contain (and/or block) files having abo extensions whenever they originate from untrusted zones & where:
The 工具 released will hopefully enable more Red Teams to simulate discussed risks and help them identify detection gaps within their Partners defenses more easily.
---
Features
This script offers following treats & goodies:
Formats supported:
| Format | Strips MOTW? | Off the shelf Windows support? | Ele required? | Remarks |
|--------|--------------|--------------------------------|---------------------|-----------------------------------------------|
| Zip | No/Yes* | Yes | No | (MOTW stripped with C) |
| 7zip | Partially | No | No | MOTW stripped only on manual files extraction |
| ISO | Yes | Yes | No | |
| IMG | Yes | Yes | No | |
| PDF | ? | Yes | No | Depends on Ja support in PDF reader |
| CAB | No | Yes | No | Requires few additional clicks on |
| VHD | Yes | Yes | Yes | This script currently can't make directories |
| VHDX | Yes | Yes | Yes | This script currently can't make directories |
* In ZIP case, MOTW can be stripped when C is abused. PackMyPayload by default marks inner ZIP files as read-only unless --zip-noreadonly given.
Installation
Sample use
1. Pack a directory with files into ISO:
2. To pack files into VHD/VHDX one must run this script on Windows from an elevated user context (e.g. Local Administrator). This is due to DISKPART requiring Admin access to physical devices objects/namespace. Best experience one gets by running the script on Windows Terminal (wt) or ConEmu as they support ANSI colors. Otherwise, should an output look bad, disable those colors with -N flag:
---
Full usage
---
Known Issues
---
TODO
MSI filesword -> embeddings -> oleObject1.bin (OLE stream) + adjust -
tar-
cpio-
pax-
xar-
ar-
mtree-
shar-
tar-
cpgz-
uu-
lha-
B64, BHX, BZ, BZ2, GZ, HQX, LHA, LZH, MIM, TAZ, TBZ, -
TBZ2, TGZ, TXZ, TZ, UU, UUE, VMDK, XXE, XZ, Z, ZIPX, ---
Trivia
I kindly ask you to read following line out loud and as fast as you can in front of a mirror:
Some say the spell summons ancient DAEMON and Sheeps ( ͡~ ͜ʖ ͡°)
---
Contributors
Round of applause & thank you to the following contributors who helped enhance this 工具:
--hide flag for hiding file(s) in ISO/IMG containers--hide flag---
☕ Show Support ☕
This and other projects are outcome of sleepless nights and plenty of hard work. If you like what I do and appreciate that I always give back to the community,
Consider buying me a coffee _(or better a beer)_ just to say thank you! 💪
---
项目信息
开发语言:Python
Star 数:1225
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats. Supports: ZIP, 7zip, PDF, ISO, IMG, CAB, VHD, VHDX展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | PackMyPayload - A PoC that packages payloads into output container |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:13:42 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 207 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |