 黑客技术
点击放大
IPA - GUI analyzer for deep-diving into PDF files. Detec
项目说明
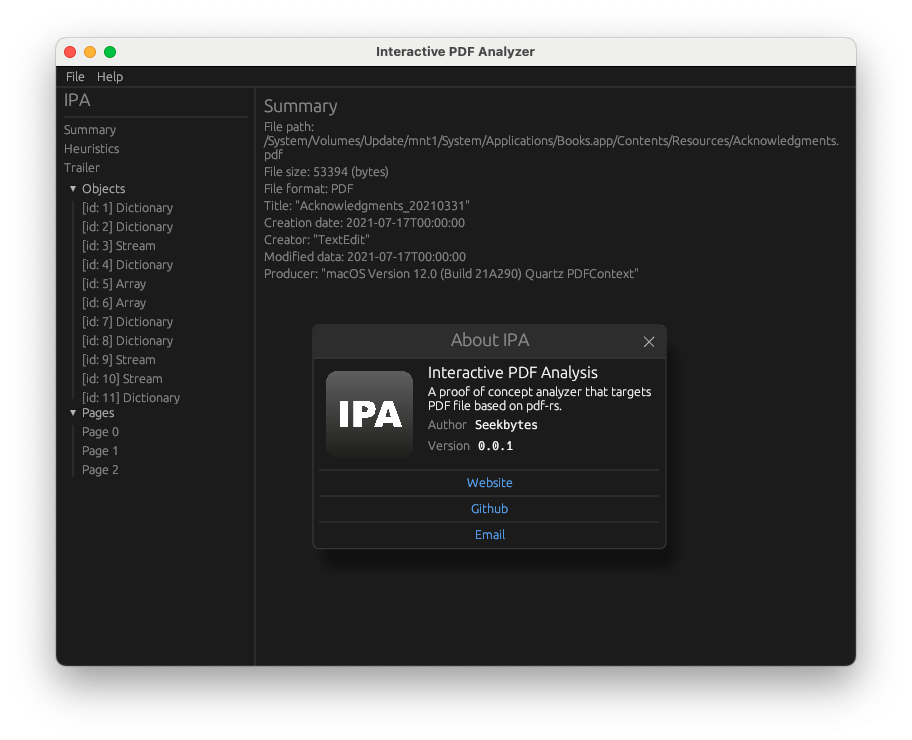
Interactive PDF Analysis
_Interactive PDF Analysis_ (also called IPA) allows any researcher to explore the inner details of any PDF file. PDF files may be used to carry malicious payloads that exploit , and issues of PDF , or may be used in phishing campaigns as social engineering artefacts.
The goal of this software is to let any analyst go deep on its own the PDF file. Via IPA, you may extract important payload from PDF files, understand the relationship across objects, and infer elements that may be helpful for triage of malicious or untrusted payloads.
The main inspiration goes to the fantastic people behind Zynamics, and their excellent product, called PDF dissector.
<p align="center">
<img alt="Main window of IPA" src="data/screenshot.png" width="600">
</p>
Simplifying analysis of PDF files
When I started reverse engineering malware, the main 工具 a for analysing malicious payloads consisted of Didier Stevens's excellent tools. Having become a _de facto_ standard, one of the main problems with these tools was the fact that they could be used from the command line, having to remember a very large combination of flags, reporting the numbers of the objects. Although analysis and de have to contend with all kinds of command-line tools on a daily basis, this does not mean that we cannot create a new graphical file inspection 工具.
In fact, part of static analysis and reverse engineering fields also focuse on how to display the most salient information to the analyst from the point of view of user experience. Didier Stevens' tools, as well as peepdf, are already used and well broken in. However, the analyst could use something graphical in order to be able to understand the relationship between the objects, to understand which pages they refer to and which object types (images, fonts, colours, metadata), to export stream content in a simple way and to see the content of dictionaries in table form.
The main 源码 of inspiration comes from the 工具 de by Zynamics called PDF-dissector: the excellent feedback from some former users and the constant requests to release it open 源码 spurred me to spend a few days creating this 工具.
Features
* Extract and analyze metadata to identify the creator, creation date, modification history, and other essential details about the PDF file.
* Examine the structure of the PDF document by analyzing its objects (such as text, images, and fonts) and pages to understand their relationships, content, and layout.
* References that point to other objects or locations within the file, such as images, fonts, or specific sections.
* Extract and save raw data streams from the PDF file to a specified location, allowing for detailed examination and analysis of the underlying binary content.
* Implement a lighter analysis that attempts to salvage usable information from a corrupted or partially damaged PDF file, even when traditional parsing methods fail.
* Does not require any additional software, libraries, or external services to function thanks to pdf-rs and Rust compatibility.
Installation
The 工具 can be compiled with Rust and cargo. No dependencies are required apart from Rust, and the crates pulled.
Credits
* pdf-rs team for their awesome library (if you have any issues parsing a PDF file, you might want to open an issue for them)
* Zynamics for the inspiration of pdf dissector
* egui for a solid immediate GUI mode
Limitations
IPA has the following limitations for now:
At the end, the 工具 can be really improved and I pretty bet some people will notice how bad my 代码 is. If you're one of these, please let me know about potential impro, better patterns, and any suggestion.
Contact
If you have any issues, impro, or you just want to text me, email .
项目信息
开发语言:Rust
Star 数:882
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕界面 analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat analysis.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | IPA - GUI analyzer for deep-diving into PDF files. Detec |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:14:11 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 508 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |