 黑客技术
点击放大
sickle-pdk - Sickle - Payload Development Kit
项目说明
Sickle - Payload De Kit
!alt text
Sickle is a 工具 I originally de to help me be more effective, in both de and understanding shellcode. However, throughout the course of its de and usage It has e into a payload de kit. Although current modules are mostly aimed towards assembly, this 工具 is not limited to shellcode.
Currently sickle can assist in the following.
Shellcode Generation
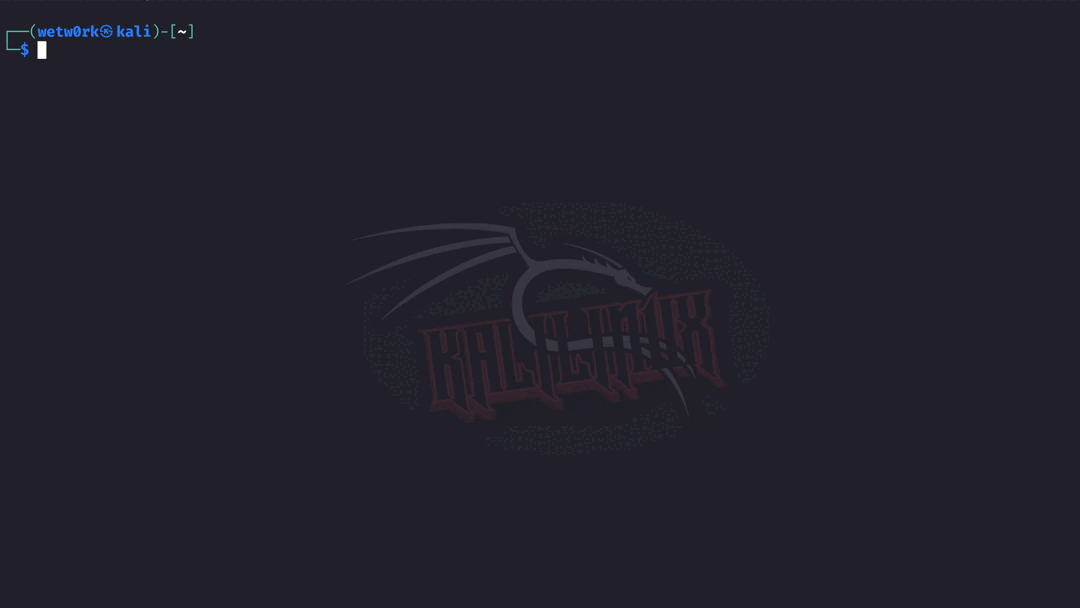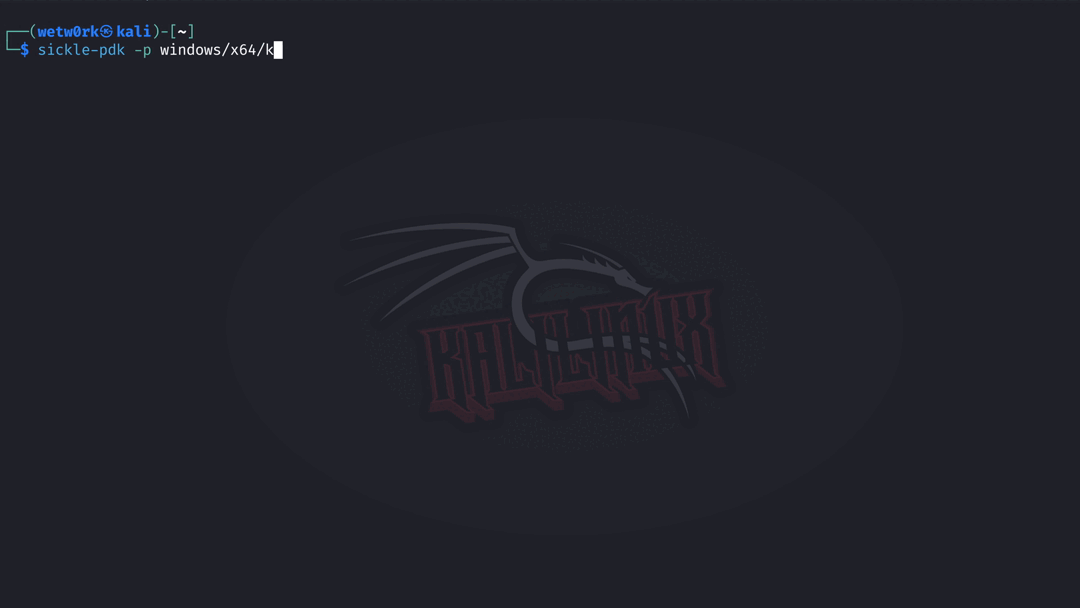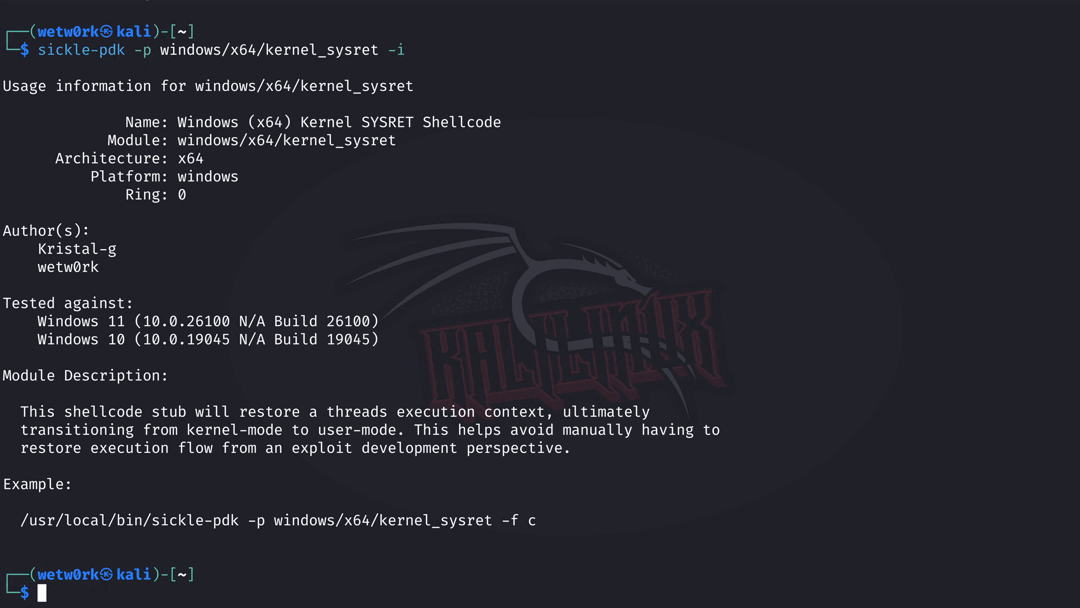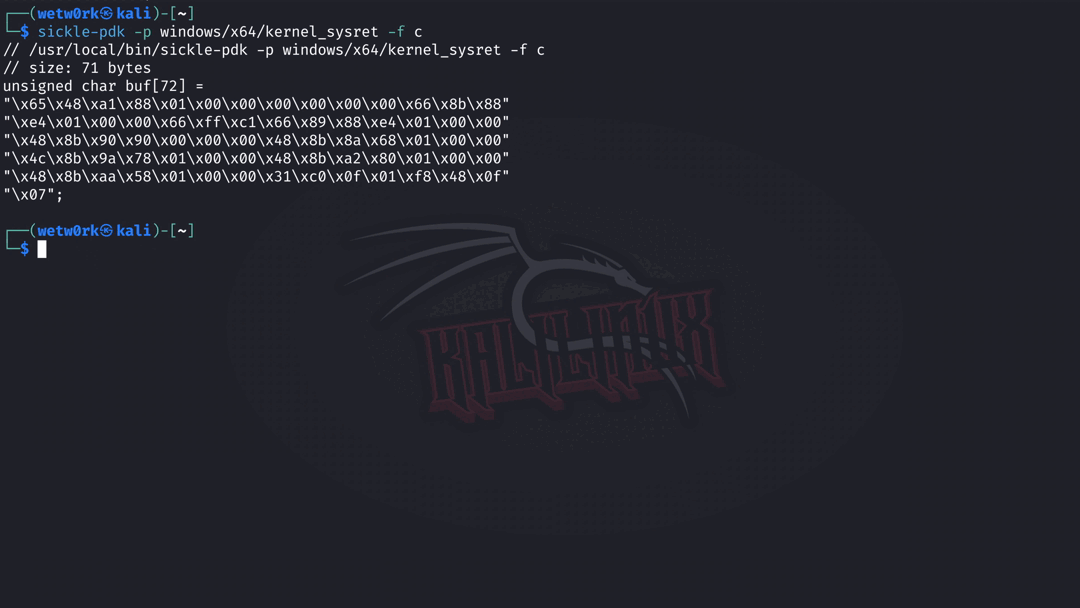
Sickle supports shellcode generation via the Keystone 引擎. Due to this being a newly added feature, payload support is limited. However, the goal is to add a basic reverse shell for each architecture and platform.
!alt text
Diffing
Sickle includes a "diffing" module initially designed for analyzing shellcode stubs. The original "asm" mode performs linear disassembly diffs at both the assembly language and opcode levels separately.
!alt text
In addition, Sickle offers modes for performing diffs, making it useful beyond shellcode de.
!alt text
Shellcode Execution
One common task you may often perform is testing your shellcode. This process typically in the following steps:
1. Compile the assembly language code.
2. Extract the shellcode and format it appropriately for your chosen wrapper.
3. Compile the wrapper.
4. Execute the wrapper.
Although these steps may seem minor, they can become time-consuming when done repeatedly. Sickle simplifies the process by automatically wrapping shellcode for quick testing, and the "run" module currently supports both Windows and Unix systems.
!alt text
Disassembly
Sickle can also convert a binary file into extracted opcodes (shellcode) and then translate those into machine instructions (assembly). Note that this process only works with raw binary files and currently performs disassembly in a linear fashion .
!alt text
In the example shown above the "disassemble" module disassembles a reverse shell designed by Stephen Fewer to assembly.
Shellcode Extraction
Shellcode extraction was the first module, or rather, the core functionality for Sickle, as opcodes are interpreted differently depending on the wrapper used. Ja, for example, does not store and interpret shellcode in the same way as a C program would.
!alt text
Perhaps the biggest inspiration for this was msfvenom.
Bad Character Identification
Although less common in 64-bit exploits, there may be instances where an exploit restricts the use of certain characters. This is where the "pinpoint" module excels, as it directly identifies and highlights the assembly instructions responsible for the identified bad character(s).
!alt text
Module Based Design
Originally, this 工具 started as a single large script. However, as it e, I found myself needing to re-learn the 代码 with each update. To address this, Sickle now follows a modular approach, allowing for new functionality to be added with minimal time spent re-learning the 工具’s design.
This approach allows each module the ability to generate detailed documentation for its functionality.
This approach also includes documentation for shellcode stubs.
项目信息
开发语言:Python
Star 数:870
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Sickle - Payload De Kit展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | sickle-pdk - Sickle - Payload Development Kit |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:14:16 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 144 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |