剑庭安
首页
黑客安全首页全部安全栏目 黑客技术黑客技术、渗透测试、漏洞利用工具与教程 安全软件安全工具、扫描器、检测与审计软件 病毒分析恶意软件分析、样本、逆向与沙箱 CTF思路CTF 题目、writeup、解题思路与工具 防护思路防御技术、加固、检测响应与蓝队 红蓝攻防红队攻击模拟、蓝队对抗、攻防演练 漏洞知识库漏洞、CVE、PoC、EXP 与安全研究
逆向|反编译
PHP源码PHP 网站源码、程序、系统 APP源码安卓/iOS APP 源码 ASP源码ASP 网站源码与程序 NET源码.NET 网站源码与系统 小程序源码微信/支付宝小程序源码 Dedecms风格模板Dedecms 织梦风格模板 Empirecms风格模板EmpireCMS 帝国风格模板 Discuz商业模板/插件Discuz 商业模板与插件 WordPress主题/插件WordPress 主题与插件 其它源码、模板其它各类源码与模板 游戏源码游戏源码与引擎项目 加密货币源码加密货币、区块链、钱包、USDT/比特币相关源码与工具 手游源码手机游戏源码、服务端、客户端与引擎项目 传奇源码热血传奇、传奇世界、复古传奇等客户端/服务端/引擎源码 页游源码网页游戏、H5 游戏、浏览器游戏源码 端游源码电脑单机游戏、PC 网游客户端/服务端源码
最新万能免驱动支持所有型号打印机下载程序 日历天气老黄历 · 每天同步真实日期与天气
站长工具站长工具 自助开通会员浏览该分类 其他资源qtziy SEO工具SEO工具 站群源码站群源码 泛程序泛程序 蜘蛛模板蜘蛛模板 蜘蛛池蜘蛛池 外链工具外链工具
搜索 自助开通会员🔓 破甲 API
登录 注册
首页 分类列表 黑客技术 EvilOSX - An evil RAT (Remot…
EvilOSX - An evil RAT (Remote Administration Tool) for macOS 黑客技术 点击放大
作者:admin 发布:2026-10-05

EvilOSX - An evil RAT (Remote Administration Tool) for macOS

项目说明<h1 align="center"> <br> <a href=" src="/data/images/logo.png?raw=true" alt="Logo" width="2…
资源可下载 免费下载 0 条讨论
会员资源
开通会员后即可下载全部资源。
登录后开通会员
会员方案
504浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-05
人工审核发布
评论区答疑

E - An evil RAT (Remote Administration Tool) for macOS

E - An evil RAT (Remote Administration Tool) for macOS

项目说明

<h1 align="center">
<br>
<a href=" src="/data/images/logo.png?raw=true" alt="Logo" width="280"></a>
<br>
E
<br>
</h1>

<h4 align="center">An evil RAT (Remote Administration 工具) for macOS / OS X.</h4>

<p align="center">
<a href="
<img src=" alt="License">
</a>
<a href="
<img src=" alt="Python">
</a>
<a href="
<img src=" alt="Issues">
</a>
<a href="
<img src=" alt="Build Status">
</a>
<a href="
<img src=" alt="Contributing">
</a>
</p>

---

Marco Generator by Cedric Owens

This project is no longer active

Features


  • Emulate a terminal instance

  • Simple extendable module system

  • No bot dependencies (pure python)

  • Undetected by anti-virus (OpenSSL AES-256 encrypted payloads)

  • Persistent

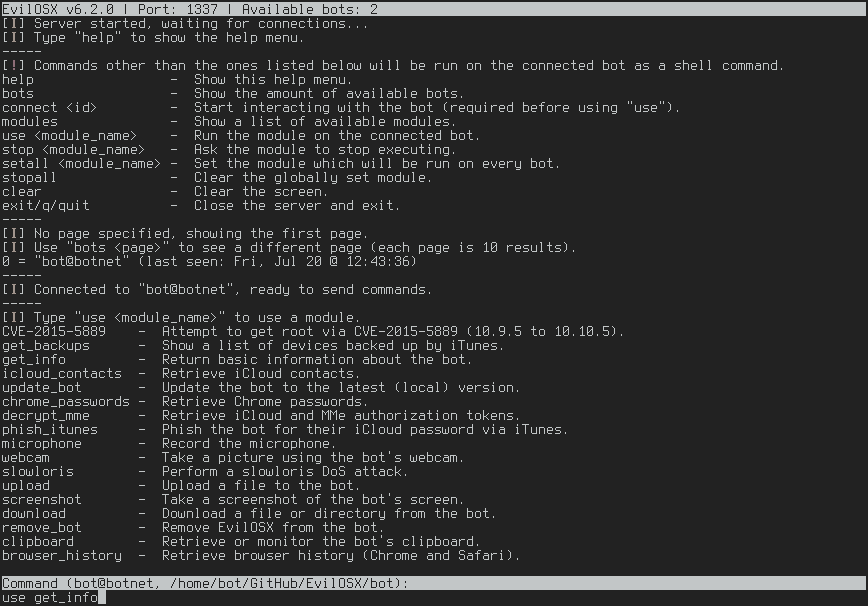
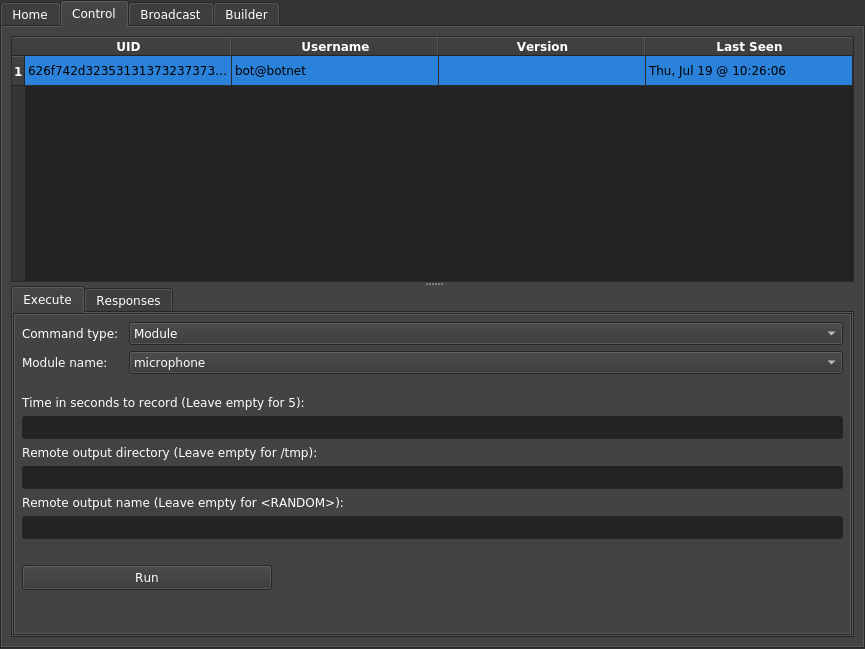
  • GUI and CLI support

  • Retrie passwords

  • Retrie tokens and contacts

  • Retrie the clipboard

  • Retrie history (Chrome and Safari)

  • Phish for iCloud passwords

  • iTunes (iOS) backup enumeration

  • Record the microphone

  • Take a desktop screenshot or picture using the webcam

  • Attempt to get root pri escalation
  • How To Use

    Warning: Because payloads are created unique to the target system (automatically by the 服务端), the 服务端 must be running when any bot connects for the first time.

    Ad users

    There's also a CLI for those who want to use this over SSH:

    Screenshots

    !CLI
    !GUI

    Moti


    This project was created to be used with my Rubber Ducky, here's the simple script:

  • It takes about 10 seconds to backdoor any unlocked Mac, which is...... *nice*

  • Terminal is spelt that way intentionally, on some systems spotlight won't find the terminal otherwise. <br/>

  • To bypass the keyboard setup assistant make sure you change the VID&PID which can be found here. <br/>

  • Aluminum Keyboard (ISO) is probably the one you are looking for.


    E will be maintained under the Semantic guidelines as much as possible. <br/>
    服务端 and bot releases will be numbered with the follow format:

    And constructed with the following guidelines:

  • Breaking backward compatibility (with older bots) bumps the major

  • New additions without breaking backward compatibility bumps the minor

  • Bug fixes and misc changes bump the patch
  • For more information on SemVer, please visit

    Design Notes


  • Infecting a machine is split up into three parts:

  • * A launcher is run on the target machine whose only goal is to run the stager
    * The stager asks the server for a loader which handles how a payload will be loaded
    * The loader is given a uniquely encrypted payload and then sent back to the stager
  • The ser it's communications by sending messages hidden in HTTP 404 error pages (from BlackHat's "Hiding In Plain Sight")

  • * Command requests are retrieved from the 服务端 via a GET request
    * Command responses are sent to the 服务端 via a POST request
  • Modules take ad of python's dynamic nature, they are simply sent over the 网络 compressed with zlib, along with any configuration options

  • Since the bot only communicates with the 服务端 and never the other way around, the 服务端 has no way of knowing when a bot goes offline
  • Issues


    Feel free to submit any issues or feature requests here.

    Contributing


    For a simple guide on how to create modules click here.

    Credits


  • The awesome Empire project

  • Shoutout to Patrick Wardle for his awesome talks, check out Objecti

  • manwhoami for his projects: OSXChromeDecrypt, MMeTokenDecrypt, iCloudContacts <br/>

  • (now deleted... let me know if you reappear)
  • The slowloris module is pretty much copied from PySlowLoris

  • urwid and this 代码 which saved me a lot of time with the CLI

  • Logo created by motusora
  • License


    GPLv3

    项目信息

    开发语言:Python

    Star 数:2421

    技术要点

    该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An evil RAT (Remote Administration 工具) for macOS / OS X.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。

    从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。

    使用与学习建议

    1. 下载源码压缩包,解压到本地环境。

    2. 根据项目类型准备对应的运行环境与依赖。

    3. 按照 README 中的步骤完成配置与部署。

    4. 在隔离的测试环境中运行验证,避免影响生产系统。

    免责声明

    本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。

    资源标题EvilOSX - An evil RAT (Remote Administration Tool) for macOS
    所属分类黑客技术
    发布作者admin
    发布时间2026-10-05 22:14:36
    下载权限 免费下载
    附件数量2 个下载链接
    浏览次数504
    讨论数量0
    主题状态正常讨论中

    本资源免费,登录后即可在本页「下载链接」区域获取全部附件。

    请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。

    请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
    还没有讨论,快来抢沙发~
    登录 后才能参与讨论
    下载链接
    会员才能下载
    登录后开通会员
    同分类推荐
    暂无同类资源
    免费登录即可下载
    查看会员
    放大预览

    © 2026 剑庭安 - 网站开发定制 SEO 优化蜘蛛池代做 在线看手相算命. 保留所有权利。

    Powered by 酷像SEOv3.0

    网站地图 Sitemap.xml
    首页 全部分类 黑客安全 逆向|反编译 精品源码 站长工具自助开通会员其他资源SEO工具站群源码泛程序蜘蛛模板蜘蛛池外链工具创意乐园 搜索 会员服务 登录 注册