 黑客技术
点击放大
boopkit - Linux eBPF backdoor over TCP. Spawn reverse shells
项目说明
Linux backdoor, rootkit, and eBPF bypass tools.
Remote command execution over raw TCP.
- Tested on Linux kernel 5.16
- Tested on Linux kernel 5.17
- Remote 代码 execution over TCP (SSH, Nginx, Kubernetes, etc)
- 网络 gateway bypass (bad checksums, TCP reset)
- Self obfuscation at runtime (eBPF process hiding)
##### Disclaimer
> This is NOT an exploit! This requires prior pri access on a 服务端 in order to work!
> I am a professional security researcher. These are white hat tools used for research purposes only.
> Use this responsibly. Never use this software illegally.
!FSpgEXTacAYme8t
Server Side
Download and build boopkit.
Run boopkit in the foreground.
Run boopkit in the background in quiet mode.
Boopkit is now running and can be exploited using the 客户端 boopkit-boop command line tool.
Client Side
Download and build boopkit.
Run boopkit-boop against the server.
Boop
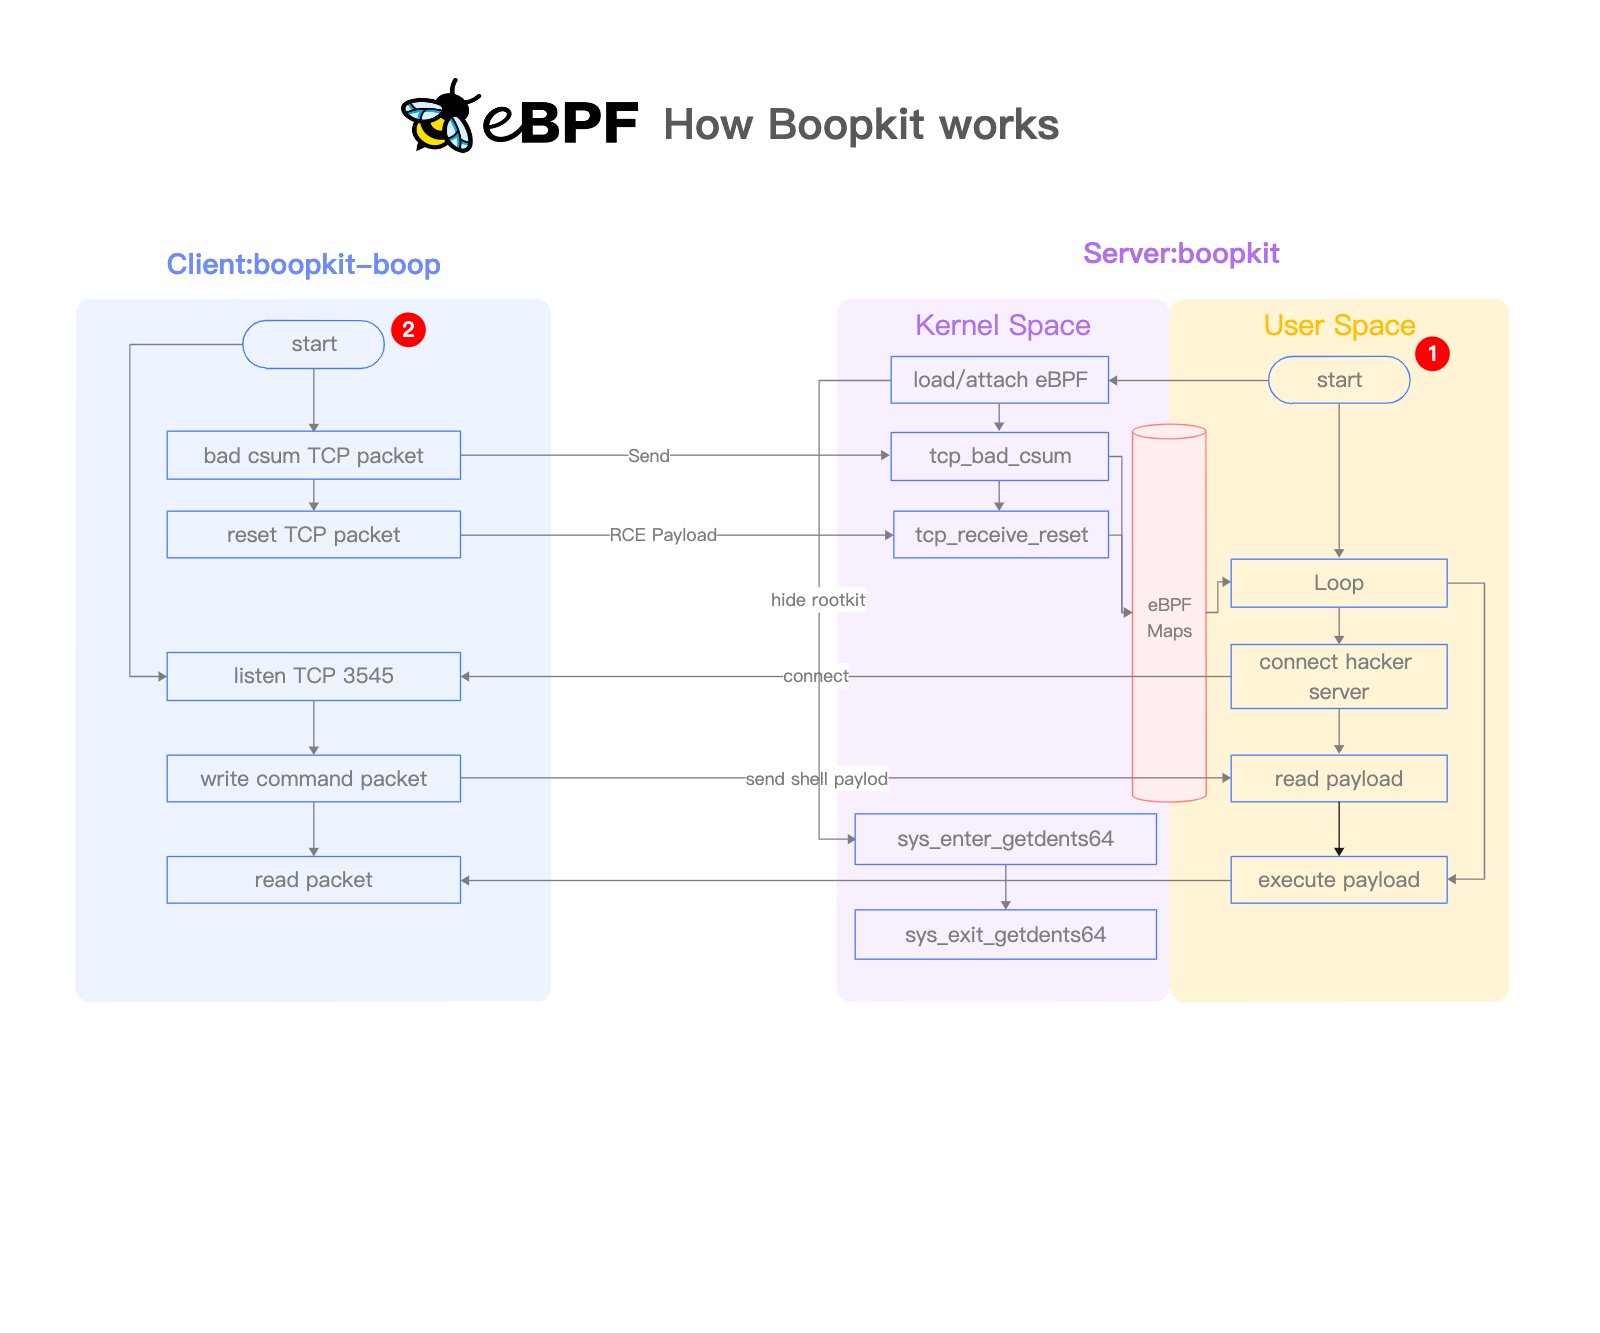
Boopkit will respond to events on the 网络. Both of which can be triggered with the boopkit-boop tool.
TCP Header Format. Taken from RFC 793. September 1981
1. Bad Checksum
First the boopkit-boop 工具 will send a malformed TCP SYN packet with an empty checksum to the 服务端 over a SOCK_RAW socket. This will trigger boopkit remotely regardless of what TCP services are running. This works against any Linux ser boopkit, regardless of the state of TCP services.
Use -p with boopkit-boop to only use this first .
⚠️ Some modern 网络 hardware will DROP all malformed checksum packets such as the one required to exploit boopkit using this !
2. Sending ACK-RST packet
Next the boopkit-boop 工具 will complete a valid TCP handshake with a SOCK_STREAM socket against a remote TCP service such as SSH, Kubernetes, Nginx, etc. After the initial TCP handshake is complete, boopkit-boop will repeat the process a 2nd time.
The 2nd handshake will flip the TCP reset flag in the packet, trigger a TCP reset on the 服务端.
Either of these tactics are enough to independently trigger boopkit.
网络 hardware and runtime conditions will make either tactic more .
Boopkit will try both, and respond to both by default.
Boopscript
The boopscript file is a Metasploit compatible script that can be used to remotely trigger the boopkit backdoor after boopkit-boop is installed on a remote Linux machine.
Compile Time Dependencies
- 'clang'
- 'bpftool' Required for libbpf
- 'xdp-tools' Required for libxdp
- 'llvm'
- 'pcap'
- 'lib32-glibc'
Reverse Shell Stabilization
References
- Tracepoints with BPF
- Raw TCP Sockets
- Bad BPF
Credit to the original authors for their helpful 代码 samples! I forked a lot of 代码 for this project!
项目信息
开发语言:C
Star 数:1681
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior pri access. Less Honkin, More Tonkin.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | boopkit - Linux eBPF backdoor over TCP. Spawn reverse shells |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:15:05 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 219 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |