 黑客技术
点击放大
ghost - :ghost: RAT (Remote Access Trojan) - Silent Botnet
项目说明
ghost
<p align="center">
<img src=" />
</p>
---
ghost is a light RAT that gives the ser full remote access to the user's command-line interpreter (cmd.exe).
They are allowed to execute commands silently without the 客户端/zombie noticing. The ser is also given the ability to download and execute files on the 客户端/zombie's computer. This is also
a silent and hidden process. Like most Remote Access Trojans, this download and execution ability helps distribute and other pieces of malware.
This malware is distributed simply by running *zombie.exe*. This file name can be changed to whatever. There is no restriction. When run, it searches for the first two arguments (IP & Port). If neither
is provided, the program doesn't run. With that being said, make sure you provide the 服务端's IP and Port in the command-line arguments. Example:
#### Bot Features
---
When successfully started, it adds itself to the start-up pool and runs silently in the background. It will try to repeatedly connect to the 服务端. This process does not hog any memory or CPU usage.
This means that the zombie will silently just idle in the background and whenever the 服务端 is up, it will automatically connect.
<p align="center">
<img src=" />
</p>
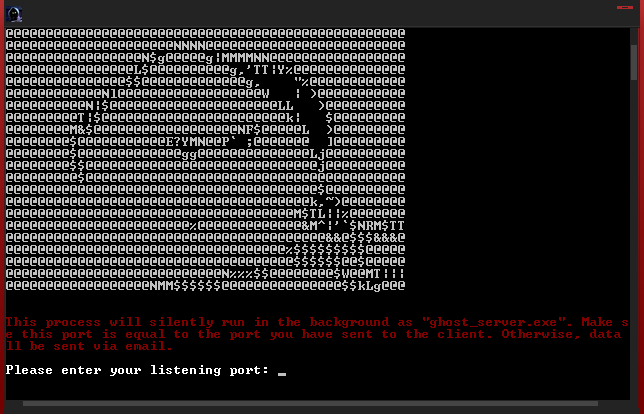
When starting the 服务端, it will prompt for you a listening port. This is the port that you need to use in the command-line for zombie.exe. Once you provide the port, your ser will be
provided and the menu will be down. The IP address provided is your external IP. With that being said, unless the 客户端/zombie is actively looking and tracking open connections, it will probably be
smart to run this ser a remote location if you want to stay anonymous. If this does not interest you, simply renaming zombie.exe and/or changing the assembly information using a 工具 will
likely fool the client/zombie.
Note: This project was only made for education purposes and to test out my recently published repositories (ahxrlogger & ahxrsocket). If you choose to use this for malicious reasons, you are completely responsible for the outcome.
项目信息
开发语言:C++
Star 数:1071
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕:ghost: RAT (Remote Access Trojan) - Silent Botnet - Full Remote Command-Line Access - Download & Execute Programs - Spread Virus' & Malware展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ghost - :ghost: RAT (Remote Access Trojan) - Silent Botnet |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:15:40 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 302 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |