 黑客技术
点击放大
Sandman - Sandman is a NTP based backdoor for hardened netwo
项目说明
Sandman
!Image !image !image
Sandman is a backdoor that is meant to work on hardened networks during red team engagements.
Sandman works as a stager and le NTP (a 协议 to sync time & date) to get and run an arbitrary shellcode from a pre-defined server.
Since NTP is a 协议 that is o by many defenders resulting in wide 网络 accessibility.
Usage
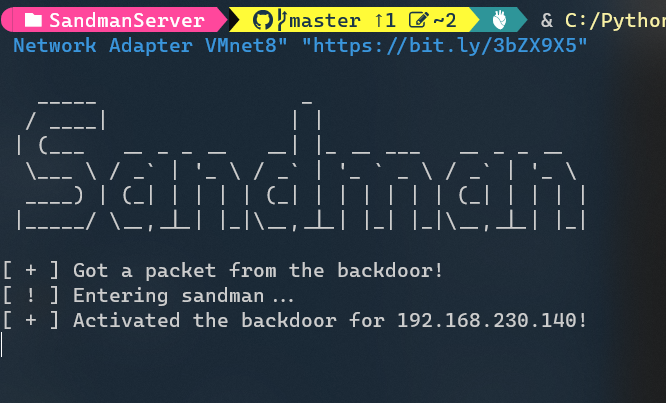
!Sandman
SandmanServer (Usage)
Run on windows / *nix machine:
SandmanBackdoor (Usage)
To start, you can compile the SandmanBackdoor as mentioned below, because it is a single lightweight C# executable you can execute it , run it as an NTP provider or just execute/inject it.
SandmanBackdoorTimeProvider (Usage)
To use it, you will need to follow simple steps:
NOTE: Make sure you are compiling with the x64 option and not any CPU option!
Capabilities
Setup
SandmanServer (Setup)
SandmanBackdoor (Setup)
To compile the backdoor I used Studio 2022, but as mentioned in the usage section it can be compiled with both and CSC.
You can compile it either using the USE_SHELLCODE and use Orca's shellcode or without USE_SHELLCODE to use WebClient.
SandmanBackdoorTimeProvider (Setup)
To compile the backdoor I used Studio 2022, you will also need to install DllExport ( or any other way) to compile it.
You can compile it either using the USE_SHELLCODE and use Orca's shellcode or without USE_SHELLCODE to use WebClient.
IOCs
Contributes
Thanks to those who already contributed and I'll happily accept contributions, make a pull request and I will review it!
项目信息
开发语言:C#
Star 数:818
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Sandman is a NTP based backdoor for hardened networks.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Sandman - Sandman is a NTP based backdoor for hardened netwo |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:16:00 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 100 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |