 黑客技术
点击放大
backdoorme - powerful auto-backdooring utility
项目说明
backdoorme ![Build Status]()
Tools like metasploit are great for exploiting computers, but what happens after you' access to a computer? Backdoorme answers that question by unleashing a slew of backdoors to establish persistence over long periods of time.
Once an SSH connection has been established with the target, Backdoorme's strengths can come to fruition. Unfortunately, Backdoorme is not a 工具 to gain root access - only keep that access once it has been gained.
Please only use Backdoorme with explicit permission - please don't hack without asking.
Usage
Backdoorme is split into two parts: backdoors and modules.
Backdoors are small snippets of 代码 which listen on a port and redirect to an interpreter, like bash. There are many backdoors written in languages to gi.
Modules make the backdoors more potent by running them more often, for example, every few minutes or whenever the computer boots. This helps to establish persistence.
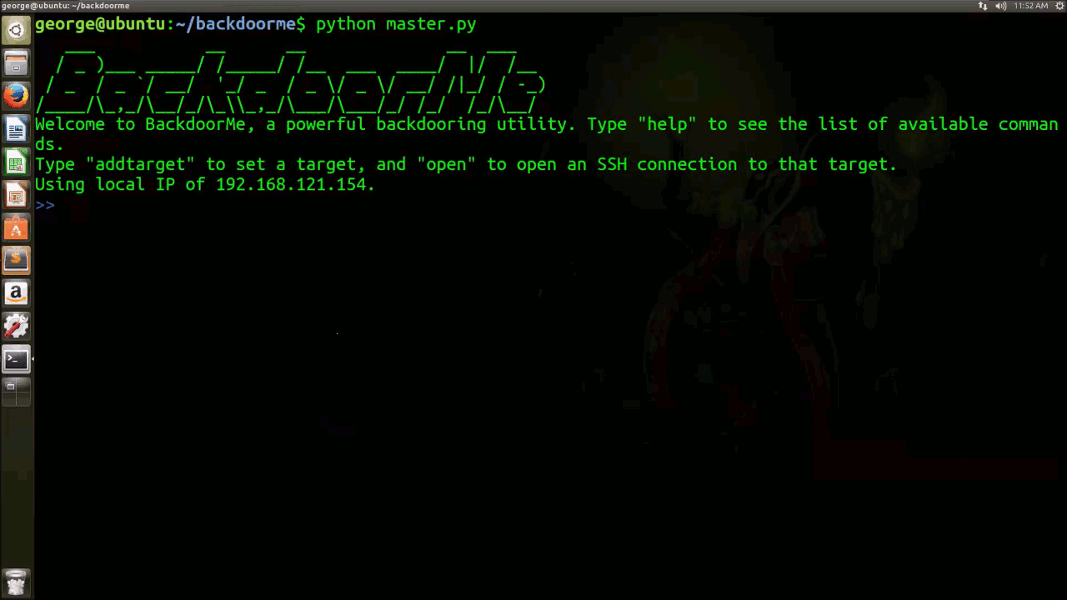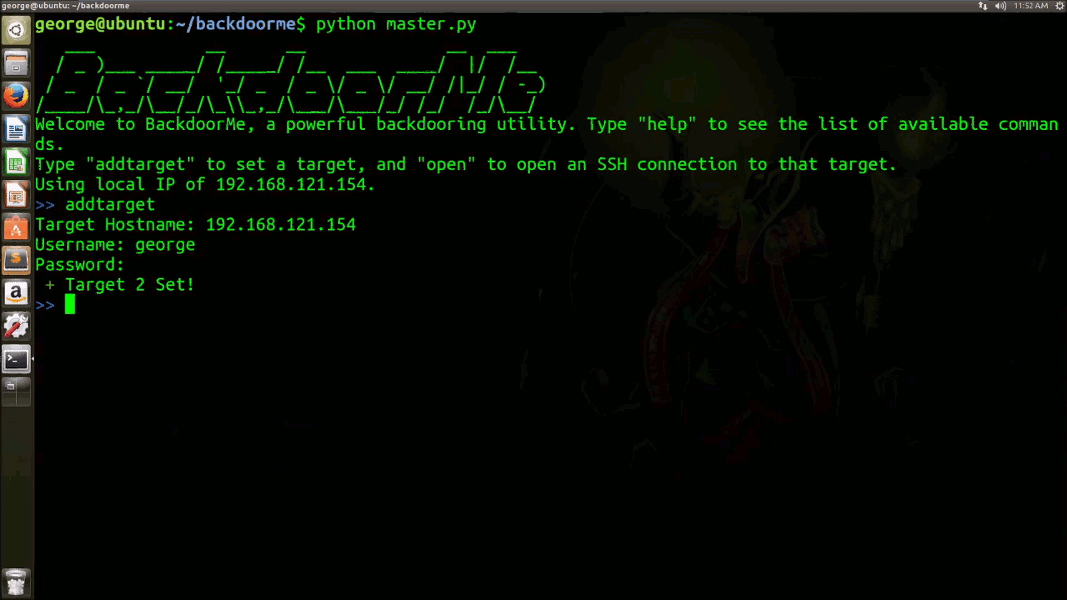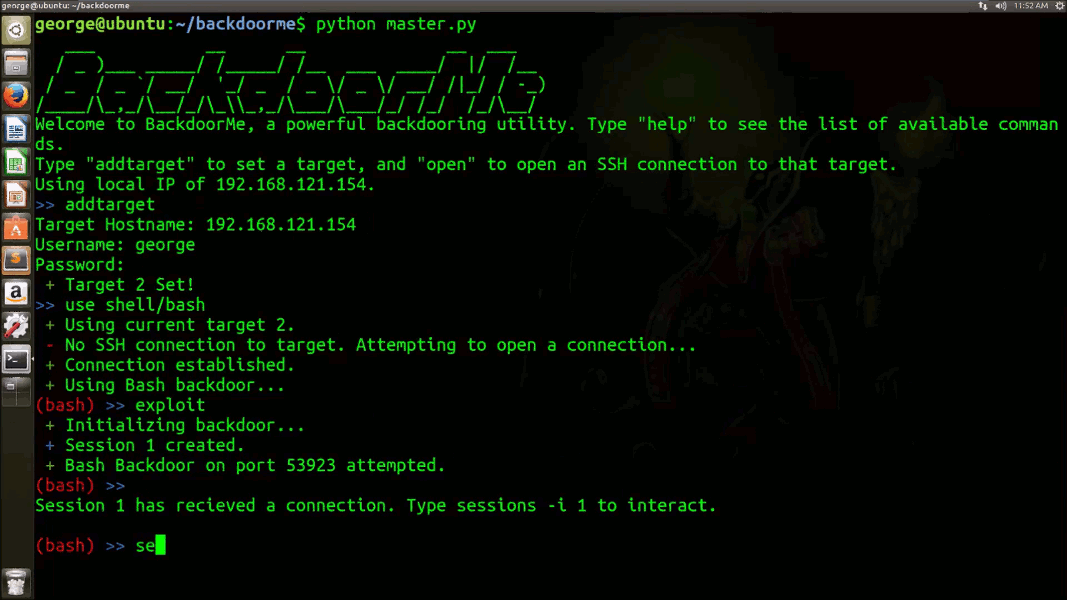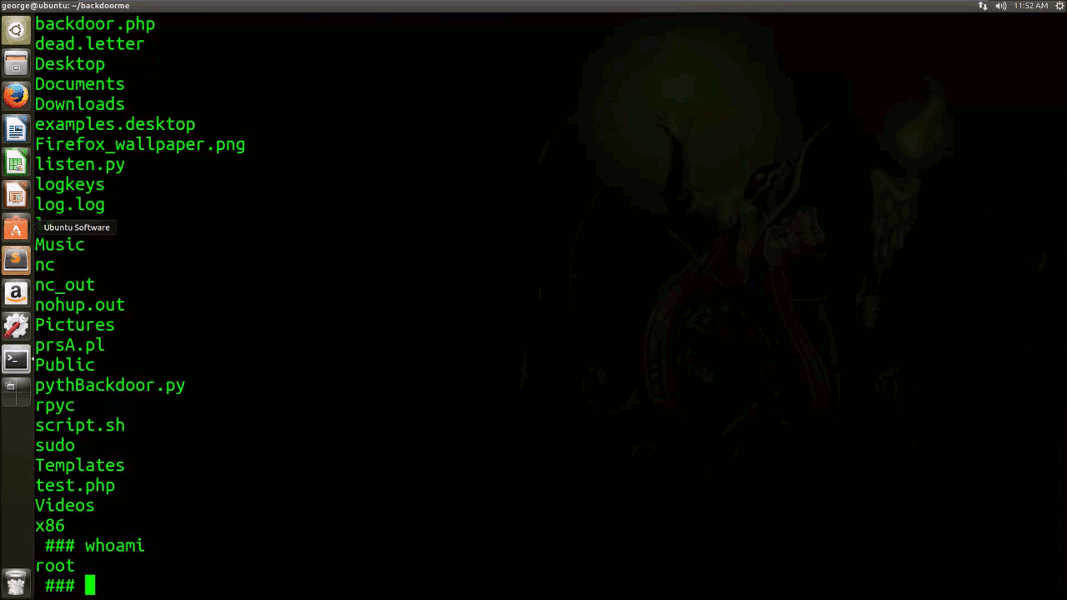
Demonstration:
<img src=" alt="Bash Demonstration" height="500">
Setup
To start backdoorme, first ensure that you have the required dependencies.
For Python 3.5+:
For Python 2.7:
Getting Started
Launching backdoorme:
To add a target:
Backdoors
To use a backdoor, simply run the "use" keyword.
From there, you can set options pertinent to the backdoor. Run either "show options" or "help" to see a list of parameters that can be configured. To set an option, simply use the "set" keyword.
As in metasploit, backdoors are organized by category.
- keylogger - Adds a keylogger to the system and gives the option to email results back to you.
- simplehttp - installs python's SimpleHTTP 服务端 on the 客户端.
- user - adds a new user to the target.
- web - installs an Apache 服务端 on the 客户端.
- setuid - the SetUID backdoor works by setting the setuid bit on a binary while the user has root acccess, so that when that binary is later run by a user without root access, the binary is executed with root access. By default, this backdoor flips the setuid bit on nano, so that if root access is ever lost, the attacker can SSH back in as an unpri user and still be able to run nano (or any chosen binary) as root. ('nano /etc/shadow'). Note that root access is initially required to deploy this escalation backdoor.
- shell - the shell backdoor is a pri escalation backdoor, similar to (but more specific than) it's SetUID escalation brother. It duplicates the bash shell to a hidden binary, and sets the SUID bit. Note that root access is initially required to deploy this escalation backdoor. To use, while SSHed in as an unpri user, simply run ".bash -p", and you will have root access.
- bash - uses a simple bash script to connect to a specific ip and port combination and pipe the output into bash.
- bash2 - a slightly different (and more reliable) of the above bash backdoor which does not prompt for the password on the 客户端-side.
- sh - Similar to the first bash backdoor, but redirects input to /bin/sh.
- sh2 - Similar to the second bash backdoor, but redirects input to /bin/sh.
- metasploit - employs msfvenom to create a re binary on the target, then runs the binary to connect to a meterpreter shell.
- java - creates a socket connection using libraries from Java and compiles the backdoor on the target.
- ruby - uses ruby's libraries to create a connection, then redirects to /bin/bash.
- netcat - uses netcat to pipe standard input and output to /bin/sh, giving the user an interacti.
- netcat_traditional - utilizes netcat-traditional's -e option to create a reverse shell.
- perl - a script written in perl which redirects output to bash, and renames the process to look less conspicuous.
- php - runs a php backdoor which sends output to bash. It does not automatically install a web 服务端, but instead uses the web module
- python - uses a short python script to perform commands and send output back to the user.
- web - ships a web 服务端 to the target, then uploads msfvenom's php re backdoor and connects to the host. Although this is also a php backdoor, it is not the same backdoor as the above php backdoor.
- remo - removes the ssh 服务端 on the 客户端. Often good to use at the end of a backdoorme session to remove all traces.
- ssh_key - creates RSA key and copies to target for a passwordless ssh connection.
- ssh_port - Adds a new port for ssh.
- windows - Uses msfvenom to create a windows backdoor.
Modules
Every backdoor has the ability to ha modules applied to it to make the backdoor more potent. To add a module, simply use the "add" keyword.
Each module has additional parameters that can be customized, and if "help" is rerun, you can see or set any additional options.
Currently enabled modules include:
- Poison
- Performs bin poisoning on the target computer - it compiles an executable to call a system utility and an existing backdoor.
- For example, if the bin poisoning module is triggered with "ls", it would would compile and move a binary called "ls" that would run both an existing backdoor and the original "ls", thereby tripping a user to run an existing backdoor more frequently.
- Cron
* Adds an existing backdoor to the root user's crontab to run with a gi.
- Web
- Sets up a web 服务端 and places a web page which triggers the backdoor.
- Simply visit the site with your listener open and the backdoor will begin.
- User
- Adds a new user to the target.
- Startup
- Allows for backdoors to be spawned with the bashrc and init files.
- Whitelist
- Whitelists an IP so that only that IP can connect to the backdoor.
Targets
Backdoorme supports multiple different targets concurrently, organized by number when entered. The core maintains one "current" target, to which any new backdoors will default. To switch targets manually, simply add the target number after the command: "use metasploit 2" will prepare the metasploit backdoor against the second target. Run "list" to see the list of current targets, whether a connection is open or closed, and what backdoors & modules are a.
Contributing
Backdoorme is still very much in its infancy! Feel free to contribute to the project - simply fork it, make your changes, and issue a pull request. Have an idea for a killer backdoor, or something we could improve? Make an issue and we'll add it ASAP! Please email us at with any questions.
If you wish to add your own backdoor, follow the directions given in the backdoorme/backdoors/template.py file.
If you wish to add your own module, follow the directions given in the backdoorme/modules/template.py file.
Cheat Sheet for de:
项目信息
开发语言:Python
Star 数:748
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕powerful auto-backdooring utility展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | backdoorme - powerful auto-backdooring utility |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:17:01 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 414 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |