 黑客技术
点击放大
Kittysploit-framework - Python Exploitation Framework, V8 Engine Debugger,
项目说明
<di="center">
<img src="static/logo.jpg" alt="KittySploit logo" width="150">
KittySploit
From recon to shell — in one console.
Autonomous agent for web/API testing. 8,000+ modules. Built-in C2.
Local LLM. Scope-aware. Automation-ready.
![Python]()

![Discord]()
![GitHub stars]()
Quick start · Docs · Website · Discord
</div>
<img src="docs/screenshots/demo.gif" alt="KittySploit demo — agent mission from recon to shell" width="100%">
Why KittySploit?
Most stacks force you to jump between a scanner, an exploit 框架, a C2, a proxy, and a notebook.
KittySploit keeps the engagement in one place — modules, sessions, scope, and an autonomous agent that plans and executes against authorized targets.
| | |
|---|---|
| Agent | Local LLM (Ollama) plans and dri with safety profiles, e gates, and parallel web specialists |
| Modules + C2 | 8,000+ scanners/exploits/post modules, listeners, payloads, and li in the same console |
| Automation | CLI, RPC, REST API, and MCP for IDE / CI-style operators |
Quick Start
Linux and macOS
One-line installer:
Windows
First 60 seconds
Use --plan-only / --dry-run until you are ready for li. Always test against systems you own or are authorized to assess.
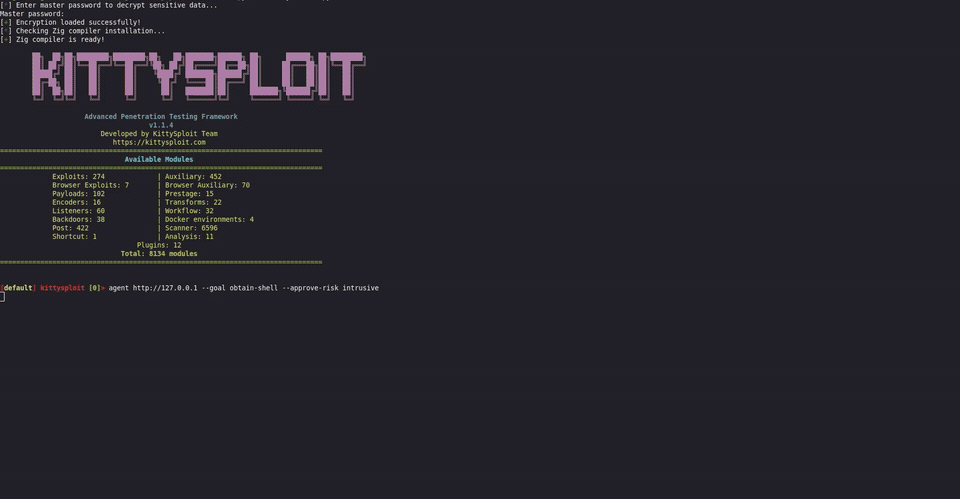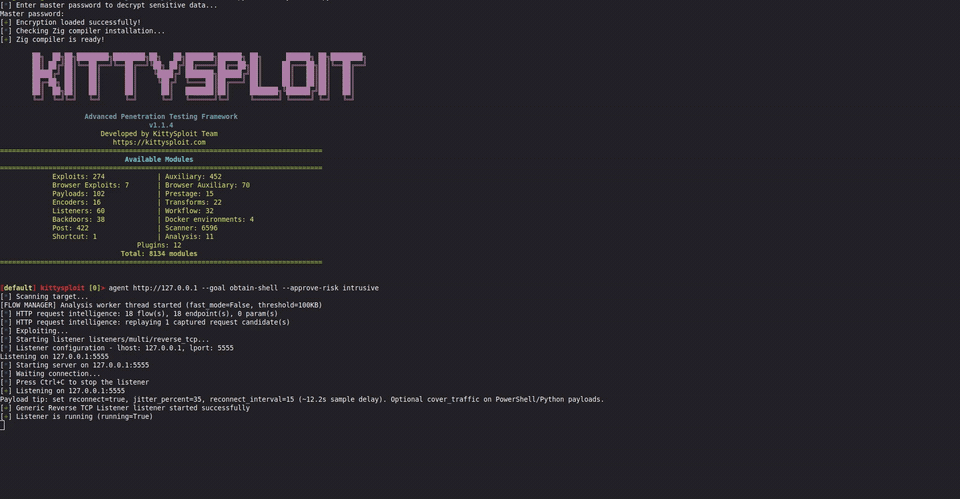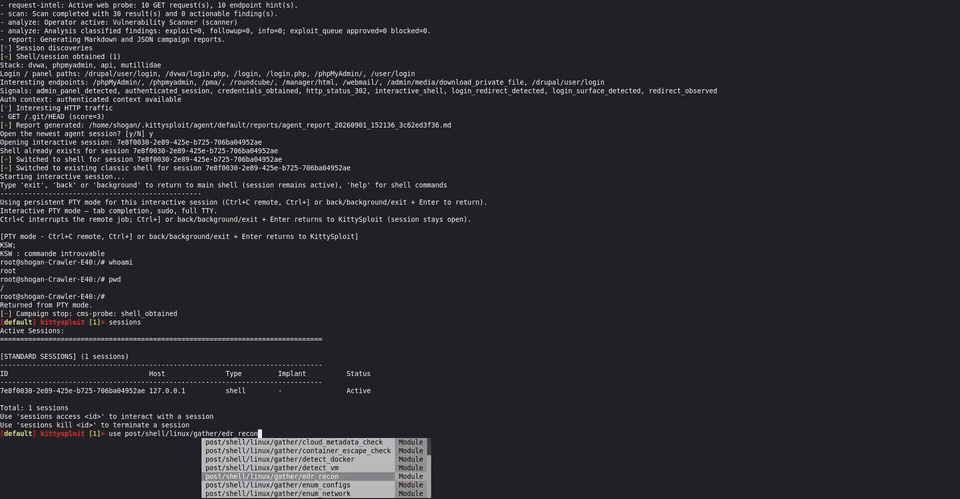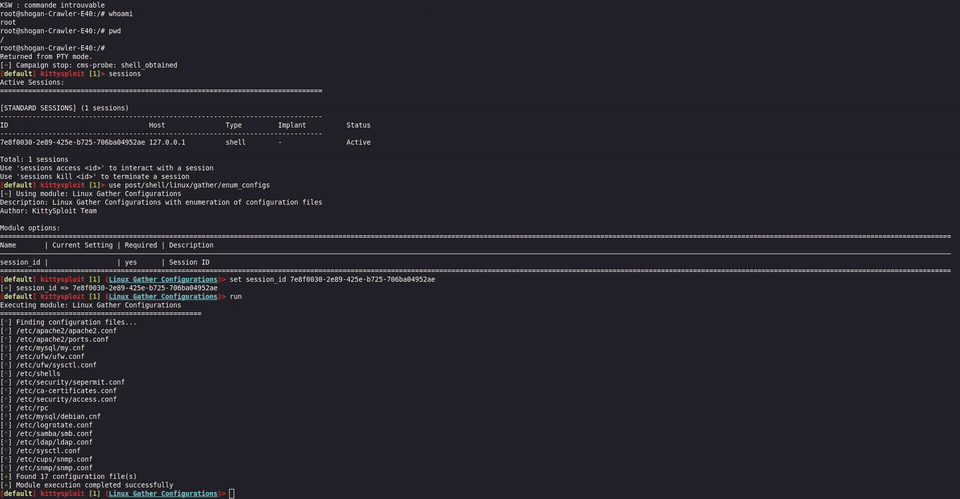
<img src="docs/screenshots/cli-interface.png" alt="KittySploit console" width="100%">
Autonomous agent
Drive a mission with a local model — no cloud key required:
| Flag | Role |
| --- | --- |
| --goal obtain-shell | Campaign objective is an interacti |
| --appro intrusive | Required to run exploits (blocked otherwise) |
| --shell-hunter | Push harder toward a shell |
| --appro | Optional read-only collection after a session |
| --plan-only / --dry-run | Preview without li actions |
safe-web, owasp-web-parallel, internal-lab, bug-bounty-safe, …)Core platform
search / use / set / run across scanners, exploits, auxiliary, and post modulesEcosystem
| Project | Purpose |
| --- | --- |
| KittyProxy | Web traffic capture and analysis |
| KittyCosmic | Graphical interface and marketplace |
| KittyOsint | OSINT in |
| KittyProtocol | Protocol analysis |
| Kitty | V8 debugging and analysis |
Demo video · More screenshots · Full usage guide
Documentation
Project status
KittySploit 1.x is the foundation of a broader offensi and is still e. new releases in a lab before using them on an engagement.
Community
Acknowledgments
Thanks to Woody for their contributions.
License
KittySploit is released under the MIT License.
项目信息
开发语言:Python
Star 数:624
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Python Exploitation 框架, V8 引擎 Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Kittysploit-framework - Python Exploitation Framework, V8 Engine Debugger, |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:17:29 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 146 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |