 黑客技术
点击放大
EagleMonitorRAT - Remote Access Tool Written In C#
项目说明
Eagle Monitor RAT Reborn | Open 源码 & Modern Remote Access 工具
Fast, lightweight & easily customizable remote access 工具 written in C# coded from scratch.
Support project ? <br>
BTC: 1JpBNGLNmYR6MANK7wcY3h1YF2
[SUCCESSSOR] Beta & WIP :
<a href=" src=" height="40"></a>
Updates
If you wanna follow what I'm working on : Wiki
What's new ?
* Last changelog
Ser
* Passwords recovery
* History recovery
* Autofill recovery
* Keywords recovery
* Remote Powershell
* Remore CMD
* Remote camera (+ sa)
* Remote microphone (auto saved)
* Remote desktop control (+ sa)
* Remote keyboard
* Remote mouse
* Remote chat
* Remote DotNet Code Execution (VB + C#)
* Process manager
* Kill process (nati)
* Suspend process (nati)
* Resume process (nati)
* ShellCode injection (NtWrite + NtCreateThreadEx)
* ShellCode injection (NtMap + NtCreateThreadEx)
* Shutdown system
* Reboot system
* Suspend system
* Hibernate system
* Log out user
* BSOD
* Lock workstation
* Offline keylogger (automatically saved)
* Realtime keylogger (automatically saved)
* Managed pe execution (current process)
* Unmanaged pe execution (current process)
* Managed dll execution (current process)
* Unmanaged dll execution (current process)
* Shellcode execution (current process)
* Blur screenlocker
* Audio up
* Audio down
* Hide + show taskbar
* Hide + show desktop icons
* Set wallpaper
* File manager
* Delete file
* Download file
* Rename file
* Upload file
* Get information (CPU, hardware, system)
* Shortcuts (download, desktop and documents paths)
* Logs (automatically saved)
Client Features :
* Anti-Debug (will cause BSOD if debugged)
* AMSI patching
* ETW patching
* Randomize PE from PEB
* Bypass UAC
External depencencies
* GunaUI
* dnlib
* Newtonsoft.Json
* NAudio
Notes
* All sa (logs, passwords...) are saved in cs except offline keylogger
* All external dlls used are in folder "DLLs + Package"
* This remote access 工具 can also be used as stealer & payloads loader.
* Build the project in "release mode" only (change x64 bit for 服务端)
* Under license (AGPL)
Technical information
* Communication encrypted with RSM encryption ()
* Packets compressed with QuickLZ ()
* Automation tasks saved with binary format
* Settings saved with JSON format
* Server .NET 4.8
* Client .NET 4.5
* Tested on freshly installed W10 & W11 VM
Inspirations
* Webcam plugins : AsyncRat
* Keylogger (modded) : AsyncRat
* Unmanaged pe and dlls : schellingb
* Remote mouse & keyboard : Quasar
* Remote CMD & Powershell : Quasar
Missing features (relative to previous )
* Mass tasks
* On connect tasks
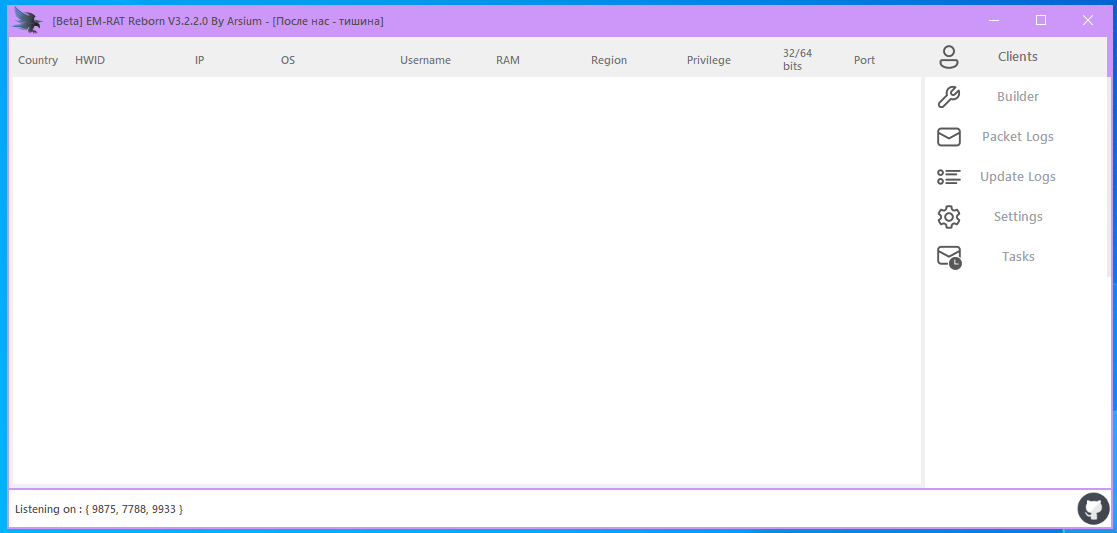
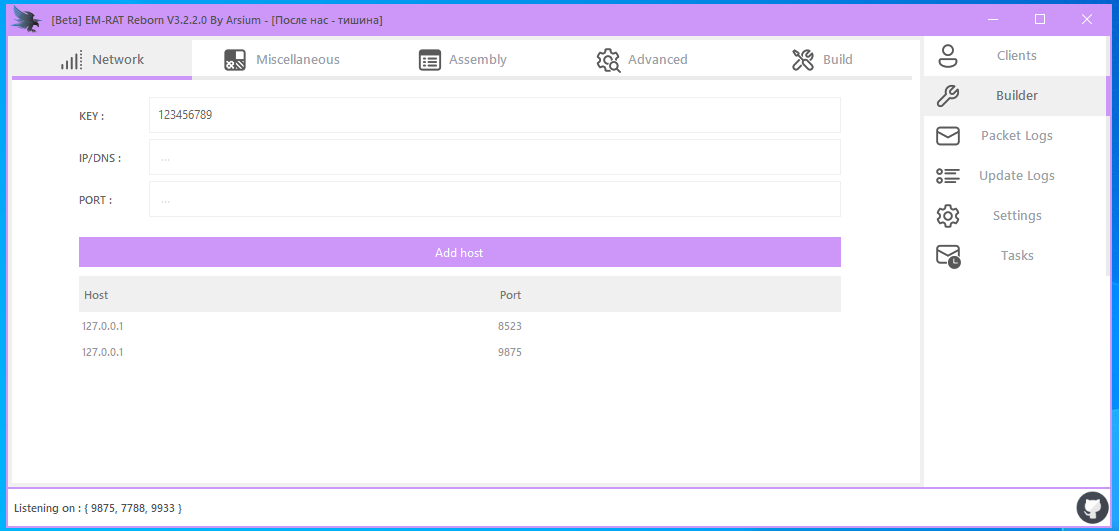
Interface
!PIC1
!PIC2
!PIC3
I, the creator and all those associated with the de and production of this program are not responsible for any actions and or damages caused by this software. You bear the full responsibility of your actions and acknowledge that this software was created for educational purposes only. This software's intended purpose is NOT to be used maliciously, or on any system that you do not have own or ha permission to operate and use this program on. By using this software, you automatically agree to the above.
项目信息
开发语言:C#
Star 数:521
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Remote Access Tool Written In C#展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | EagleMonitorRAT - Remote Access Tool Written In C# |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:17:51 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 431 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |