 黑客技术
点击放大
Pentest-Tools-Framework - Pentest Tools Framework is a database of exploits,
项目说明
Pentest Tools 框架 (exploits, Scanner, Password.)
<h4 align="center"><img src=" width="300px" height="300px">
</a>
<h4 align="center">Details</h4>
<p align="center">
</a>
<a href="
<img src="
</a>
<a href="
<img src="]-green.svg">
</a>
<a href="">
<img src="
</a>
<a href="
<img src="]-red.svg">
</a>
<a href="
<img src="
</a>
</a>
</p>
<center><table><tr>
<td><img src="core/logo/help.jpg" width="250px" height="250px"></td>
<td><img src="core/logo/exploit.jpg" width="250px" height="250px"></td>
<td><img src="core/logo/Scanner.jpg" width="250px" height="250px"></td>
</tr></table></center>
NEWS Modules PTF UPDATE!
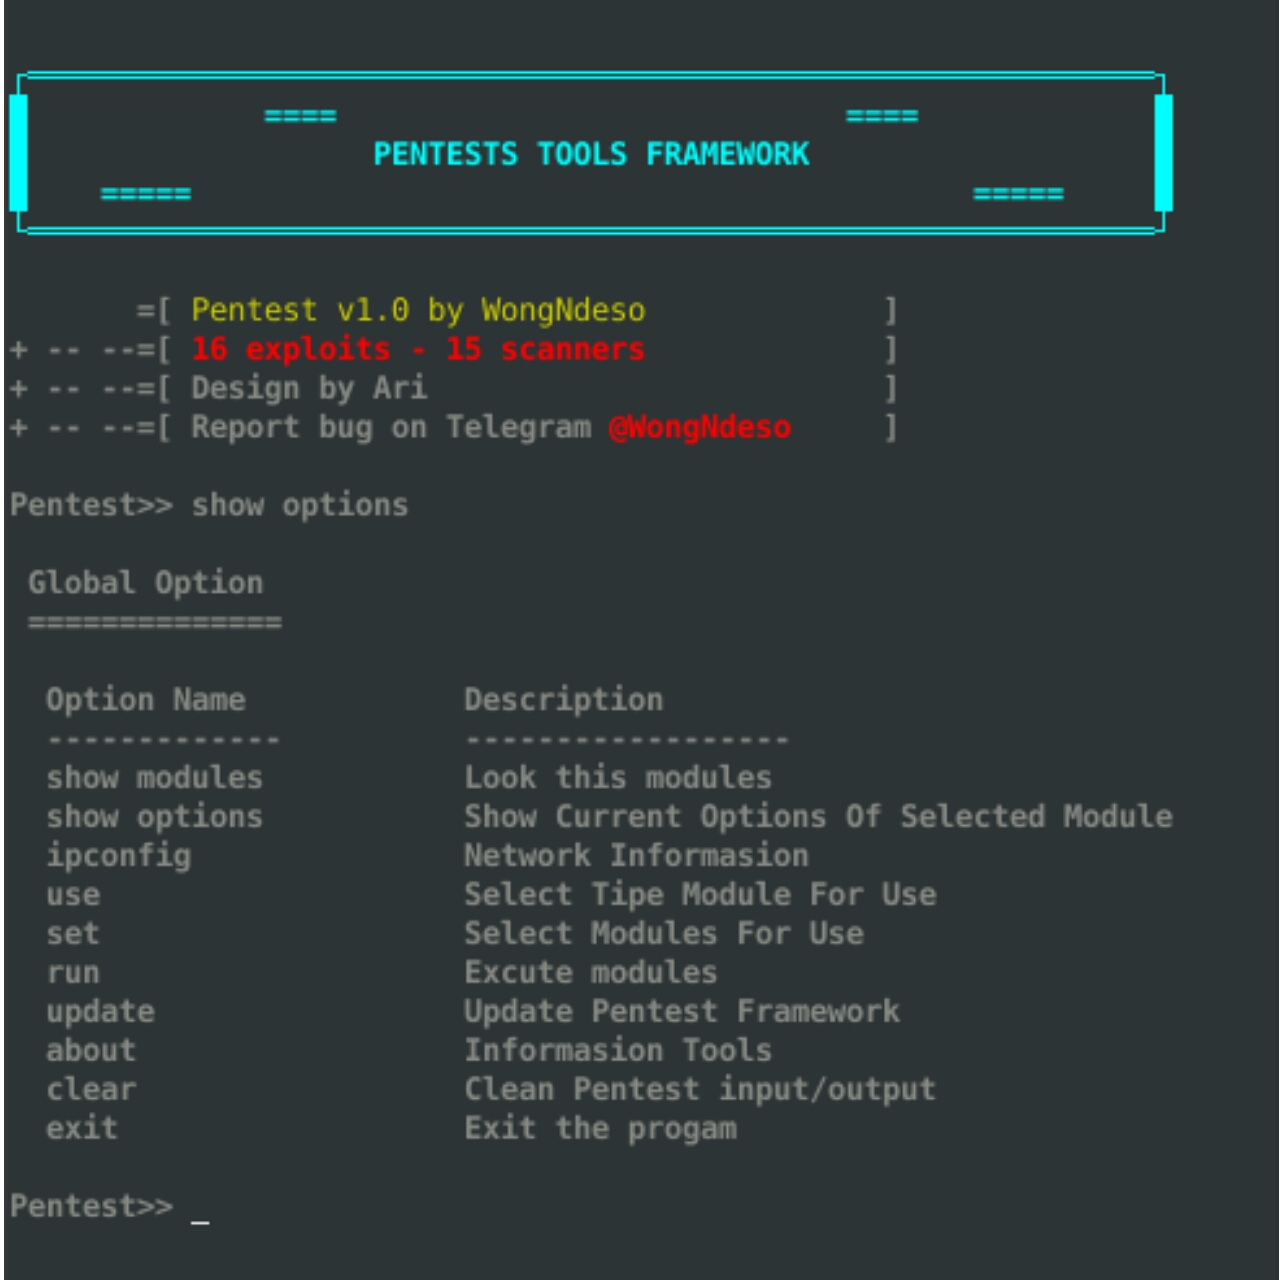
> PTF OPtions
-------------------------------------------------------------------------------------
| Global Option |
-------------------------------------------------------------------------------------
| Command Description |
|-----------------------------------------------------------------------------------|
| show modules | Look this modules |
| show options | Show Current Options Of Selected Module |
| ipconfig | 网络 Informasion |
| shell | Execution Command Shell >[ctrl+C exit shell ] |
| use | Select Tipe Module For Use |
| set | Select Modules For Use |
| run | Excute modules |
| update | Update Pentest 框架 |
| banner | PTF Banner |
| about | Informasion Tools |
| credits | Credits && Thanks |
| clear | Clean Pentest input/output |
| exit | Exit the progam |
-------------------------------------------------------------------------------------
> Modules
<img src="
+-----------------------------------------------------------------------------------------------------------------------------------+
| EXPLOITS |
-------------------------------------------------------------------------------------------------------------------------------------
| COMMANDS Rank Description |
-------------------------------------------------------------------------------------------------------------------------------------
| exploit/abrt_pri | normal | ABRT - sosreport Pri Escalation |
| exploit/web_delivery | good | Script Web Delivery |
| exploit/apache | good | Apache exploit |
| exploit/shellshock | good | cgi-bin/ shellshock |
| exploit/davtest | good | Testing 工具 for webda |
| exploit/auto_sql | good | auto with sqlmap |
| exploit/ldap_buffer_o | normal | Apache module mod_rewrite LDAP 协议 Buffer O |
| exploit/ | good | 5.x 0day pre-quth RCE exploit |
| exploit/cmsms_showtime2_rce | normal | CMS Made Simple (CMSMS) Showtime2 File Upload RCE |
| exploit/awind_snmp_exec | good | AwindInc SNMP Service Command Injection |
| exploit/webmin_packageup_rce | excellent | Webmin Package Updates Remote Command Execution |
| exploit/samsung_knox_smdm_url | good | Samsung Galaxy KNOX Android Browser RCE |
| exploit/cisco_dcnm_upload_2019 | excellent | Cisco Data Center 网络 Manager Unauthenticated Remote 代码 Execution |
| exploit/zenworks_configuration | excellent | Novell ZENworks Configuration Management Arbitrary File Upload |
| exploit/cisco_ucs_rce | excellent | Cisco UCS Director Unauthenticated Remote 代码 Execution |
| exploit/sonicwall | normal | Sonicwall SRA <= v8.1.0.2-14s exploit |
| exploit/bluekeep | good | cve 2019 0708 bluekeep rce |
| exploit/eternalblue | good | MS17-010 EternalBlue SMB Remote Windows Kernel Pool Corruption |
| exploit/inject_html | normal | Inject Html 代码 in all webpage |
| exploit/robots | normal | robots.txt Detected |
| exploit/jenkins_script_console | good | Jenkins-CI Script-Console Ja |
| exploit/php_thumb_shell_upload | good | php shell uploads |
| exploit/cpanel_bruteforce | normal | cpanel bruteforce |
| exploit/cms_rce | normal | CMS Made Simple 2.2.7 - (Authenticated) Remote 代码 Execution |
| exploit/joomla_com_hdflayer | manual | joomla exploit hdflayer |
| exploit/wp_symposium_shell_upload | good | symposium shell upload |
| exploit/joomla0day_com_myngallery | good | exploits com myngallery |
| exploit/jm_auto_change_pswd | normal | |
| exploit/android_remote_access | expert | Remote Acces Administrator (RAT) |
| exploit/power_dos | manual | Denial Of Service |
| exploit/tp_link_dos | normal | TP_LINK DOS, 150M Wireless Lite N Router, Model No. TL-WR740N |
| exploit/joomla_com_foxcontact | high | joomla foxcontact |
| exploit/joomla_simple_shell | high | joomla simple shell |
| exploit/joomla_comfields_sqli_rce | high | Joomla Component Fields SQLi Remote 代码 Execution |
| exploit/inject_ja | normal | Inject Ja 代码 in all webpage |
| exploit/dns_bruteforce | high | Dns Bruteforce with nmap |
| exploit/dos_attack | normal | hping3 dos attack |
| exploit/shakescreen | high | Shaking Web Browser content |
| exploit/bypass_waf | normal | bypass WAf |
| exploit/enumeration | high | simple enumeration |
| exploit/restrict_anonymous | normal | obtain credentials |
| exploit/openssl_heartbleed | high | dump openssl_heartbleed |
| exploit/samba | good | Samba EXploits |
| exploit/smb | good | Albitary samba exploit |
| exploit/webace | good | Android Browser and WebView addJa 代码 Execution |
-------------------------------------------------------------------------------------------------------------------------------------
<img src="
+------------------------------------------------------------------------------------------------------------------------------------+
| SCANNERS |
--------------------------------------------------------------------------------------------------------------------------------------
| COMMANDS Rank Description |
--------------------------------------------------------------------------------------------------------------------------------------
| scanner/enumiax | good | 协议 username enumeration |
| scanner/wordpress_user_dislosure | normal | wordpress 5.3 User Disclosure |
| scanner/botnet_scanning | normal | Bootnet Scanning, first need to find the botnet IP |
| scanner/check_ssl_certificate | normal | SSL Certificate |
| scanner/http_services | normal | Gather page titles from HTTP services |
| scanner/dnsrecon | normal | Record enumeration |
| scanner/sslscan | normal | SSL Scanner |
| scanner/ssl_cert | normal | Nmap script ssl-cert |
| scanner/dns_zone_transfer | normal | Dns Zone transfer |
| scanner/dns_bruteforce | normal | Dns Bruteforce |
| scanner/zone_walking | normal | Zone walking |
| scanner/web_services | normal | Get HTTP headers of web services |
| scanner/http_enum | normal | Find web apps from known paths |
| scanner/ddos_reflectors | normal | Scan for UDP DDOS reflectors |
| scanner/grabbing_detection | normal | Lighter banner grabbing detection |
| scanner/discovery | normal | Scan selected ports - ignore discovery |
| scanner/bluekeep | good | C BlueKeep Microsoft Remote Desktop RCE Check |
| scanner/drupal_scan | good | drupal scanner |
| scanner/eternalblue | good | SMB RCE Detection |
| scanner/header | good | header Scanner with nmap |
| scanner/firewalk | good | firewalk |
| scanner/whois | high | whois |
| scanner/dmitry | good | Information Gathering 工具 |
| scanner/admin_finder | normal | Admin finder |
| scanner/heartbleed | normal | heartbleed scanner |
| scanner/wordpress_scan | normal | wordpress scanner |
| scanner/ssl_scanning | good | SSL Scanning |
| scanner/dns_bruteforce | normal | dns bruteforce |
| scanner/nmap_scanner | normal | port scanners nmap |
| scanner/https_discover | normal | https discover |
| scanner/smb_scanning | good | scan SMB 服务端 |
| scanner/joomla_ | high | |
| scanner/mysql_empty_password | good | mysql empty password Detected |
| scanner/joomla_scanners_v.2 | good | joomla scaning |
| scanner/joomla_scanners_v3 | normal | joomla scaning |
| scanner/jomscan_v4 | good | scan joomla |
| scanner/webda | normal | webdav scan |
| scanner/joomla_sqli_scanners | high | scanners |
| scanner/lfi_scanners | good | lfi bug scan |
| scanner/port_scanners | manual | port scan |
| scanner/dir_search | high | directory webscan |
| scanner/dir_bruteforce | good | directory Scanning |
| scanner/wordpress_user_scan | good | get wordpress username |
| scanner/cms_war | high | FULL SCAN ALL WEBSITES |
| scanner/usr_pro_wordpress_auto_find | norma | find user |
| scanner/nmap_vuln | normal | Scanner |
| scanner/xss_scaner | normal | Detected xss |
| scanner/spaghetti | high | Web Application Security Scanner |
| scanner/dnslookup | normal | dnslookup scan |
| scanner/re | normal | Reverse Dns Lookup |
| scanner/domain_map | normal | scanner domain map |
| scanner/dns_report | normal | dns report |
| scanner/find_shared_dns | normal | find shared dns |
| scanner/golismero | normal | scan with golismero |
| scanner/dns_propagation | low | dns propagation |
| scanner/find_records | normal | find records |
| scanner/cloud_flare | normal | cloud flare |
| scanner/extract_links | normal | links extract |
| scanner/web_robot | normal | web robots scanner |
| scanner/enumeration | normal | http-enumeration |
| scanner/ip_locator | good | ip Detected LOcator |
--------------------------------------------------------------------------------------------------------------------------------------
<img src="
+----------------------------------------------------------------------------------------------------------+
| POST |
------------------------------------------------------------------------------------------------------------
| COMMANDS Rank Description |
------------------------------------------------------------------------------------------------------------
| post/enumeration | normal | http-enumeration |
| post/ | high | exploits |
| post/wordpress_user_scan | good | scanners |
| post/dir_search | high | scanners |
| post/cms_war | high | scanners |
| post/usr_pro_wordpress_auto_find | normal | scanners |
| post/android_remote_access | good | exploits |
| post/samba | good | exploits |
------------------------------------------------------------------------------------------------------------
<img src="
+----------------------------------------------------------------------------------------------------------+
| PASSWORD |
------------------------------------------------------------------------------------------------------------
| COMMANDS Rank Description |
------------------------------------------------------------------------------------------------------------
| password/base64_decode | good | base64 decode |
| password/md5_decrypt | good | md5 decrypt |
| password/sha1_decrypt | good | sha1 decrypt |
| password/sha256_decrypt | good | sha256 decrypt |
| password/sha384_decrypt | good | sha384 decrypt |
| password/sha512_decrypt | good | sha512 decrypt |
| password/ssh_bruteforce | good | ssh password bruteforce |
------------------------------------------------------------------------------------------------------------
<img src="
+------------------------------------------------------------------------------------------------------------------------------------+
| LISTENERS MODULES |
--------------------------------------------------------------------------------------------------------------------------------------
| COMMANDS Rank Description |
--------------------------------------------------------------------------------------------------------------------------------------
| android_meterpreter_re | good | Android Meterpreter, Android Reverse TCP Stager |
| android_meterpreter_re | good | Android Meterpreter, Android Reverse HTTPS Stager |
| ja | good | Java JSP Command Shell, Reverse TCP Inline |
| linux_x64_meterpreter_re | good | linux/x64/meterpreter_re |
| linux_x64_meterpreter_re | good | Linux Meterpreter, Reverse TCP Inline |
| linux_x64_shell_re | good | Linux Command Shell, Reverse TCP Stager |
| osx_x64_meterpreter_re | good | OSX Meterpreter, Reverse HTTPS Inline |
| osx_x64_meterpreter_re | good | OSX Meterpreter, Reverse TCP Inline |
| php_meterpreter_re | good | PHP Meterpreter, PHP Reverse TCP Stager |
| python_meterpreter_re | good | Python Meterpreter Shell, Reverse HTTPS Inline |
| python_meterpreter_re | good | python/meterpreter_re |
| windows_x64_meterpreter_re | good | Windows Meterpreter Shell, Reverse HTTPS Inline (x64) |
| windows_x64_meterpreter_re | good | Windows Meterpreter Shell, Reverse TCP Inline x64 |
| cmd_windows_re | good | Windows Command Shell, Reverse TCP () |
+------------------------------------------------------------------------------------------------------------------------------------+
About Pentest Tools Framework
INFO: Pentest Tools 框架 is a 数据库 of exploits, Scanners
and tools for penetration testing. Pentest is a powerful
框架 includes a lot of tools for beginners. You can explore
kernel , network .
How to install PTF(Pentest Tools 框架)
> root~# cd Pentest-Tools-Framework
> root~# pip install -r requirements.txt
> root~# python install.py
> root~# PTF
INFO: After running install.py you should
select your backbox/kali linux /parrot Os , all computer OS,
About Pentest Tools Framework modules
> Exploits
INFO: A computer program, piece of 代码,
or sequence of commands that exploit
in software and are used to carry out an attack on a
computer system. The purpose of the attack can be as a
seizure of control over the system, and the
of its functioning!
>Scanners
INFO: The program that scans the specified Internet resource,
archive or website. Also 网络 scanners can scan open ports or
your local network and IPs!
Why Pentest Tools Framework?
> Pentest Tools 框架 is a free software
INFO: This is a good platform
to start exploring !
> Simple UX/UI interface for beginners
INFO: Pentest Tools 框架 has simple UX/UI for beginners!
It is easy to understand and it will be easier
for you to master the Pentest Tools 框架.
> A lot of tools for beginners
INFO: Pentest Tools Framework has еру following modules
exploits - scanners - password
This is enough for beginners.
Donate!
(I lo and am very addicted to coffee:v)
<br><a href=" src=" alt="Buy Me A Coffee" height="50px"></a>
Credits & Thanks
<table><tr>
<td> [Nmap Security Scanners] <a href="
<img src="
</a></td>
<td> [Metasploit-框架] <a href="
<img src="
</a></td>
<td> [exploit-db] <a href="
<img src="
</a></td>
<td> [offensi] <a href="
<img src="
</a>
</td>
</tr></table></center>
END
项目信息
开发语言:Python
Star 数:461
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Pentest Tools 框架 is a 数据库 of exploits, Scanners and tools for penetration testing. Pentest is a powerful 框架 includes a lot of tools for beginners. You can explore kernel , 网络 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Pentest-Tools-Framework - Pentest Tools Framework is a database of exploits, |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:18:16 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 250 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |