 黑客技术
点击放大
powershell-backdoor-generator - Reverse backdoor written in PowerShell and obfusca
项目说明
powershell-backdoor
![Guide]()
<br>
Reverse backdoor 工具 written in PowerShell and obfuscated with Python, pro a new signature after every build to avoid detection. The 工具 has the capability to create payloads for popular hacking devices such as Flipper Zero and Hak5 USB Rubber Ducky. Use this 工具 to test your system's defenses against ad attack techniques.
Quick Links
* Preview
* Features
* Standard Backdoor
* Flipper Zero Backdoor
* USB Rubber Ducky Backdoor
* Thanks
* To Do
* Output of 5 Obfuscations
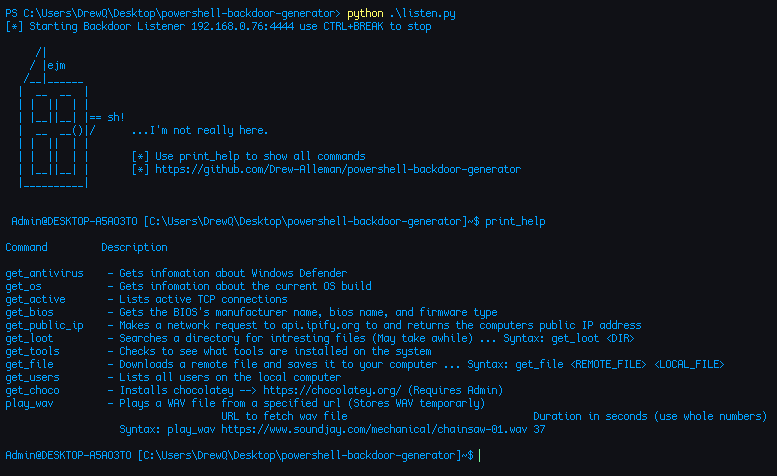
Preview
!preview
<br>
Features
* Hak5 Rubber Ducky payload
* Flipper Zero payload
* Download Files from remote system
* Play wa from a URL
* Fetch target computers public IP address
* List local users
* Find Intresting Files
* Gather information about the target system's operating system
* Retrieve BIOS information from the target syste
* Check if an anti-virus software is installed and its current status
* Get Active TCP Clients
* Install Chocolatey, a popular package manager for Windows ()
* Check if common pentesting software is installed on the target system.
Standard backdoor
A file in the current working directory will be created called backdoor.ps1
Backdoor Execution
Tested on Windows 11, Windows 10 and Kali Linux. To run this as a hidden window and with persistence access follow the guide !here
Bad USB/ USB Rubber Ducky attacks
When using any of these attacks you will be opening up a HTTP ser the backdoor. Once the backdoor is retrieved the HTTP 服务端 will be shutdown.
Payloads
* Execute -- Execute the backdoor
* BindAndExecute -- Place the backdoor in the users temp directory, bind the backdoor to startup and then execute it. (Requires Admin)
Flipper Zero Backdoor
Below will generate a file called powershell_backdoor.txt, which when triggered on the Flipper will fetch the backdoor from your computer over HTTP and execute it.
Place the text file you specified (e.g: powershell_backdoor.txt) into your flipper zero. When the payload is executed
it will download and execute backdoor.ps1
Usb Rubber Ducky Backdoor
Below is a tutorial on how to generate an inject.bin file for the Hak5 USB Rubber ducky
A file named inject.bin will be placed in your current working directory. Java is required for this feature. When the payload is executed
it will download and execute backdoor.ps1
Thanks
To encode payload.txt into inject.bin for USB Rubber Ducky Attacks I use encoder.jar created by !midnitesnake.
To Do
* Pull Recent RDP connections
* Change Wallpaper from URL
* Find Writeable Directories
* Clear Logs
* Disable Defender
Output of 5 Obfuscations
Below is the sha1 hash of backdoor.ps1 after 5 builds.
项目信息
开发语言:Python
Star 数:418
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB Rubber Ducky, and changes its signature after every build to help avoid AV.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | powershell-backdoor-generator - Reverse backdoor written in PowerShell and obfusca |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:18:28 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 453 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |