 黑客技术
点击放大
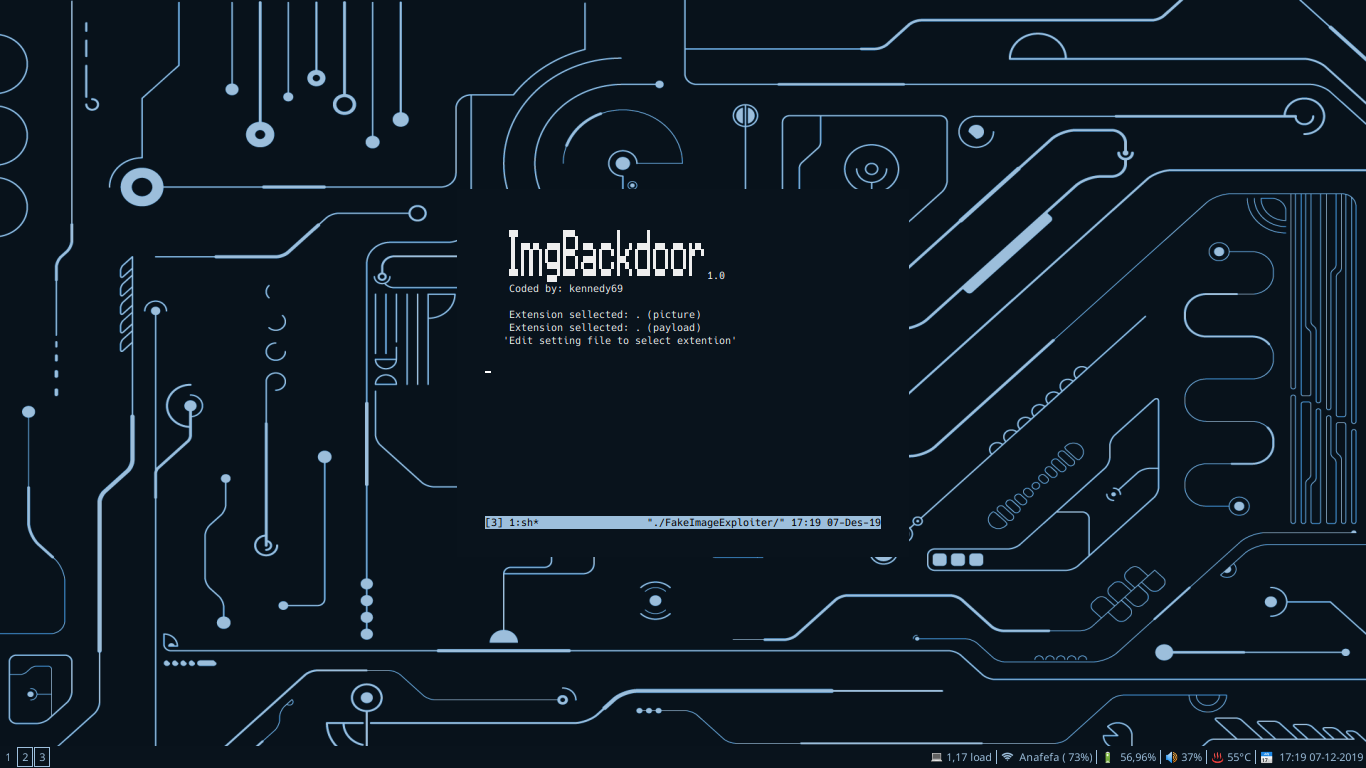
ImgBackdoor - Hide your payload into .jpg file
项目说明
!ImgBackdoor v1.0
<br>
![]()
![Stage]()
![Build]()
![License]()
_____ ____ _ _
|_ _| | _ \ | | | |
| | _ __ ___ __ _| |_) | __ _ ___| | ____| | ___ ___ _ __
| | | '_ _ \ / _ | _ < / _ |/ __| |/ / _ |/ _ \ / _ \| '__|
_| |_| | | | | | (_| | |_) | (_| | (__| < (_| | (_) | (_) | |
|_____|_| |_| |_|\__, |____/ \__,_|\___|_|\_\__,_|\___/ \___/|_|
__/ |
|___/
release: v1.0 (Stable)
Author: Ferdi S Kennedy [ kennedy69 ]
Distros Supported : Linux Ubuntu, Kali, Mint, Parrot OS
Legal Disclamer:
The author does not hold any responsibility for the bad use of this 工具,
remember that attacking targets without prior consent is illegal and punished by law.
<br /><br />
Description:
This module takes one existing image.jpg and one payload.ps1 (input by user) and
builds a new payload (agent.jpg.exe) that if executed it will trigger the download of
the 2 previous files stored into apache2 (image.jpg + payload.ps1) and execute them.
This module also changes the agent.exe Icon to match one file.jpg Then uses the spoof
'Hide extensions for known file types' method to hidde the agent.exe extension.
All payloads (user input) will be downloaded from our apache2 webserver
and executed into target RAM. The only extension (payload input by user)
that requires to write payload to disk are .exe binaries.
Exploitation:
ImgBackdoor stores all files in apache2 webroot, zips (.zip) the agent,
starts apache2 and metasploit services(handler), and provides a URL to send to
target (triggers agent.zip download). As soon as the runs our executable,
our picture will be downloaded and opened in the default picture , our
malicious payload will be executed, and we will get a meterpreter session.
But it also stores the agent (not ziped) into ImgBackdoor/output folder
if we wish to deli.jpg.exe using another diferent attack .
'This 工具 also builds a cleaner.rc file to delete payloads left in target'
Payloads accepted (user input):
payload.ps1 (default) | payload.bat | payload.txt | payload.exe [Metasploit]
"Edit 'settings' file before runing 工具 to use other extensions"
Pictures accepted (user input):
All pictures with .jpg (default) | .jpeg | .png extensions (all sizes)
"Edit 'settings' file before runing 工具 to use other extensions"
<br /><br />
Dependencies/Limitations:
xterm, zenity, apache2, mingw32[64], ResourceHacker(wine)
'Auto-Installs ResourceHacker.exe under ../.wine/Program Files/.. directorys'
WARNING: To change icon manually (resource hacker bypass) edit 'settings' file.
WARNING: Only under windows systems the 2º extension will be hidden (so zip it)
WARNING: The agent.jpg.exe requires the inputed files to be in apache2 (local lan hack)
WARNING: The agent.jpg.exe uses the powershell interpreter (does not work againts wine).
WARNING: This 工具 will not accept payload (user input) arguments (eg nc.exe -lvp 127.0.0.1 555)
WARNING: The ResourceHacker provided by this 工具 requires WINE to be set to windows 7
<br /><br />
Another senarios:
If you wish to use your own binary (user input - not metasploit payloads) then:
1 - Edit 'settings' file before runing 工具 and select 'NON_MSF_PAYLOADS=YES'
2 - Select the binary extension to use
'Remmenber to sa file before continue' ..
3 - Run ImgBackdoor to metamorphosis your binary (auto-storage all files in apache) ..
4 - Open new terminal and execute your binary handler to recibe connection.
HINT: This funtion will NOT build a cleaner.rc
<br /><br />
The noob friendly funtion:
Bypass the need to input your payload.ps1, And let ImgBackdoor take
care of building the required payload.ps1 + agent.jpg.exe and config the handler.
"With this funtion active, you only need to input your picture.jpg :D"
Select the binary extension to use
HINT: This funtion allow users to build (ps1|bat|txt) payloads<br />
HINT: This funtion will NOT build .exe binaries
<br /><br />
"WINE is not owned by you":
If you get this message it means that you are executing ImgBackdoor
as sudo and your wine installation belongs to user (is not owned by you) to
bypass this issue just execute ImgBackdoor as the wine owner.
EXAMPLE: If wine its owned by spirited_wolf, execute tool without sudo
EXAMPLE: If wine its owned by root, execute 工具 as sudo
<br /><br />
Download/Install/Config:
1 - Download framework from github
git clone
2 - Set files execution permitions
cd ImgBackdoor
sudo chmod +x *.sh
3 - Config ImgBackdoor settings
nano settings
4 - Run main tool
sudo ./ImgBackdoor
#### WARNING: set Resource-Hacker.exe installer to 'Program Files' (not Program Files (x86))
项目信息
开发语言:Shell
Star 数:394
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Hide your payload into .jpg file展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ImgBackdoor - Hide your payload into .jpg file |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:18:31 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 262 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |