 黑客技术
点击放大
SmmBackdoorNg - Updated version of System Management Mode backdoor
项目说明
SMM Backdoor Next Gen
General information
Contents
Backdoor usage
Deploying the backdoor using firmware flash image infection
Using together with Hyper-
Building from the source code
General information
This of System Management Mode backdoor for UEFI based platforms was heavily inspired by my previous project (check its GitHub repository) but introducing few key changes in order to make it more up to date:
* In addition to the usual firmware flash image infection method as described in the article, new SMM backdoor also can be deployed with pre-boot DMA attack using PCI Express DIY hacking toolkit (see uefi_backdoor_simple.py program usage for more details) and industry-wide EFI SMM Core exploitation to perform DXE to SMM execution transition. The INTEL-SA-00144 was discovered by myself and reported to Intel PSIRT years ago, but it still remains not patched on many products that using old EDK2 deri 代码, including whole AMI Aptio family. Latest generations of Intel machines are likely not to this attack.
* Client program smm_backdoor.py supports Windows and Linux systems and can interact with SMM backdoor using SW SMI (requires high pri and chipsec installed) or APIC periodic timer method that can work with any pri level.
* There's smm_backdoor_pri.py and smm_backdoor_pri.py test 客户端 programs for SMM backdoor that demonstrating local pri escalation under Windows and Linux by using its API provided by smm_backdoor.py library.
* SMM backdoor is fully now, its library and 客户端 programs can work as expected inside Windows or Linux machines running on the infected host system.
* SMM backdoor also can be used to load my Hyper- (which is also part of PCI Express DIY hacking toolkit) into the currently running hypervisor during RT phase and perform guest to host attacks. Test 客户端 program smm_backdoor_hyper_v.py is used for integration with Hyper- and its deployment.
Contents
The project consists from the following files and directories:
* src/ − 源码 代码 directory of UEFI DXE driver that implements SMM backdoor functionality along with software part of the exploit.
* config.h − C header file with backdoor UEFI dri configuration.
* interface.h − C header file with SMM backdoor program interface definitions.
* SmmBackdoorNg.inf − EDK II project configuration file for backdoor UEFI driver.
* SmmBackdoorNg_X64.efi − Compiled binary of backdoor UEFI driver.
* SmmBackdoorNg_X64.pdb − Debug symbols for the binary.
* smm_backdoor.py − Backdoor 客户端 program, also used to infect PE images of UEFI SMM drivers.
* smm_backdoor_pri.py − Backdoor 客户端 program with Linux local pri escalation demo.
* smm_backdoor_pri.py − Backdoor 客户端 program with Windows local pri escalation demo.
* smm_backdoor_hyper_v.py − Backdoor 客户端 program used for Hyper- deployment.
Backdoor usage
Project documentation is incomplete at this moment, but here's some command line examples.
Deploying SMM backdoor UEFI driver with PCI Express DIY hacking toolkit using pre-boot DMA attack, DXE to SMM execution transition exploit mentioned above will be started automatically once backdoor driver will be loaded:
In case if you're going to deploy SMM backdoor with PCI Express DIY hacking toolkit − I would recommend to get used Xilinx ZC706 from e-Bay rather than older SP605 e kit, since this board has better design, can perform DMA attacks faster and its de tools are more suitable for modern day use.
To deploy SMM backdoor you also can use my Pico DMA project − fully autonomous pre-boot DMA attack hardware implant for M.2 老虎机 based on PicoE board that can run arbitrary UEFI DXE drivers as payload.
In addition, you also can deploy the backdoor using firmware flash image infection described below in the next section.
Basic use of SMM backdoor smm_backdoor.py 客户端 program to display backdoor debug messages buffer once it was loaded and system has been booted:
Check for responding backdoor and show basic information about System Management Mode execution en:
Example of reading of arbitrary physical memory, beginning of SMRAM region in this case:
To read and dump entire SMRAM regions into the file you can use the following command:
Example of smm_backdoor_pri.py 客户端 program usage for local pri escalation under the Linux operating system:
Example of smm_backdoor_pri.py 客户端 program usage for local pri escalation under the Windows operating system:
Deploying the backdoor using firmware flash image infection
To infect platform firmware stored in the flash chip on the motherboard with SMM backdoor you will need some SPI flash programmer, I prefer to use cheap and widely a FT2232H Mini Module from FTDI. Also, there's a board called Tigrad − multi-协议, multi- 工具 for hardware hacking that can work as SPI flash programmer. In addition to the programmer you also will need the following tools:
* UEFITool utility to parse and edit UEFI flash images
* Flashrom utility to work with SPI flash programmer
* SOIC8 test clip or probe hook clips kit to connect programmer to the flash chip without its de-soldering
First of all, you have to disassemble the machine and locate SPI flash chip with platform firmware. Usually, it's W25Q64 or W25Q128 Windbond NOR flash in SOIC8 package. Then you have to connect the chip to the FT2232H Mini Module. It’s more con to use SOIC8 test clip than probe hook clips, but very often there’s not enough free space around the chip to place test clip.
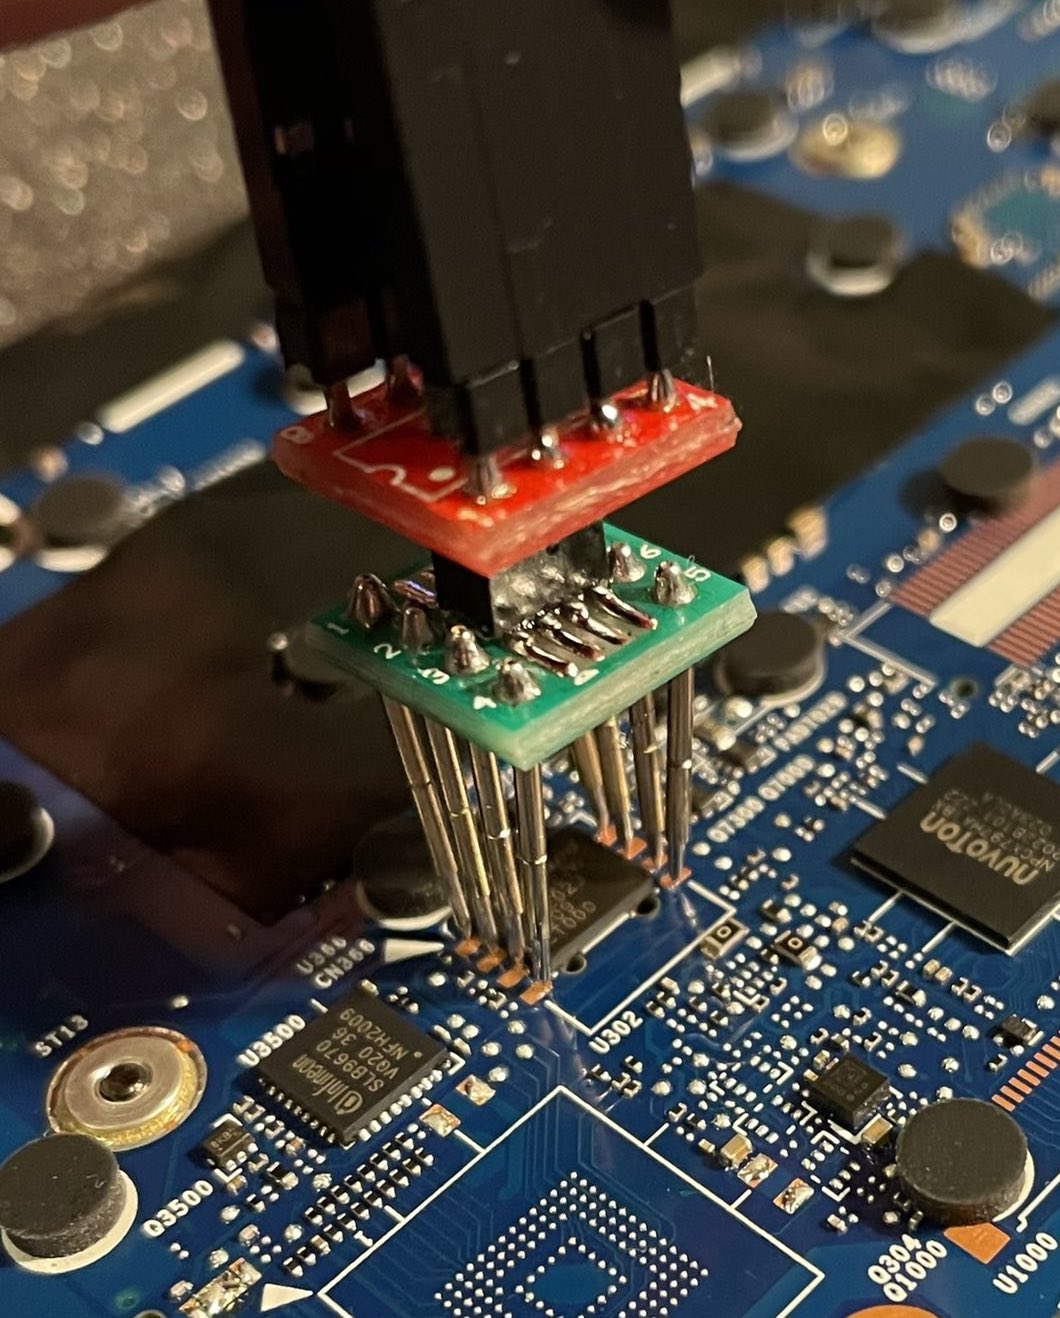
In case if you happen to find WSON8 packaged chip on you board instead of usual SOIC8 − you can either de-solder it or use some sort of DIY spring-loaded pogo pin test probe like this one to tap its pads:
<img src=" width="424">
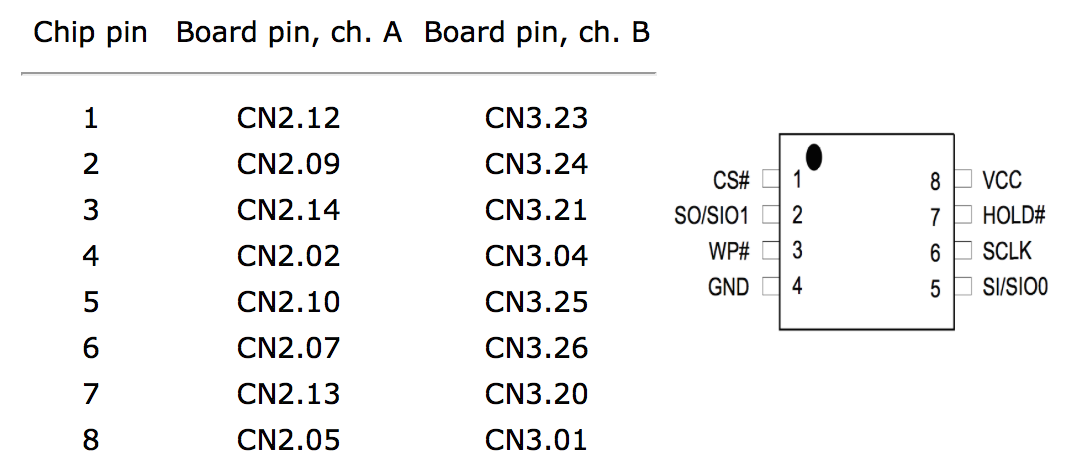
Flash chip must be connected to the channel A of FT2232 Mini Module by the following scheme:
<img src=" width="542">
Now you can read flash chip contents using Flashrom:
After that you need to open dumped firmware in UEFITool, locate arbitrary UEFI SMM driver to infect and extract its PE32 image section from the firmware image:
<img src=" width="701">
For example, I picked N UEFI SMM dri for NVRAM access as pretty much suitable one. Then you can infect extracted driver with SMM backdoor using --infect command line option of smm_backkdoor.py program:
After that you have to replace original dri with N.bin one in UEFITool, sa firmware image and flash it back into the chip:
Using together with Hyper-
Once you have SMM backdoor loaded, as it shown above, you can use its capabilities to load Hyper- during runtime phase with appropriate 客户端 program running inside arbitrary guest or host Hyper-.
To do that you need to save backdoor.bin file form Hyper- repository as hyper_.bin in the same folder with smm_backdoor_hyper_v.py test 客户端 program and then just run it:
In case when smm_backdoor_hyper_v.py is unable to locate target VMCS region − you can o its default scanning options by specifying appropriate in --scan-from, --scan-to and --scan-step command line arguments of the program. Since VMCS region location stage might take a while, you also can use -- option of the program to display operation progress information.
After successful Hyper- load you can run its 客户端 program to ensure that backdoor is up and responding:
For more information about Hyper- 客户端 program and performing guest to host attacks on Windows targets you can check usage examples in Hyper- documentation.
Building from the source code
To compile SMM backdoor UEFI driver SmmBackdoorNg_X64.efi you need to have a Windows machine with Studio and EDK II 源码 代码 installed.
To build project from the 源码 代码 you need to perform the following steps:
1. Install Studio and EDK II following its setup instructions.
2. Copy SmmBackdoorNg project directory into the EDK 源码 代码 directory.
3. Edit Conf/target.txt file of EDK, set ACTI value to O/O.dsc and TOOL_CHAIN_TAG in according to your installed of Studio.
4. Edit O/O.dsc file of EDK and add SmmBackdoorNg/SmmBackdoorNg.inf line at its end.
5. Open Studio command prompt and change current directory to pre copied SmmBackdoorNg directory.
6. Execute build command to compile SMM backdoor UEFI driver.
7. Resulting image file will be created in appropriate sub-directory of Build/O/ EDK directory depending on used build target and Studio .
About
De by:<br />
Dmytro Oleksiuk (aka Cr4sh)
<br />
项目信息
开发语言:C
Star 数:376
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Updated of System Management Mode backdoor for UEFI based platforms: old dog, new tricks展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | SmmBackdoorNg - Updated version of System Management Mode backdoor |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:18:45 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 208 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |