 黑客技术
点击放大
OSRipper - AV evading cross platform Backdoor and Crypter Fra
项目说明
OSRipper v0.4.2
<di="center">
!OSRipper Logo
![CodeFactor]()
![Python ]()

![Platform]()
Ad cross-platform payload generator and crypter with FUD capabilities
Features • Quick Start • Web UI • Payload Types • Documentation
</div>
---
O
OSRipper is a sophisticated, fully undetectable (FUD) backdoor generator and crypter designed for authorized penetration testing and red team operations. It features ad e techniques, multiple payload types, and a modern web-based C2 interface for managing compromised systems.
Key Highlights
---
Features
Payload Generation
| Payload Type | Description | Use Case |
|-------------|-------------|----------|
| Bind Shell | Opens port on machine | Direct access when reverse connections blocked |
| Reverse TCP Meterpreter | SSL/TLS encrypted reverse connection | Standard penetration testing |
| DNS-o C2 | Stealthy DoH-based command & control | Bypass network restrictions |
| HTTPS C2 | Certificate-pinned HTTPS C2 | Secure, authenticated C2 channel |
| Staged Payload | Multi-stage web delivery | Enhanced stealth deployment |
| Custom Code Crypter | Obfuscate any Python script | Custom payload encryption |
E Techniques
Web UI Features
Ad Capabilities
---
Quick Start
Installation
Important — run setup for optional features (ngrok, binary compilation):
On many systems (especially Linux with an externally-managed Python en), you must run the built-in setup so optional dependencies are installed into OSRipper’s own venv. Do this once after installation:
This creates ~/.local/share/osripper/venv, installs pyngrok, nuitka, and sandboxed there, and all later runs of osripper / osripper-cli will use them automatically. Without this, --ngrok and --compile will prompt you to run setup. Use osripper-cli setup --system only if you prefer a system/user pip install instead of the venv.
Basic Usage
Interactive Mode:
Command Line:
Web UI:
---
Web UI
OSRipper includes a modern web-based C2 interface for managing compromised systems.
Features
Starting the C2 Server
Accessing the Web UI
Once the 服务端 is running, access the dashboard at:
---
Payload Types
1. Bind Shell Backdoor
Opens a port on the machine and waits for connections.
Connection:
2. Reverse TCP Meterpreter
Encrypted reverse connection with SSL/TLS.
3. DNS-o C2
Stealthy C2 channel using DNS-o 协议. Bypasses many 网络 restrictions.
Features:
4. HTTPS C2 (Certificate Pinning)
Secure HTTPS C2 with certificate pinning for authentication.
Features:
5. Staged Payload
Multi-stage web delivery for enhanced stealth.
6. Custom Code Crypter
Obfuscate and encrypt any Python script.
---
Command Line Interface
Common Options
| Option | Description |
|-------|-------------|
| --obfuscate | Enable multi-layer obfuscation |
| --enhanced | Enhanced obfuscation (anti-debug, ) |
| --compile | Compile to standalone binary |
| --icon PATH | Custom icon for compiled binary |
| --delay | Add random startup delay (5-15 seconds) |
| --output, -o NAME | Output filename |
| --quiet, -q | Quiet mode (minimal output) |
Examples
---
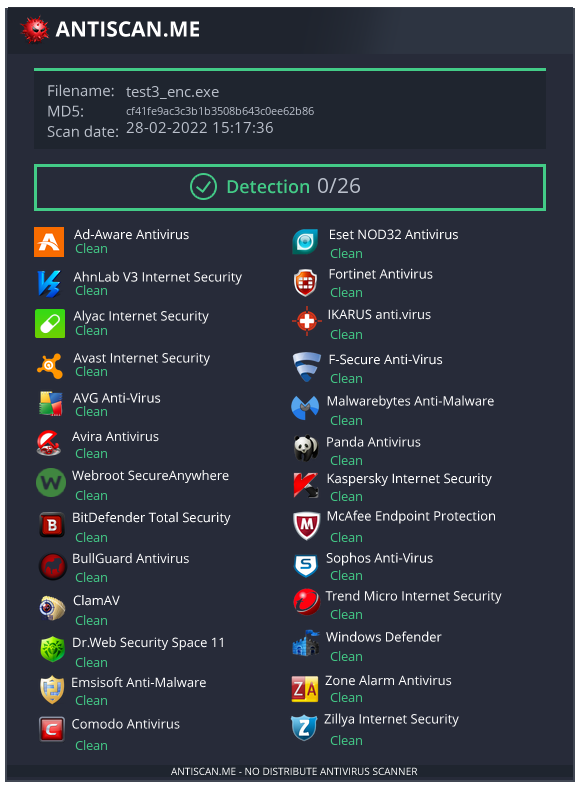
Detection Results
Latest Scans
antiscan result
!Antiscan Results
---
Architecture
---
Screenshots
Main Interface
Web UI Dashboard
!Web UI Dashboard
---
Ad Configuration
Ngrok Integration
Custom Icons
Obfuscation Levels
Standard Obfuscation:
Enhanced Obfuscation:
HTTPS C2 Setup
---
Documentation
---
Roadmap
Completed (v0.3.2)
In Progress
Future Plans
---
Contributing
We welcome contributions from the security research community!
How to Contribute
1. Fork the repository
2. Create a feature branch (git checkout -b feature/amazing-feature)
3. Commit your changes (git commit -m 'Add amazing feature')
4. Push to the branch (git push origin feature/amazing-feature)
5. Open a Pull Request
De Guidelines
---
Acknowledgments
Special thanks to the security research community and these projects:
---
Legal Disclaimer
IMPORTANT: This 工具 is de for educational purposes and authorized penetration testing only.
The de are not responsible for misuse of this software. Users must comply with all applicable laws and regulations.
---
Support
项目信息
开发语言:Python
Star 数:330
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A cross platform Backdoor and Crypter 框架 with a integrated lightweight webUI展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | OSRipper - AV evading cross platform Backdoor and Crypter Fra |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:19:02 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 255 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |