 黑客技术
点击放大
x64dbg - An open-source user mode debugger for Windows. Opt
项目说明
x64dbg
<img width="100" src="
![Crowdin]() ![Download x64dbg]() ![Ask DeepWiki]()
![Discord]() ![Slack]() ![Gitter]() ![Matrix]() ![IRC]()
An open-源码 binary debugger for Windows, aimed at malware analysis and reverse engineering of executables you do not have the 源码 代码 for. There are many features a and a comprehensive plugin system to add your own. You can find more information on the blog!
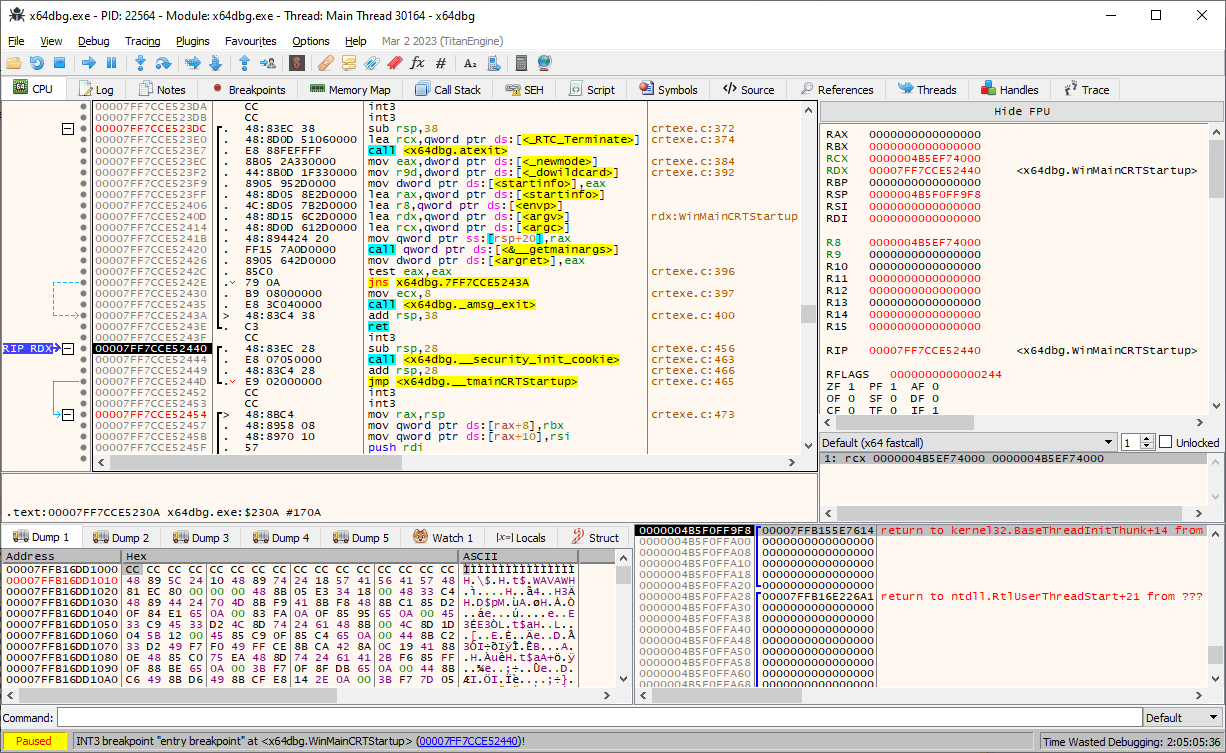
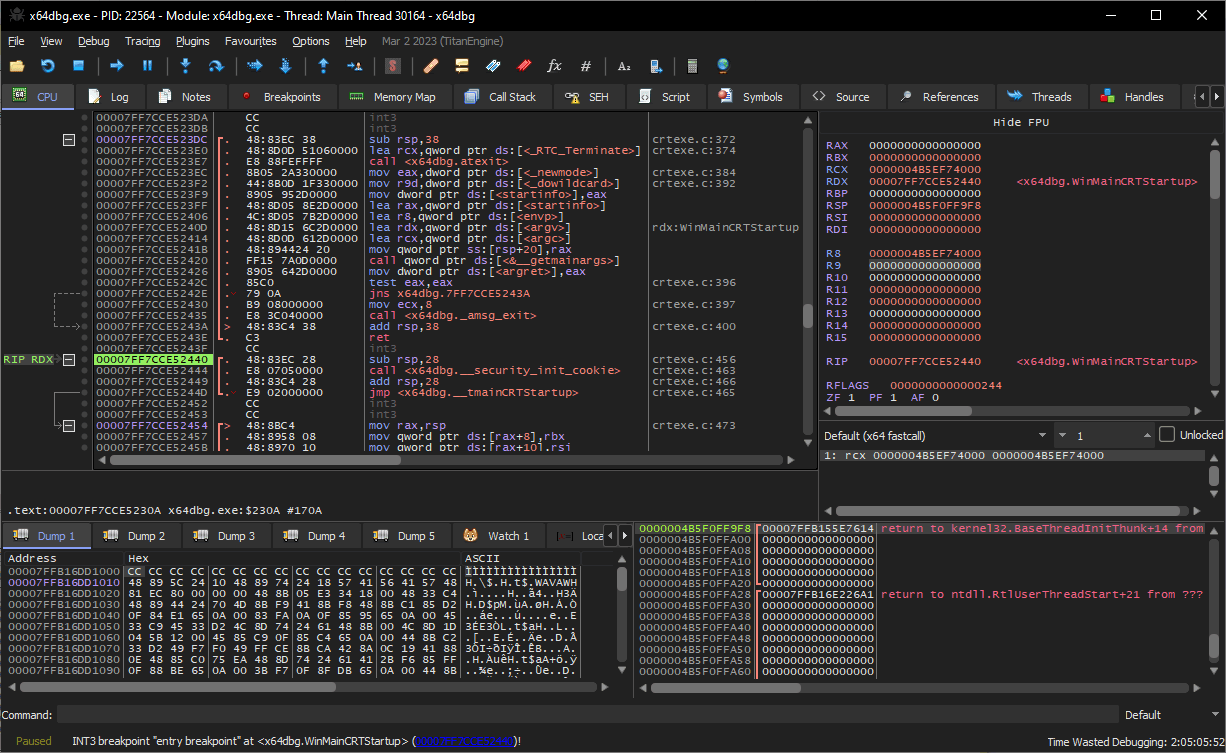
Screenshots
!main interface (light)
!main interface (dark)
| !graph | !memory map |
| :--: | :--: |
Installation & Usage
1. Download a snapshot from GitHub or SourceForge and extract it in a location your user has write access to.
2. _Optionally_ use x96dbg.exe to register a shell extension and add shortcuts to your desktop.
3. You can now run x32\x32dbg.exe if you want to debug a 32-bit executable or x64\x64dbg.exe to debug a 64-bit executable! If you are unsure you can always run x96dbg.exe and choose your architecture there.
You can also compile x64dbg yourself with a few easy steps!
Sponsors
<di="center" markdown="1">
<a href=" target="_blank">
<img alt="Warp sponsorship" width="400" src="
</a>
Warp, built for coding with multiple AI agents
<br>
![]()
</div>
Contributing
This is a community effort and we accept pull requests! See the CONTRIBUTING document for more information. If you have any questions you can always contact us or open an issue. You can take a look at the good first issues to get started.
Credits
De
Code contributions
You can find an exhaustive list of GitHub contributors here.
Special Thanks
Without the help of many people and other open-源码 projects, it would not have been possible to make x64dbg what it is today, thank you!
Historical Donors
Before fully transitioning to GitHub Sponsors, this project recei through BountySource. The original donation terms included an optional website link for donors who requested one at the time of donation. Links marked below reflect those requests. BountySource has since been shut down, so these records are reconstructed by hand. If you donated during this period and your username/amount is missing or incorrect, please reach out.
|Username|Amount|Date||Username|Amount|Date|
|-|-|-|-|-|-|-|
|sghctoma|$50|2015-04-19||dfrunza|$20|2017-01-30|
|o|$50|2015-04-25||ham3di|$100|2017-02-01|
|jl2id|$15|2015-04-29||johnny5|$5|2017-02-19|
|cypherpunk|$50|2015-05-02||Da|$90|2017-02-26|
|Aciid|$50|2015-05-05||Alexandro Sanchez Bach|-|2017-03-02|
|PI32|$15|2015-05-09||(unknown)|$6|2017-03-11|
|dark|$8|2015-05-21||fred26|$50|2017-04-08|
|fearless|$5|2015-05-24||gatesbillou|$20|2017-04-15|
|0x90|$10|2015-05-31||Da|$10|2017-04-24|
|acidflash|$50|2015-06-03||Adir|$20|2017-05-03|
||$10|2015-06-14||ferbeb|$10|2017-05-17|
|Artic|$10|2015-06-29||(unknown)|$16|2017-06-04|
|crystalidea|$24|2015-07-10||androsa|$20|2017-06-11|
|jl2id|$10|2015-08-13||robersor|$25|2017-07-05|
|PELock|$115|2015-08-26||DDSTrainers|$10|2017-07-15|
|tslater2006|$20|2015-09-04||blaquee|$20|2017-08-27|
|Exidous|$20|2015-09-04||SmilingWolf|$15|2017-09-26|
|lupier|$40|2015-09-08||Alexander H.|$150|2017-10-11|
|Stef|$10|2015-09-15||gatesbillou|$25|2017-10-14|
|d3|$5|2015-10-06||t4rmo|$5|2017-10-18|
|Artur|$20|2015-10-24||joelcornu|$5|2017-10-27|
|RoBa|$100|2015-11-18||Adir|$35|2017-11-02|
|mr.tuna7331|-|2015-12-15||(unknown)|$10|2017-11-11|
|lupier|$90|2016-01-12||xdeng|$10|2018-01-04|
|f|$10|2016-01-21||v-p-b|$50|2018-03-21|
|willi.neu9|$10|2016-01-30||EmptyBrain|$50|2018-03-30|
|rithien|$100|2016-02-19||mentebinaria|$19|2018-04-12|
|ey|$20|2016-02-26||Mauro Bollini|$50|2018-06-07|
|clockwork|$10|2016-03-06||gatesbillou|$15|2018-06-17|
|codespy|$5|2016-03-23||Kirbiflint|$3|2018-06-22|
|test|$100|2016-03-28||Chisato Rokumiya|$20|2018-09-20|
|RomanGol|$10|2016-03-28||pengchang|$100|2018-10-24|
|fearless|$10|2016-04-24||younsunmin|$5|2018-11-18|
|Jack|$5|2016-05-17||EmptyBrain|$50|2018-12-27|
|willi.neu9|$30|2016-05-26||Yim|$10|2019-01-13|
|gatesbillou|$20|2016-06-02||OALabs|-|2019-01-27|
|AGI|$155|2016-06-16||Lixinist|$10|2019-04-15|
|lupier|$100|2016-06-24||bloodmc|$50|2019-04-29|
|0x90|$50|2016-07-19||(unknown)|$20|2019-05-24|
|tr4nc3|$15|2016-07-31||masacate|$10|2019-07-10|
|MikeGuidry|$2500|2016-07-31||User Manuals|$5|2020-01-20|
|Alexander H.|$150|2016-09-09||Jim Conyngham|$50|2020-03-23|
|dark|$10|2016-10-04||Danya|$5|2020-06-08|
|h907308901|$5|2016-10-06||RooT|$160|2020-07-22|
|Adir|$20|2016-10-24||jadakiss9018|$2|2020-09-11|
|NicoG|$100|2016-10-27||samsonpianofingers|$15|2020-09-14|
|Angie|$150|2016-11-03||tpericin|$1337|2020-10-09|
|hulucc|$20|2016-12-02||nikkej|$100|2020-10-22|
|napcode|$10|2016-12-05||kha1ifaa|$10|2021-01-04|
|TechLord|-|2016-12-26||rikaardhosein|$20|2021-09-08|
|ayylmao5|$5|2017-01-01||Lukas21|$50|2021-09-15|
|affelwafro|$10|2017-01-03||Fla|$30|2021-12-01|
|FS|$40|2017-01-15||ste|$1000|2021-12-03|
|EmptyBrain|$50|2017-01-27||ethical.blue|$19|2022-05-14|
_To all our early supporters: thank you for believing in this project before it became what it is today!_
项目信息
开发语言:C++
Star 数:49691
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An open-源码 user mode debugger for Windows. Optimized for reverse engineering and malware analysis.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | x64dbg - An open-source user mode debugger for Windows. Opt |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:28:17 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 107 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |