 黑客技术
点击放大
bettercap - The Swiss Army knife for 802.11, BLE, HID, CAN-bus
项目说明
<p align="center">
<small>Join the project community on our 服务端!</small>
<br/><br/>
<a href=" target="_blank" title="Join our community!">
<img src="
</a>
</p>
<hr/>
<p align="center">
<img alt="BetterCap" src=" height="140" />
<p align="center">
<a href=" alt="Release" src="
<a href=" alt="Software License" src="
<a href=" alt="Tests on Linux" src="
<a href=" alt="Tests on macOS" src="
<a href=" alt="Tests on Windows" src="
<a href=" alt="Docker Hub" src="
<img src=" alt="This project is 100% made by humans."/>
</p>
</p>
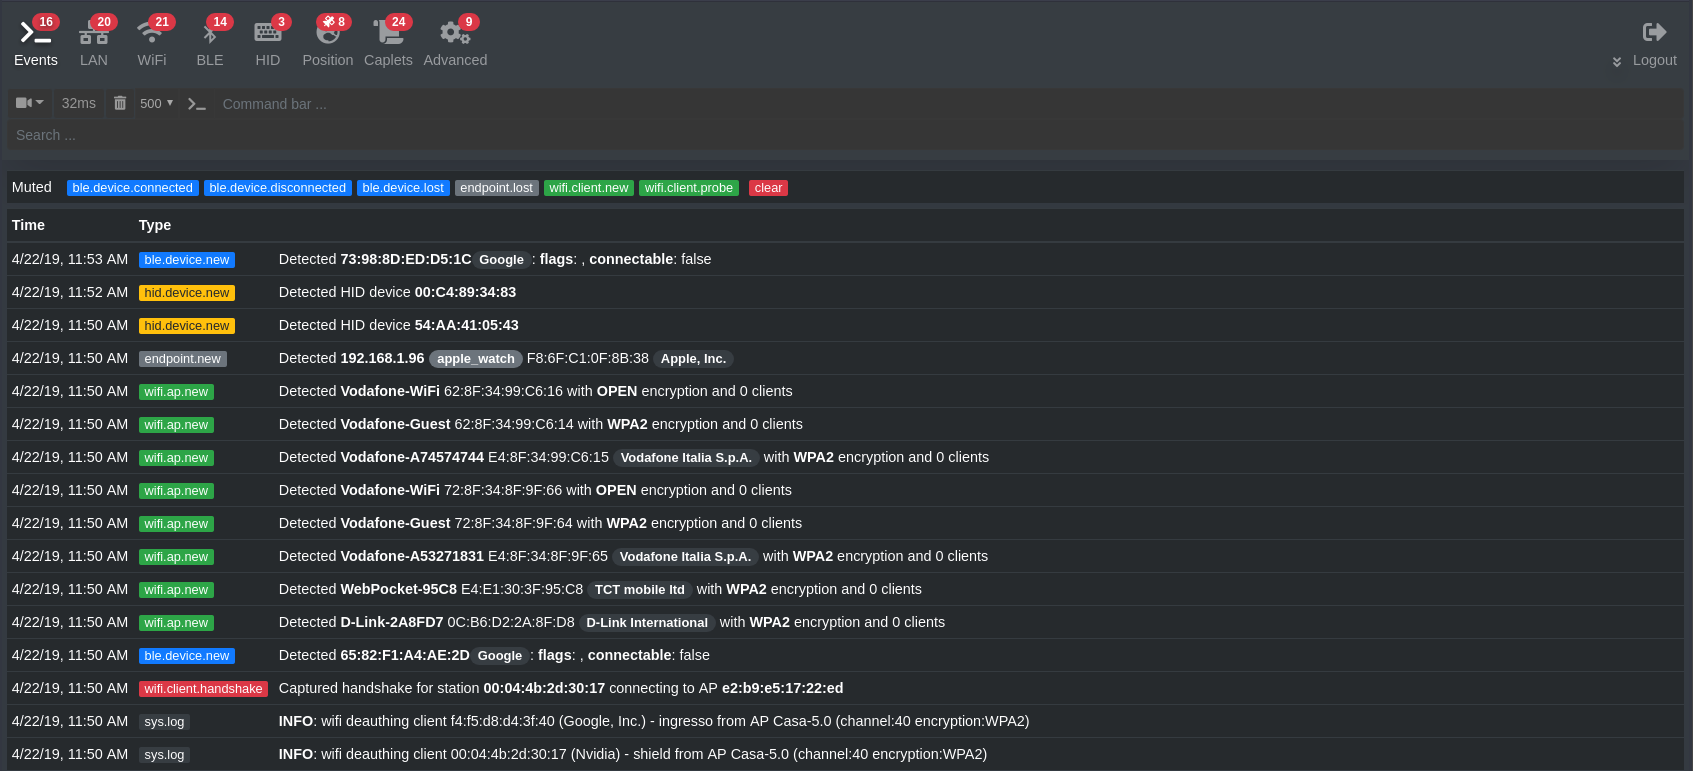
bettercap is a powerful, easily extensible and portable 框架 written in Go which aims to offer to security researchers, red teamers and reverse engineers an easy to use, all-in-one solution with all the features they might possibly need for performing reconnaissance and attacking WiFi networks, Bluetooth Low Energy devices, CAN-bus, wireless HID devices and Ethernet networks.
!UI
Main Features
* WiFi networks scanning, deauthentication attack, clientless PMKID association attack and automatic WPA/WPA2/WPA3 客户端 handshakes capture.
* Bluetooth Low Energy devices scanning, characteristics enumeration, reading and writing.
* 2.4Ghz wireless devices scanning and MouseJacking attacks with o HID frames injection (with DuckyScript support).
* CAN-bus and DBC support for decoding, injecting and fuzzing frames.
* Passive and active IP 网络 hosts probing and recon.
* ARP, DNS, NDP and DHCPv6 spoofers for MITM attacks on IPv4 and IPv6 based networks.
* Proxies at packet level, TCP level and HTTP/HTTPS application le scriptable with easy to implement ja plugins.
* A powerful network sniffer for credentials har which can also be used as a network protocol fuzzer.
* A very fast port scanner.
* A powerful REST API with support for asynchronous events notification on websocket to orchestrate your attacks easily.
* A very con web UI.
* More!
Contributors
<a href="
<img src=" alt="bettercap project contributors" />
</a>
License
bettercap is made with ♥ and released under the GPL 3 license.
Stargazers over time
![Stargazers over time]()
项目信息
开发语言:Go
Star 数:20097
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | bettercap - The Swiss Army knife for 802.11, BLE, HID, CAN-bus |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:28:36 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 226 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |