 安全软件
点击放大
Raccoon - A high performance offensive security tool for rec
项目说明
Raccoon
!Racoon
#### Offensi 工具 for Reconnaissance and Information Gathering
!Build Status
!license
!os
!pythonver
!raccoonver
##### Features
certificate details and SANs
SAN discovery and bruteforce
- CMS detection
- Web server info and X-Powered-By
- robots.txt and sitemap extraction
- Cookie inspection
- Extracts all fuzzable URLs
- Discovers HTML forms
- Retrieves all Email addresses
- Scans target for S3 buckets and enumerates them
for sensiti
and modules by files
##### Roadmap and TODOs
About
Raccoon is a 工具 made for reconnaissance and information gathering with an emphasis on simplicity.<br> It will do e from
fetching DNS records, retrieving WHOIS information, obtaining TLS data, detecting WAF presence and up to threaded dir busting and
subdomain enumeration. Every scan outputs to a corresponding file.<br>
As most of Raccoon's scans are independent and do not rely on each other's results,
it utilizes Python's asyncio to run most scans asynchronously.<br>
Raccoon supports Tor/proxy for anonymous routing. It uses default wordlists (for URL fuzzing and subdomain discovery)
from the amazing SecLists repository but different lists can be passed as arguments.<br>
For more options - see "Usage".
Installation
For the latest stable :<br>
Please note Raccoon requires Python3.5+ so may need to use pip3 install raccoon-scanner.<br>
You can also clone the GitHub repository for the latest features and changes:<br>
#### macOS
To support Raccoon on macOS you need to ha on your machine.<br>
gtimeout can be installed by running brew install coreutils.
#### Docker<br>
##### Prerequisites
Raccoon uses Nmap to scan ports as well as utilizes some other Nmap scripts
and features. It is mandatory that you have it installed before running Raccoon.<br>
OpenSSL is also used for TLS/SSL scans and should be installed as well.
Usage
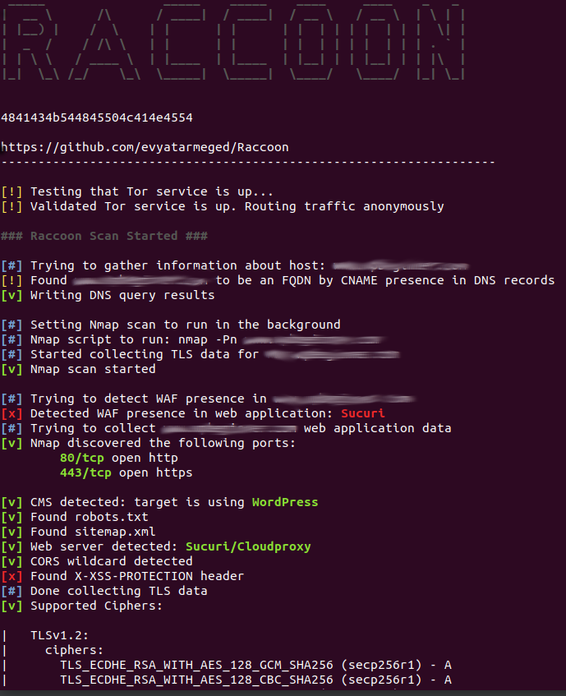
Screenshots
!poc2<br>
Web application data including S3 bucket:<br>
!somepoc
HTB challenge example scan:<br>
!poc<br>
Nmap scan results:<br>
!<br>
Results folder tree after a scan:<br>
!poc3
Contributing
Any and all contributions, issues, features and tips are welcome.
项目信息
开发语言:Python
Star 数:4039
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A high performance offensive security 工具 for reconnaissance and vulnerability scanning展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Raccoon - A high performance offensive security tool for rec |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:28:54 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 314 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |