 黑客技术
点击放大
awesome-shodan-queries - 🔍 A collection of interesting, funny, and depressi
项目说明
Awesome Shodan Search Queries ![Awesome]()
Over time, I' an assortment of interesting, funny, and depressing search queries to plug into Shodan, the (literal) internet search 引擎. Some return facepalm-inducing results, while others return serious and/or ancient in the wild.
<p align="center">
<img src="screenshots/shodan.png" /><br />
<strong><a href=" search filters require a Shodan account.</a></strong>
</p>
You can assume these queries only return unsecured/open instances when possible. For your own legal benefit, do not attempt to login (even with default passwords) if they aren't! Narrow down results by adding filters like country:US or org:"Harvard Uni" or hostname:"nasa.gov" to the end.
The world and its devices are quickly becoming more connected through the shiny new Internet of ~~Things~~ Sh*t — and exponentially more dangerous as a result. To that end, I hope this list spreads awareness (and, quite frankly, pant-wetting fear) rather than harm.
And as always, discover and disclose responsibly! 🤓
---
Table of Contents
---
Industrial Control Systems
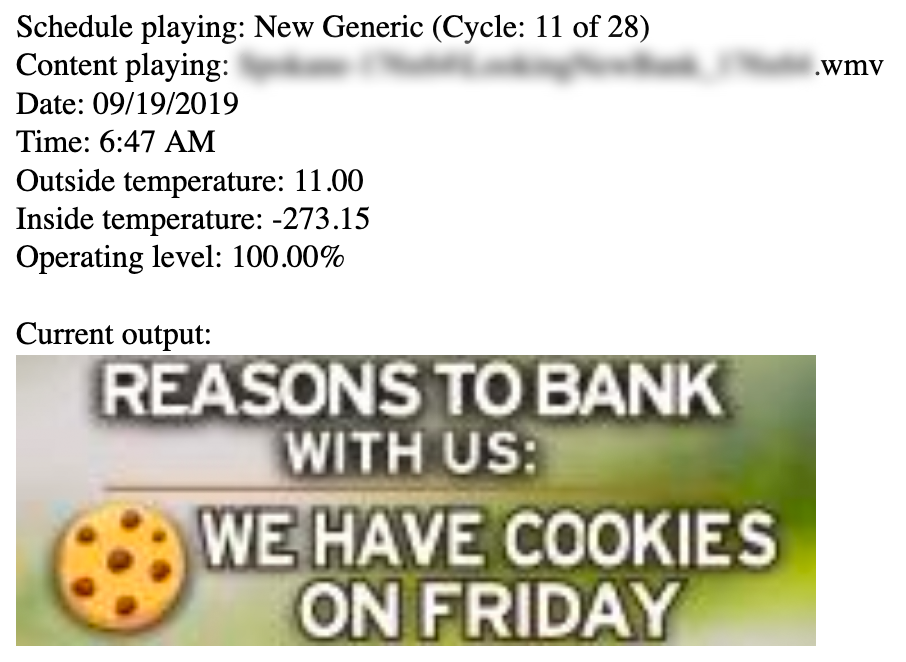
Samsung Electronic Billboards 🔎 →
<di="center"><img src="screenshots/billboard3.png" alt="Example: Electronic Billboards" width="500" /></div>
Gas Station Pump Controllers 🔎 →
<di="center"><img src="screenshots/7-11.png" alt="Example: Gas Station Pump In" width="700" /></div>
Automatic License Plate Readers 🔎 →
<di="center"><img src="screenshots/plate-reader.png" alt="Example: Automatic License Plate Reader" /></div>
Traffic Light Controllers / Red Light Cameras 🔎 →
Machines in the United States 🔎 →
Telcos Running Cisco Lawful Intercept Wiretaps 🔎 →
Wiretapping mechanism outlined by Cisco in RFC 3924:
> Lawful intercept is the lawfully authorized interception and monitoring of communications of an intercept subject. The term "intercept subject" [...] refers to the subscriber of a telecommunications service whose communications and/or intercept related information (IRI) has been lawfully authorized to be intercepted and delivered to some agency.
Prison Pay Phones 🔎 →
Tesla PowerPack Charging Status 🔎 →
<di="center"><img src="screenshots/tesla.png" alt="Example: Tesla PowerPack Charging Status" /></div>
Electric Chargers 🔎 →
Maritime Satellites 🔎 →
Shodan made a pretty sweet Ship Tracker that maps ship locations in real time, too!
<di="center"><img src="screenshots/sailor-vsat.png" alt="Example: Maritime Satellites" width="700" /></div>
Submarine Mission Control Dashboards 🔎 →
CAREL PlantVisor Refrigeration Units 🔎 →
<di="center"><img src="screenshots/refrigeration.png" alt="Example: CAREL PlantVisor Refrigeration Units" /></div>
Nordex Wind Turbine Farms 🔎 →
C4 Max Commercial GPS Trackers 🔎 →
<di="center"><img src="screenshots/c4max.png" alt="Example: C4 Max GPS" width="780" /></div>
DICOM Medical X-Ray Machines 🔎 →
Secured by default, thankfully, but these 1,700+ machines still have no business being on the internet.
GaugeTech Electricity Meters 🔎 →
<di="center"><img src="screenshots/power-gaugetech.png" alt="Example: GaugeTech Electricity Meters" width="650" /></div>
Siemens Industrial Automation 🔎 →
Siemens H 🔎 →
Door / Lock Access Controllers 🔎 →
Railroad Management 🔎 →
---
Remote Desktop
Unprotected VNC 🔎 →
Shodan Images is a great supplementary 工具 to browse screenshots, by the way! 🔎 →
<p align="center">
<img src="screenshots/vnc.png" alt="Example: Unprotected VNC" /><br />
<em>The first result right now. 😞</em>
</p>
Windows RDP 🔎 →
99.99% are secured by a secondary Windows login screen.
---
Network Infrastructure
Wea Dashboards 🔎 →
Command-line access inside Kubernetes pods and Docker containers, and real-time /monitoring of the entire infrastructure.
<di="center"><img src="screenshots/wea.png" alt="Example: Wea Dashboards" /></div>
MongoDB 🔎 →
Older were insecure by default. Very scary.
<di="center"><img src="screenshots/mongo.png" alt="Example: MongoDB" width="500" /></div>
Mongo Express Web GUI 🔎 →
Like the infamous phpMyAdmin but for MongoDB.
<di="center"><img src="screenshots/mongo-express.png" alt="Example: Mongo Express 界面" width="700" /></div>
Jenkins CI 🔎 →
<di="center"><img src="screenshots/jenkins.png" alt="Example: Jenkins CI" width="700" /></div>
Docker APIs 🔎 →
Docker Private Registries 🔎 →
Pi-hole Open DNS Servers 🔎 →
Already Logged-In as root 🔎 →
Android Root Bridges 🔎 →
A tangential result of Google's sloppy fractured update approach. 🙄 More information here.
Lantronix Serial-to-Ethernet Adapter Leaking Telnet Passwords 🔎 →
Citrix Apps 🔎 →
<di="center"><img src="screenshots/citrix.png" alt="Example: Citrix Apps" width="700" /></div>
Cisco Smart Install 🔎 →
(kind of "by design," but especially when exposed).
PBX IP Phone Gateways 🔎 →
Polycom Video Conferencing 🔎 →
Telnet Configuration: 🔎 →
<di="center"><img src="screenshots/polycom.png" alt="Example: Polycom Video Conferencing" /></div>
Bomgar Help Desk Portal 🔎 →
Intel Acti C 🔎 →
HP iLO 4 C 🔎 →
Outlook Web Access:
#### Exchange 2007 🔎 →
<di="center"><img src="screenshots/owa2007.png" alt="Example: OWA for Exchange 2007" width="400" /></div>
#### Exchange 2010 🔎 →
<di="center"><img src="screenshots/owa2010.png" alt="Example: OWA for Exchange 2010" width="400" /></div>
#### Exchange 2013 / 2016 🔎 →
<di="center"><img src="screenshots/owa2013.png" alt="Example: OWA for Exchange 2013/2016" width="500" /></div>
Lync / Skype for Business 🔎 →
---
Network Attached Storage (NAS)
SMB (Samba) File Shares 🔎 →
Produces ~500,000 results...narrow down by adding "Documents" or "", etc.
Specifically domain controllers: 🔎 →
Concerning default 网络 shares of QuickBooks files: 🔎 →
FTP Servers with Anonymous Login 🔎 →
Iomega / LenovoEMC NAS Drives 🔎 →
<di="center"><img src="screenshots/iomega.png" alt="Example: Iomega / LenovoEMC NAS Drives" width="600" /></div>
Buffalo TeraStation NAS Drives 🔎 →
<di="center"><img src="screenshots/buffalo.png" alt="Example: Buffalo TeraStation NAS Drives" width="600" /></div>
Logitech Media Servers 🔎 →
<di="center"><img src="screenshots/logitech.png" alt="Example: Logitech Media Servers" width="500" /></div>
Plex Media Servers 🔎 →
Tautulli / PlexPy Dashboards 🔎 →
<di="center"><img src="screenshots/plexpy.png" alt="Example: PlexPy / Tautulli Dashboards" width="570" /></div>
---
Webcams
Example images not necessary. 🤦
Yawcams 🔎 →
webcamXP/webcam7 🔎 →
Android IP Webcam Server 🔎 →
Security DVRs 🔎 →
---
Printers & Copiers:
HP Printers 🔎 →
<di="center"><img src="screenshots/hp.png" alt="Example: HP Printers" width="650" /></div>
Xerox Copiers/Printers 🔎 →
<di="center"><img src="screenshots/xerox.png" alt="Example: Xerox Copiers/Printers" width="550" /></div>
Epson Printers 🔎 →
<di="center"><img src="screenshots/epson.png" alt="Example: Epson Printers" width="500" /></div>
Canon Printers 🔎 →
<di="center"><img src="screenshots/canon.png" alt="Example: Canon Printers" width="500" /></div>
---
Home Devices
Yamaha Stereos 🔎 →
<di="center"><img src="screenshots/yamaha.png" alt="Example: Yamaha Stereos" width="500" /></div>
Apple AirPlay Receivers 🔎 →
Apple T, etc.
Chromecasts / Smart TVs 🔎 →
Crestron Smart Home Controllers 🔎 →
---
Random Stuff
OctoPrint 3D Printer Controllers 🔎 →
<di="center"><img src="screenshots/octoprint.png" alt="Example: OctoPrint 3D Printers" width="740" /></div>
Etherium Miners 🔎 →
<di="center"><img src="screenshots/eth.png" alt="Example: Etherium Miners" /></div>
Apache Directory Listings 🔎 →
Substitute .pem with any extension or a filename like phpinfo.php.
Misconfigured WordPress 🔎 →
Exposed wp-config.php files containing database credentials.
Too Many Minecraft Servers 🔎 →
Literally E in North Korea 🇰🇵 🔎 →
TCP Quote of the Day 🔎 →
Port 17 (RFC 865) has a bizarre history...
Find a Job Doing This! 👩💼 🔎 →
---
If you' any other juicy Shodan gems, whether it's a search query or a specific example, definitely drop a comment on the blog or open an issue/PR here on GitHub.
Bon , fellow penetrators! 😉
License
![CC0]()
To the extent possible under law, Jake Jarvis has waived all copyright and related or neighboring rights to this work.
Mirrored from a blog post at
项目信息
开发语言:未知
Star 数:7764
技术要点
该项目属于黑客技术方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🔍 A collection of interesting, funny, and depressing search queries to plug into shodan.io 👩💻展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | awesome-shodan-queries - 🔍 A collection of interesting, funny, and depressi |
| 所属分类 | 黑客技术 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:29:42 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 239 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |