 安全软件
点击放大
open-kritt - Open-source, self-hosted AI vulnerability research
项目说明
<di="center">
<picture>
<源码 media="(prefers-color-scheme: dark)" srcset="docs/images/logo-dark.png" />
<img alt="open·kritt" src="docs/images/logo-light.png" width="96" height="96" />
</picture>
open·kritt
Orchestrate AI agents to find real in 代码.
An open-源码, self-hosted security and research platform that turns
focused AI analysis into de-duplicated, ranked findings with configurable and
enrichment.

![Release]()
Website ·
Documentation ·
Getting started ·
Contributing ·
Owners ·
Research paper
<a href=" alt="Join the open·kritt Discord community" src=" /></a>
<a href=" alt="Follow Kritt on X" src=" /></a>
</div>
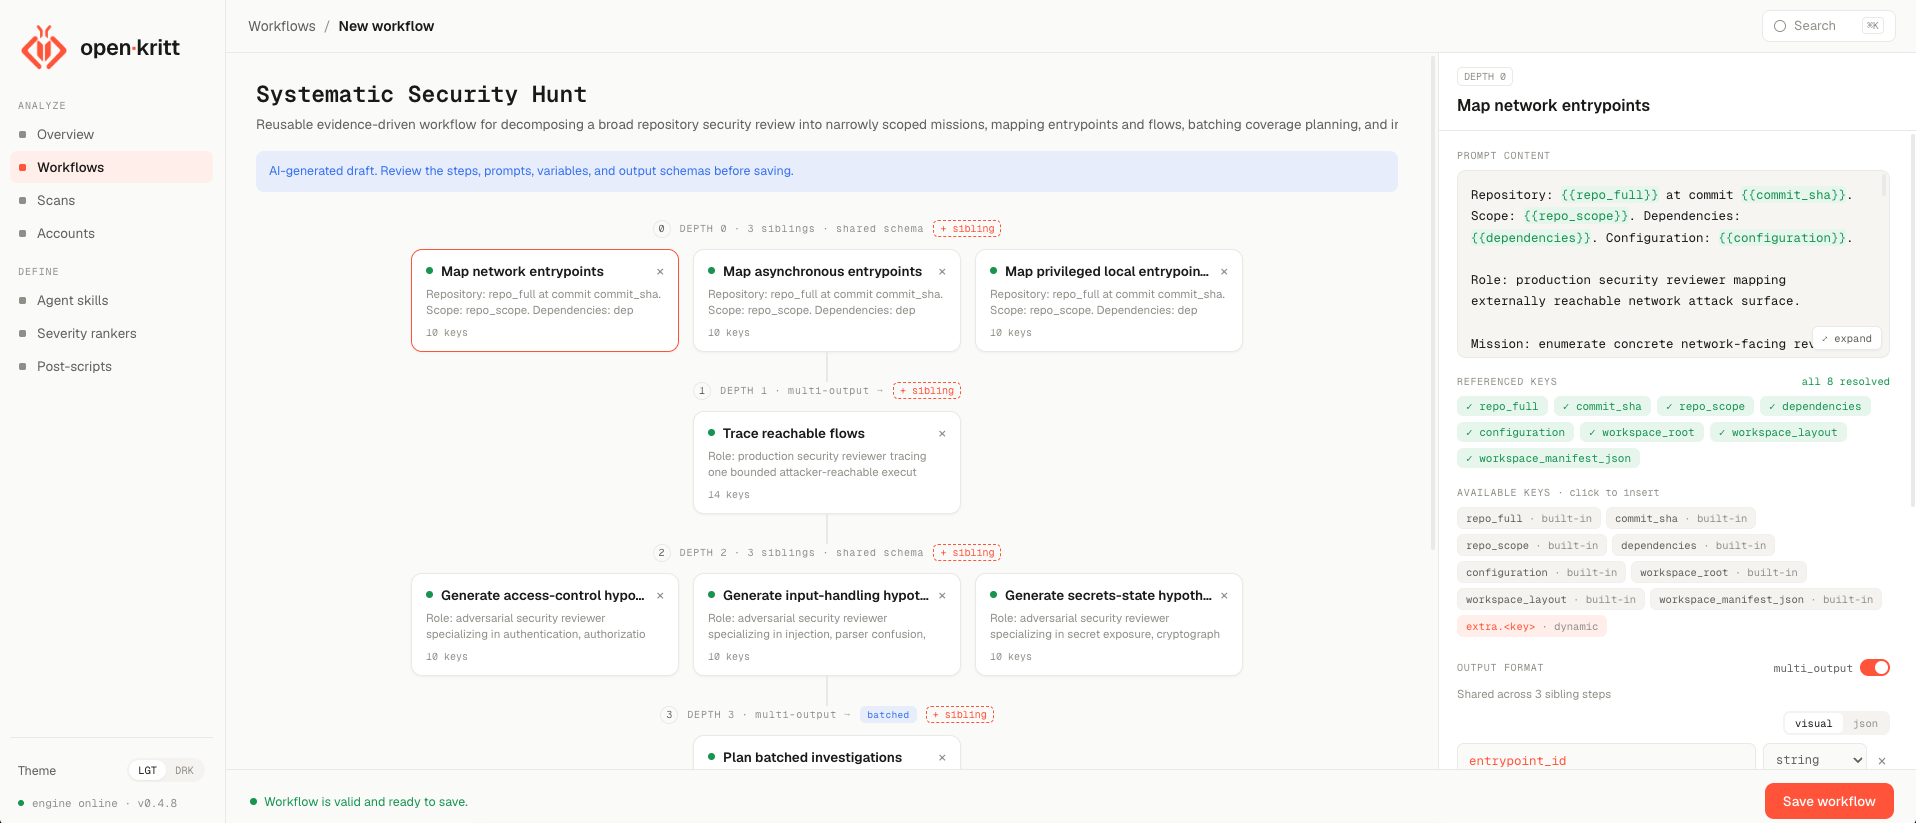
!open·kritt workflow builder
What is open·kritt?
Pointing a model at an entire repository and asking it to find rarely
works well. open·kritt takes a focused approach: break the research into small,
well-defined tasks, run them across AI agents in parallel, and combine their output into
findings you can and prioritize.
It is built for security researchers and security-minded de who want control
o prompts, workflows, model pro, and infrastructure.
What it does
Claude Code, or Grok Build.
produce reports.
output, reports, and proofs of concept in one ZIP archive with a share-safe manifest;
completed scans produce complete exports, while stopped or failed scans with findings
produce clearly marked partial exports. Attacker-influenced report and PoC 源码 is
kept as plain text.
and automatic de-duplication.
Anthropic, DeepSeek, OpenRouter, or xAI.
> Built from real security research. The Kritt team has earned over **$1,500,000 in
> bug-bounty payouts under the researcher name Blockian**
> (Immunefi ·
> HackenProof ·
> blockian.xyz · ).
> open·kritt is the open-源码 distillation of the internal project behind that work.
Getting started
You need Git, Docker with Docker Compose, and Node.js 20 or newer. The repository-local
CLI has no install step.
Open once the stack is running. You only
need one model-access option; ./kritt setup guides you through the a logins and
API keys. A GITHUB_TOKEN is optional and only needed for private GitHub repositories.
On a ser a browser or desktop, leave the stack running and open another shell:
The headless CLI imports portable workflow, post-script, skill, and ranker JSON; creates
scans with the same backend as the web form; displays scan status, stages, and
failure reasons; edits non-secret runtime settings; and exports finding bundles. It does
not display finding contents in the terminal. See the
headless CLI guide.
The default ports bind to 127.0.0.1, and the backend does not include application
authentication. Keep the stack private.
工具-enabled agents run as root inside disposable job containers, with writable repository
copies and direct internet access so they can install tools, compile targets, run tests,
and build proofs of concept. Run open·kritt on a dedicated Docker host or VM; see the
threat model before scanning untrusted 代码.
For prerequisites, manual Docker setup, and pro instructions, read the
installation guide and
AI provider setup.
In Accounts, use the persisted Active switch to choose which accounts may receive
new assignments while keeping other credentials saved. See acti accounts.
Documentation
Preview the documentation locally with Mint:
Open to view the site.
Community and contributing
open·kritt is jointly owned and maintained by
Harel Rom (-coffee) and
Gabriel Balko (). See
project ownership and copyright for details.
Questions and ideas belong in GitHub Discussions.
Use GitHub Issues for bugs and feature
requests.
Contributions are welcome. Read CONTRIBUTING.md for the de
setup, test commands, and Con Commit requirements.
Please report security pri by following SECURITY.md, not through a public issue.
License
open·kritt is licensed under the GNU Affero General Public License v3.0.
项目信息
开发语言:JavaScript
Star 数:2212
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Open-源码, self-hosted AI vulnerability research 工具 that orchestrates agents to find and validate security issues in 代码.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | open-kritt - Open-source, self-hosted AI vulnerability research |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:29:53 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 114 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |