 安全软件
点击放大
OpenOSINT - AI-powered OSINT agent with interactive REPL, MCP
项目说明
mcp-name: io.github.OpenOSINT/openosint
<di="center">
<img src=" alt="OpenOSINT" width="200" />
<h1>OpenOSINT</h1>
<p>An OSINT (Open 源码 Intelligence) agent for security researchers and analysts: 20 in tools behind a natural-language interface, plus an MCP (Model Context 协议) 服务端 so any MCP-compatible AI 客户端 can drive them directly.</p>
<p>Use it as a REPL, CLI, MCP 服务端, or browser Web UI.</p>
<p><em>The AI issues hard-stop 工具 calls; your 代码 executes the real binary — hallucinated findings are structurally impossible.</em></p>
</div>
<di="center">
![Release]()
![PyPI]()
![PyPI downloads]()

![MCP]()
![MCP Registry]()
![Sponsored by IP2Location]()
![Sponsored by RapidProxy]()
![Sponsored by TestMu AI]()
</div>
Self-host (free, MIT)
<di="center">
<a href="
<img src="
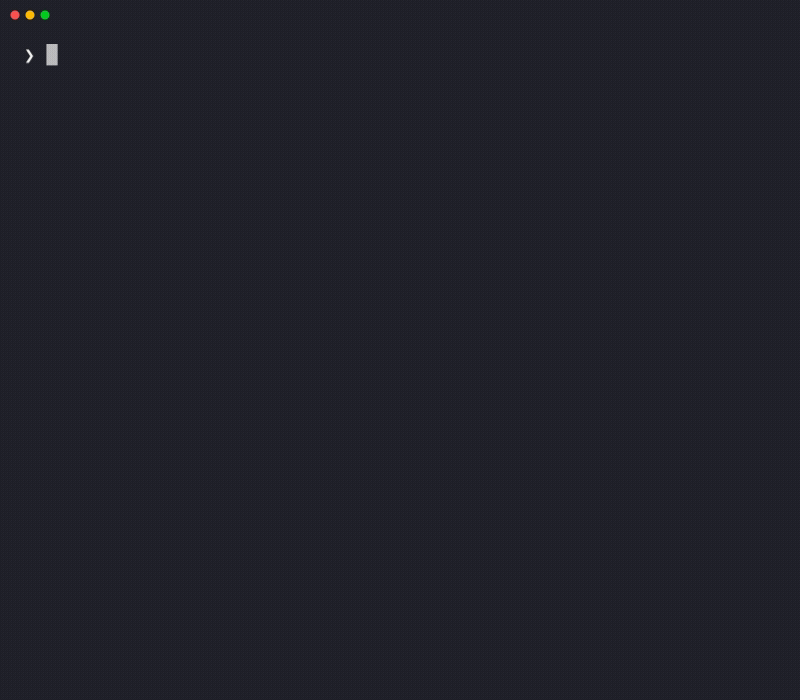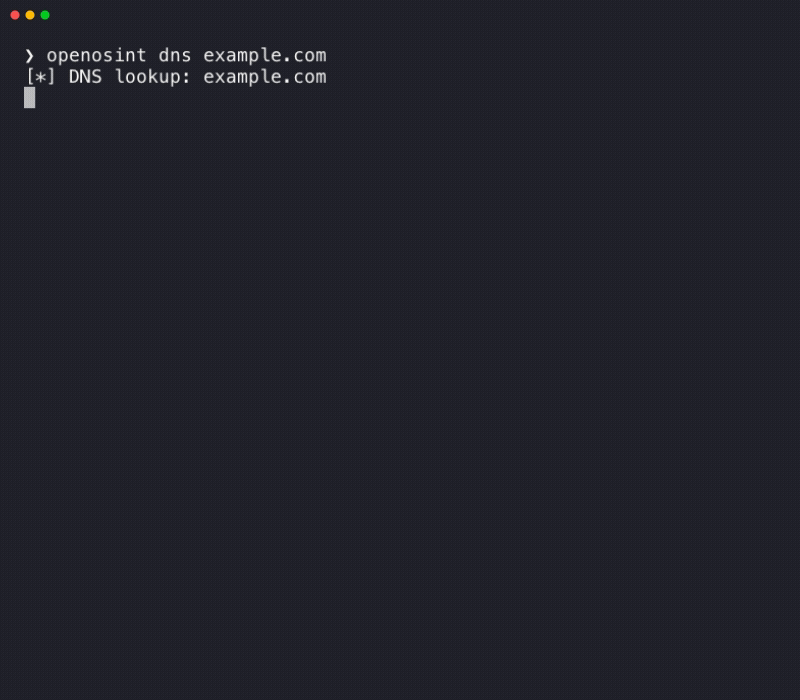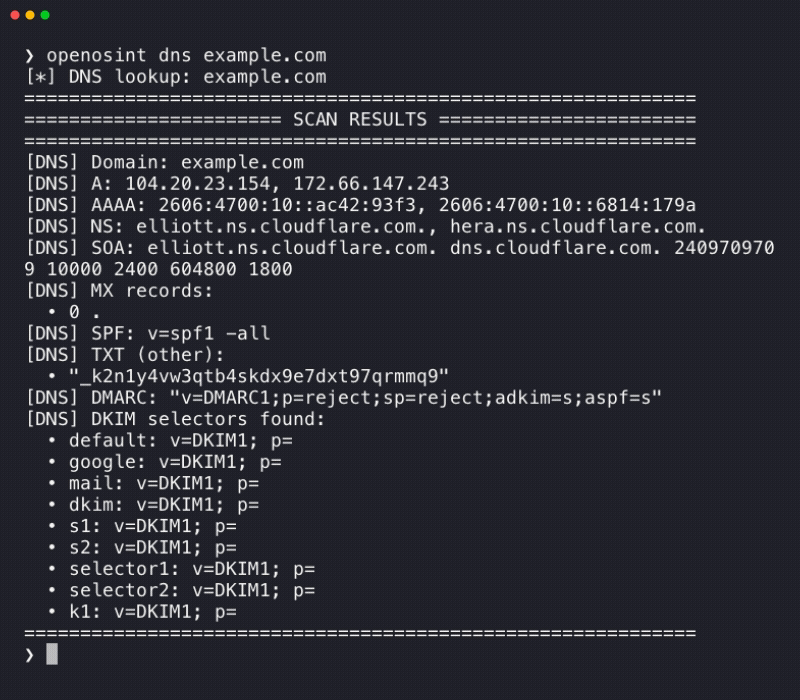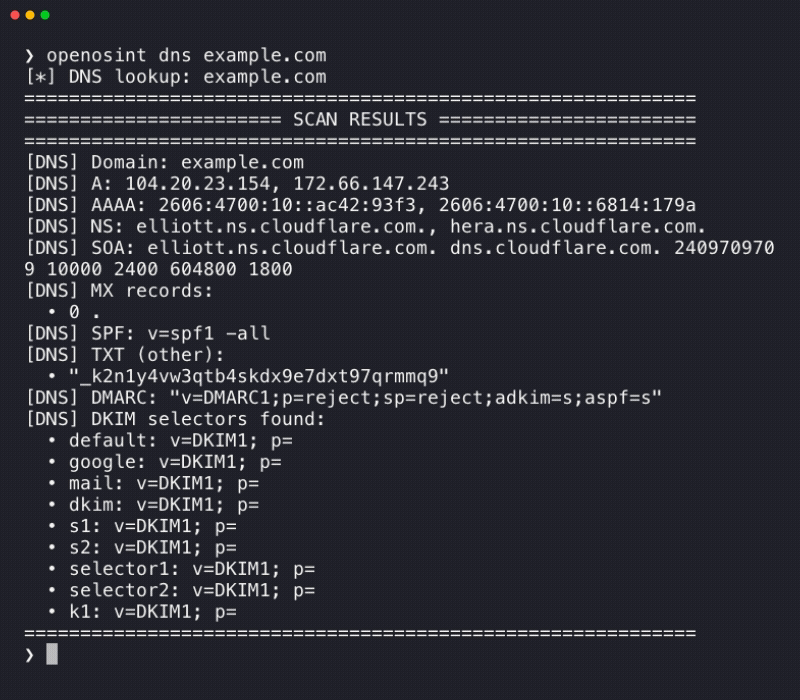
alt="OpenOSINT running a DNS lookup and returning records in under two seconds"
width="800" />
</a>
</div>
Try the live demo → — bring your own Anthropic / OpenRouter / Ollama key, no signup.
☁️ OpenOSINT Cloud — no install, pay per use
Run OpenOSINT tools with zero install as pay-per-use Apify Actors, in your browser or as MCP tools in Claude, Cursor, and Windsurf.
| Actor | Input | Output | Price | |
|---|---|---|---|---|
| OpenOSINT Email Recon | an email address | linked accounts across 100+ services | from $0.015/run | ▶ Run on Apify |
| OpenOSINT Username Recon | one or more usernames | every platform where each is registered | $0.04/username | ▶ Run on Apify |
| OpenOSINT Domain Recon | one or more domains | A-F email-security grade, RDAP data, dork URLs | $0.02/domain | ▶ Run on Apify |
<!-- Add one row per new Actor here as they ship -->
All three are also a as MCP tools with no 服务端 to run:
Cloud or self-host? Cloud: zero setup, pay per call, hosted by us — cloud usage funds ongoing de of the self-hosted project. Self-host: free forever, your own API keys, full control.
📬 Agents & OSINT — the newsletter
One AI-OSINT workflow you can run + a ruthless roundup of what's new, every week.
Subscribe →
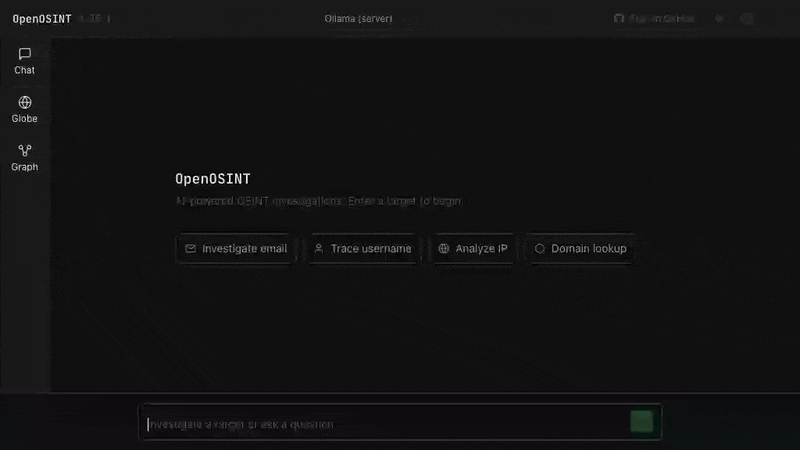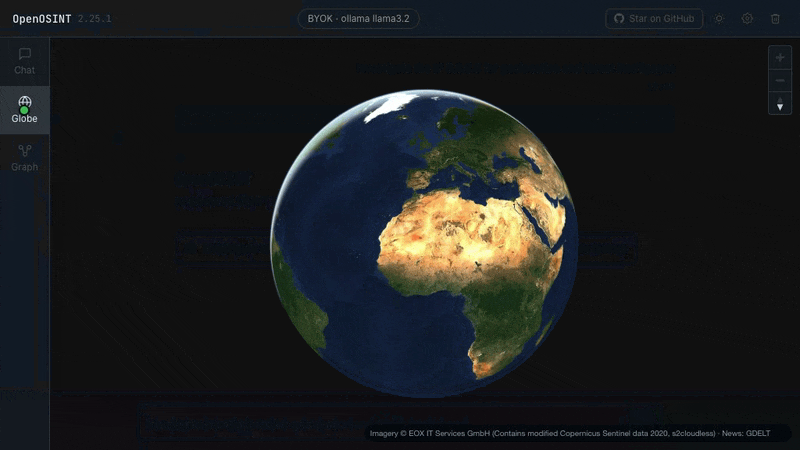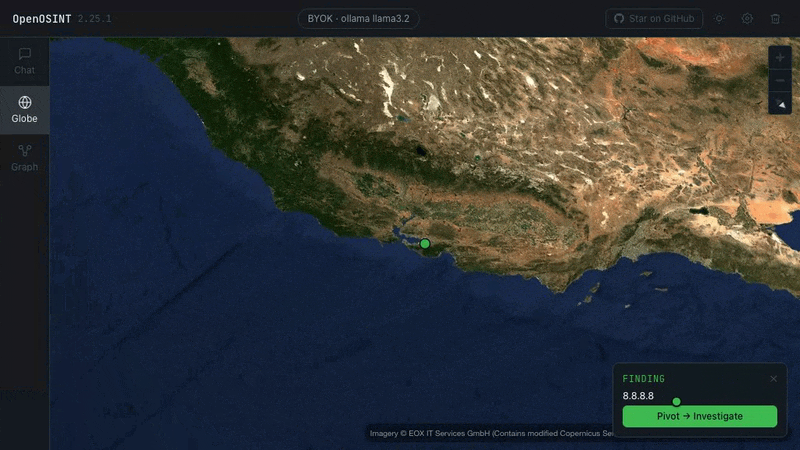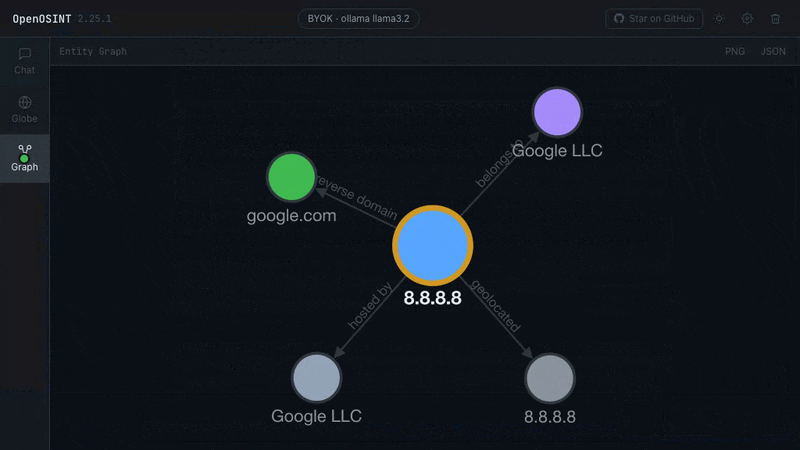
!OpenOSINT globe view: an agent in triggered from a chat prompt lands as a point on an interactive 3D globe, clicking the point pivots into a follow-up in, and the new entity appears in the entity graph
*In results land live on the globe — click a point to pivot. Watch the sharper MP4.*
<di="center">
<img src="
alt="Graph web UI demo (synthetic data): the entity graph explorer shows two Organization nodes obser by the openosint:github and openosint:whois datasets, linked by a dashed same_as candidate edge scored 0.83; clicking a node opens a side panel listing each statement with its dataset, extractor, run id, and confidence; clicking the dashed edge opens the human review card comparing both entities field by field — matching green, differing amber — with the name-match feature explanation that produced the score; the re clicks Accept and the graph updates in place: the pair clusters and the edge becomes a solid same_as check"
width="900" />
<p><em>Deterministic, synthetic-data demo — every entity shown is fictional; regenerate with <a href="demo/web_demo.py">demo/web_demo.py</a>.<br>
The entities are seeded at the statement layer, not produced by today's mappers — see <a href="demo/README.md">demo/README.md</a>.</em></p>
</div>
<!-- SPONSORS:START -->
Featured Integrations
<a href=" rel="noopener sponsored"><img src=" alt="IP2Location.io logo" height="40"></a>
IP2Location.io — powers search_ip2location · Integration guide
> Enhanced IP geolocation, ISP, /Tor, and datacenter detection
<a href=" rel="noopener sponsored"><picture><源码 media="(prefers-color-scheme: dark)" srcset=" src=" alt="RapidProxy logo" width="400"></picture></a>
RapidProxy · Integration guide
> Reliable Residential Proxies for Data Collection & Automation — 90M+ IPs across 200+ countries. 10% off: RAPID10.
<a href=" rel="noopener sponsored"><picture><源码 media="(prefers-color-scheme: dark)" srcset=" src=" alt="TestMu AI logo" width="353"></picture></a>
TestMu AI
> TestMu AI (formerly LambdaTest) is an AI-nati cloud platform built for modern engineering teams. It covers e from autonomous test creation and fast execution to testing AI agents, chatbots and voice assistants.
_Open: Breach / Compromised-Credential Data · Email / Identity Lookup — see SPONSORSHIP.md._
<!-- SPONSORS:END -->
Usage
Start the REPL and in any target — the agent decides which tools to run and chains them on findings:
Want the full in workflow behind this? → AI OSINT Complete Kit ($55)
Features
| Capability | Details |
|---|---|
| AI tool chaining | The agent selects and chains tools based on findings; describe the target in plain language |
| 20 modular tools | Email, username, breach, WHOIS, IP, subdomain, dorks, paste, phone, Shodan, , Censys, IP2Location, AbuseIPDB, GitHub, DNS, live dork search, URL scraping, SERP footprint |
| Three AI backends | Anthropic Claude (default), local Ollama, or any OpenAI-compatible endpoint (LiteLLM, vLLM, LM Studio, ...) |
| Native MCP server | All 20 tools exposed to Claude 代码, Claude Desktop, and any MCP-compatible 客户端 — no extra config |
| Parallel execution | --parallel runs complementary tools concurrently via asyncio.gather() |
| Reports | PDF + Markdown auto-sa every in (reportlab optional) |
| Session history | All REPL sessions saved to ~/.openosint/history/; browse with openosint history |
| Web UI | Browser-based AI chat with streaming output, 工具 cards, light/dark theme |
---
> Legal Disclaimer: OpenOSINT is intended for legal and authorized use only.
> Users are solely responsible for ensuring their use complies with all applicable laws and regulations.
> The authors accept no liability for misuse. See DISCLAIMER.md.
Tools
| Tool | Powered by | What it in |
|------|-----------|---------------------|
| search_email | holehe | Social accounts linked to an email address |
| search_username | sherlock | Username presence across 400+ platforms |
| search_breach | Ha v3 API | Data breach exposure |
| search_whois | python-whois | Domain registrant and DNS info |
| search_ip | ipinfo.io | Geolocation, ASN, hostname |
| search_domain | sublist3r | Subdomain enumeration |
| generate_dorks | built-in | 12 targeted Google dork URLs (no 网络 calls) |
| search_paste | psbdmp.ws | Pastebin dump mentions |
| search_phone | phoneinfoga | Carrier, country, line type |
| search_shodan | Shodan API | Open ports, banners, CVEs |
| search_ | API v3 | from 70+ antivirus engines |
| search_ip2location | IP2Location.io API | Enhanced IP intel: /Tor/datacenter flags *(sponsored)* |
| search_censys | Censys Search API | Internet-facing infrastructure, certificates |
| search_abuseipdb | AbuseIPDB v2 API | IP abuse reputation: confidence score, reports, country, ISP |
| search_github | GitHub REST API | Profile, repos, commit-discovered emails, username/keyword search |
| search_dns | dnspython (built-in) | A/AAAA/MX/NS/TXT/CNAME/SOA records; SPF, DMARC, DKIM analysis |
| search_gdelt_geo | GDELT GEO 2.0 API | Worldwide geolocated news co, GeoJSON output |
| search_dorks_live | Bright Data SERP API | Li search results for dork queries (title, URL, snippet) |
| scrape_url | Bright Data Web Unlocker | Fetch any URL bypassing Cloudflare/CAPTCHA — returns clean Markdown |
| search_footprint | Bright Data SERP API | Entity-type-aware public search-引擎 footprint: detects email/username/domain/phone/name and returns structured results + Entity Correlation Graph nodes/edges |
Full per-工具 documentation, CLI flags, and output formats: openosint.tech.
search_email
Enumerates online services linked to an email address using holehe.
search_username
Searches for a username across 400+ platforms using sherlock.
search_breach
Checks data breach exposure via Ha v3 API. Requires HIBP_API_KEY.
search_whois
Retrie data using python-whois.
search_ip
Retrie and ASN data via ipinfo.io. Free tier: 50k/month.
search_domain
Enumerates subdomains using sublist3r.
generate_dorks
Generates 12 targeted Google dork URLs for any target. No 网络 calls.
search_paste
Searches Pastebin dumps via psbdmp.ws.
search_phone
Gathers phone intelligence using phoneinfoga. Use E.164 format.
search_shodan
IPv4 input → host lookup (open ports, org, CVEs). Any other query → banner/keyword search. Requires SHODAN_API_KEY.
search_
Checks an IP, domain, URL, or file hash against 's 70+ engines. Auto-detects input type. Requires .
search_ip2location
Queries IP2Location.io for enhanced IP intelligence: geolocation, ISP, ASN, and — on the Security Plan — /Tor/datacenter detection. Sponsored integration. Requires IP2LOCATION_API_KEY.
search_censys
IPv4 → host view (open ports, services, ASN). Domain → certificate search (SANs, issuer). Requires CENSYS_API_ID and CENSYS_SECRET.
search_abuseipdb
Checks an IP against AbuseIPDB v2. Returns abuse confidence score, total reports, country, ISP, and last reported timestamp. Requires ABUSEIPDB_API_KEY.
Warning appears when abuseConfidenceScore exceeds 50%.
search_github
Queries GitHub REST API. Username → profile, repos, commit-discovered emails. Keyword → user/repo search. Optional GITHUB_TOKEN raises rate limit from 60 to 5000 req/h.
search_dns
Queries A/AAAA/MX/NS/TXT/CNAME/SOA records and analyzes SPF, DMARC, and DKIM configuration using dnspython (no external API).
search_dorks_live
Executes li dork queries through the Bright Data SERP API¹, returning structured results (title, URL, snippet). Defaults to 5 dorks per run; each is a separate billable API call. Requires BRIGHTDATA_API_KEY and BRIGHTDATA_SERP_ZONE.
scrape_url
Fetches any public URL through Bright Data Web Unlocker¹, bypassing Cloudflare/CAPTCHA. Returns clean Markdown. Requires BRIGHTDATA_API_KEY and BRIGHTDATA_UNLOCKER_ZONE.
search_footprint
Collects a target's public search-引擎 footprint via Bright Data SERP API¹. Detects entity type (email, username, domain, phone, or full name) and runs entity-type-aware Google queries, returning structured results plus Entity Correlation Graph nodes/edges for discovered domains and profiles. Requires BRIGHTDATA_API_KEY and BRIGHTDATA_SERP_ZONE.
---
Graph module (optional)
An additive FollowTheMoney entity graph —
statement-le, an append-only store, non-destructi
deduplication, and a human review queue — sits alongside the tools above
without changing anything about them. Opt in with pip install (Python 3.10+) or
"openosint[graph]""openosint[graph-dedup]" (adds
same_as scoring, needs Python 3.11+), then use it MCP tools:graph_export, graph_neighbors, graph_re. See
docs/graph.md for the full guide and a worked example.
The same workflow is shown end to end — including the .ftm export that
passes ftm — in the terminal demo in
docs/graph.md; the web UI walkthrough is the demo at the top
of this README.
---
Interfaces
Web UI
Browser-based AI chat with streaming 工具 output, inline result cards, light/dark theme toggle. Supports local inference or any OpenAI-compatible endpoint — no Anthropic API key required.
Which hosts and sites may talk to the 服务端. On a loopback bind the 服务端 only answers requests whose Host is 127.0.0.1, localhost or ::1. Every /api/* request from a browser must come from the UI's own origin; cross-site requests are refused (scripts and curl, which send no Origin, are unaffected).
| | Use it when |
|---|---|
| OPENOSINT_ALLOWED_HOSTS | You reach the UI by another name (LAN name, Docker hostname, reverse proxy), e.g. OPENOSINT_ALLOWED_HOSTS=osint.lan,localhost. Comma-separated; host or host:port. On a non-loopback bind (--allow-remote, Docker) the Host check only runs when this is set, so set it there. |
| OPENOSINT_ALLOWED_ORIGINS | A separate front end on another origin calls the API, e.g. OPENOSINT_ALLOWED_ORIGINS=. Comma-separated. |
<di="center">
<a href="
<img src="
alt="OpenOSINT Web UI — li correlation graph demo: in openosint.tech"
width="900" />
</a>
<p><a href=" the live demo →</a> — bring your own Anthropic / OpenRouter / Ollama key, no signup.</p>
</div>
> Breaking change (v2.28+): key usage now follows bind address, not an env var.
> Bound to 127.0.0.1/localhost (the default) — no change: keys in your .env
> work as before. Bound to any other interface (--host 0.0.0.0, which already
> requires --allow-remote) — the web UI never uses a key from your en
> to serve a request; every caller must supply their own, and breach lookups
> (search_breach) are disabled outright. This applies **regardless of any env
> var**, including OPENOSINT_DEMO_MODE, which can only add restriction, never
> remove it. If you were exposing the web UI on a LAN with your own keys and no
> per-caller auth in front of it, that access pattern no longer works.
>
> Running behind a reverse proxy? A loopback bind (127.0.0.1) only means
> the OS accepted the connection from this machine — it says nothing about
> who can reach it if something in front (nginx, Caddy, a Docker/K8s sidecar,
> a tunnel) forwards requests to it from elsewhere. By default, a request that
> carries proxy-forwarding headers (X-Forwarded-For, X-Forwarded-Proto,
> X-Forwarded-Host, Forwarded, CF-Connecting-IP) is treated exactly like
> a non-loopback bind: your local keys are never used, breach lookups are
> blocked, and the caller is told why. **If you deliberately serve this
> through a reverse proxy and want it to behave like a normal local
> instance for requests relayed by that proxy, set OPENOSINT_TRUSTED_PROXY=true.**
> This is a separate from the existing TRUSTED_PROXY (which only
> affects which IP a rate-limit bucket is attributed to — a low-stakes,
> already-loosely-scoped setting some self-hosters already have on).
> Reusing that flag here would ha upgraded an existing
> rate-limit-only configuration into one that also permits credentialed
> access, without asking. OPENOSINT_TRUSTED_PROXY gets its own explicit
> opt-in for that reason. Setting it does not blindly trust the
> forwarded headers' content — internally inconsistent (e.g. two
> disagreeing X-Forwarded-Proto on one request) are still treated
> as public regardless. **Setting OPENOSINT_TRUSTED_PROXY=true means you
> are choosing to ser lookups to whoever your reverse proxy
> relays to this instance — you are the controller for their queries, the
> same way OpenOSINT Cloud is for its customers. Put real authentication in
> front of it if "whoever the proxy relays" is broader than you intend.**
Interactive REPL
Run openosint with no arguments to start the AI-powered REPL:
<di="center">
<img src=" alt="OpenOSINT terminal REPL demo" width="900" />
</div>
REPL commands:
| Command | Description |
|---------|-------------|
| <target> | In any target — email, username, domain, IP, name |
| clear | Reset con memory |
| save | Save last report to reports/ |
| tools | List a tools and their status |
| config | Show current configuration |
| history | Browse sa |
| help | Show all commands |
| exit / Ctrl-D | Exit |
All sessions are auto-saved to ~/.openosint/history/. Browse with openosint history.
For the REPL/CLI with an OpenAI-compatible backend:
Li
Full per-工具 reference, CLI flags, and configuration options at openosint.tech.
<di="center">
<img src=" alt="openosint.tech documentation tour" width="900" />
</div>
MCP Server
Expose all 20 OpenOSINT tools to any MCP-compatible AI 客户端. Once connected, Claude can natively invoke all 20 tools during con.
Claude Code:
Claude Desktop — add to ~/Library/Application Support/Claude/claude_desktop_config.json:
MCP hosts launch this 服务端 with a cwd that has nothing to do with your.env (often your home directory, or wherever the host itself runs from).
The ser back to a repo-root .env for a source checkout, then an
upward search from that arbitrary cwd — but for a pip installedopenosint, neither is reliable. Setting OPENOSINT_EN in the
client's own env block above, as shown, is the one option guaranteed to
work regardless of how the host launches the process.
Agentic use Code:
---
Installation
Quickstart — web UI in one command
Install uv once. It runs OpenOSINT in its own isolated en, so there is no Python setup:
Then start OpenOSINT (open a new terminal first if uvx is not found):
You should see:
Your browser opens automatically; if it doesn't, open < No .env file and no API keys are needed to start — keyless tools work immediately, and AI chat needs a provider key (ANTHROPIC_API_KEY) or a local Ollama.
| Want to… | Do this |
|---|---|
| Use another port | u web --port 8081 (if 8080 is busy, OpenOSINT exits and tells you this) |
| Keep the browser closed | u web --no-browser |
| Find your data | Graph 数据库 and session history live in ~/.openosint/ (%USERPROFILE%\.openosint on Windows). Move it with OPENOSINT_HOME=/path; OPENOSINT_GRAPH_DB still o just graph.db. |
| Find reports | CLI and REPL reports are written to ./reports/ in the directory you ran openosint from. The web UI writes none. |
| Use the entity graph view | Needs the graph extra, which builds PyICU and so needs libicu and a C++ compiler first (Python 3.11+). Ubuntu: sudo apt install libicu-de g++. macOS: brew install icu4c pkg-config and export PKG_CONFIG_PATH="$(brew --prefix icu4c)/lib/pkgconfig". Then u "openosint[graph]" openosint web. On Windows, or to skip the build, use Docker, which includes it. |
Alternatives
External binaries (must be in PATH):
| Binary | Purpose | Install |
|--------|---------|---------|
| holehe | Email account enumeration | pip install holehe |
| sherlock | Username enumeration (300+ platforms) | pip install sherlock-project |
| sublist3r | Subdomain enumeration | pip install sublist3r |
| phoneinfoga | Phone number intelligence | Download binary |
If a binary is absent, the corresponding 工具 returns a descripti. All other tools remain operational.
Optional Python packages:
| Package | Purpose | Install |
|---------|---------|---------|
| ollama | Local LLM backend (no API key) | pip install "openosint[ollama]" *(also requires Ollama runtime)* |
| openai | OpenAI-compatible backend | pip install "openosint[openai]" |
| shodan | Shodan API client | pip install "openosint[shodan]" |
| reportlab | PDF report export | pip install "openosint[pdf]" |
| censys | Censys API client | pip install "openosint[censys]" |
Configuration
Copy .en to .env and fill in your keys. .env is read from the
directory you run openosint from (searched upward, like git finds.git) — it does not need to be at any particular "project root", and a
regular pip install works the same way as running from a 源码 checkout.
Set OPENOSINT_EN=/path/to/.env to point at an explicit file instead
(useful for the MCP 服务端, which is launched by its host with an arbitrary
working directory). A real en always takes priority over
a value in .env.
Required below means required for that specific 工具 to run, not for openosint
itself — the app starts and every key-less 工具 works with zero configuration.
| | Tool | Required | Purpose |
|----------|------|----------|---------|
| ANTHROPIC_API_KEY | AI agent (REPL/Web UI) | Yes, unless using Ollama or an OpenAI-compatible endpoint | Anthropic API key |
| ANTHROPIC_MODEL | AI agent | Optional | Model name to request (default: claude-sonnet-5). Replaces the deprecated OPENOSINT_MODEL. |
| OPENAI_BASE_URL | AI agent | Optional | Base URL of an OpenAI-compatible endpoint (e.g. ) |
| OPENAI_API_KEY | AI agent | Optional | API key for the endpoint (local servers may ignore it) |
| OPENAI_MODEL | AI agent | Optional | Model name to request (default: gpt-4o-mini) |
| OPENOSINT_EN | All | Optional | Explicit path to a .env file, o the directory search above |
| HIBP_API_KEY | search_breach | Required for this tool | Ha v3 — get one |
| IPINFO_TOKEN | search_ip | Optional | Works without it; raises ipinfo.io rate limits |
| SHODAN_API_KEY | search_shodan | Required for this tool | Shodan API — get one |
| | search_ | Required for this tool | API v3 — get one |
| IP2LOCATION_API_KEY | search_ip2location | Required for this tool | IP2Location.io — get one *(sponsored)* |
| CENSYS_API_ID + CENSYS_SECRET | search_censys | Required for this tool | Censys — get one |
| ABUSEIPDB_API_KEY | search_abuseipdb | Required for this tool | AbuseIPDB v2 — get one |
| GITHUB_TOKEN | search_github | Optional | Works without it (60 req/h); raises the limit to 5000 req/h — get one |
| BRIGHTDATA_API_KEY | search_dorks_live, scrape_url, search_footprint | Required for these tools | Bright Data — get one¹ (free tier: 5,000 req/month) |
| BRIGHTDATA_SERP_ZONE | search_dorks_live, search_footprint | Required for these tools | Your Bright Data SERP zone name (e.g. serp_api1) |
| BRIGHTDATA_UNLOCKER_ZONE | scrape_url | Required for this tool | Your Bright Data Web Unlocker zone name (e.g. web_unlocker1) |
On a fresh install with no keys at all, these still work: generate_dorks,search_dns, search_whois, search_domain, search_email, search_username,search_paste, search_phone, search_ip (rate-limited), search_github
(rate-limited), and search_gdelt_geo.
CLI Reference
| Flag / Subcommand | Description |
|---|---|
| openosint | Interactive AI REPL (default) |
| openosint web [--port N] [--no-browser] | Launch browser UI |
| openosint email ADDRESS [-t N] | Direct email scan |
| openosint username HANDLE [-t N] | Direct username scan |
| openosint shodan QUERY [-t N] | Shodan lookup |
| openosint TARGET [-t N] | lookup |
| openosint censys TARGET [-t N] | Censys lookup |
| openosint ip2location IP [-t N] | IP2Location lookup |
| openosint abuseipdb IP [-t N] | AbuseIPDB reputation check |
| openosint github QUERY [-t N] | GitHub profile/repo/email discovery |
| openosint dns DOMAIN [-t N] | DNS records + email security analysis |
| openosint search-dorks-li [--max-dorks N] [-t N] | Li dork results Data |
| openosint scrape URL [-t N] | Fetch a URL Data Web Unlocker |
| openosint footprint TARGET [--max-queries N] [-t N] | SERP footprint Data |
| openosint multi TARGETS | Parallel multi-target in (max 10) |
| openosint playbook RECIPE TARGET | Run a deterministic in playbook (no AI) |
| openosint history [--all] [open N] [clear] | View/manage REPL session history |
| openosint proxy-test | the configured upstream proxy |
| openosint sponsors | List current sponsors and featured integrations |
| openosint prompts | Show info about the AI OSINT Prompt Pack |
| openosint shell | Explicit alias for the default REPL |
| - | Enable debug logging to stderr |
| -t, --timeout N | O subprocess timeout (seconds) |
| --api-key KEY | Anthropic API key (o env var) |
| --parallel | Run complementary tools concurrently |
| --json | Output results as structured JSON |
| --provider {anthropic,ollama,openai} | AI provider (default: anthropic) |
| --ollama-model MODEL | Ollama model name (default: llama3.2) |
| --ollama-host URL | Ollama server URL (default: ) |
| --openai-base-url URL | OpenAI-compatible endpoint base URL (env: OPENAI_BASE_URL) |
| --openai-model MODEL | Model to request from the endpoint (default: gpt-4o-mini; env: OPENAI_MODEL) |
| --openai-api-key KEY | API key for the endpoint (env: OPENAI_API_KEY) |
| --no-pdf | Disable automatic PDF generation |
Docker
.env is optional: with no keys the web UI still starts at < To provide keys today, list them under en: in docker-compose.yml (or in a .env next to it), or put a .env in the data (/data/.env). Reports are persisted to ./reports/; the graph 数据库 and session history live in the openosint-data (/data in the container, via OPENOSINT_HOME). The image includes the graph view.
The port is published on 127.0.0.1 only, and the Host check is on (OPENOSINT_ALLOWED_HOSTS defaults to localhost,127.0.0.1 in the compose file; extend it if you reach the UI by another name). To reach it from other machines on purpose, run OPENOSINT_BIND=0.0.0.0 docker compose up: the instance then runs in restricted mode (it ne keys held on the 服务端). Security note: the UI's setup endpoint accepts and stores API keys, so only do this on a 网络 and behind a firewall or reverse proxy you trust.
> Warning: OPENOSINT_PUBLISHED_BIND. docker-compose.yml sets this to the same value as OPENOSINT_BIND to tell the ser address the port is published on; an exact loopback value (127.0.0.1, localhost, ::1) lifts the restriction that a container's 0.0.0.0 bind otherwise gets. Never set it to a loopback value yourself, or edit the compose port mapping away from it, when the port is published on any other interface.
Integrations
| Service | URL | Tool | Tier | Auth |
|---------|-----|------|------|------|
| IP2Location.io | | search_ip2location | Featured (sponsored) | API key — free tier |
| RapidProxy | | — | Featured (sponsored) | — |
| AbuseIPDB | | search_abuseipdb | Community | API key — free tier |
| Censys | | search_censys | Community | API key — free tier |
| GitHub | | search_github | Community | Token optional |
| Ha | | search_breach | Community | API key — paid |
| holehe | | search_email | Community | None — local binary |
| ipinfo.io | | search_ip | Community | Token optional |
| phoneinfoga | | search_phone | Community | None — local binary |
| psbdmp.ws | | search_paste | Community | None |
| sherlock | | search_username | Community | None — local binary |
| Shodan | | search_shodan | Community | API key — free tier |
| sublist3r | | search_domain | Community | None — local binary |
| | | search_ | Community | API key — free tier |
| WHOIS (IANA) | | search_whois | Community | None |
| DNS (system resolver) | — | search_dns | Community | None |
| Google Search | | generate_dorks | Community | None |
Limitations
It does not bypass authentication, exploit systems, or access anything you
aren't already entitled to see. You are responsible for complying with the
law and the terms of service of every 源码 you query. See
DISCLAIMER.md.
currently returns. A negati (no breach found, no accounts found)
means the 源码 didn't report a match — not that no exposure exists.
the 20 tools hard-require an API key and are subject to that provider's
uptime, rate limits, and pricing (Shodan, , Censys, AbuseIPDB,
IP2Location, Ha, and the three Bright Data–backed tools). Free
tiers are small; heavy use requires a paid plan with the provider, not with
OpenOSINT.
holehe, sherlock,sublist3r, and phoneinfoga run as external processes on your machine.Keep them updated yourself; OpenOSINT does not patch or vet them.
openosint[graph]) is additive, notauthoritative.**
same_as links are scored candidates for human review,not identity matches — see docs/graph.md.
open web freely, run arbitrary 代码, or invent data — every finding comes
from a real 工具 call, but the agent's 工具 selection can still be wrong
or incomplete for a gi.
Resources
Purchases directly fund OpenOSINT's de.
Sponsor this project
OpenOSINT is used by OSINT practitioners, security researchers, and de actively e intelligence APIs. Every time a user configures an integration, the docs route them to that provider's sign-up page — high-intent exposure at the moment of adoption.
Featured Integration ($2,000/year or $220/month): recommended/default provider for one 工具 category, exclusive. Logo + badge across README, docs, CLI banner, and Web UI. One per category.
Current sponsors and open categories are listed in the sponsor block at the top of this README. Full media kit, pricing, and the referral funnel: SPONSORSHIP.md.
Open Collective · · SPONSORSHIP.md
Affiliate program
Earn 30–45% commission promoting the AI OSINT Prompt Pack, Operator's Playbook, and Complete Kit.
Good fit for OSINT/infosec newsletter authors, security YouTube channels, and 工具-directory maintainers.
→ Affiliate program details & terms
Commercial License & Support
OpenOSINT is free and MIT-licensed for e — personal projects, commercial products, SaaS, and closed-源码 are all covered with no purchase required. Organizations that additionally need a contract, written warranty, indemnification, SLA, or priority support for procurement and compliance can purchase a commercial plan. Three tiers a from €300/year — see COMMERCIAL.md for full details and pricing. Contact: .
Contributing
Issues and pull requests are welcome. See CONTRIBUTING.md for the de workflow, integration registration checklist, and coding con. Please read DISCLAIMER.md before contributing.
Regenerating the demo GIF/MP4
See scripts/record-demo/README.md for full prerequisites and pipeline details.
Maintainer
Tommaso Bertocchi
Contributors
| Contributor | Contribution |
|---|---|
| | ven binary resolution fix — co-installed tools are now found without a separate acti step (#6) |
License
OpenOSINT is open 源码 under the MIT License — free for any use, including personal, commercial, academic, and closed-源码.
---
¹ Bright Data links in this README are affiliate/referral links — OpenOSINT earns a commission if you sign up through them, at no extra cost to you.
*For authorized security research only. See DISCLAIMER.md.*
*OpenOSINT v2.30.0 — October 2026*
Star History
![Star History Chart]()
项目信息
开发语言:Python
Star 数:1691
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AI-powered OSINT agent with interactive REPL, MCP 服务端, and CLI. 20 tools. Works with Claude, GPT-4, or local models. For authorized security research only.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | OpenOSINT - AI-powered OSINT agent with interactive REPL, MCP |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:30:52 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 119 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |