 安全软件
点击放大
vuls - Agent-less vulnerability scanner for Linux, FreeBS
项目说明
Vuls: Scanner
![License]()
![Go Report Card]()
![Contributors]()
!
scanner for Linux/FreeBSD, agent-less, written in Go.
Twitter: @
!
!
![asciicast]()
!
----
Abstract
For a system administrator, having to perform security analysis and software update on a daily basis can be a burden.
To avoid downtime in a production en, it is common for a system administrator to choose not to use the automatic update option provided by the package manager and to perform update manually.
This leads to the following problems.
Vuls is a tool created to solve the problems listed above. It has the following characteristics.
!
----
Main Features
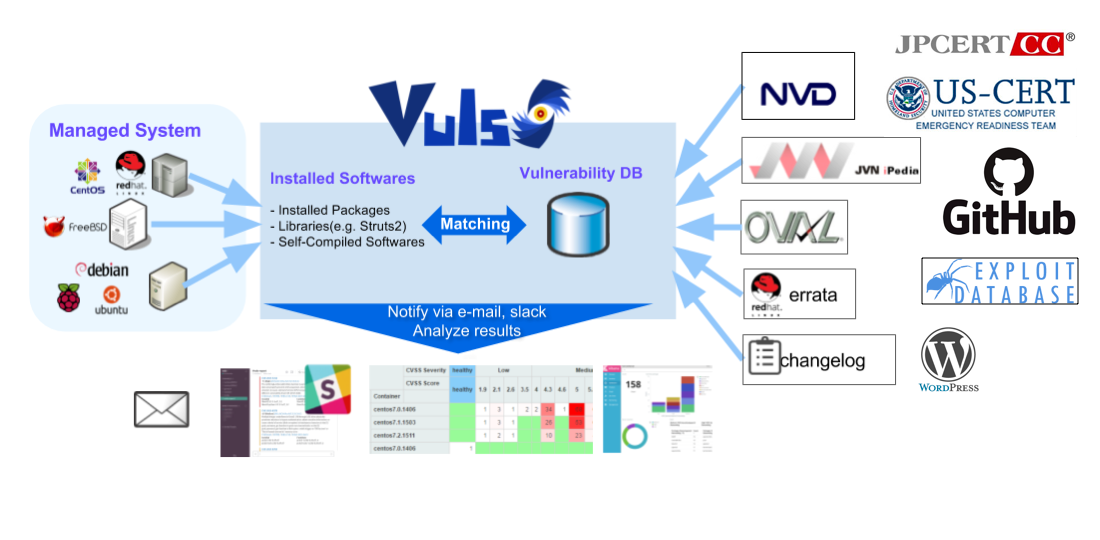
Scan for any in Linux/FreeBSD/Windows/macOS
Supports major Linux/FreeBSD/Windows/macOS
High-quality scan
- NVD
- J)
- Red Hat
- Debian
- Ubuntu
- SUSE
- Oracle Linux
- Alpine-secdb
- Red Hat Security Ad
- Debian Security Bug Tracker
- Ubuntu C
- Microsoft CVRF
- RHSA / ALAS / ELSA / FreeBSD-SA
- Changelog
- Exploit Database
- Metasploit-Framework modules
- qazbnm456/awesome-c
- nomi-sec/PoC-in-GitHub
- gmatuz/inthewilddb
- projectdiscovery/nuclei-templates
- US-CERT
- JPCERT
- CISA(Cybersecurity & Infrastructure Security Agency): Known Exploited Catalog
- : KEV
- mitre/cti
- aquasecurity/
- wpscan
Scan mode
Fast Scan
Fast Root Scan
Remote, Local scan mode, Server mode
Remote scan mode
Local scan mode
Server mode
Dynamic Analysis
Scan of non-OS-packages
Vuls has some options to detect the
Scan WordPress core, themes, plugins
MISC
- Vuls works well with Continuous Integration since tests can be run every day. This allows you to find very quickly.
- Auto-detection of servers set using CIDR, generate configuration file template
----
What Vuls Doesn't Do
----
Document
For more information such as Installation, Tutorial, Usage, visit vuls.io
日本語翻訳ドキュメント
----
Authors
kotakanbe () created vuls and these fine people ha.
Contribute
see
----
Sponsors
| | |
| ------------- | ------------- |
| <a href=" src="img/sponsor/tines.png" align="left" width="600px" ></a> | Tines is no-code automation for security teams. Build powerful, reliable workflows without a de team. |
| <a href=" src=" align="left" width="600px" ></a> | SAKURA internet Inc. is an Internet company founded in 1996. We provide cloud computing services such as "Sakura's Shared Server", "Sakura's VPS", and "Sakura's Cloud" to meet the needs of a wide range of customers, from indi and corporations to the education and public sectors, using its own data centers in Japan. Based on the philosophy of "changing what you want to do into what you can do," we offer DX solutions for all fields. |
----
License
Please see LICENSE.
项目信息
开发语言:Go
Star 数:12276
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | vuls - Agent-less vulnerability scanner for Linux, FreeBS |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:31:48 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 421 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |