 安全软件
点击放大
osv-scanner - Vulnerability scanner written in Go which uses the
项目说明
<picture>
<source srcset="/docs/images/osmode.svg" media="(prefers-color-scheme: dark)">
<!-- markdown-link-check-disable-next-line -->
<img src="/docs/images/ostmode.svg">
</picture>
---
![OpenSSF Scorecard]()
![Checks]()
![codecov]()
![SLSA 3]()
![GitHub Release]()
Use OS to find existing affecting your project's dependencies.
OS provides an officially supported frontend to the OS and CLI interface to OS that connects a project’s list of dependencies with the that affect them.
OS supports a wide range of project types, package managers and features, including but not limited to:
OS uses the extensible OS library under the hood to provide this functionality. If a language or package manager is not supported currently, please file a feature request.
#### Underlying database
The underlying database, OSV.dev has several benefits in comparison with closed source ad databases and scanners:
The above all results in accurate and actionable notifications, which reduces the time needed to resolve them. Check out OSV.dev for more details!
Basic installation
To install OS, please refer to the installation section of our documentation. OS releases can be found on the releases page of the GitHub repository. The recommended method is to download a prebuilt binary for your platform. Alternatively, you can usego install github.com/google/os/v2/cmd/os to build it from source.
Key Features
For more information, please read our detailed documentation to learn how to use OS. For detailed information about each feature, click their titles in this README.
Please note: These are the instructions for the latest OS V2 beta. If you are using V1, checkout the V1 README and documentation instead.
Scanning a source directory
This command will recursively scan the specified directory for any supported package files, such as package.json, go.mod, pom.xml, etc. and output any discovered .
OS has the option of using call analysis to determine if a function is actually being used in the project, resulting in fewer false positives, and actionable alerts.
OS can also detect C/C++ code for scanning. See here for details.
#### Supported Lockfiles
OS supports 11+ language ecosystems and 19+ lockfile types. To check if your ecosystem is covered, please check out our detailed documentation.
Container Scanning
OS also supports comprehensi scanning for container images to detect in the following operating system packages and language-specific dependencies.
| Distro Support | Language Artifacts Support |
| -------------- | -------------------------- |
| Alpine OS | Go |
| Debian | Java |
| Ubuntu | Node |
| | Python |
See the full documentation for details on support.
Usage:
!screencast of html output of container scanning
License Scanning
Check your dependencies' licenses using deps.dev data. For a summary:
To check against an allowed license list (SPDX format):
Offline Scanning
Scan your project against a local OS. No network connection is required after the initial database download. The database can also be manually downloaded.
Guided Remediation (Experimental)
> [!WARNING]
> Guided remediation (the fix command) can be risky when run on untrusted projects. It may trigger the package manager to execute scripts or follow external registries specified in the project. Please ensure you trust the source code and artifacts before proceeding.
OS provides guided remediation, a feature that suggests package upgrades based on criteria such as dependency depth, minimum se, fix strategy, and return on in.
We currently support remediating in the following files:
| Ecosystem | File Format (Type) | Supported Remediation Strategies |
| :-------- | :----------------------------- | :--------------------------------------------------------------------------------------------------------------------- |
| npm | package-lock.json (lockfile) | in-place |
| npm | package.json (manifest) | relock |
| Maven | pom.xml (manifest) | o |
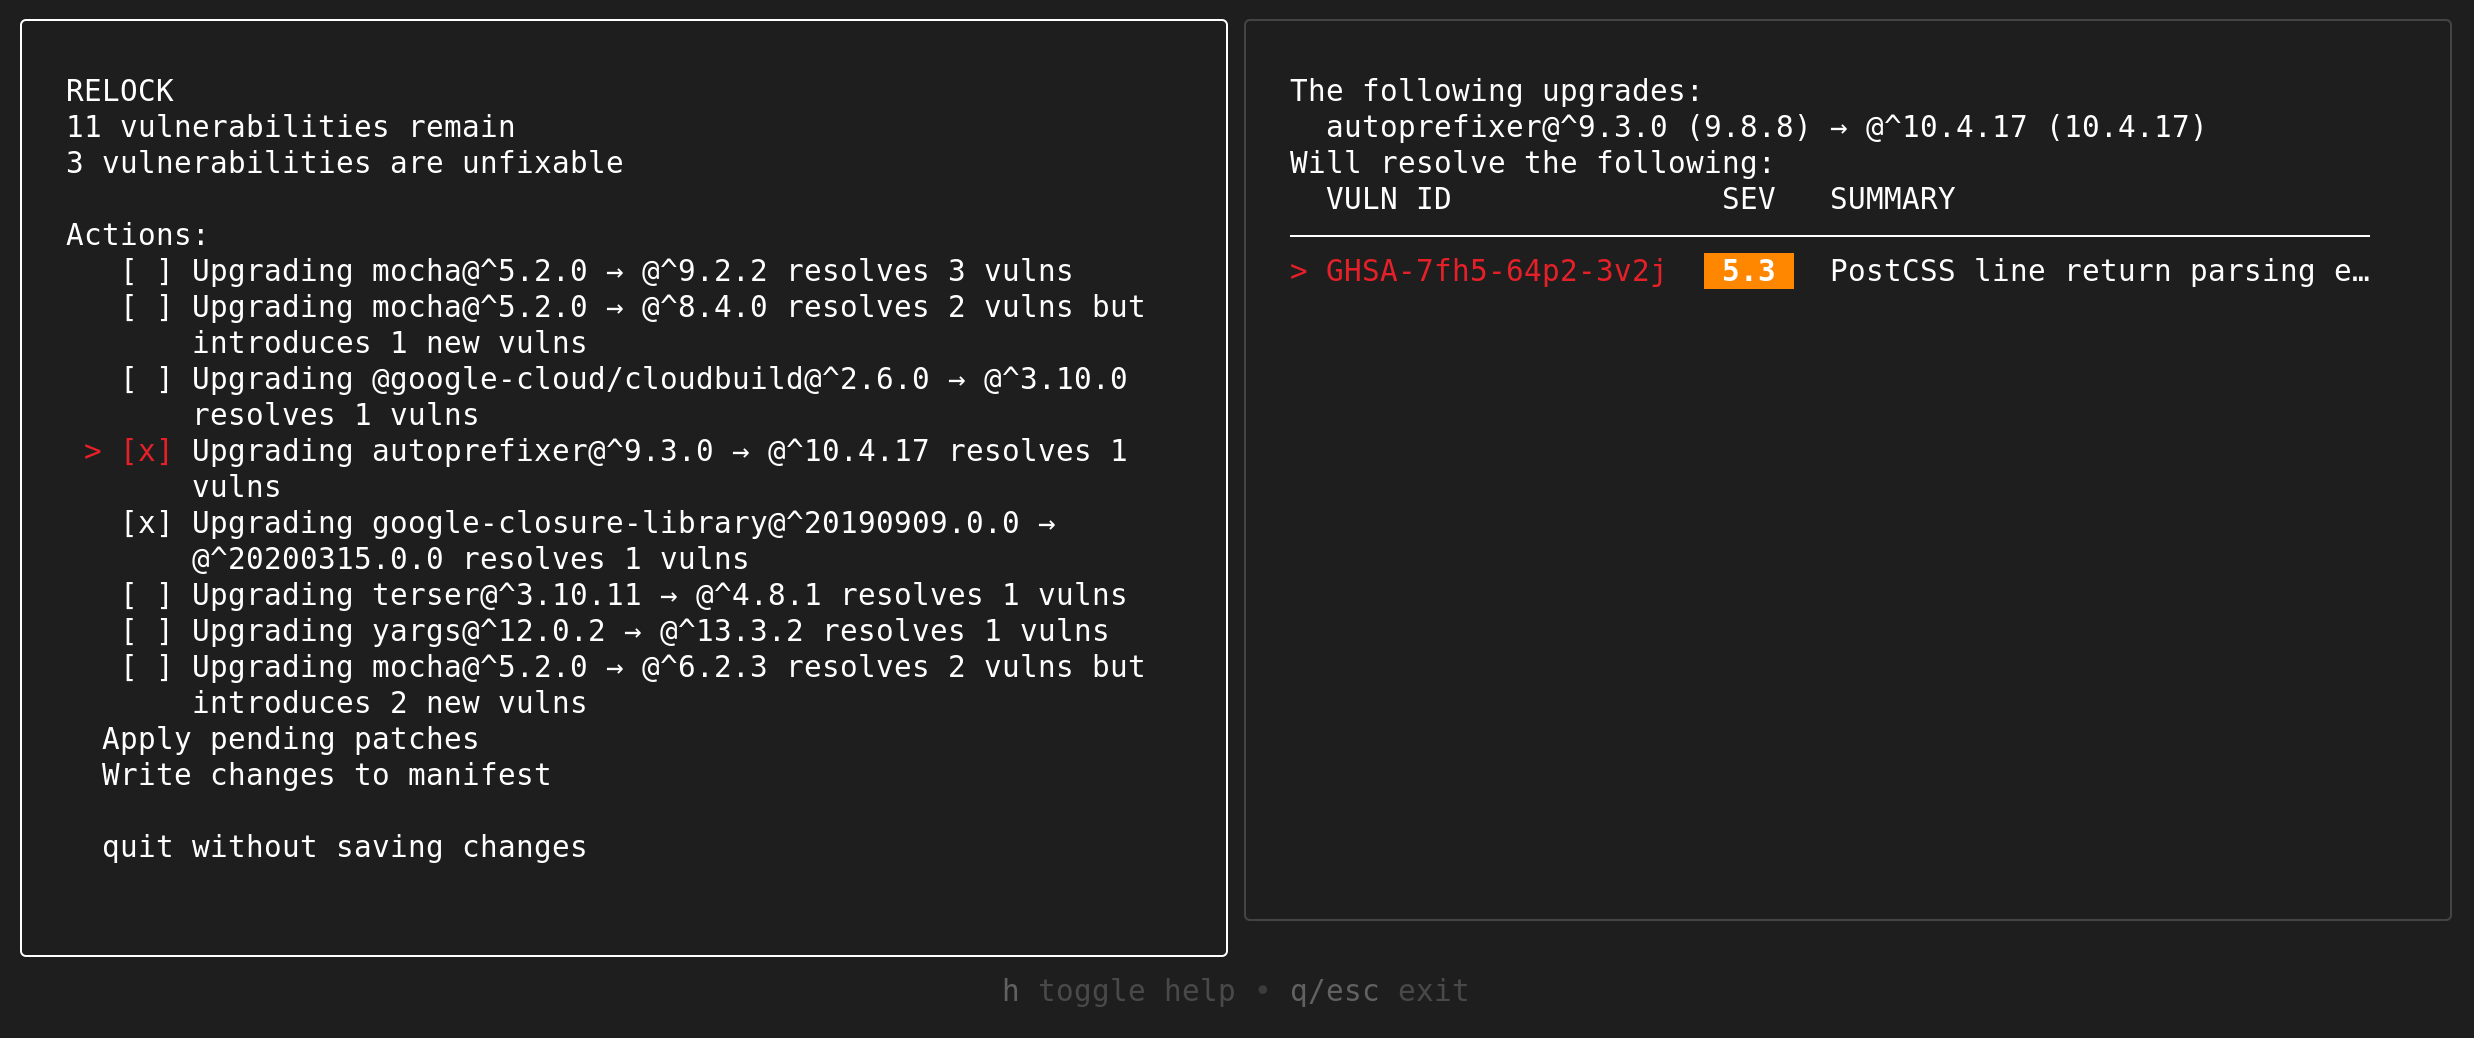
This is a as a headless CLI command, as well as an interactive mode.
#### Example (for npm)
#### Interactive mode (for npm)
<img src=" alt="Screenshot of the interacti results screen with some relaxation patches selected">
Data Sources and Privacy
OS communicates with the following external services during operation:
OSV.dev API
The primary data source for information. OS queries this API to check packages for known and to identify C/C++ dependencies. Data sent includes package names, , ecosystems, and file hashes. Use --offline mode to disable network requests and scan against a local database instead.
deps.dev API
Used for supplementary package information:
--licenses flag): Retrie information for packagesData sent includes package names, , and ecosystems. No source code is transmitted.
Package Registries
When using nati for dependency resolution (instead of deps.de may query:
| Registry | URL | Used For |
| ------------- | ------------------------------ | ------------------------------------ |
| Ma | repo.ma.org/maven2 | Ma metadata and POM files |
| npm Registry | registry.npmjs.org | npm package metadata |
| PyPI | pypi.org | Python package metadata |
Contribute
Report Problems
If you have what looks like a bug, please use the GitHub issue tracking system. Before you file an issue, please search existing issues to see if your issue is already covered.
Contributing code to os
See CONTRIBUTING.md for documentation on how to contribute code.
Star History
![Star History Chart]()
项目信息
开发语言:Go
Star 数:11138
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Vulnerability scanner written in Go which uses the data provided by
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | osv-scanner - Vulnerability scanner written in Go which uses the |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:31:51 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 87 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |