 安全软件
点击放大
cwe_checker - cwe_checker finds vulnerable patterns in binary ex
项目说明
<p align="center">
<img src="doc/images/cwe_checker_logo.png" alt="cwe_checker logo" width="50%" height="50%"/>
</p>
cwe_checker #
!Acceptance tests
!Unit tests
!Docker-Pulls
![Documentation]()
What is cwe_checker? ##
cwe_checker is a suite of checks to detect common bug classes such as Null pointer dereferences and buffer o.
These bug classes are formally known as Common Weakness Enumerations (CWEs).
The checks are based on a of anaylsis techniques ranging from simple heuristics to abstract interpretation-based data-flow analysis.
Its main goal is to aid analysts to quickly find potentially code paths.
Its main focus are ELF binaries that are commonly found on Linux and Unix operating systems.
The cwe_checker uses Ghidra to disassemble binaries into one common intermediate representation
and implements its own analyses on this IR.
Hence, the analyses can be run on most CPU architectures that Ghidra can disassemble,
which makes the cwe_checker a tool for firmware analysis.
The following arguments should convince you to gi* a try:
<p align="center">
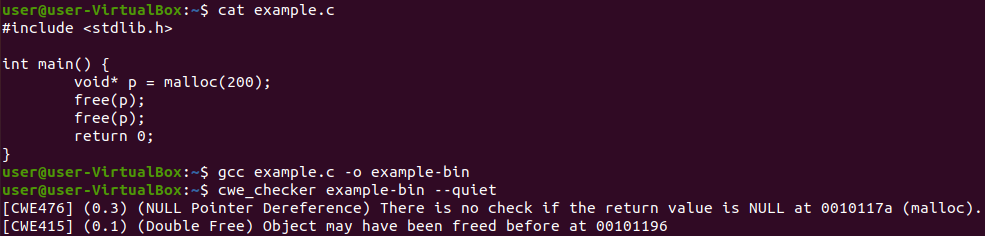
<img src="doc/images/example_usage.png" alt="Usage Example" width="80%" height="80%"/>
</p>
Installation ##
Using the docker image ###
The simplest way is to pull the latest Docker image from the Github container registry:
docker pull ghcr.io/fkie-cad/cwe_checker:latest yields an image based on the current master branch.docker pull ghcr.io/fkie-cad/cwe_checker:stable yields an image based on the latest stable release .docker pull ghcr.io/fkie-cad/cwe_checker:v0.9 yields an image based on the v0.9 stable release .However, it is recommended to switch to newer stable releases as soon as they get published, since impro between stable can be quite significant.
If you want to build the docker image yourself, just run
This way you can also build nati images for ARM-based PCs (e.g. newer Apple Macs).
The prebuilt Docker images are currently only x86-based.
Local installation ###
The following dependencies must be installed in order to build and install the *cwe_checker* locally:
Run make all GHIDRA_PATH=/path/to/ghidra_folder (with the correct path to the local Ghidra installation inserted) to compile and install the cwe_checker.
If you omit the GHIDRA_PATH argument the installer will search your file system for a local installation of Ghidra.
Usage ##
The *cwe_checker* takes a binary as input,
runs several checks based on static analysis on the binary
and then outputs a list of CWE warnings that have been found during the analysis.
If you use the official docker image, just run
If you installed the *cwe_checker* locally, run
If you use nix flakes, run
You can adjust the behavior of most checks via a configuration file located at src/config.json.
If you modify it, add the command line flag --config=src/config.json to tell the *cwe_checker* to use the modified file.
For information about other a command line flags you can pass the --help flag to the *cwe_checker*.
There is _experimental_ support for the analysis of Linux loadable kernel modules
(LKMs). *cwe_checker* will recognize if you pass an LKM and will execute a
subset of the CWE checks a for user-space programs. Analyses are
configurable via a separate configuration file.
If you use the stable , you can also look at the online documentation for more information.
For Bare-Metal Binaries ###
The cwe_checker offers experimental support for analyzing bare-metal binaries.
For that one needs to provide a bare metal configuration file via the --bare-metal-config command line option.
An example for such a configuration file can be found at bare_metal/stm32f407vg.json
(which was created and tested for an STM32F407VG MCU).
For more information take a look at the online documentation.
Documentation and Tests ##
The test binaries for our test suite can be built with make compile_test_files (needs Docker to be installed!). The test suite can then be run with make test.
Source code documentation can be built with make documentation. For the stable , the documentation can be found here.
Implemented Checks <a name=checks></a> ##
So far the following analyses are implemented:
Please note that both false positives and false negatives are to be expected due to shortcuts and the nature of static analysis as well as o.
You can find information on the inner workings of each check as well as known reasons for false positives and false negatives on the check-specific documentation pages.
Integration into other tools ##
cwe_checker comes with a script for Ghidra,
which parses the output of the cwe_checker and annotates the found CWEs in the disassembler for easier manual analysis.
The script is located at ghidra_plugin/cwe_checker_ghidra_plugin.py, usage instructions are contained in the file.
<p align="center">
<img src="doc/images/example_ghidra_integration.png" alt="Ghidra Integration" width="90%" height="90%"/>
</p>
The cwe_checker is also integrated as a plugin in FACT.
If you want to integrate the cwe_checker into your own analysis toolchain, you can use the --json command line flag (in combination with either the --quiet or the --out=... command line options) to generate the CWE warnings in an easily parseable JSON output format.
How does cwe_checker work internally? ##
Building the documentation using cargo doc --open --document-pri --no-deps will give you more information about the internal structure of the cwe_checker.
However, the best documentation is still the source code itself.
If you ha, be sure to ask them on our discussions page!
We are constantly striving to impro and documentation and your questions will help us to achieve that!
To get a quick/initial o of its internals you can also look at the slides of conference presentations on the *cwe_checker* in the *doc* folder.
We presented cwe_checker at the following conferences so far:
Contribute ##
Contributions are always welcome. Just fork it and open a pull request!
Acknowledgements ##
This project is partly financed by German Federal Office for Information Security (BSI).
A special thanks goes out to the BAP community (especially the official gitter) for answering questions and discussing solutions.
License ##
项目信息
开发语言:Rust
Star 数:1361
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕cwe_checker finds vulnerable patterns in binary executables展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | cwe_checker - cwe_checker finds vulnerable patterns in binary ex |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:33:31 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 186 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |